Categories
Self-Hosted Reverse Proxy Docker Management Network Gateway Port Forwarding Dynamic DNS Web Application Firewall SSL CertificatesStars
Forks
Watchers
Developer links
Gately
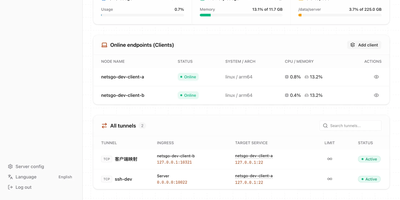
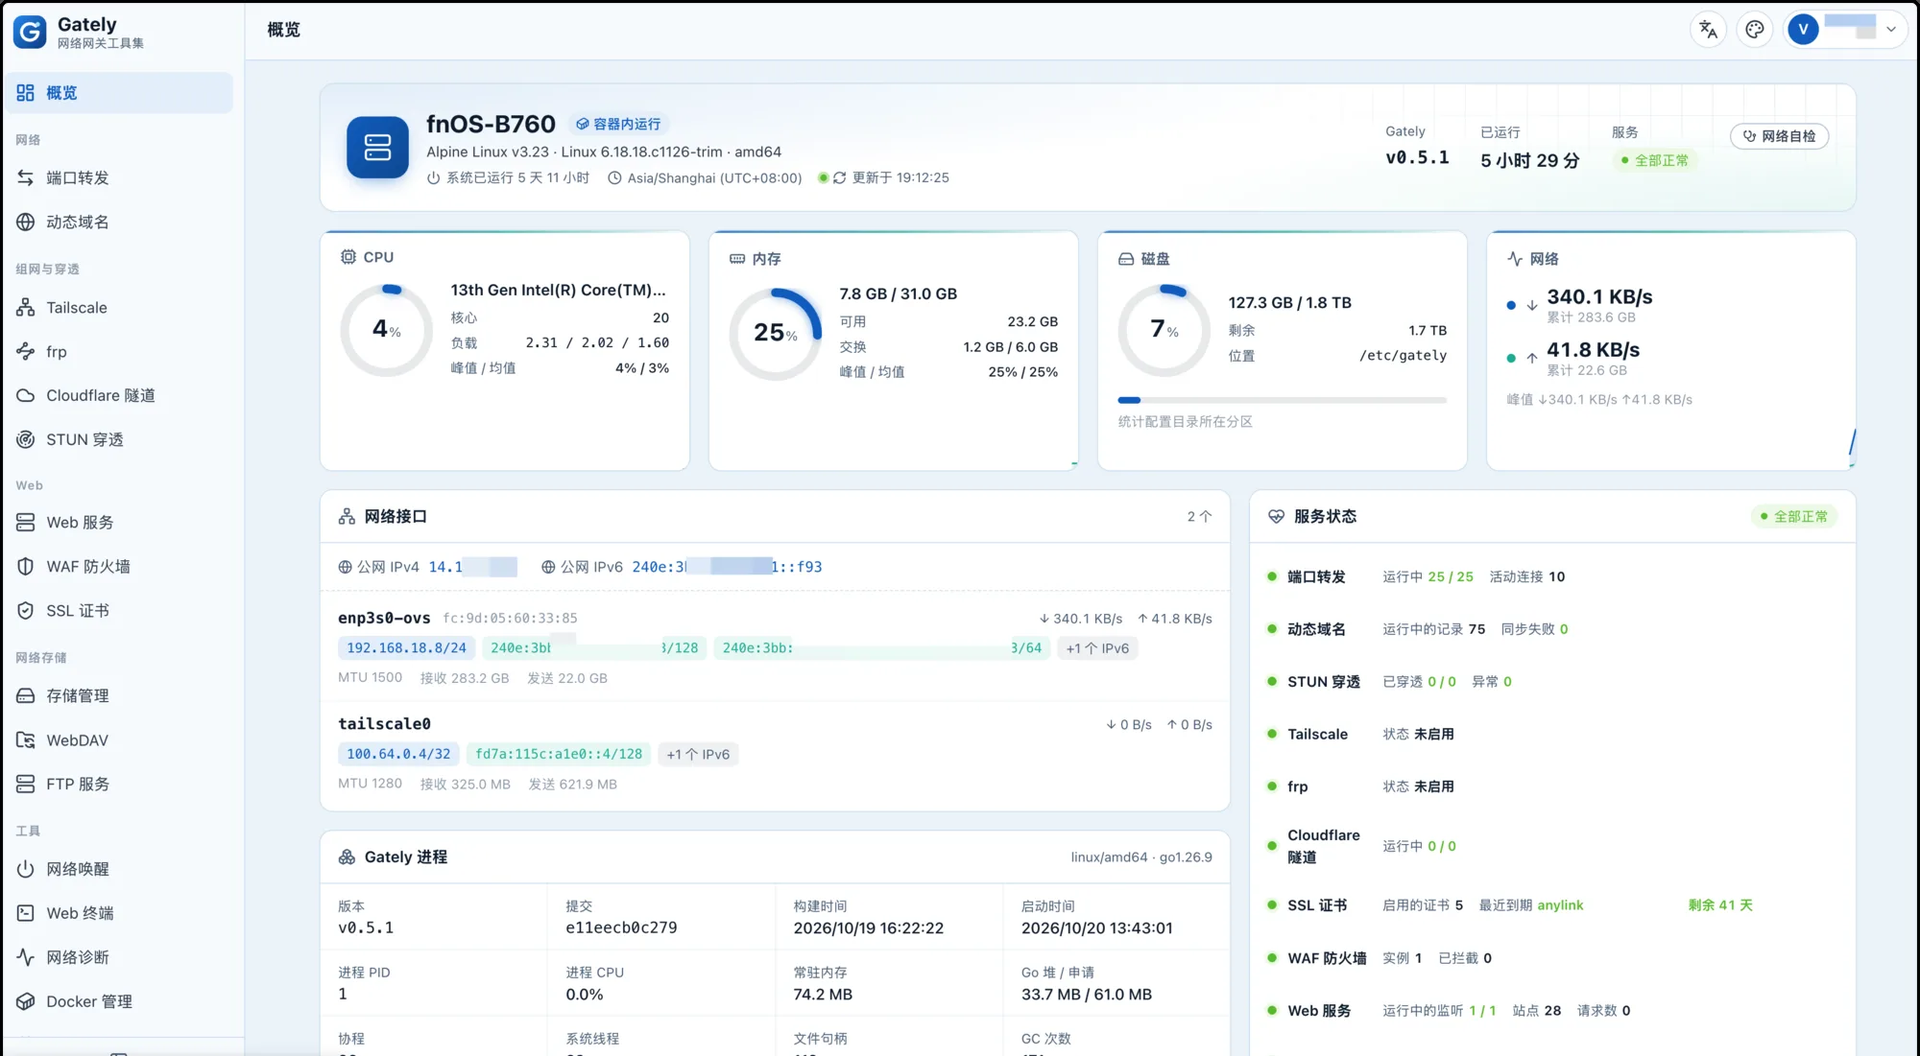
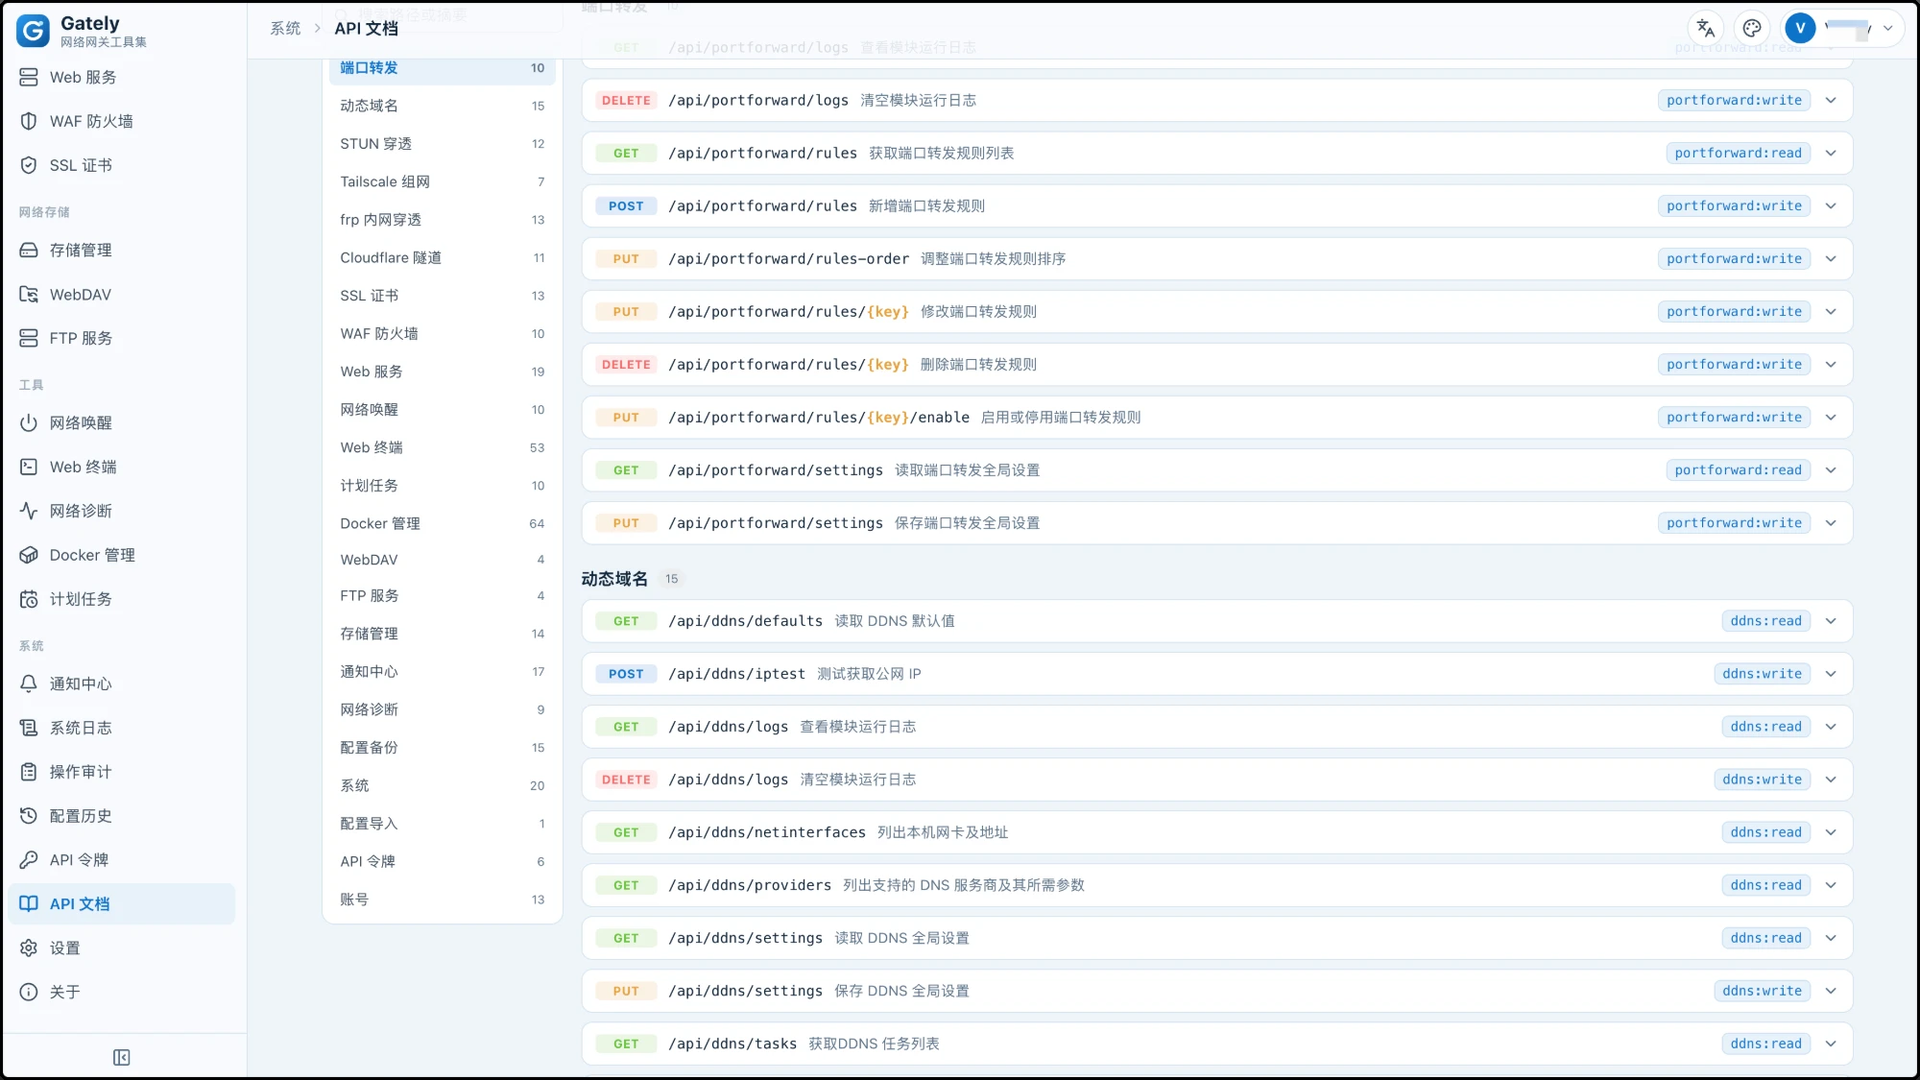
Gately keeps your domain names current, forwards ports, terminates HTTPS, and blocks hostile traffic from one admin console, so a server or home network needs no pile of separate gateway tools. Dynamic DNS updates records at Cloudflare, Alibaba Cloud, Tencent Cloud, DNSPod, Huawei Cloud, Route 53, OVHcloud, Gandi, Namecheap, DuckDNS, and other providers, finding the public address over IPv4 or IPv6 by URL, network interface, or command. Port forwarding relays TCP and UDP with port ranges, failover targets, connection limits, traffic statistics, and PROXY protocol, while SNI routing lets several services share port 443. Certificates are issued and renewed through ACME with DNS-01 wildcards or HTTP-01, then pushed to other hosts over SSH. Web services add per-domain reverse proxies, redirects, and static sites with HTTP/3, WebSocket, load balancing, health checks, rate limiting, caching, and sign-in through OIDC, GitHub, Google, or TOTP-protected shared users. A WAF running the OWASP Core Rule Set and fail2ban-style jails with trap ports and nftables bans guard the edge. Manage Docker containers and Compose projects with one-click upgrades and rollback, open SSH sessions with an SFTP file manager, run ping, traceroute, and speed tests, and receive alerts in Telegram, Discord, Slack, ntfy, or email. An audit log, config history with diff and rollback, encrypted backups, scoped API tokens, and Prometheus metrics round it out. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- One Console For Every Gateway Job
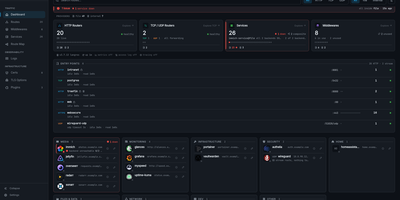
- DDNS, port forwarding, certificates, reverse proxy, WAF, Docker, and a web terminal share one admin UI, and each module can be switched off so disabled modules start no services and serve no API.
- Edge Defense Without Extra Tools
- Coraza WAF with the OWASP Core Rule Set, fail2ban-style log jails, trap ports, and GeoIP filtering block attackers, with bans written to the host nftables firewall, escalating durations, and permanent blocks.
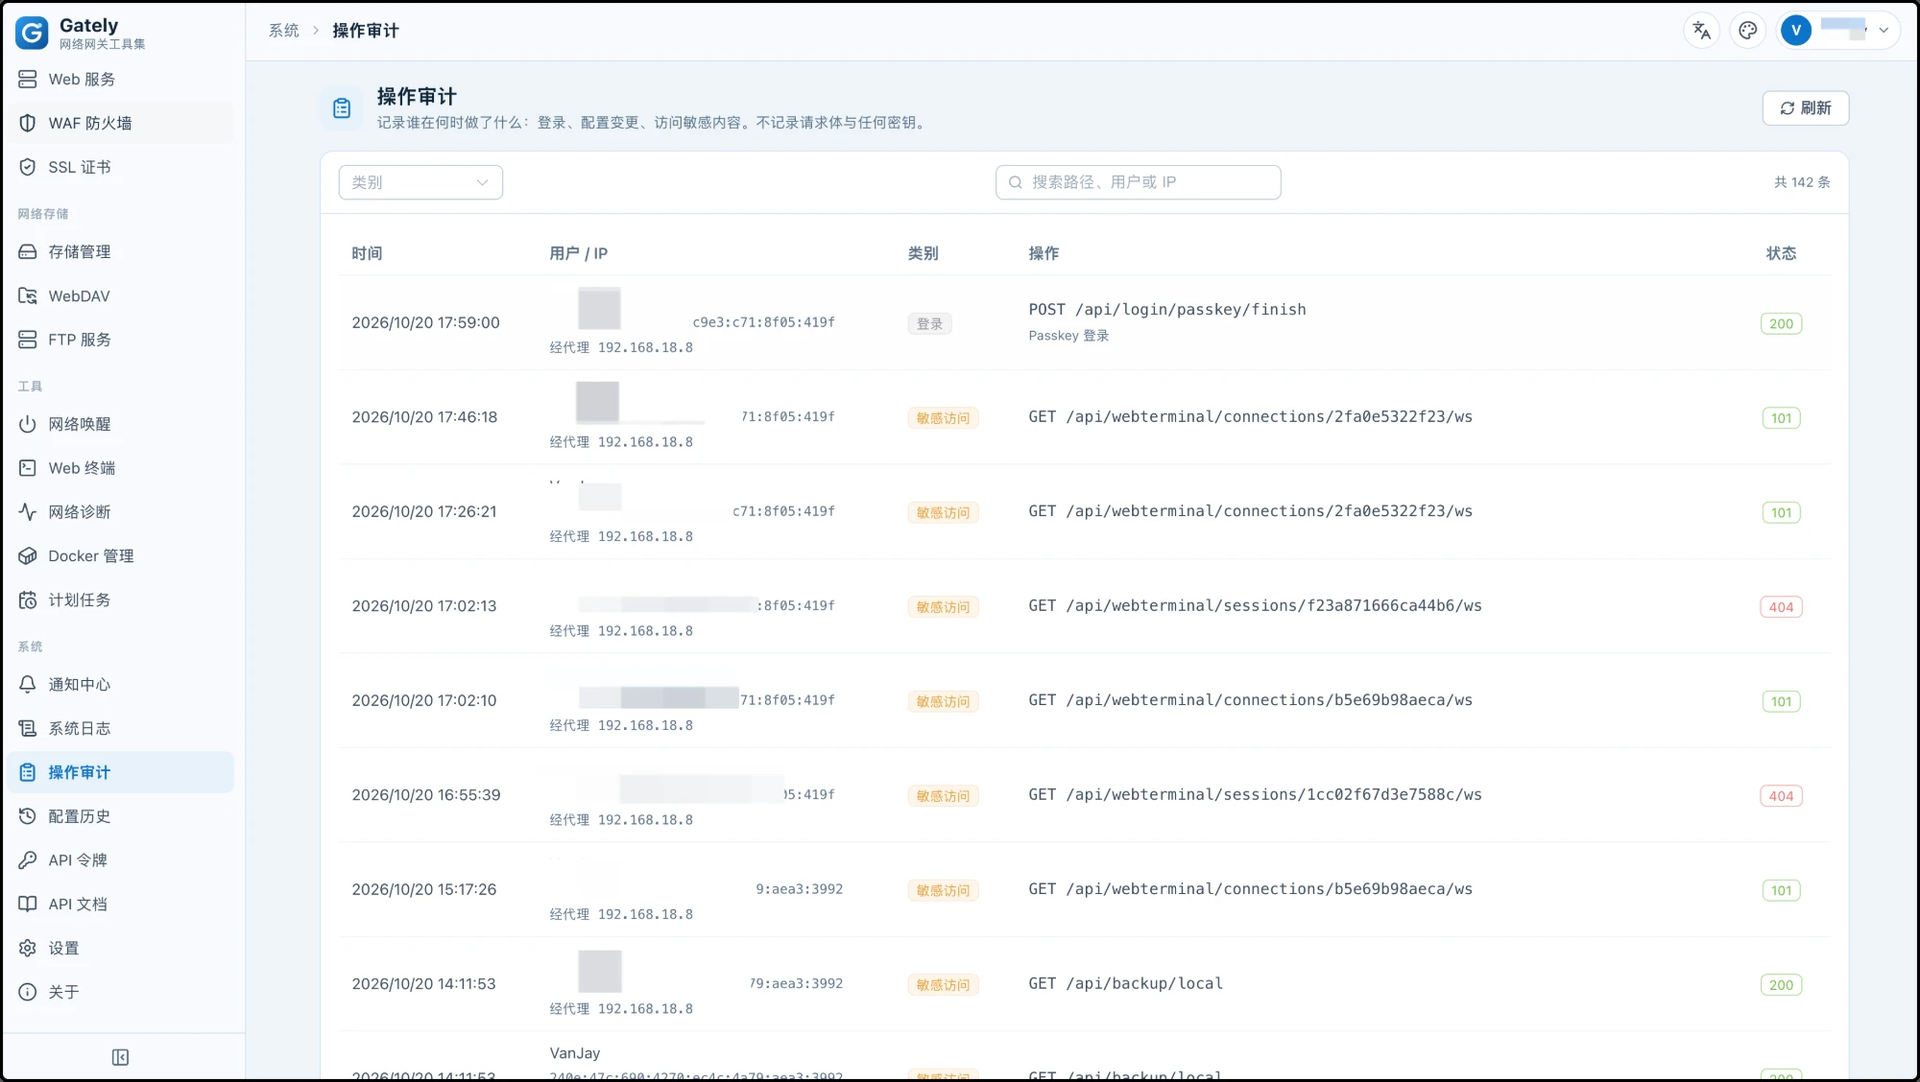
- Private, Transparent, And Auditable
- No connections to project servers and no device reporting by default; every outbound address is visible and editable, and configuration is plain JSON with restricted file permissions, ready for git diffs.
- Small Footprint, Flexible Deployment
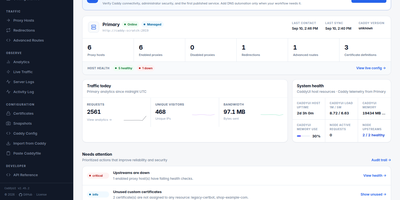
- One static binary of about 32 MB with the web UI embedded runs under Docker, systemd, or OpenWrt on amd64, arm64, and arm hosts, measured at roughly 110 MB of memory under load.
Features
- Dynamic DNS Providers
- Updates records at Cloudflare, Alibaba Cloud, Tencent Cloud, DNSPod, Route 53, OVHcloud, Gandi, Namecheap, DuckDNS, and DynDNS2 services, detecting IPv4 or IPv6 addresses by URL, interface, or command.
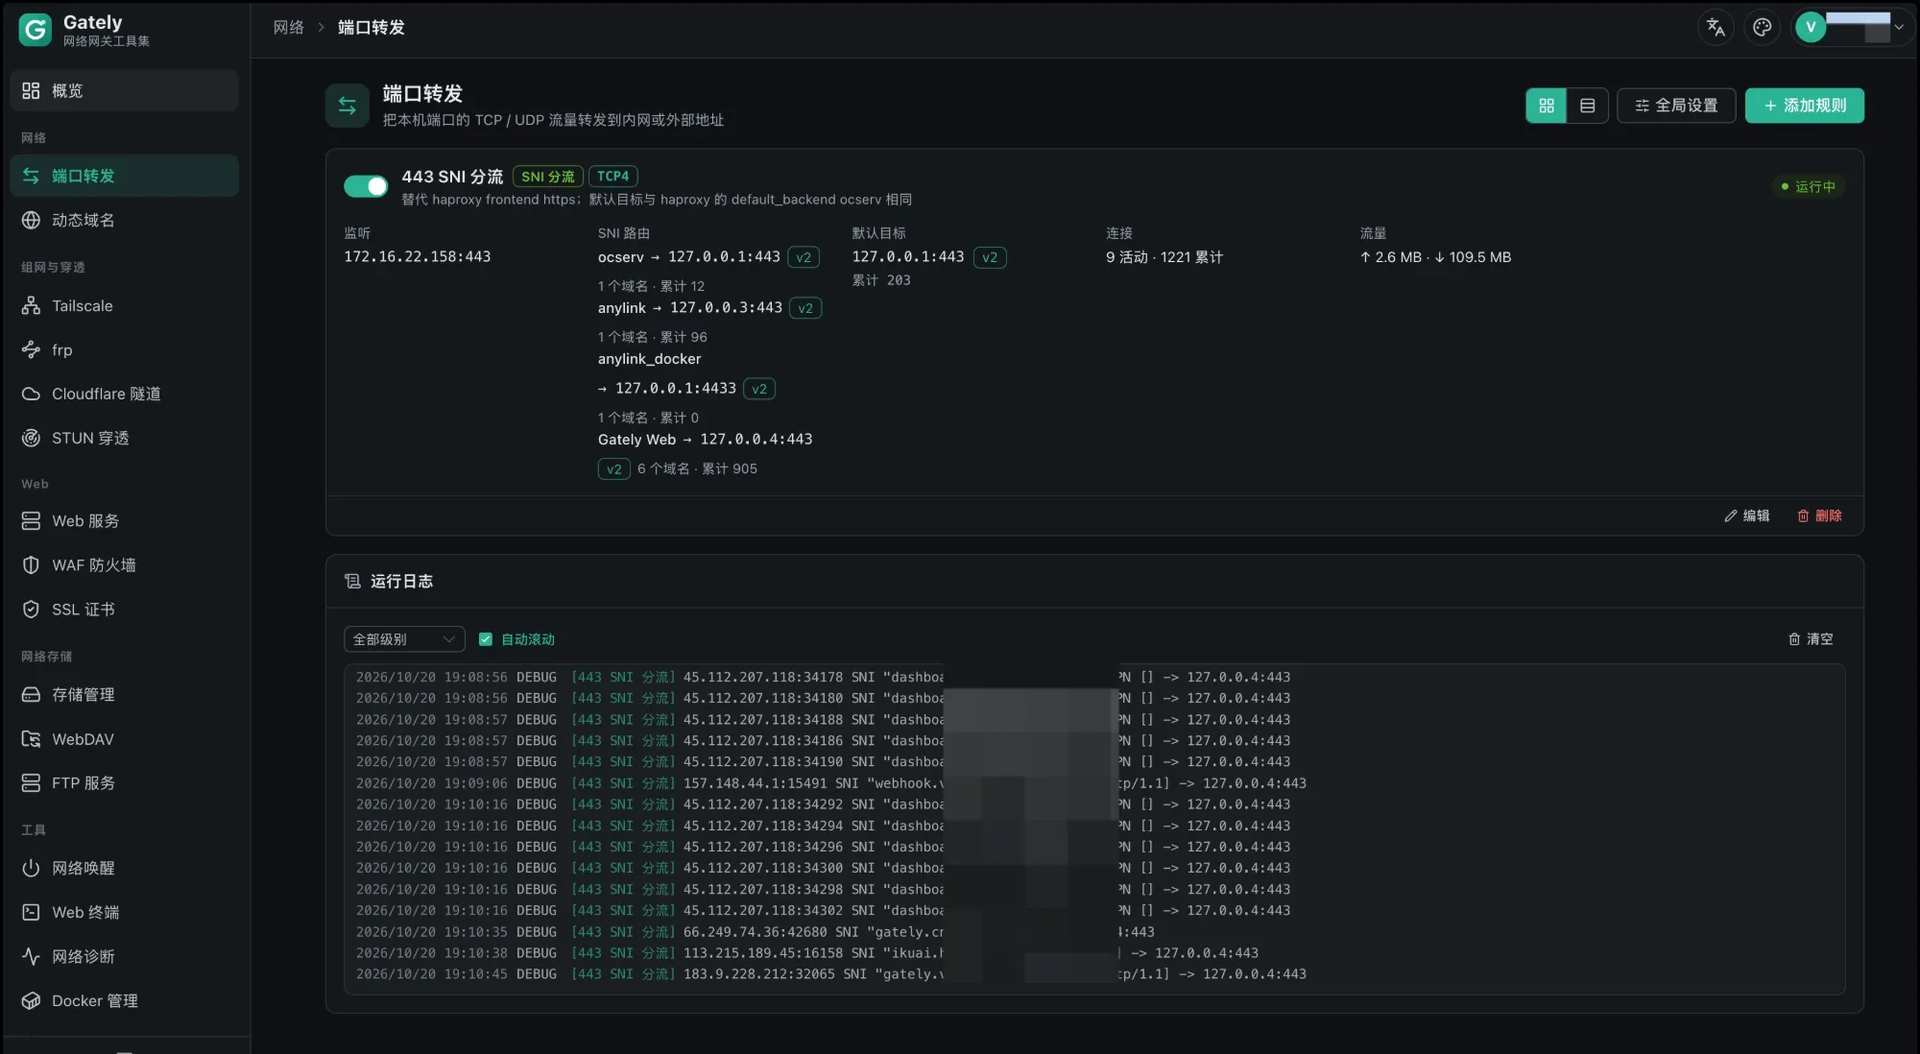
- SNI Port Forwarding
- Relays TCP and UDP with port ranges, failover targets, connection limits, and PROXY protocol v1 or v2, while SNI routing lets several TLS services share port 443.
- Automatic ACME Certificates
- Issues and renews certificates through ACME with DNS-01 wildcards, HTTP-01, or EAB, then pushes them to other hosts over SSH or restarts the Docker containers that use them.
- Reverse Proxy And Sign-In
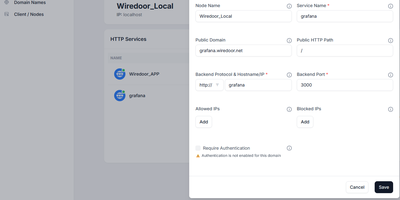
- Per-domain proxies with HTTP/3, WebSocket, weighted load balancing, health checks, and rate limiting, protected by OIDC, GitHub, Google, or TOTP shared users and forward auth to Authelia.
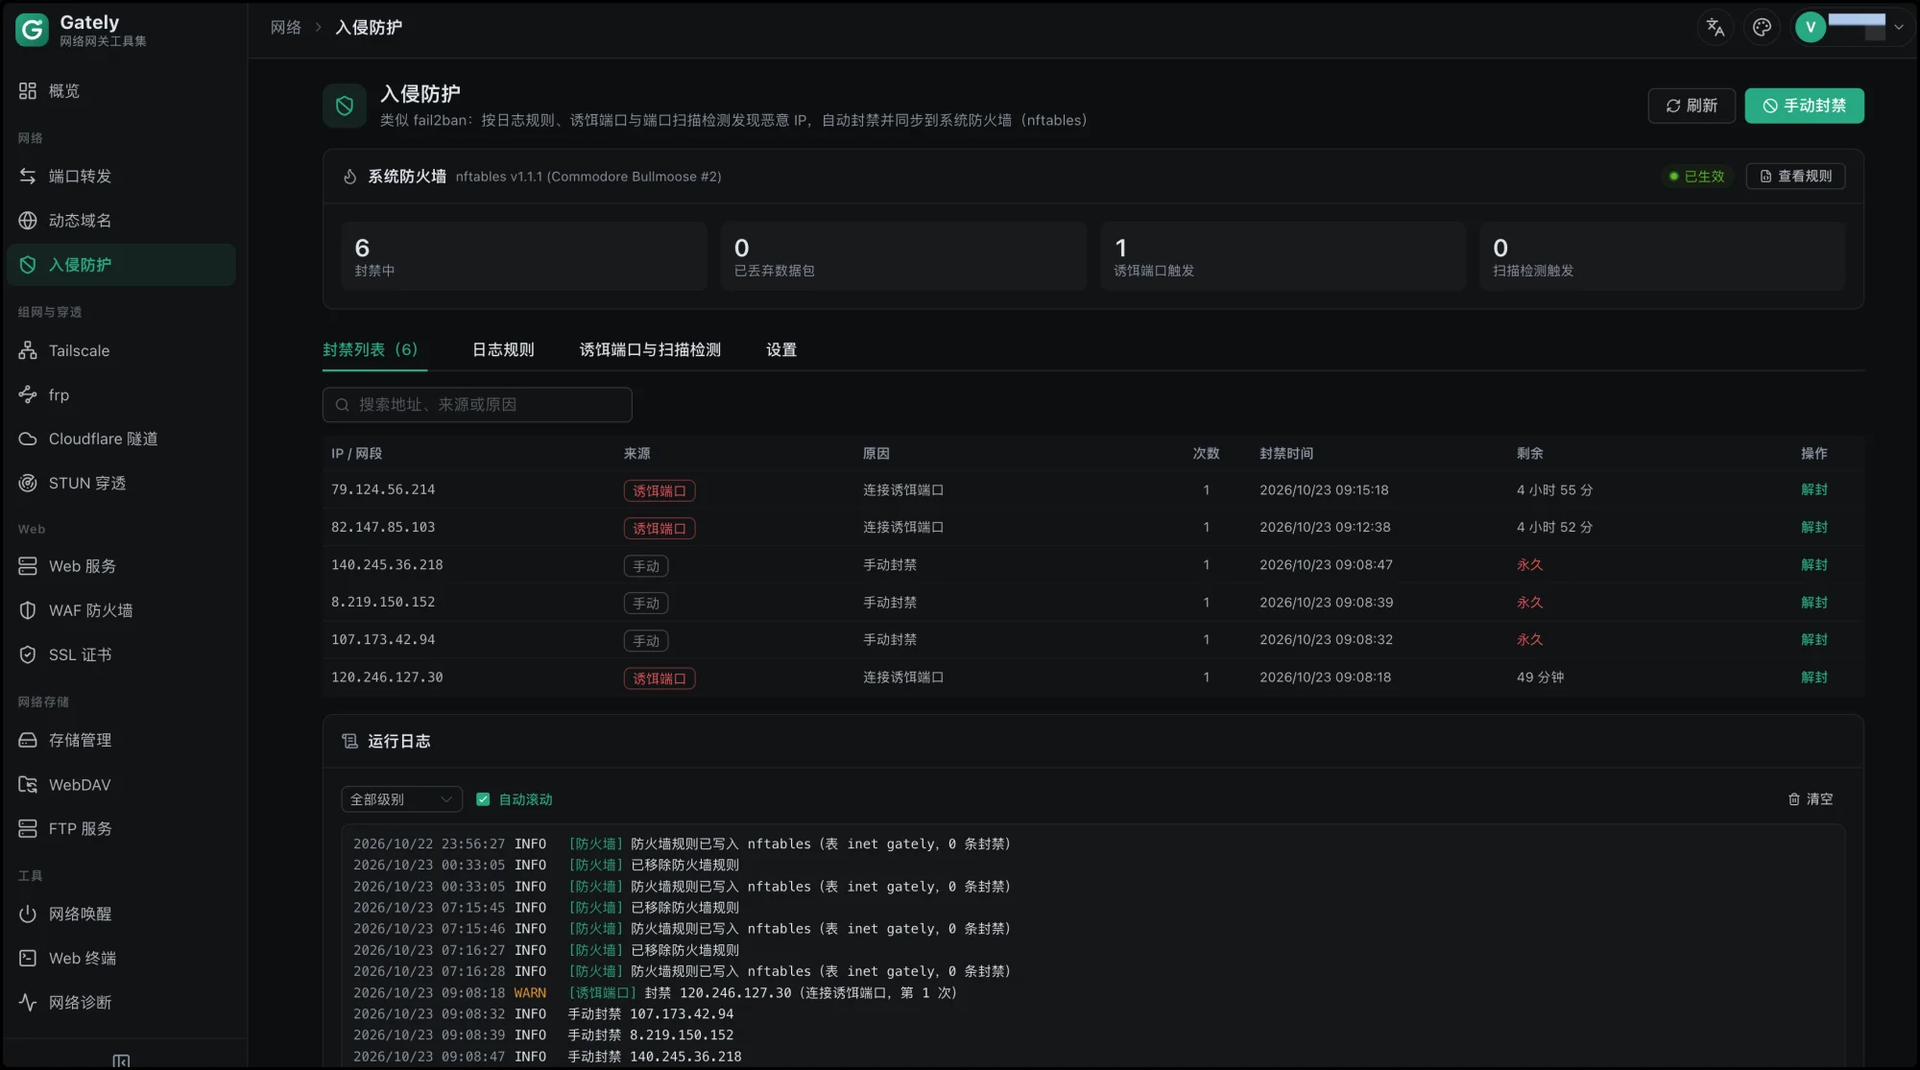
- WAF And Intrusion Prevention
- Coraza with the OWASP Core Rule Set, fail2ban-style log jails for SSH and Nginx, trap ports, and port-scan detection feed bans into nftables.
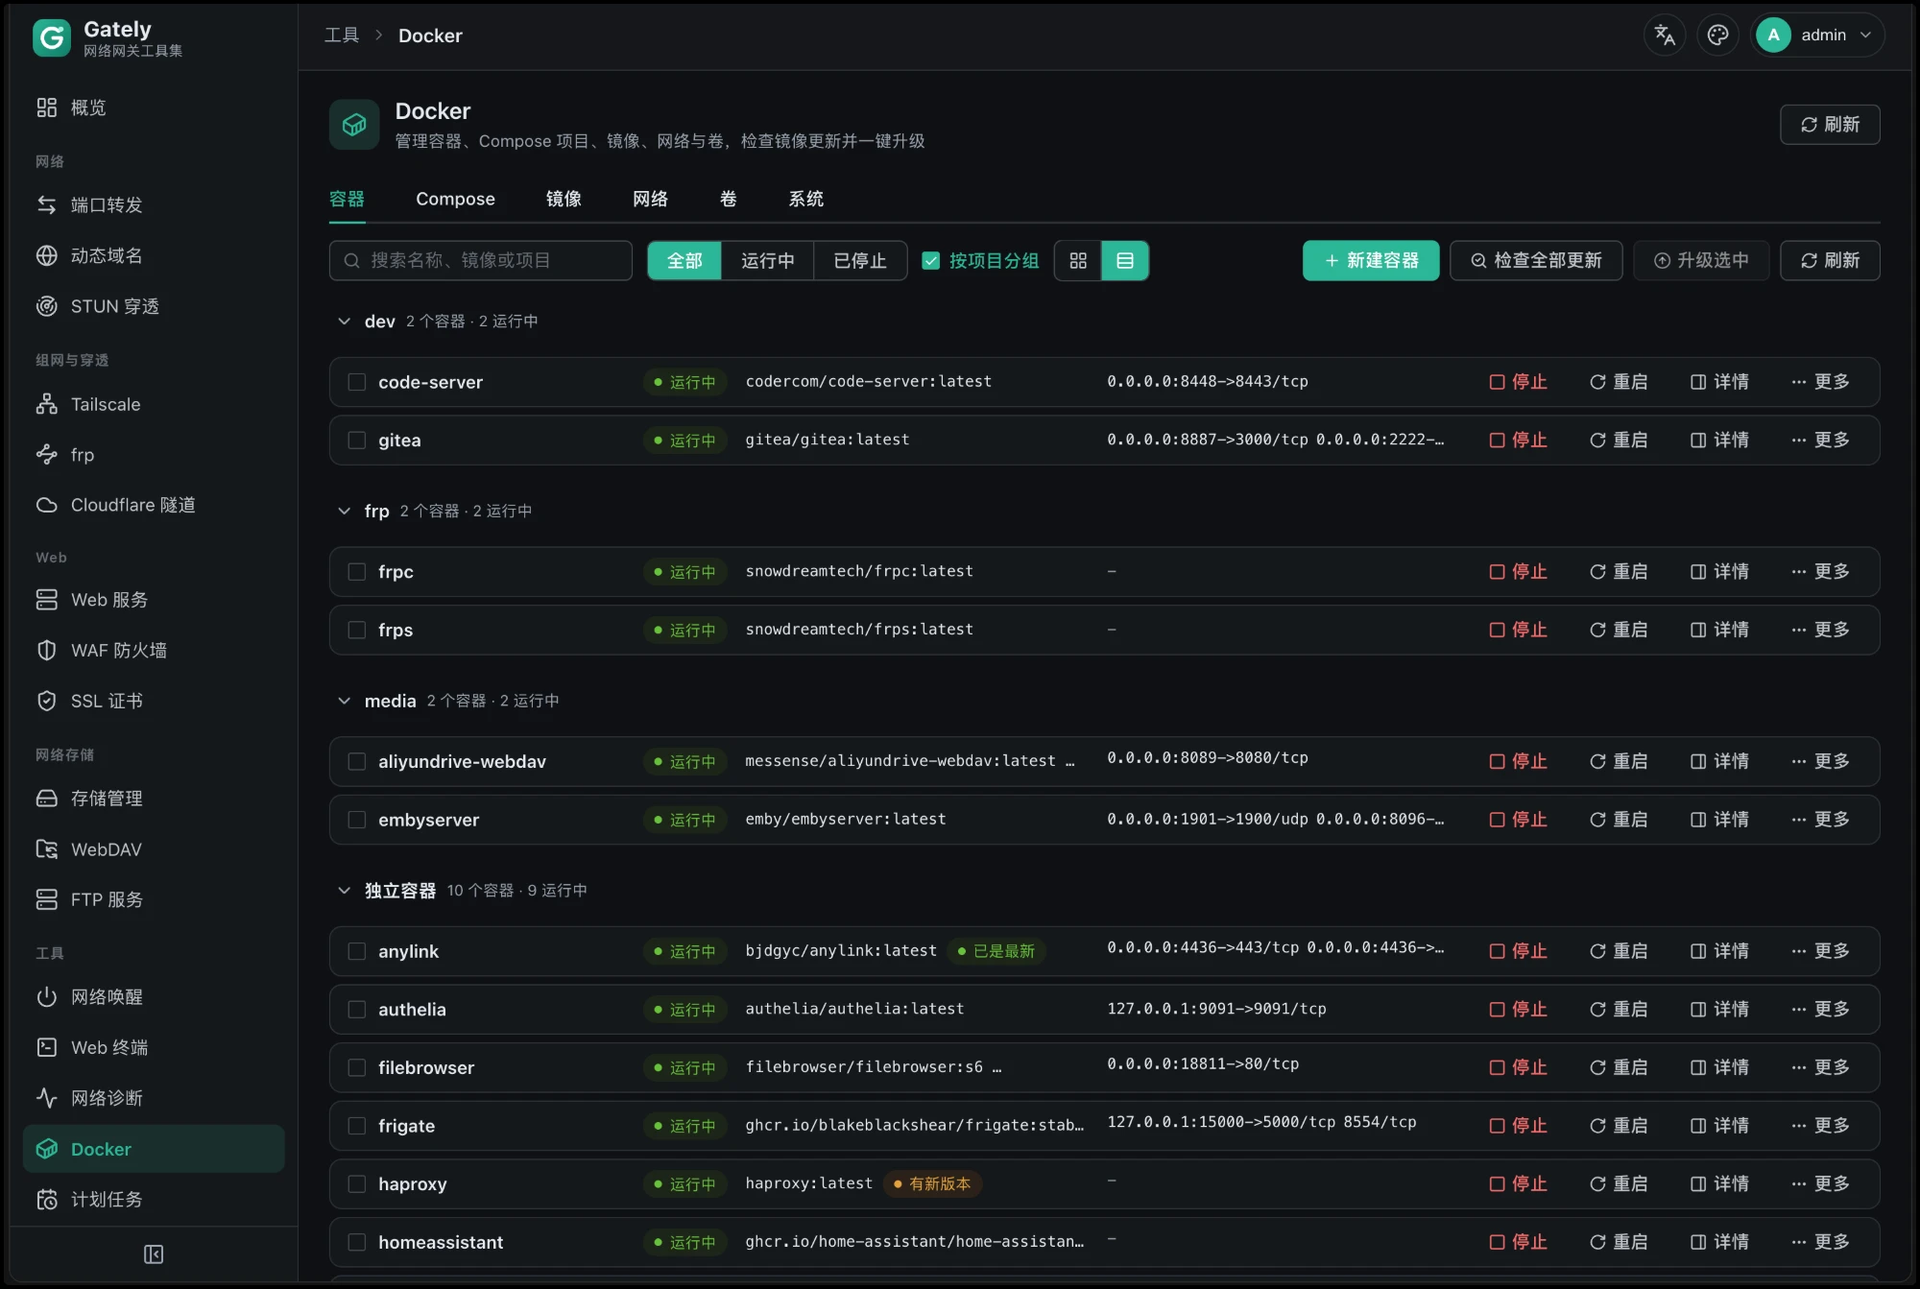
- Docker And Web Terminal
- Manage containers, Compose projects, images, and volumes with one-click upgrades and automatic rollback, plus SSH and Telnet sessions with an SFTP file manager and split panes.