Categories
self-hosted docker zero-trust reverse-proxy cloudflare-tunnel ingress-controller network-automationStars
Forks
Watchers
Developer links
DockFlare
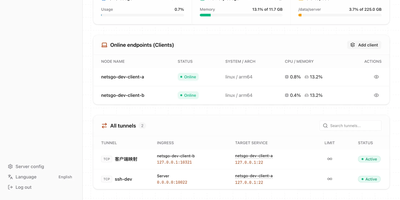
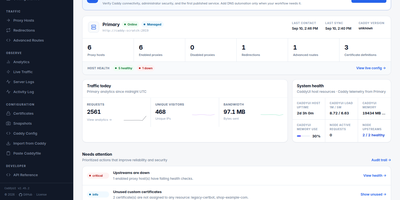
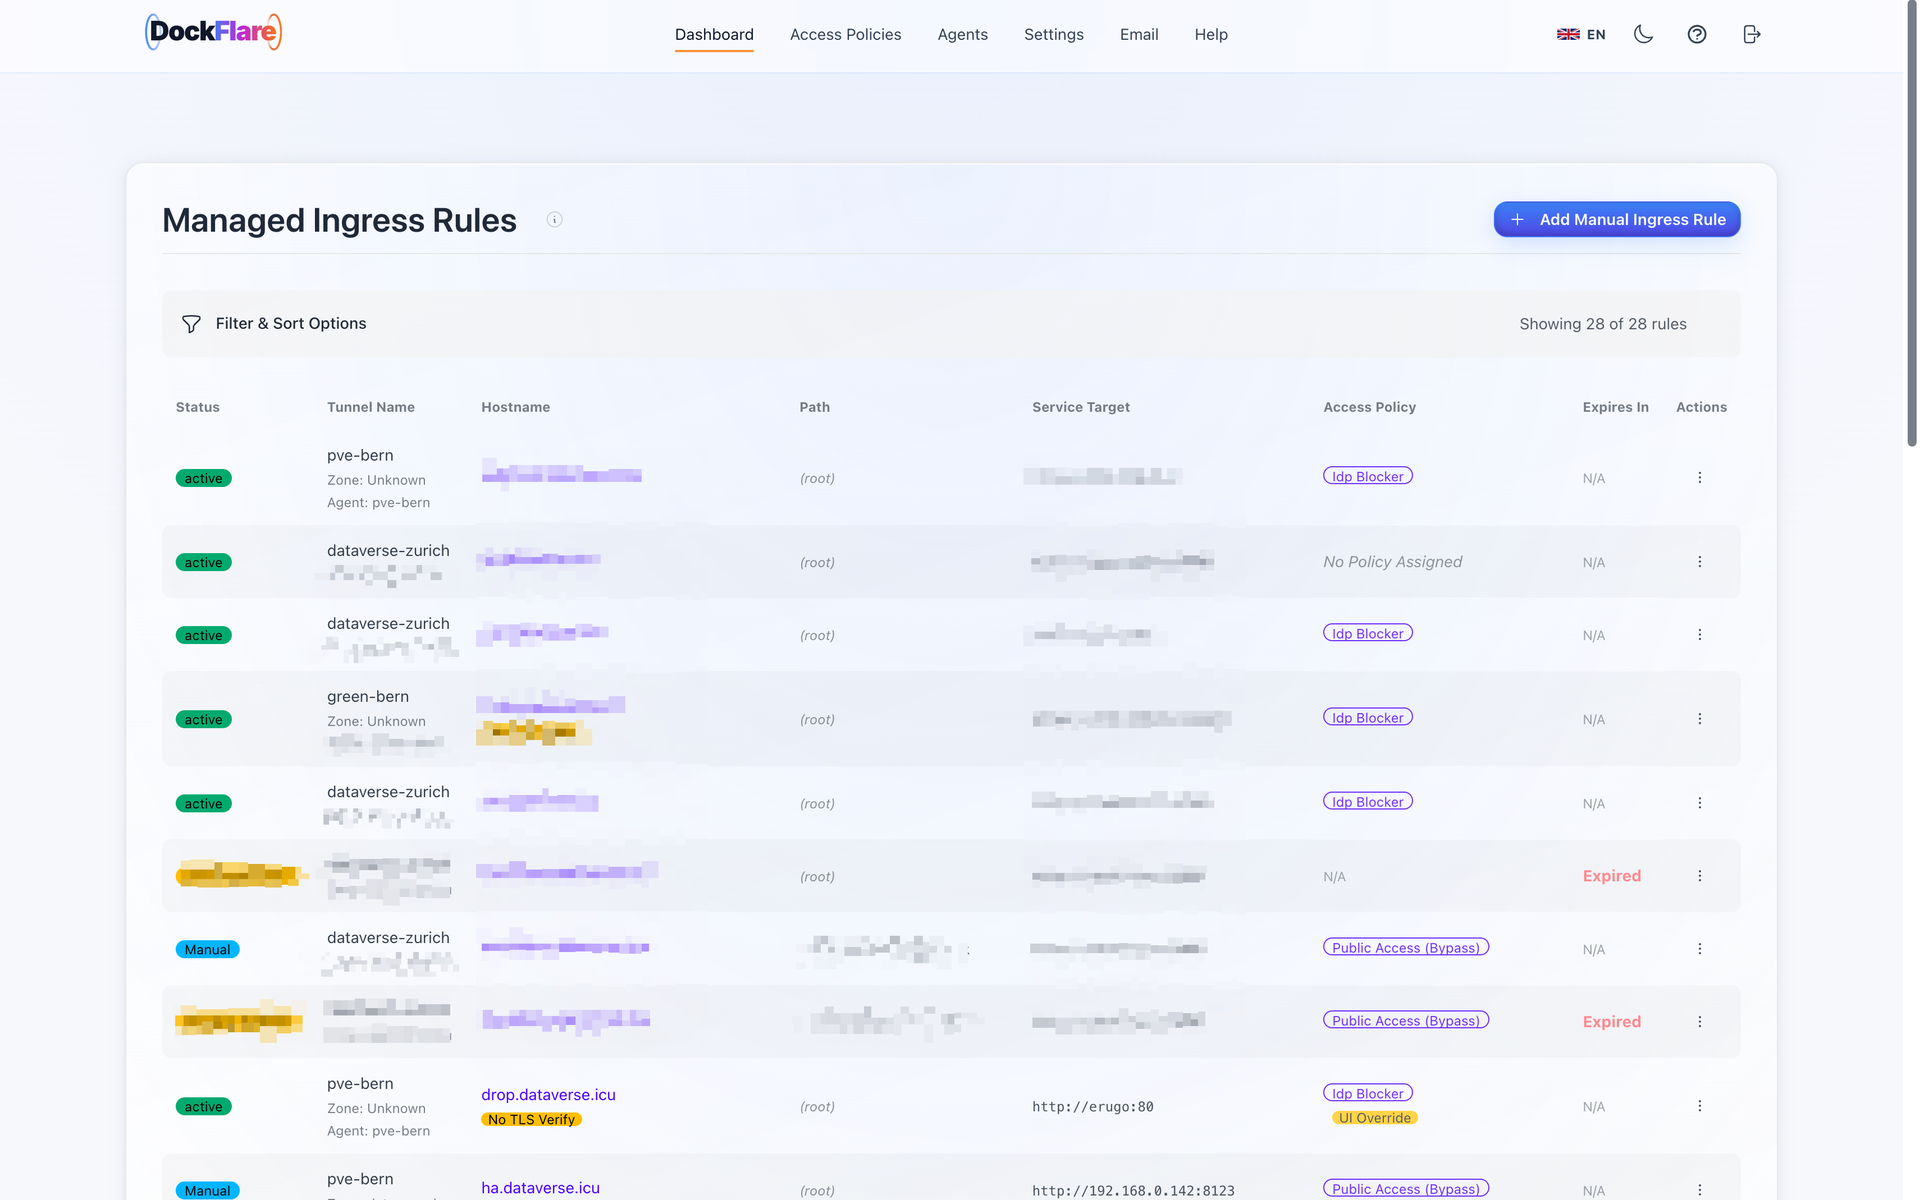
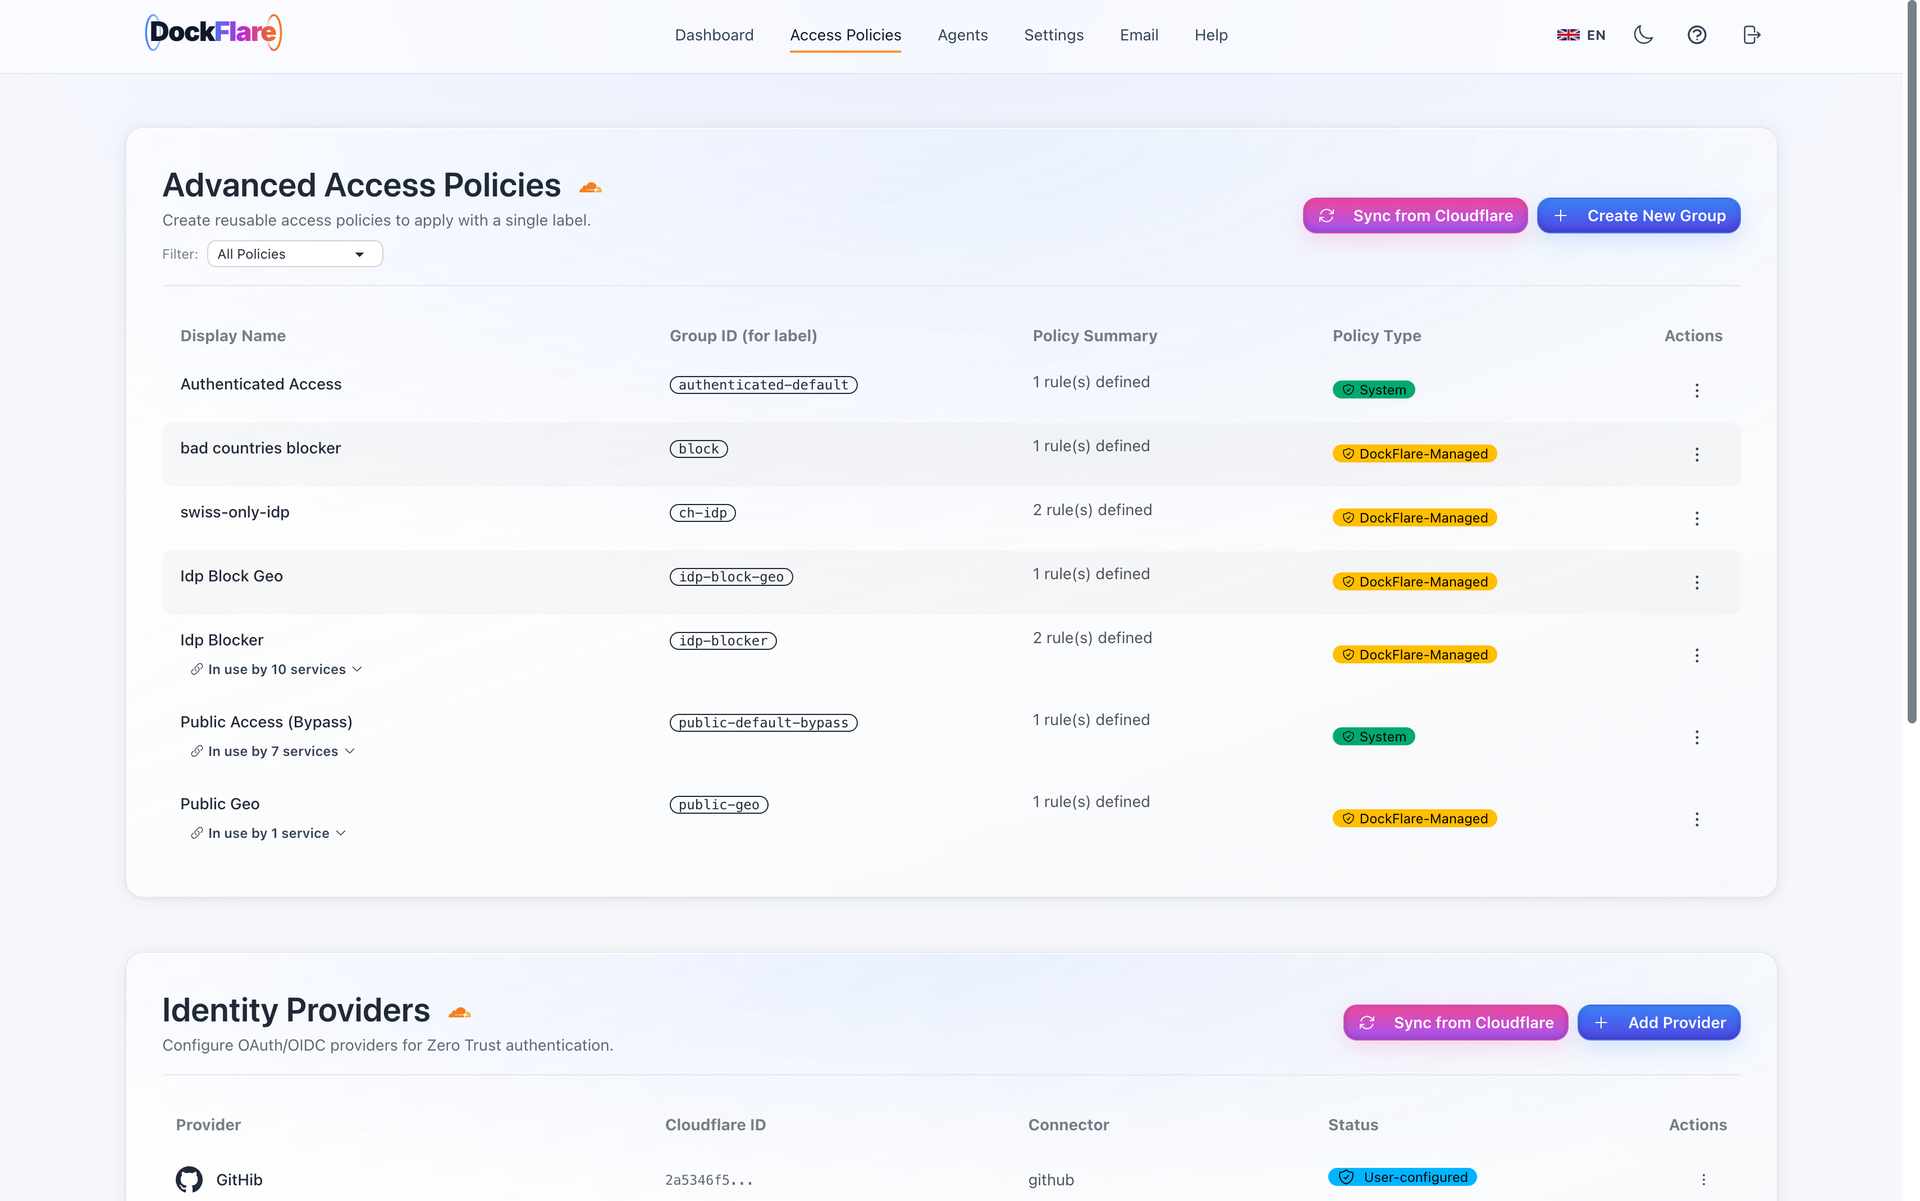
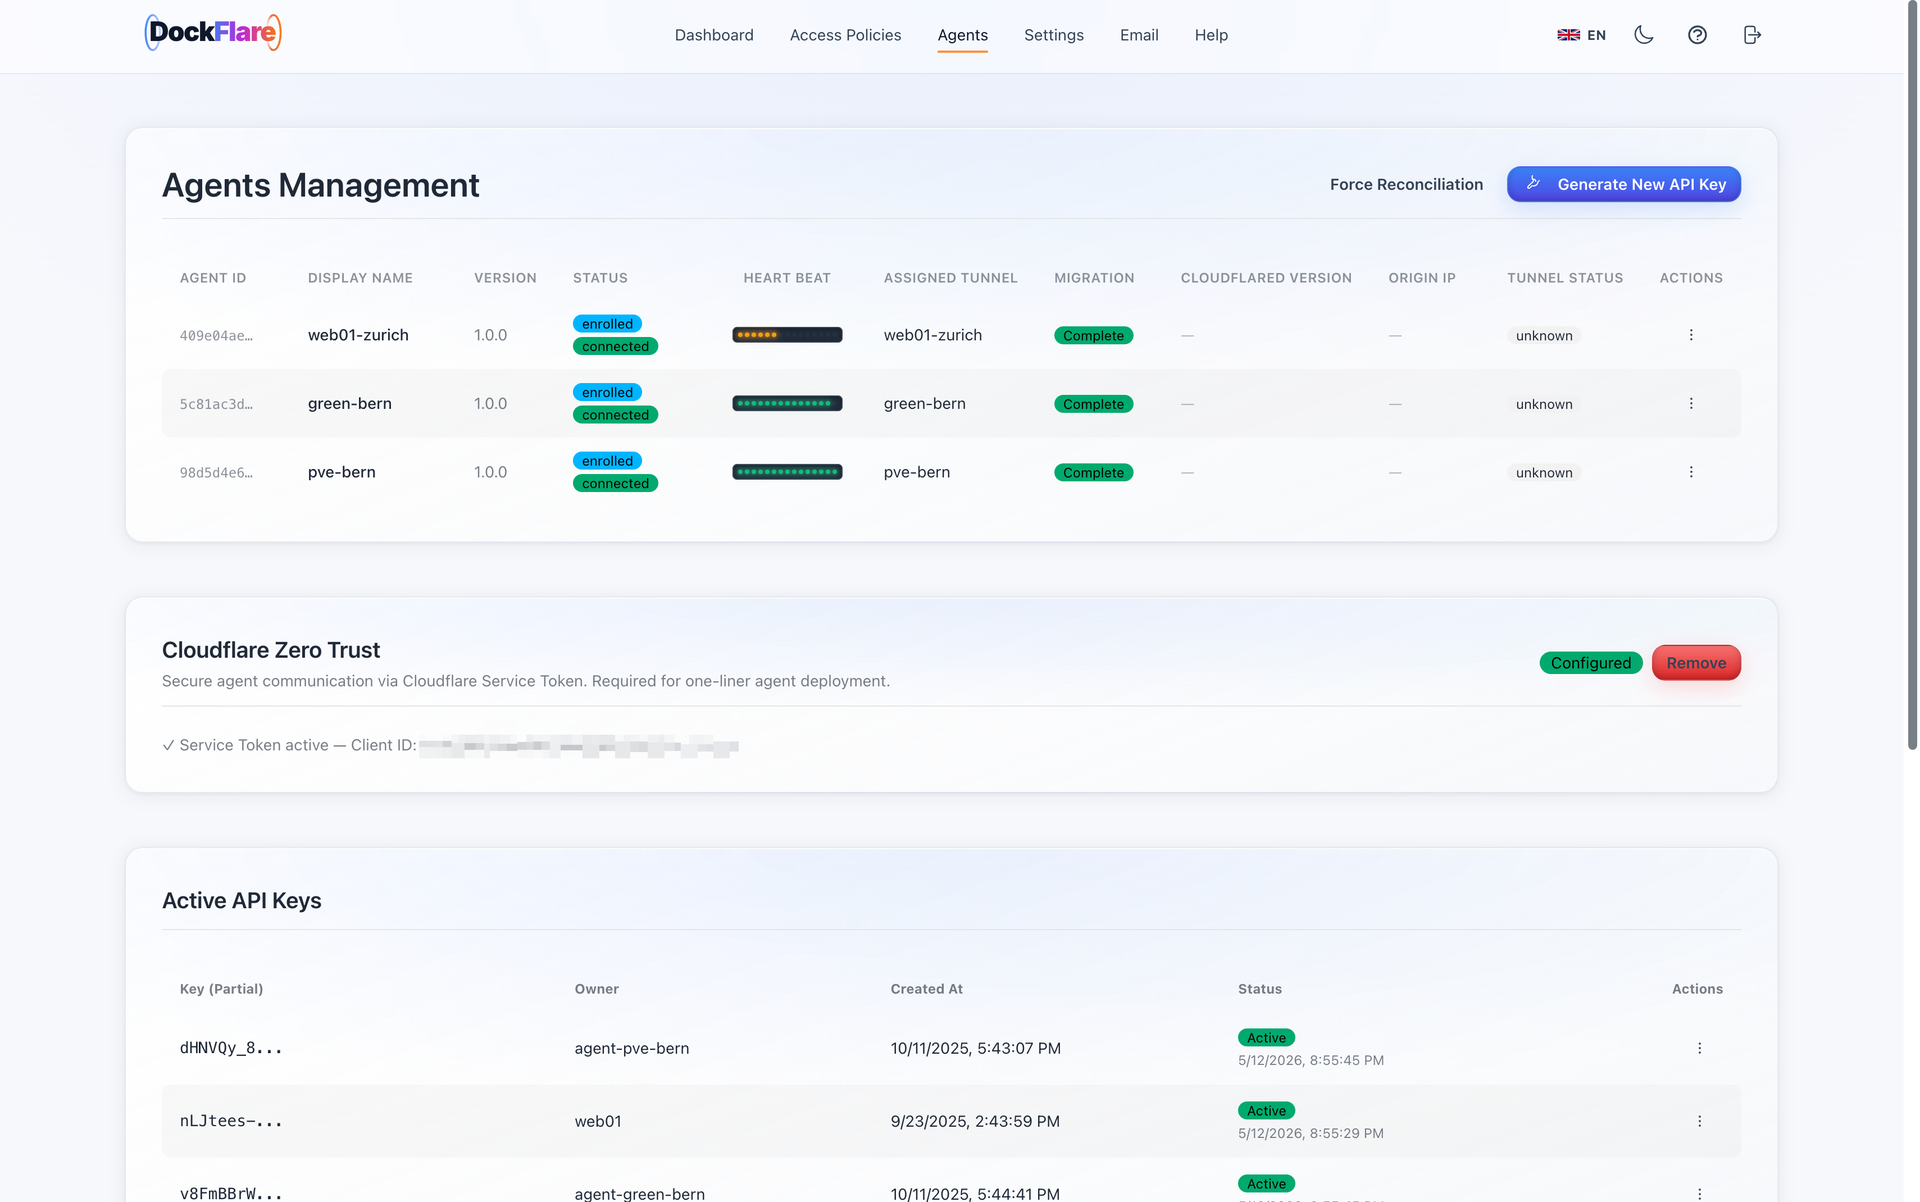
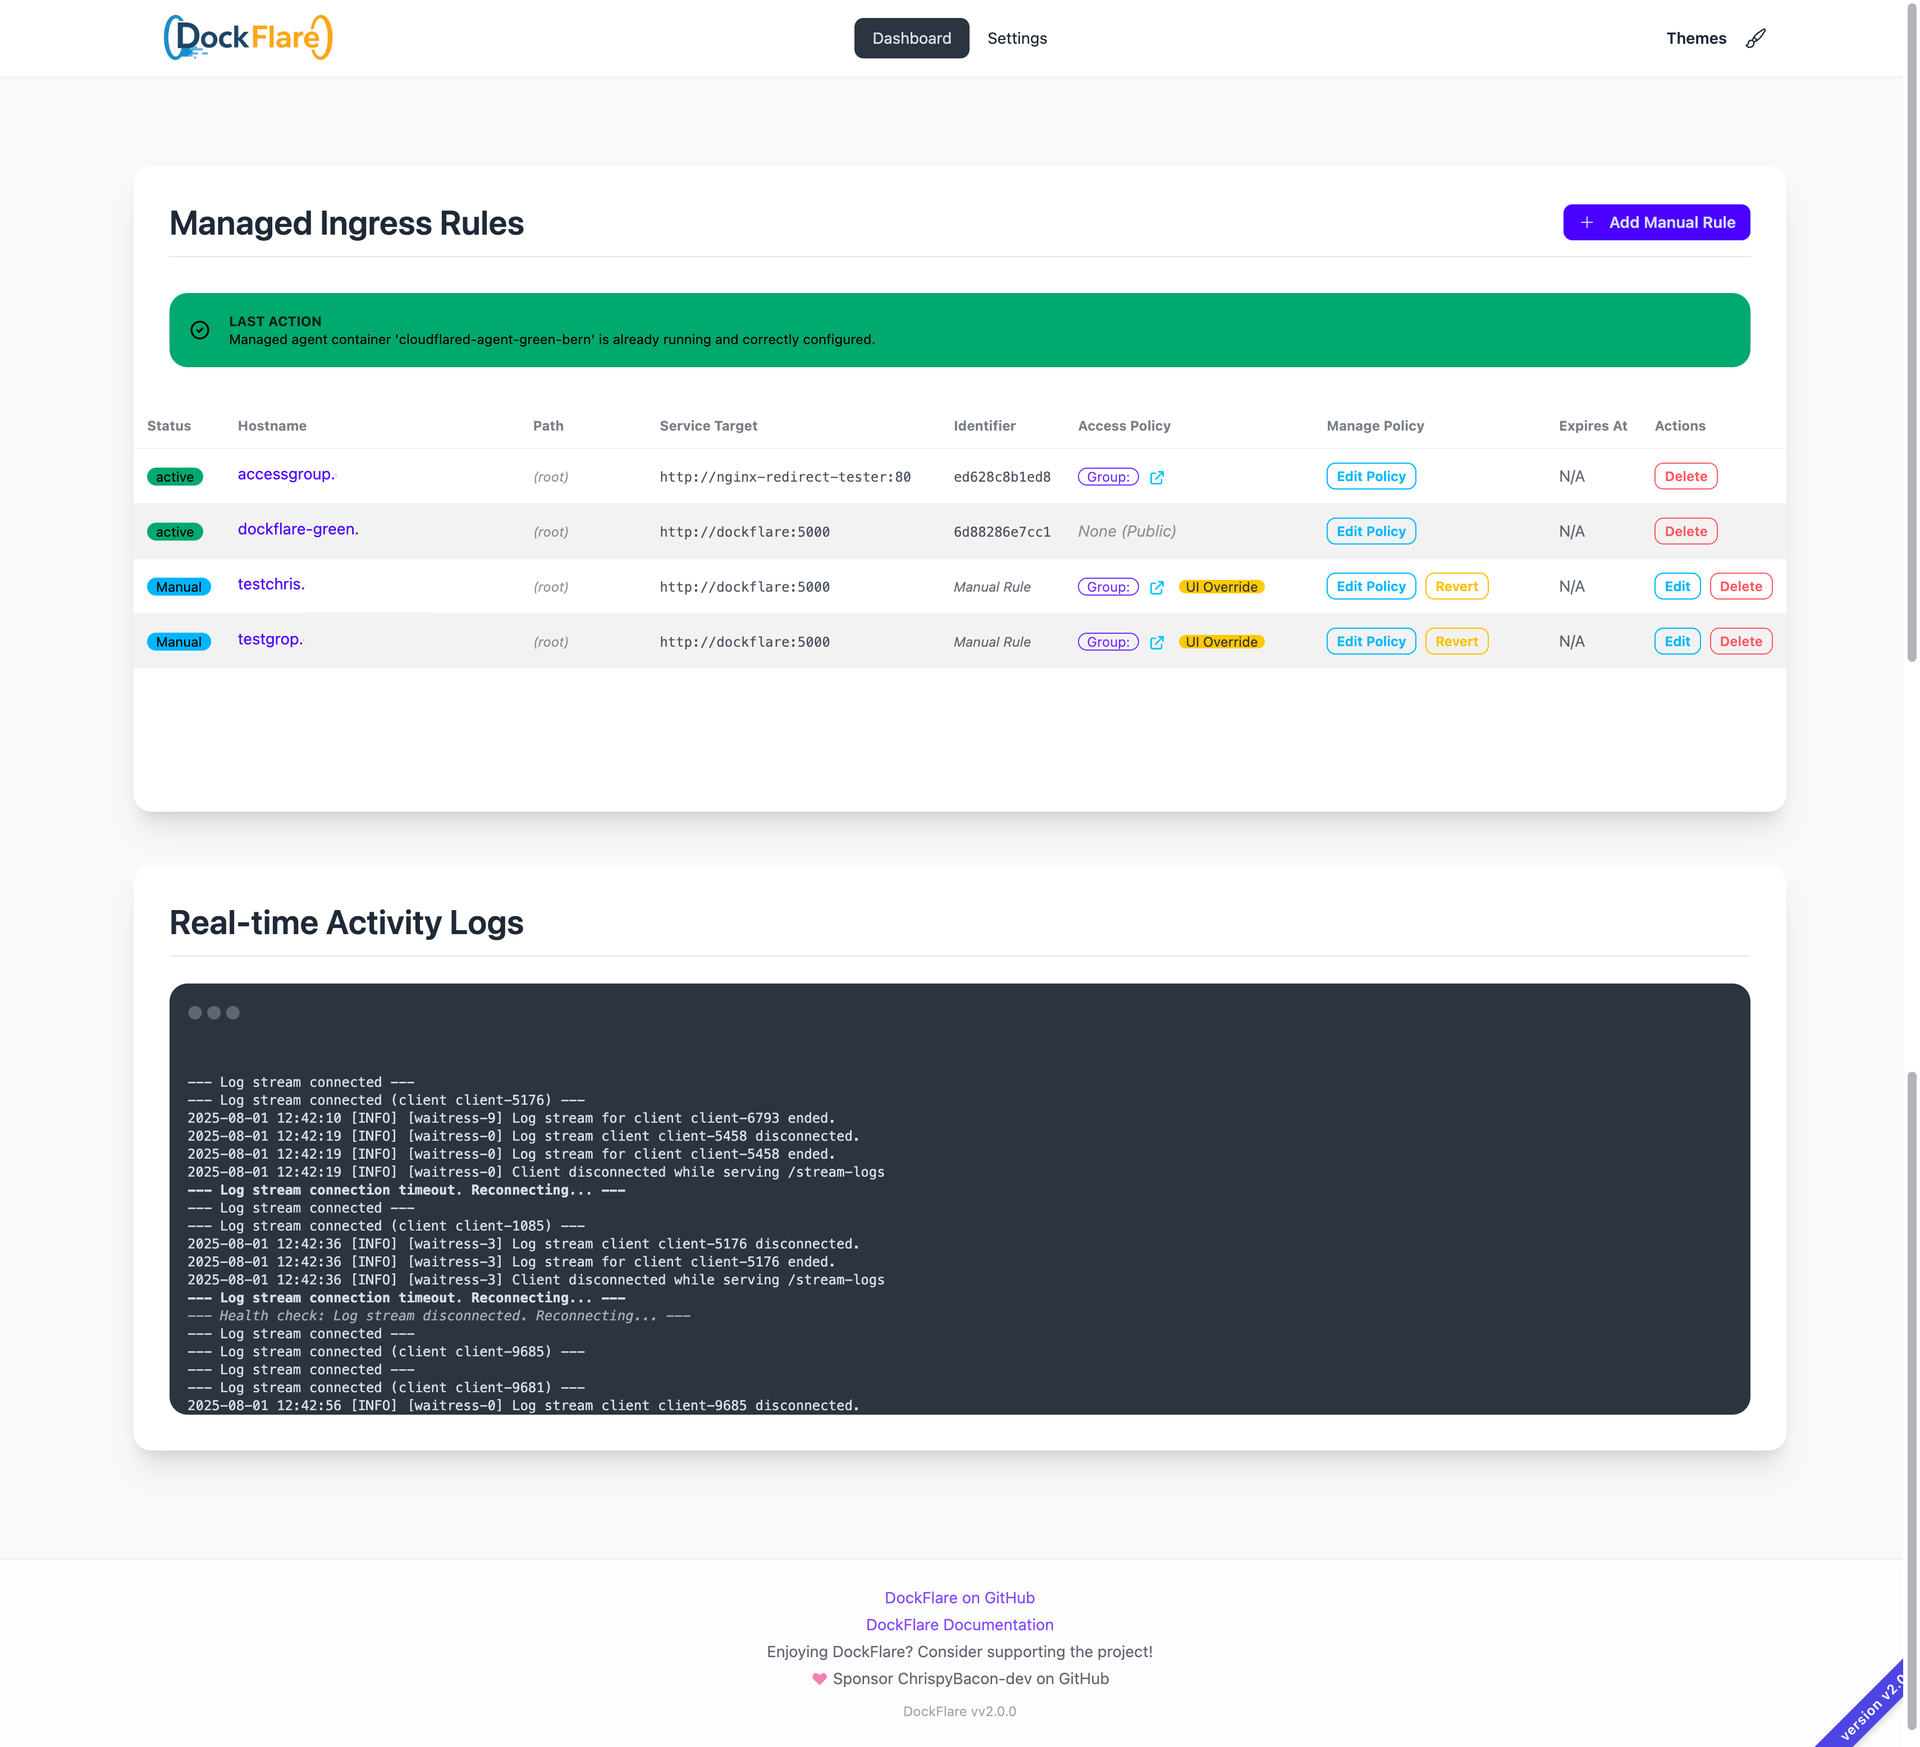
Combining Docker container labels with a live web control plane, DockFlare automates Cloudflare Tunnel ingress routing, multi-zone DNS records, and Zero Trust Access policies across self-hosted infrastructure. DevOps engineers and homelab operators can attach simple container labels to expose HTTP, HTTPS, TCP, SSH, and RDP services publicly in seconds without clicking through external cloud dashboards. For non-containerized workloads such as bare-metal hypervisors or network appliances, administrators can define manual ingress rules, path-based routes, custom TLS SNI headers, and origin certificate bypass flags directly in the web interface. Security teams use reusable Access Groups and wildcard zone policies to enforce Google, GitHub, Azure AD, or custom OIDC authentication across every subdomain from a single policy definition. Distributed deployments connect lightweight remote agents back to the primary controller using Zero Trust service tokens so multi-host clusters share one unified routing view. When containers stop or restart, configurable grace-period timers prevent accidental route churn before cleaning up stale DNS entries, while encrypted state backups protect your entire ingress configuration. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
Benefits
- Label-Driven Cloudflare Tunnel Automation
- Watches Docker container start and stop events in real time to provision Cloudflare Tunnel ingress routes and multi-zone CNAME records from declarative container labels with zero manual dashboard steps.
- Unified Zero Trust Policy Management
- Creates and reconciles Cloudflare Access applications, reusable Access Groups, wildcard TLD policies, and identity provider rules for Google, GitHub, Azure AD, and OIDC directly from labels or the web UI.
- Hybrid Docker and Non-Docker Routing
- Combines automated container discovery with persistent Web UI manual rules for bare-metal hosts, supporting HTTP, HTTPS, TCP, SSH, and RDP origins with custom SNI and TLS verification controls.
- Multi-Host Agent Orchestration and Backups
- Coordinates remote Docker hosts through lightweight DockFlare agents secured by Cloudflare Zero Trust service tokens while safeguarding runtime state with encrypted backup archives and graceful deletion timers.
Features
- Declarative Container Labels
- Reads dockflare.hostname, dockflare.service, dockflare.path, and dockflare.zonename labels to configure public endpoints and path-based routing across multiple Cloudflare DNS zones automatically.
- Reusable Zero Trust Groups
- Defines centralized Access Groups with session durations, launcher visibility, and identity provider restrictions that apply across multiple containers using a single label reference.
- Managed Cloudflared Reconciliation
- Inspects and manages the local cloudflared tunnel agent container automatically on startup, verifying network bindings, tunnel tokens, and desired ingress state stored in state.json.
- Multi-Host Remote Agents
- Deploys lightweight dockflare-agent containers on secondary servers that authenticate to the master controller via Cloudflare Zero Trust service tokens for centralized multi-node ingress management.
- Graceful Cleanup and Backups
- Applies configurable grace periods when containers stop to prevent route flapping during restarts, paired with encrypted configuration and state backup and restore tools.