Stars
Forks
Watchers
Developer links
Warpgate
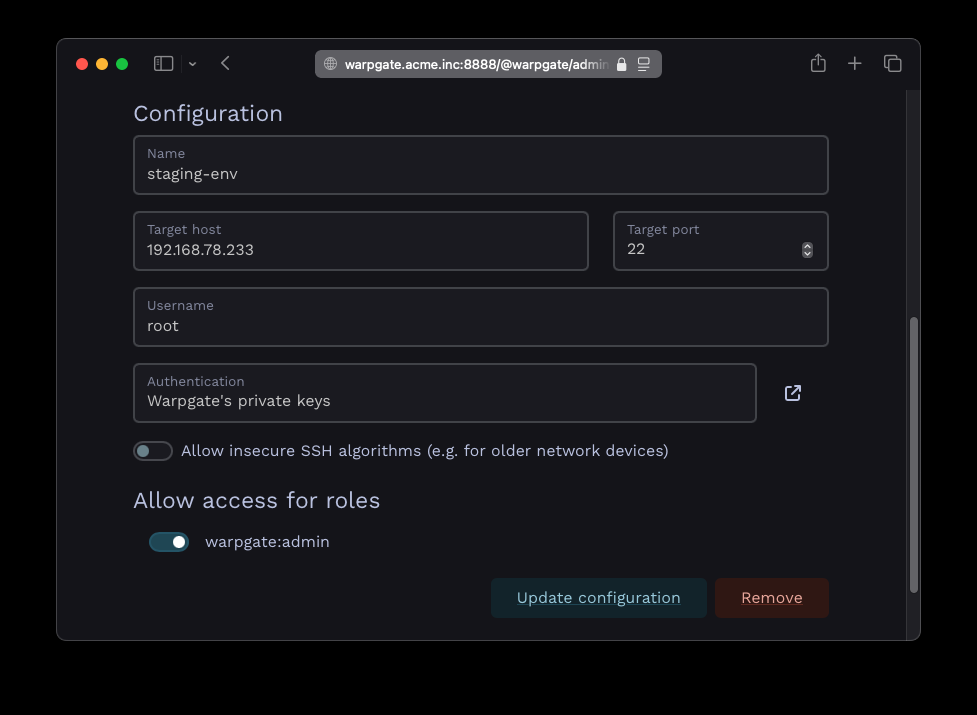
Warpgate is a clientless bastion host and privileged access management gateway that lets engineering teams secure, assign, and audit access to internal SSH servers, databases, Kubernetes clusters, web applications, and remote desktops from a single portal without installing VPN clients. Connect directly from standard tools like OpenSSH, VS Code Remote, psql, mysql, kubectl, or native RDP clients using formatted credentials, or launch browser-based SSH terminals, RDP desktops, and VNC sessions straight from the web interface. Administrators map users and roles to specific internal targets with granular 1:1 permissions, enforcing multi-factor authentication via TOTP and Single Sign-On through OpenID Connect providers like Google Workspace, Microsoft Entra ID, and Okta with automatic group-to-role provisioning. Every interactive terminal command, database query, HTTP request, and remote desktop session is captured in real time so security auditors can watch active connections live or replay historical recordings on demand from the web dashboard. Built-in brute-force defense automatically blocks suspicious IP addresses and locks compromised accounts, while temporary access tickets, just-in-time session approvals, encrypted credential storage, and S3-compatible recording archival support enterprise compliance workflows across multi-node clusters. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- Zero Client Software or Wrappers Required
- Engineers connect using unmodified native clients including OpenSSH, VS Code, DataGrip, psql, mysql, and kubectl without installing custom CLI wrappers, browser extensions, or systemic VPN daemons on workstations.
- Live Session Recording and Audit Replay
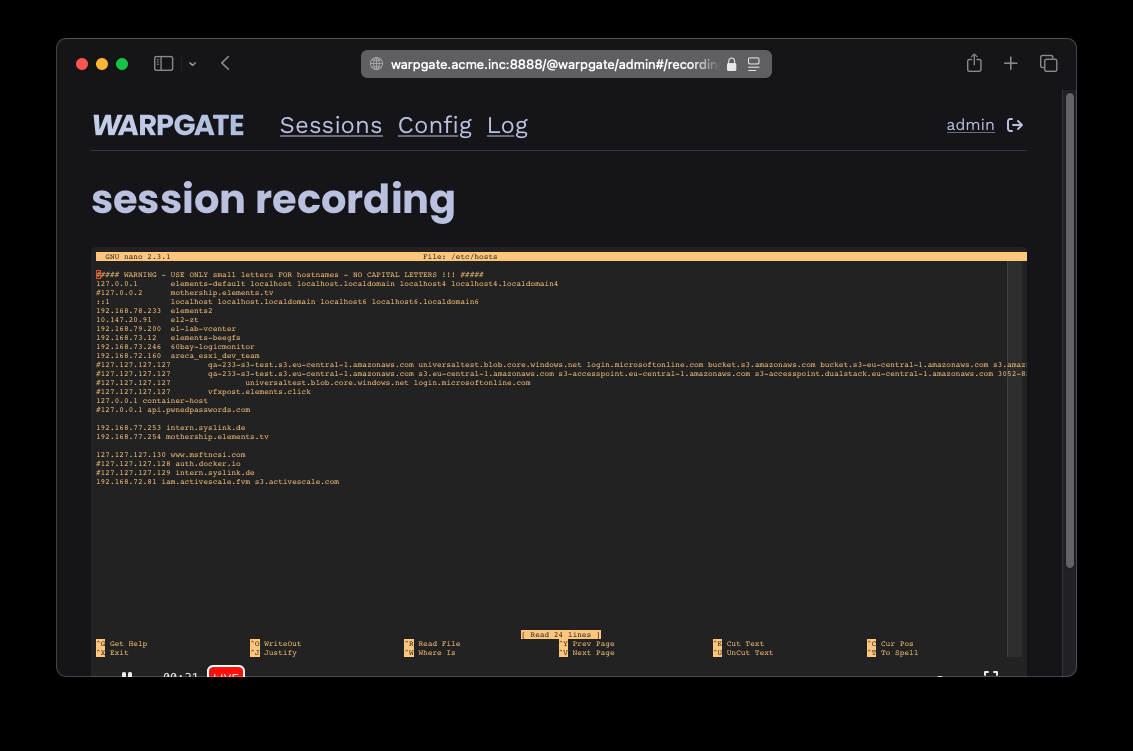
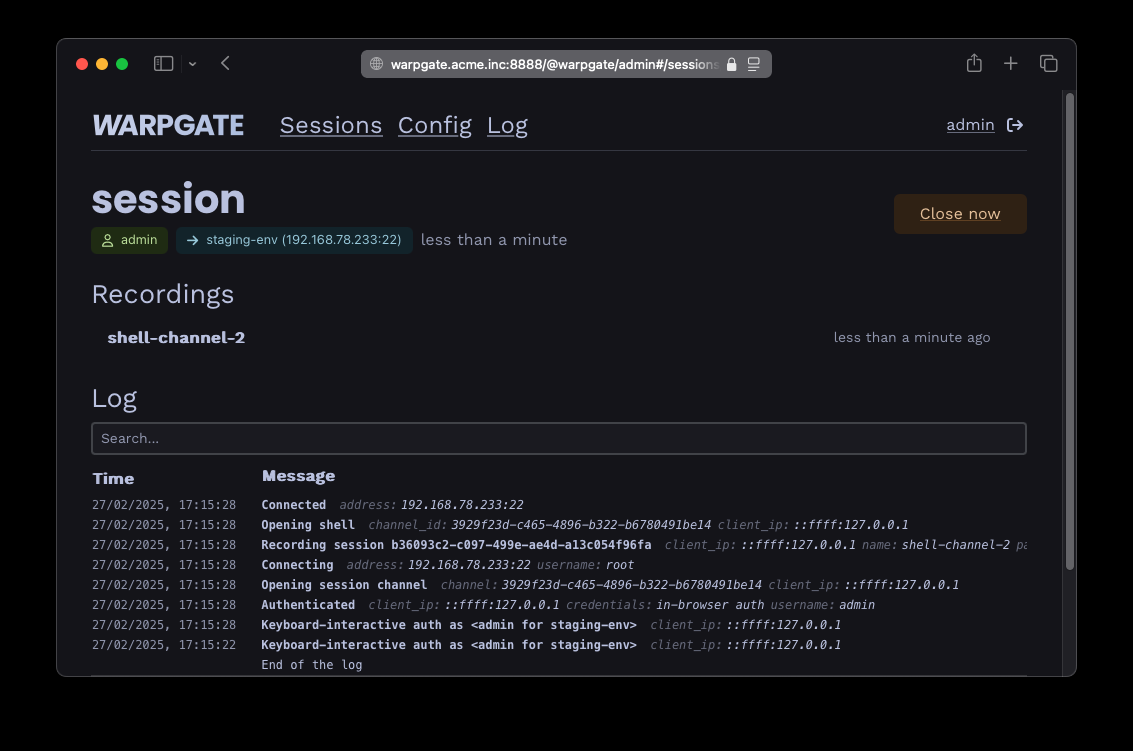
- Captures interactive SSH terminal streams, RDP and VNC desktop video, Kubernetes API calls, and database traffic in real time for live monitoring and on-demand compliance playback in the browser.
- Unified Multi-Protocol Infrastructure Access Control
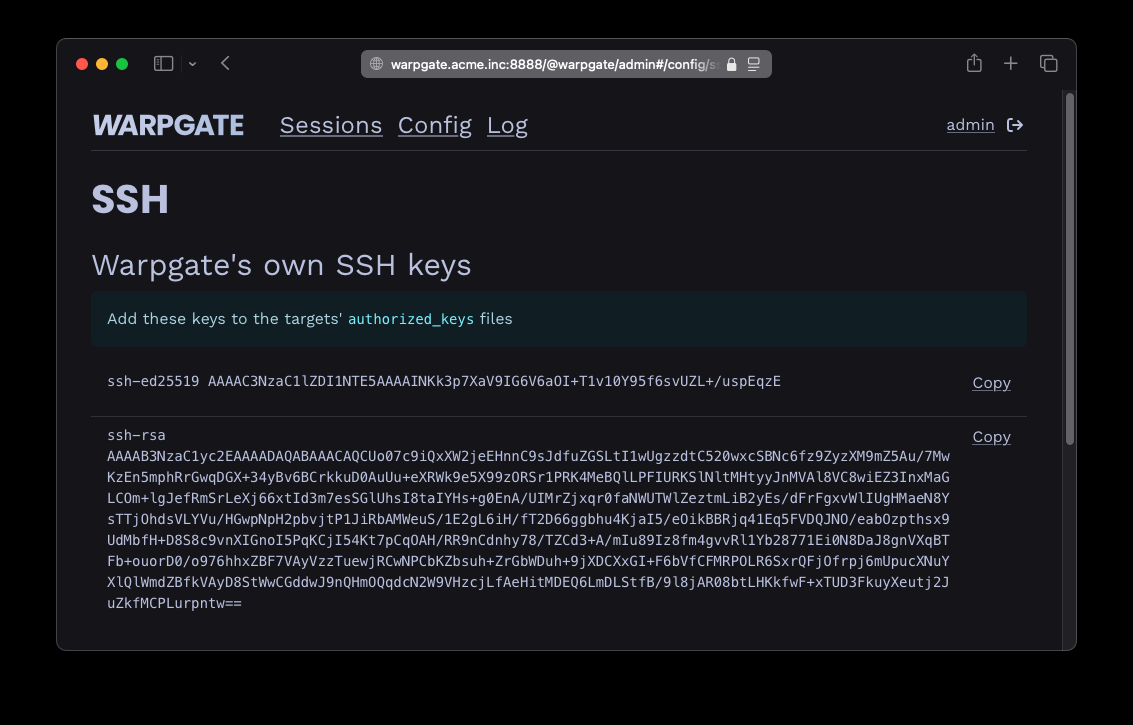
- Consolidates access policies across SSH, HTTPS, Kubernetes, MySQL, PostgreSQL, RDP, and VNC targets in one gateway, replacing scattered authorized_keys files and network-wide VPN tunnels with 1:1 target assignments.
- Identity Provider SSO and Brute-Force Defense
- Integrates with OpenID Connect identity providers for automated group-to-role mapping alongside built-in TOTP multi-factor enforcement, automated IP rate limiting, account lockouts, and temporary single-use access tickets.
Features
- Multi-Protocol Bastion Proxy
- Exposes native protocol listeners that transparently proxy SSH, HTTPS, Kubernetes API, MySQL, PostgreSQL, RDP, and VNC connections directly to internal hosts.
- Browser Terminal and Desktop
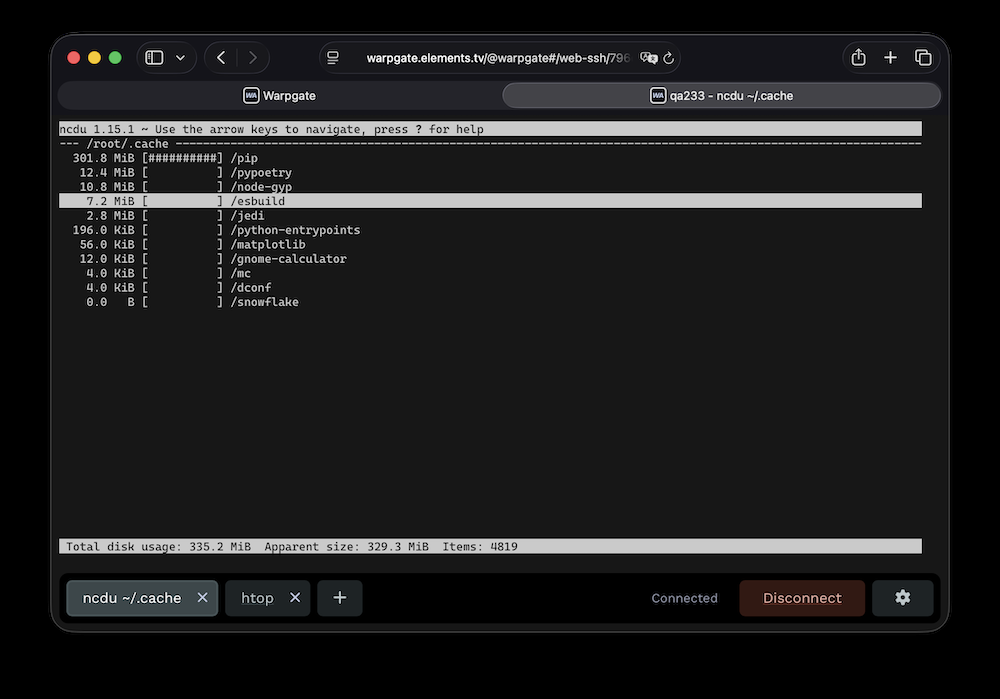
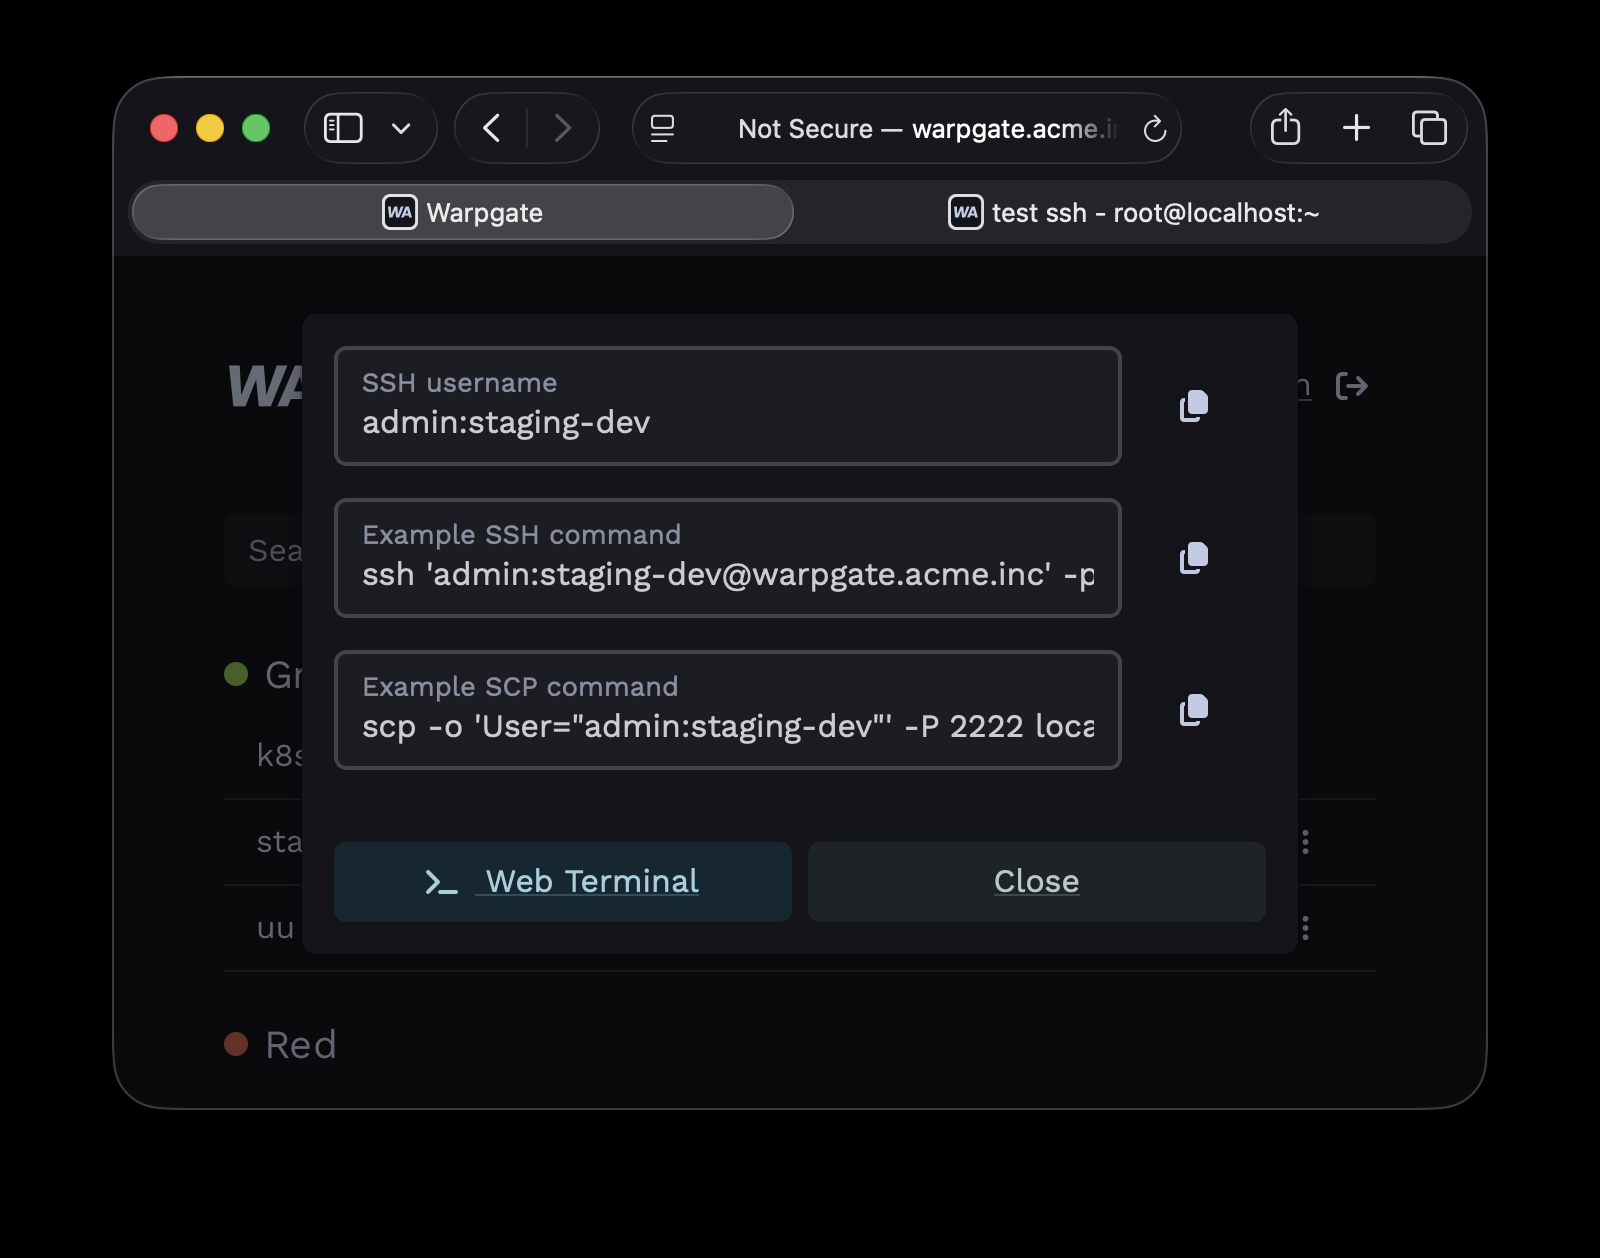
- Provides an integrated HTML5 web portal with instant browser-based SSH terminal access, RDP desktop streaming, VNC viewing, and copy-paste connection snippets.
- OIDC Single Sign-On
- Authenticates users through OpenID Connect providers including Google, Microsoft Azure AD, Apple, and custom OIDC servers with automatic user provisioning and role synchronization.
- Real-Time Session Recorder
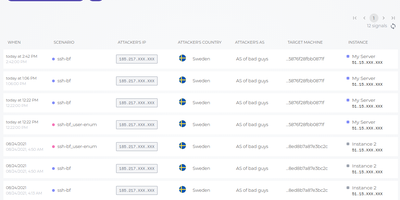
- Records terminal keystrokes, output streams, and remote desktop sessions to local storage or S3-compatible object buckets for live viewing and historical audit replay.
- Just-In-Time Access Tickets
- Issues time-bound, credential-free access tickets and enforces just-in-time session approval workflows alongside TOTP two-factor authentication and AWS IAM role integration.