Stars
Forks
Watchers
Developer links
Containarium
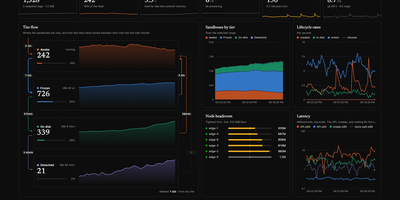
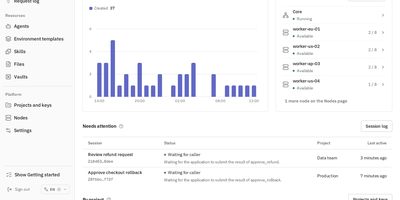
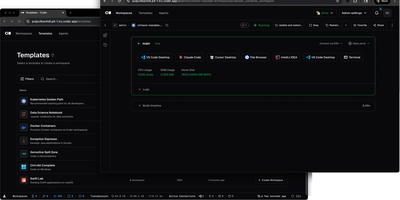
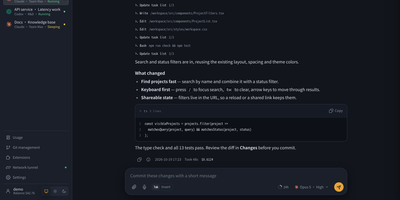
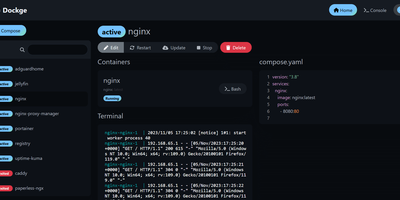
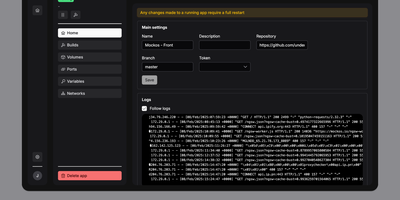
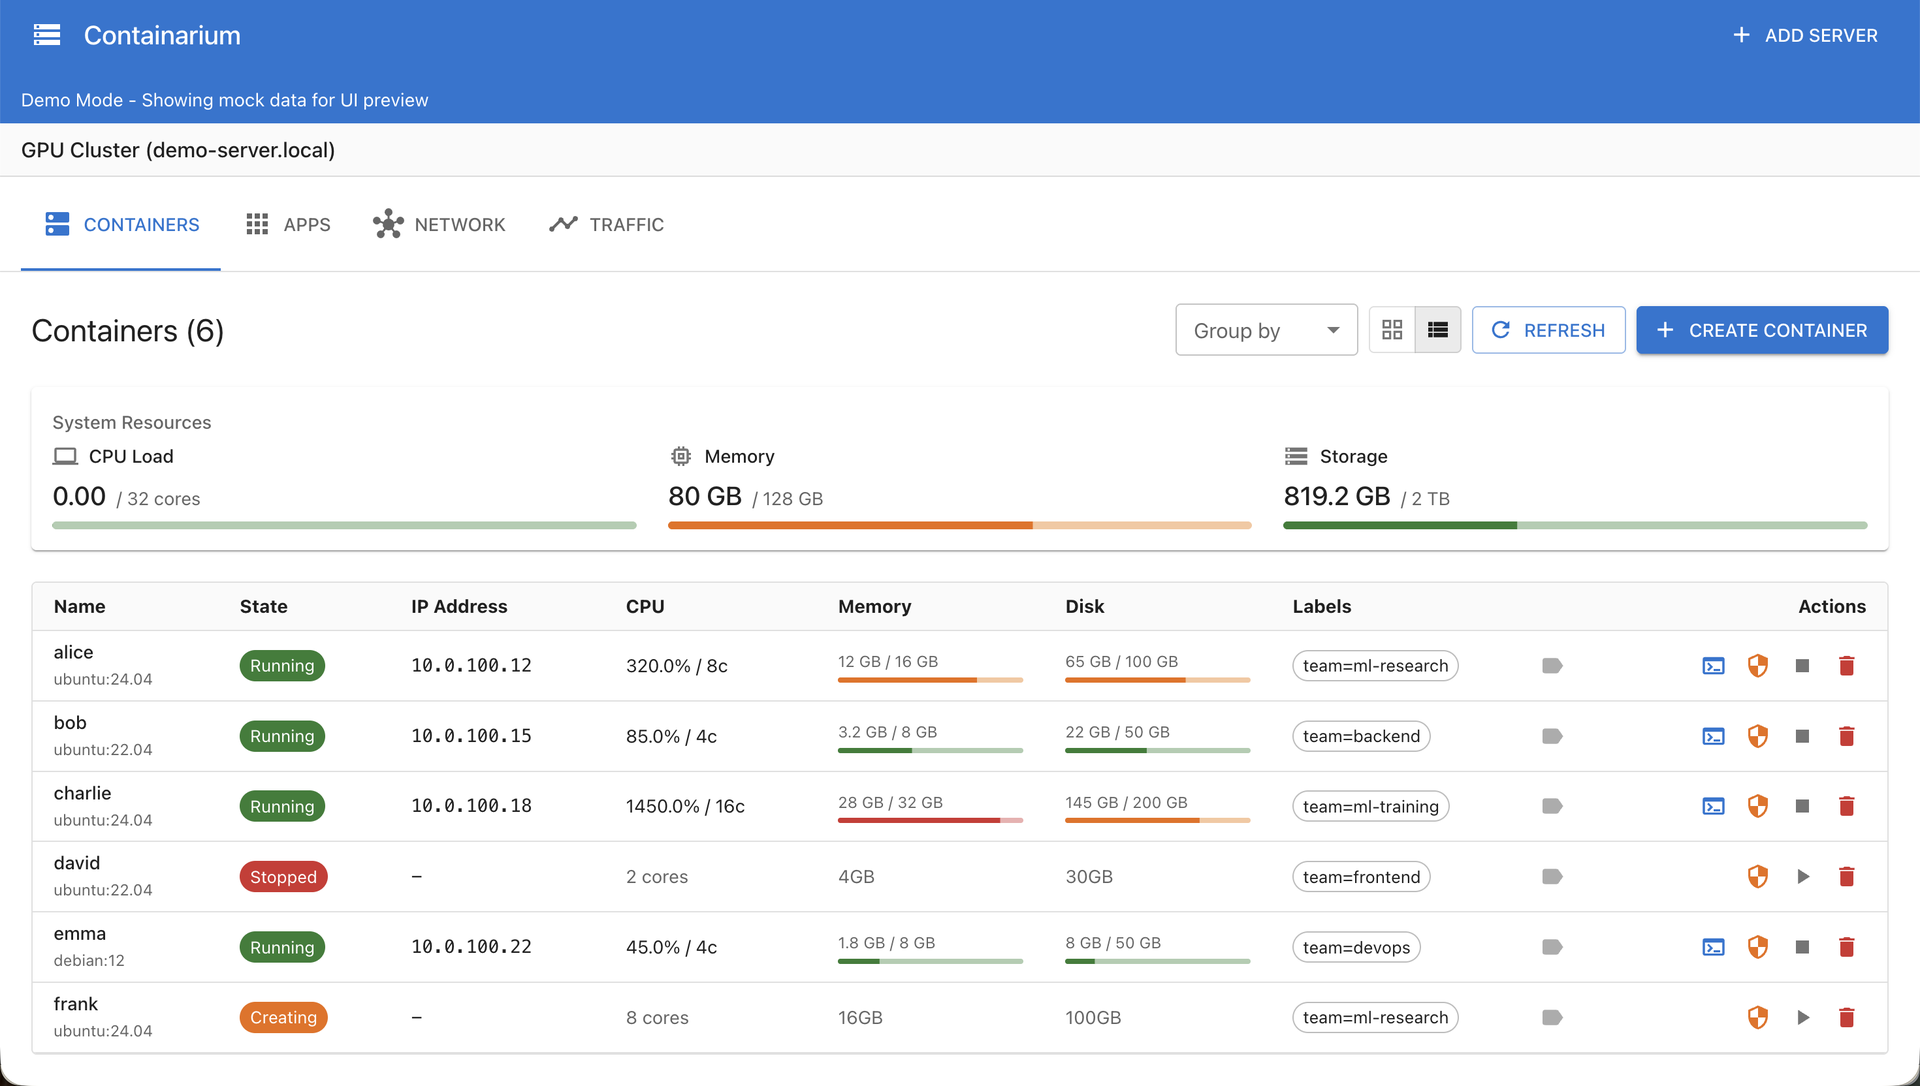
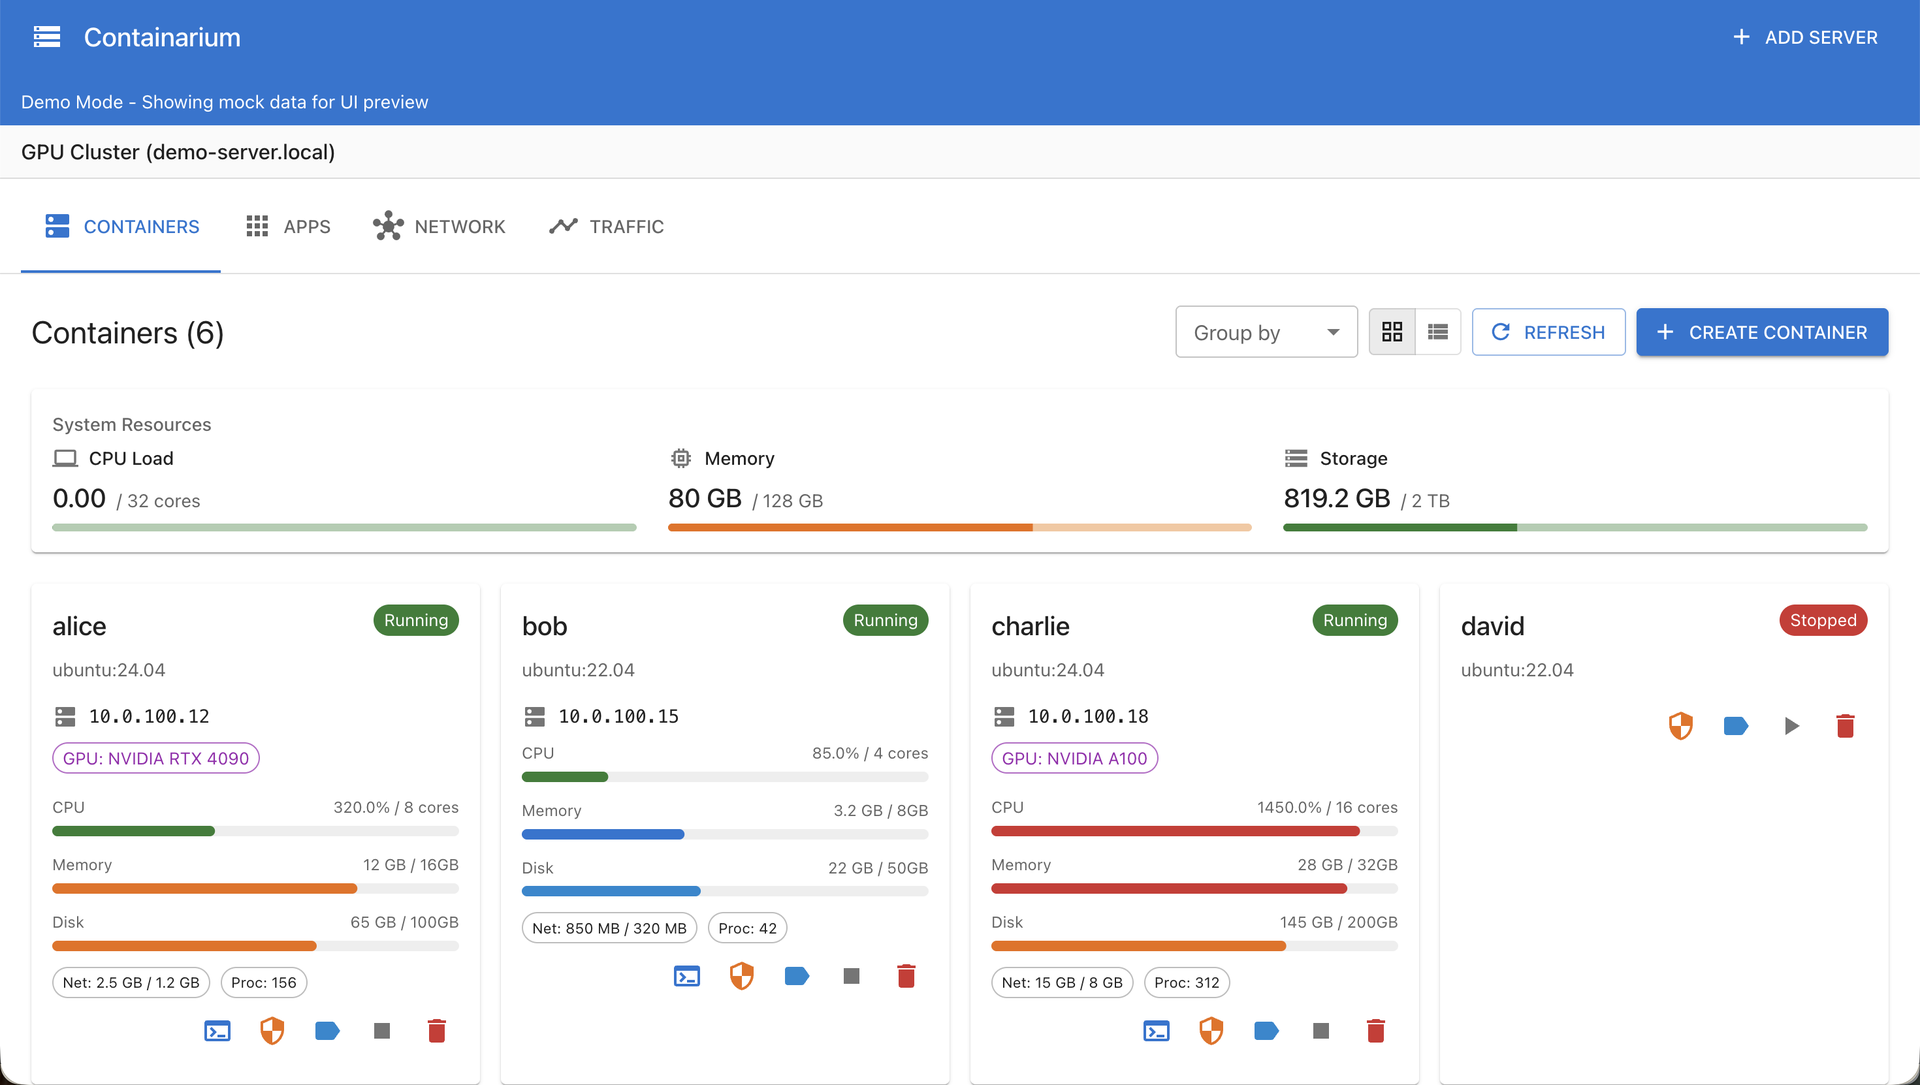
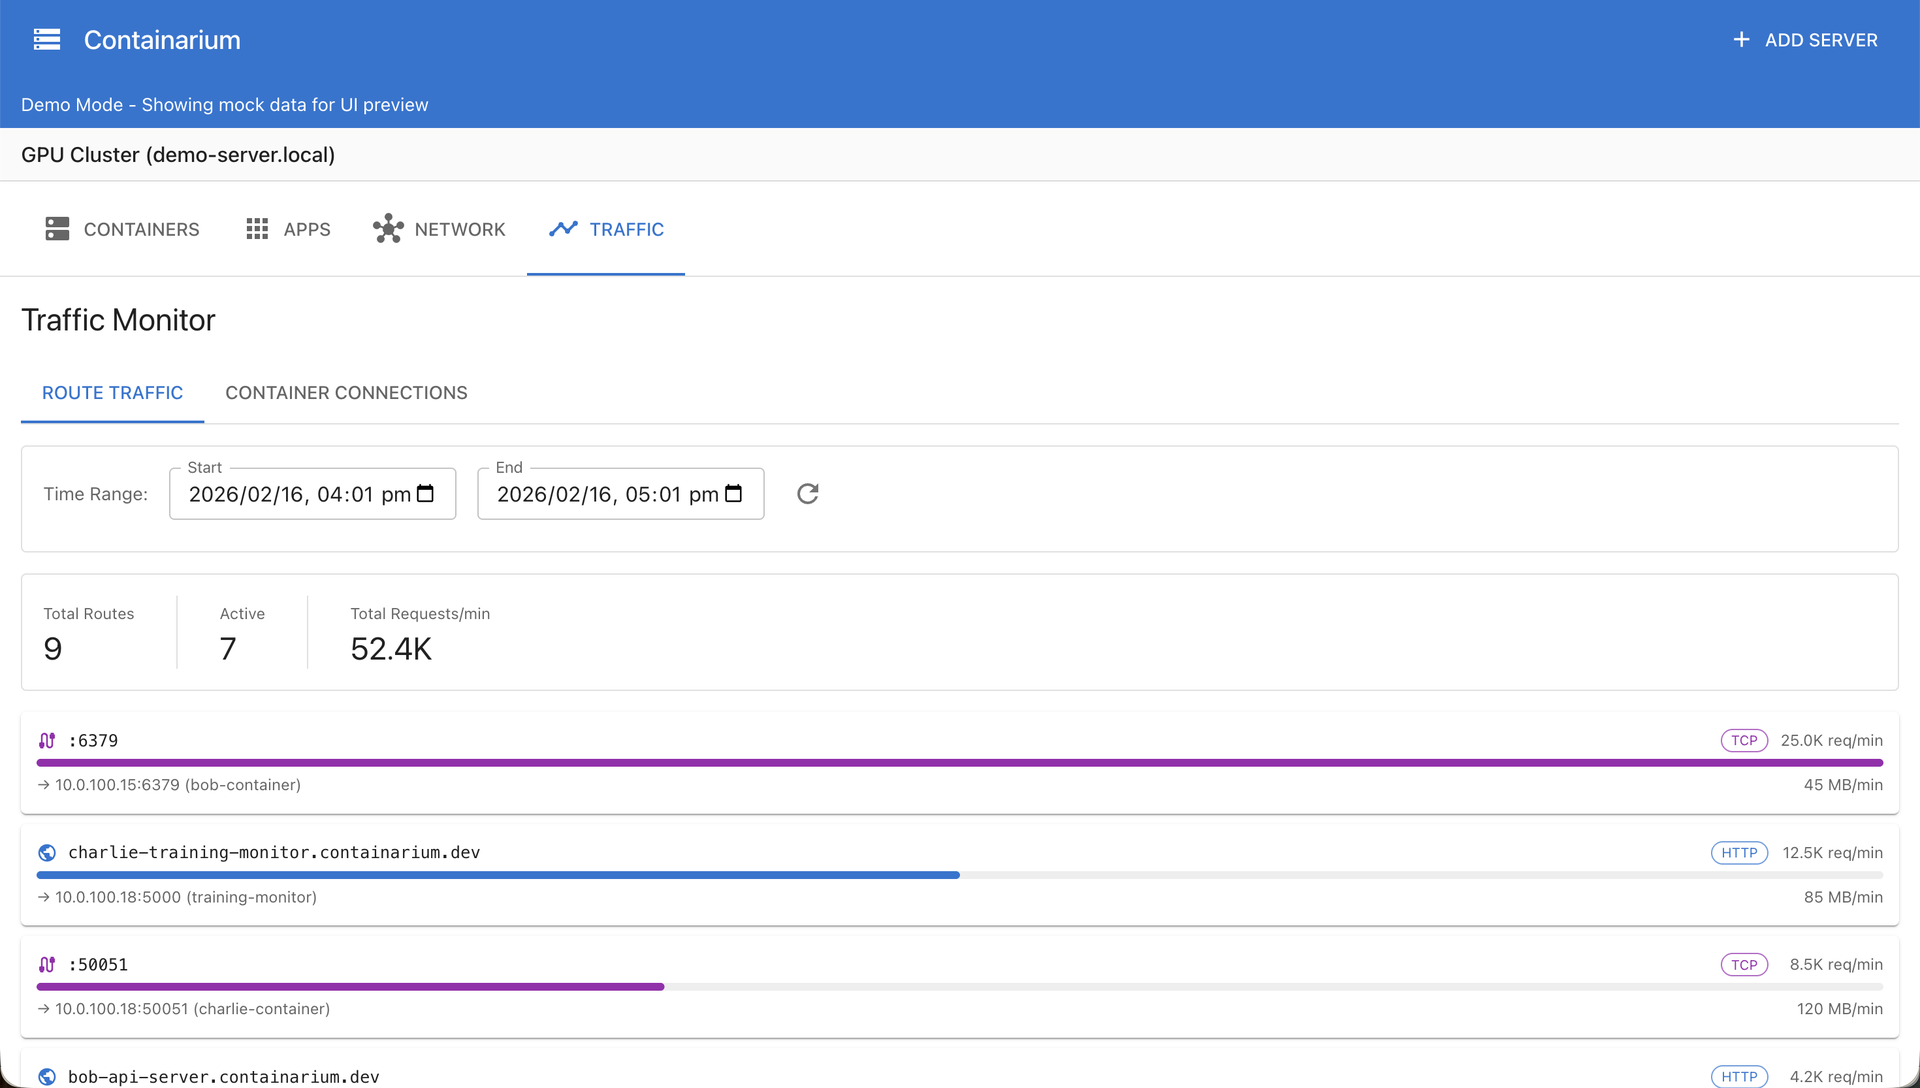
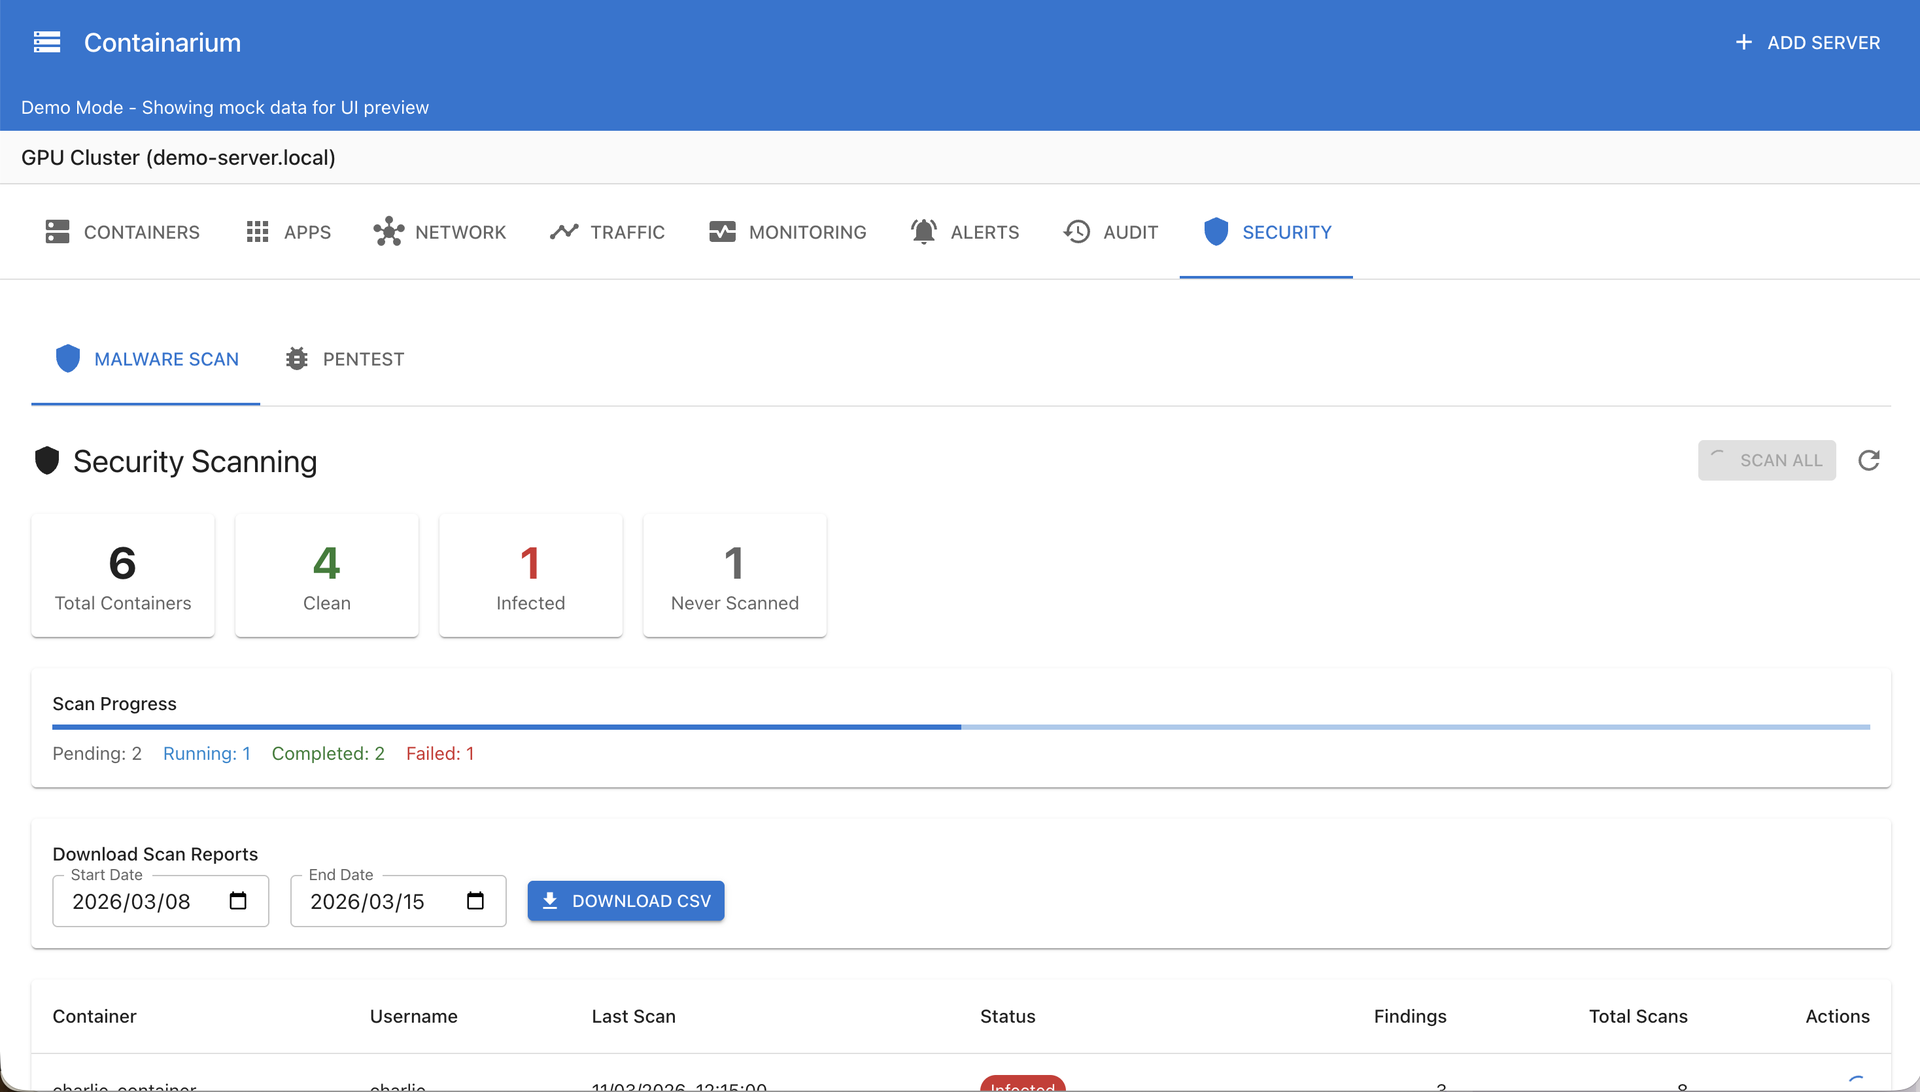
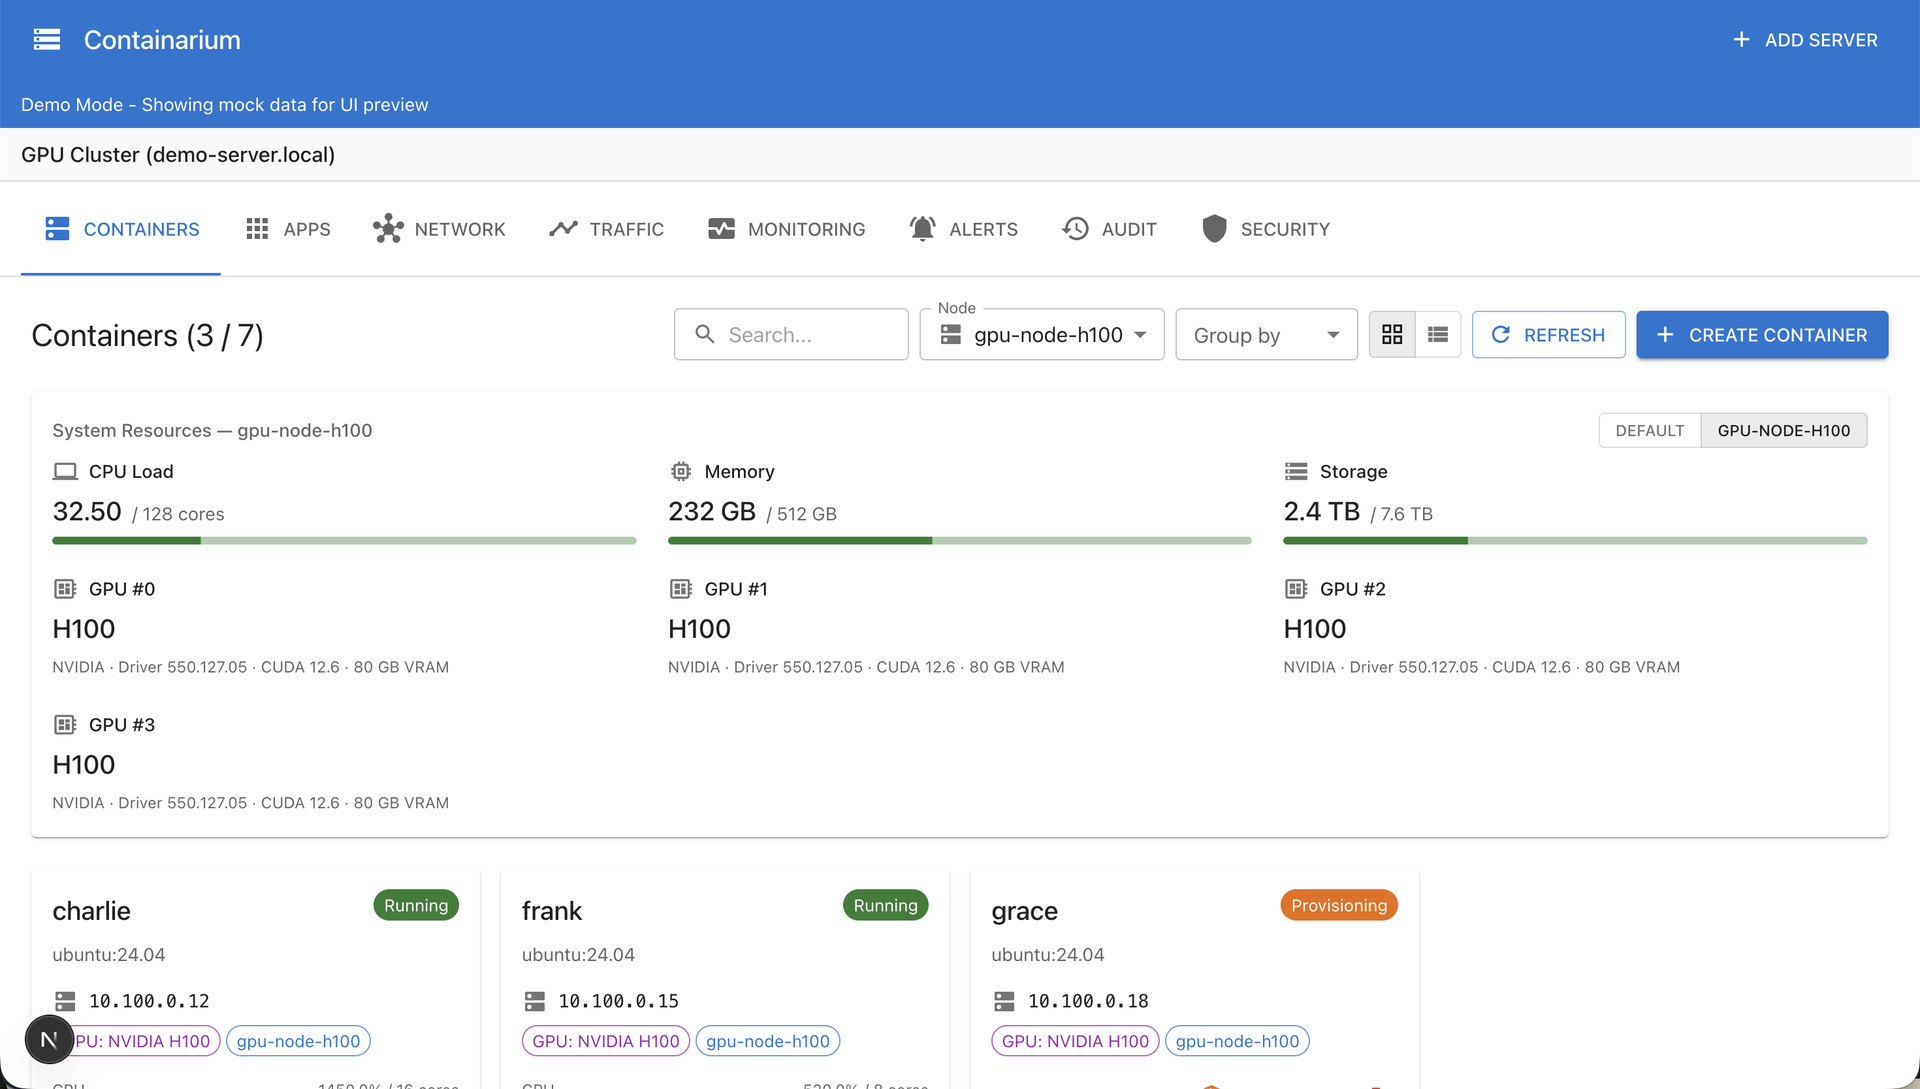
Containarium gives every AI agent a persistent Linux box of its own, reachable over SSH and driven through structured tools instead of a fragile terminal session. One command creates a named sandbox, syncs the SSH configuration, and wires the box into Claude Code, Codex, Gemini or Cursor through an MCP server that runs inside the container. From there the agent can execute shell commands, read and write files, install services, and expose a port on a public hostname with TLS terminated by a Caddy sentinel. Detached code runs keep working after a laptop sleeps or a connection drops, and the operator reattaches to the same byte-exact log later, checks status, or stops the run without losing output. An optional per-tenant eBPF egress policy limits outbound traffic per box, logs denied attempts for audit, and keeps provider API keys inside a model gateway rather than inside the agent environment. Boxes run on LXC or Kubernetes, keep state between agent sessions, support GPU passthrough for local model work, and stay separate from the host operating system and the cluster control plane. The dashboard presents containers, traffic, security events, audit records, GPU state and monitoring in one place. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- Persistent Boxes For Agents
- Each agent receives a named Linux container with systemd, real networking and stored state that survives between sessions, so long builds and services stay alive after the operator disconnects completely.
- Structured Access Over SSH
- Agents work through an in-box MCP server with shell execution and file operations, backed by ordinary SSH access for people, instead of typing blind commands into a scrolling terminal window.
- Bounded Network Blast Radius
- Per-tenant eBPF egress policy can restrict outbound traffic for each box, audit-logged denials show blocked attempts, and the agent holds an SSH key rather than cluster credentials or host access.
- Runs That Survive Disconnects
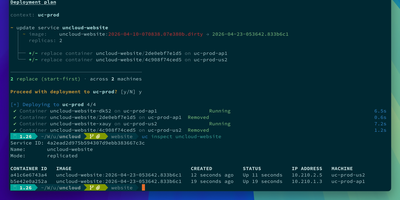
- Detached coding runs continue on the box when a laptop sleeps or wifi drops, and the operator reattaches to a byte-exact captured log, checks the exit code, or stops the run.
Features
- LXC And Kubernetes Backends
- Boxes run as unprivileged LXC containers or on Kubernetes, with GPU passthrough for local inference, persistent storage, real networking and public hostname exposure through a TLS sentinel.
- Model Gateway Key Isolation
- A gateway routes model calls for the boxes and keeps provider API keys outside the agent environment, so a compromised sandbox does not hand an attacker reusable cloud credentials.
- One Command Quickstart
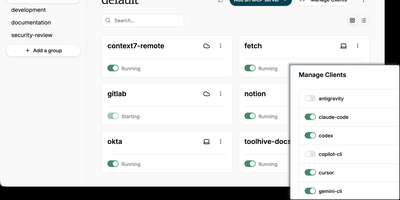
- The quickstart creates a box, reuses or generates an SSH key, writes the client configuration, and wires Claude Code, Codex or Gemini into the box through MCP automatically.
- Public Hostname Exposure
- Expose a container port on a domain and a Caddy sentinel terminates TLS and forwards traffic to the box, turning an agent-built service into a reachable public web application.
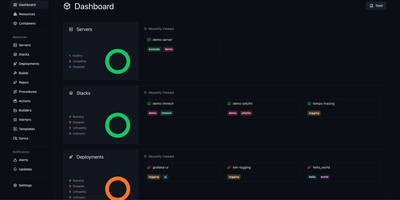
- Operations Dashboard Included
- Container lists, traffic views, security events, audit records, GPU state, alerts and monitoring present the runtime in one web dashboard for the operator who owns the host.