Stars
Forks
Watchers
Developer links
Versus Incident
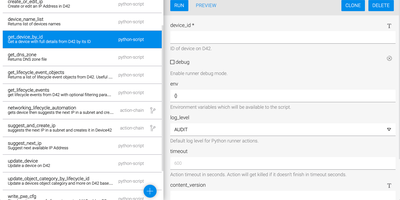
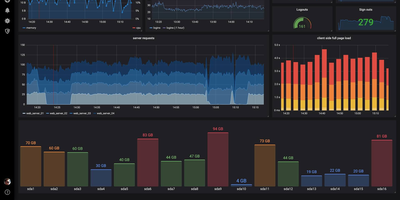
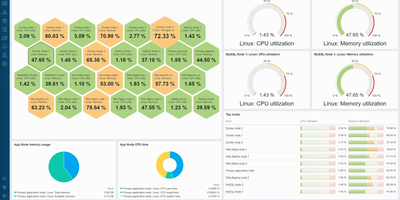
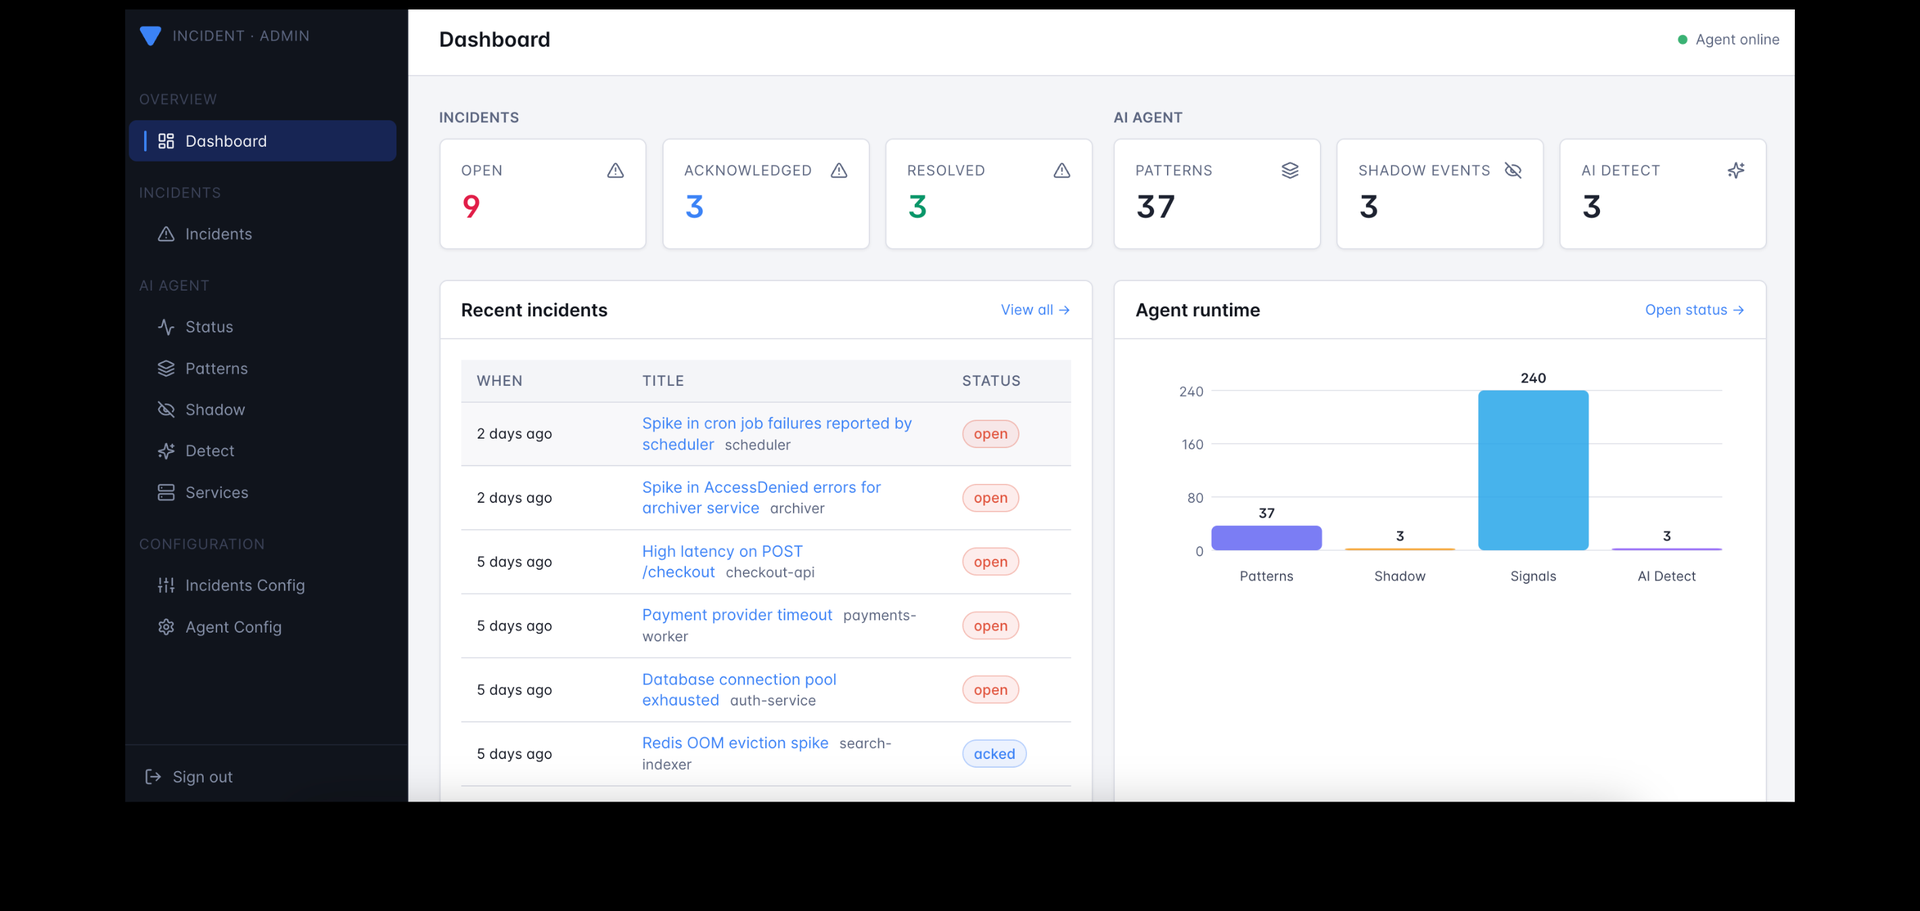
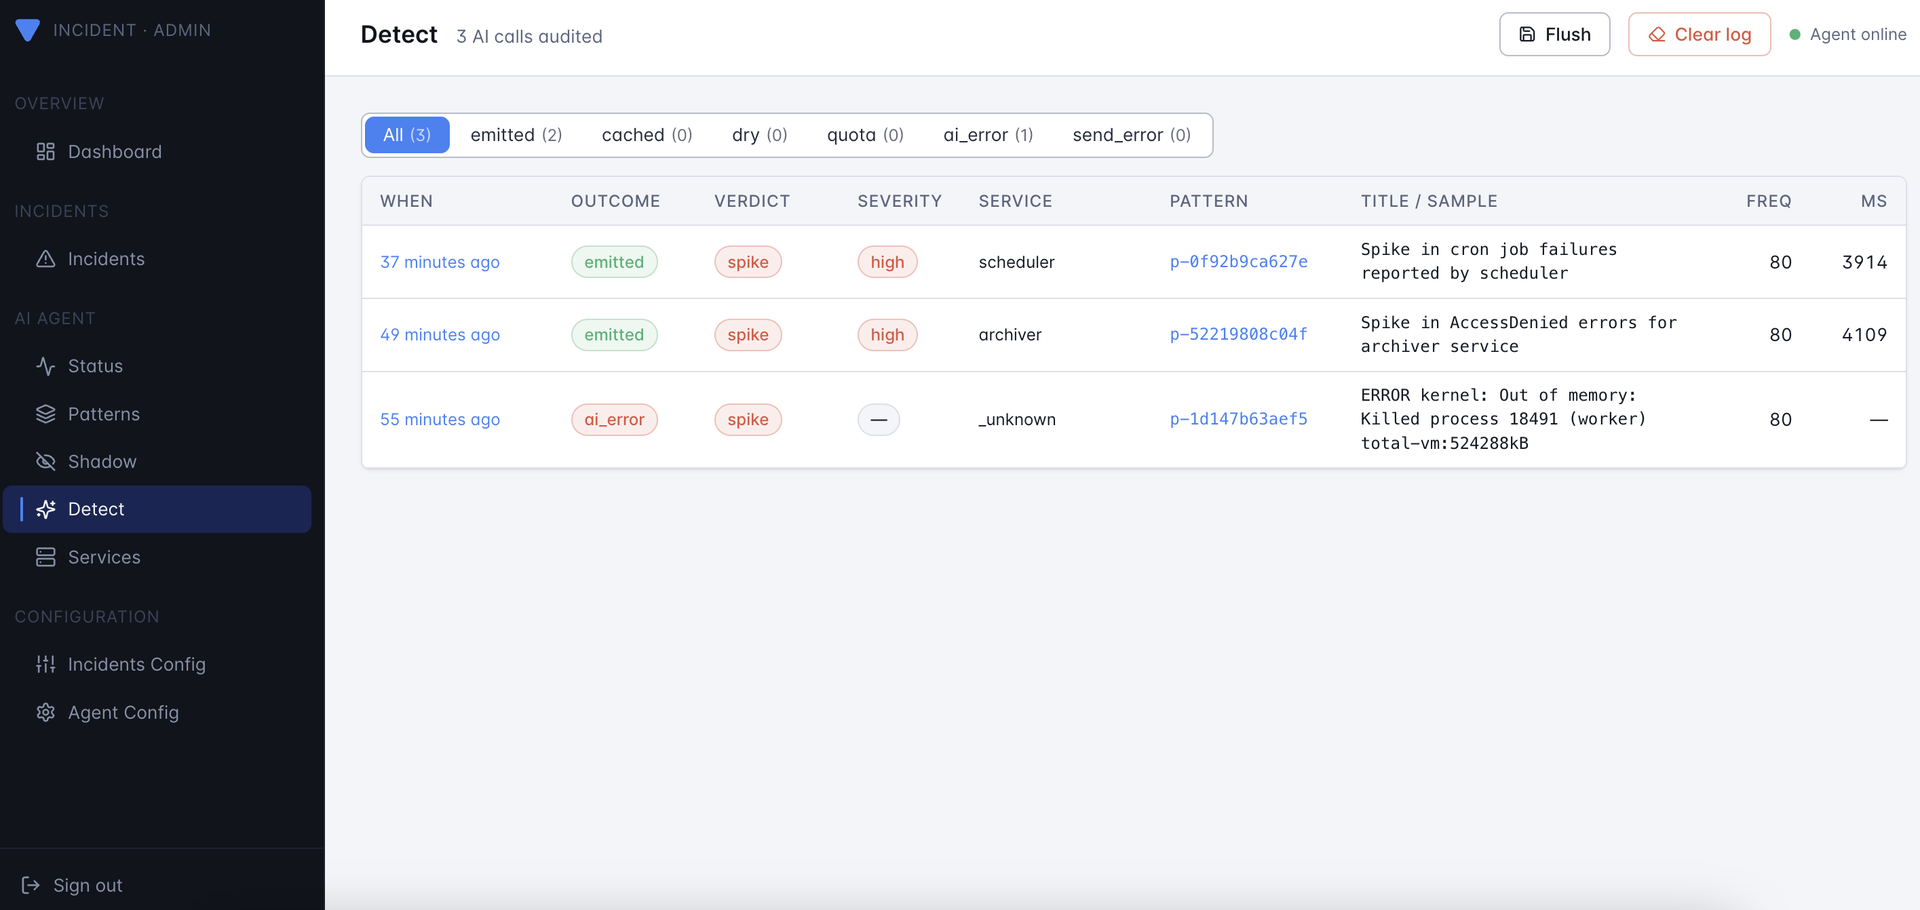
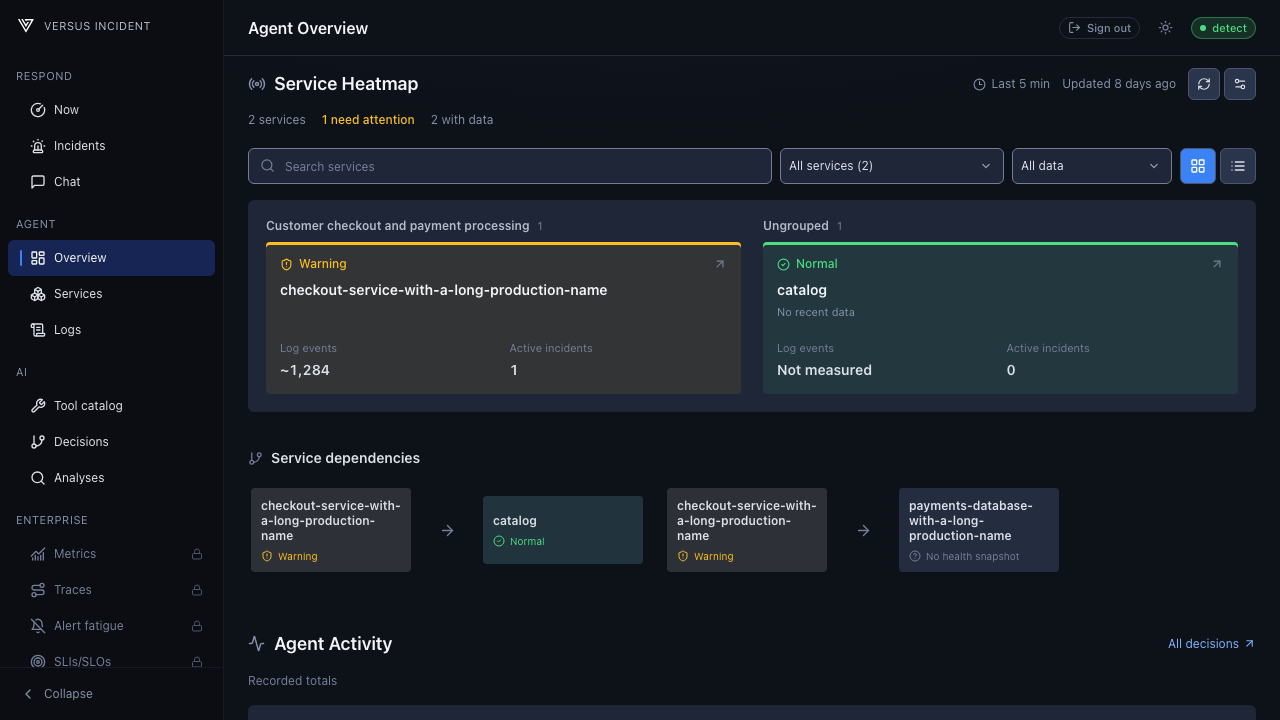
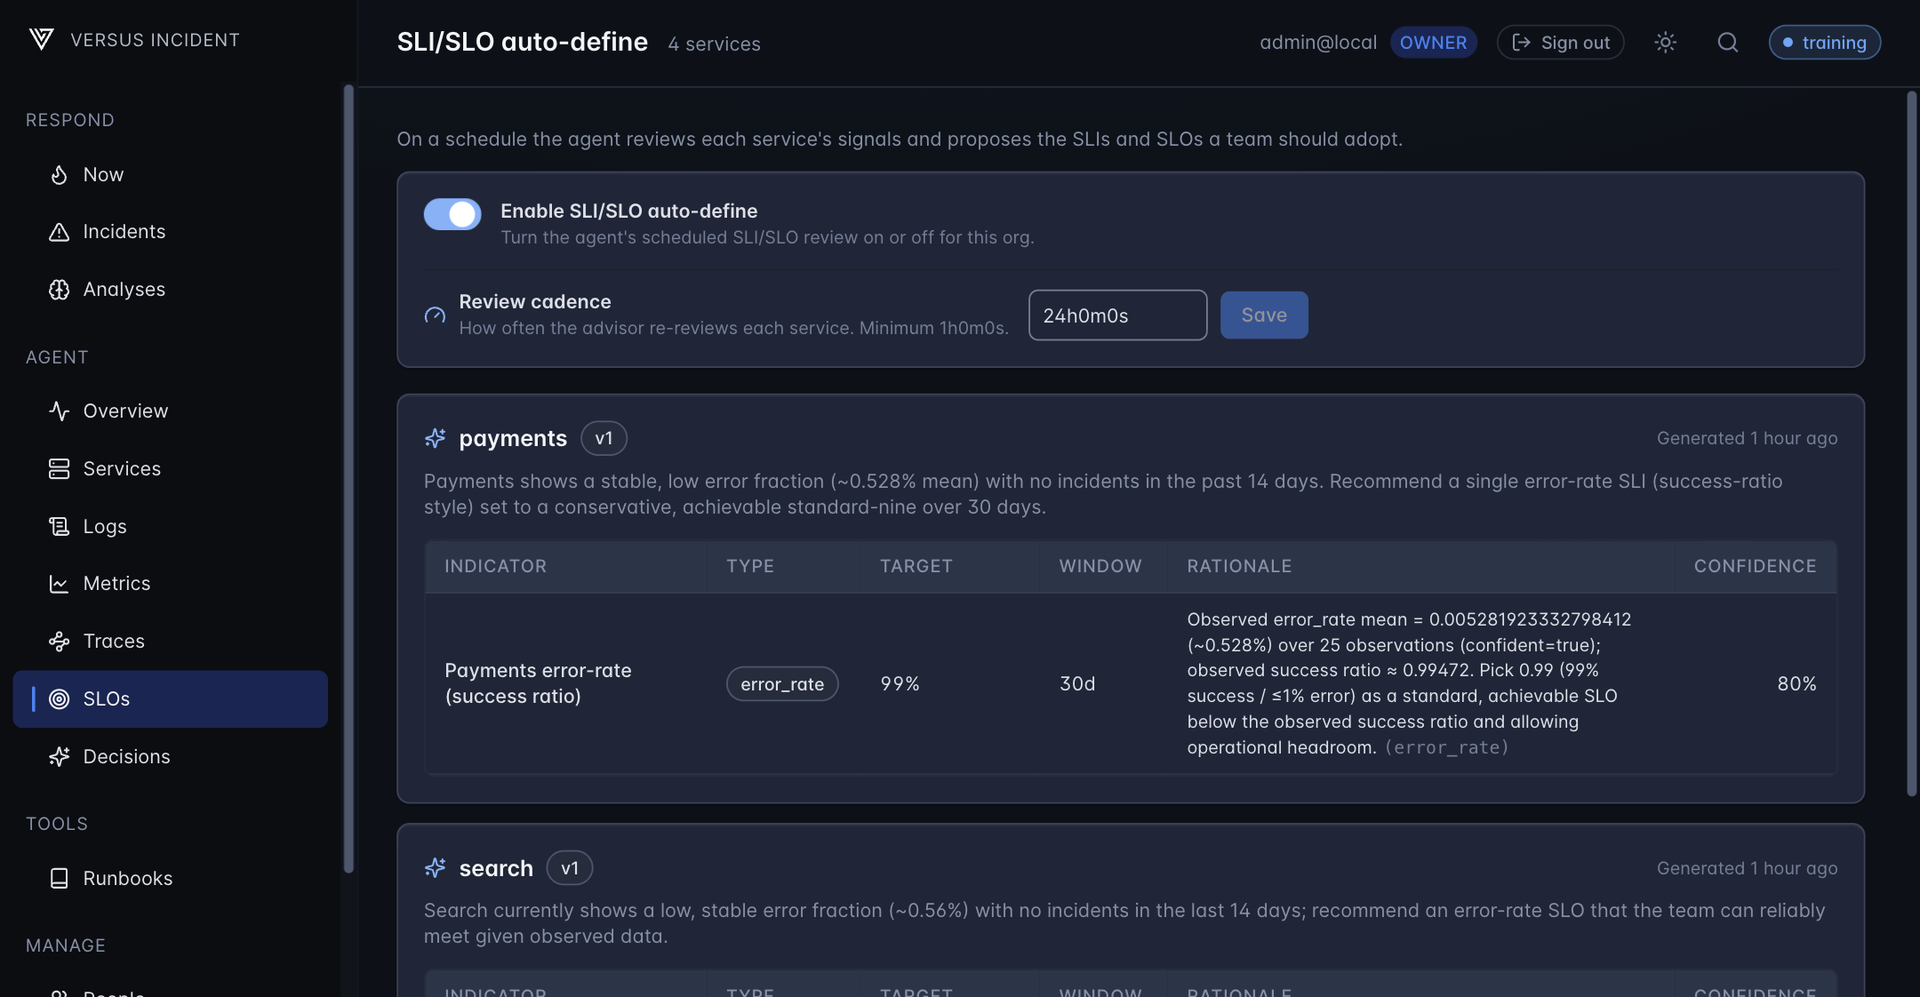
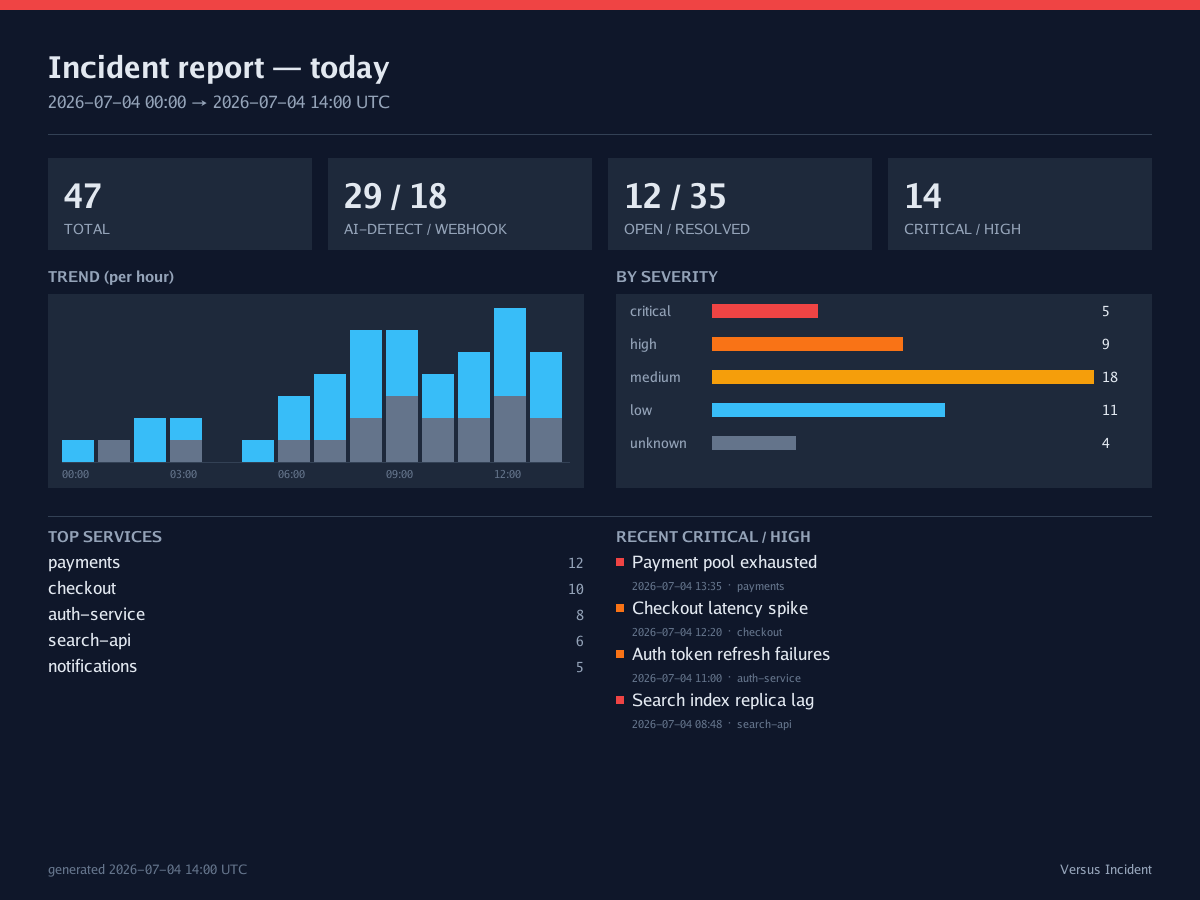
Versus Incident is a self-hosted AI SRE agent and incident manager that learns what normal looks like in your logs, metrics, traces, and Kubernetes clusters, then opens a triaged incident the moment something genuinely new appears. Detection earns trust gradually. Training mode only observes and catalogs patterns; shadow mode records what it would have alerted so you can judge its instincts; detect mode creates real incidents with an AI-written summary, a severity, and suggested next steps attached. Existing alerting does not have to move: Alertmanager, Grafana, Sentry, CloudWatch, Fluent Bit, and custom scripts post to the same webhook endpoint, and every incident, however it arrived, is rendered with your Go templates. Delivery fans out to Slack, Microsoft Teams, Telegram, Viber, email, and Lark. Silence has a deadline, because unacknowledged incidents escalate to on-call through PagerDuty, AWS Incident Manager, Opsgenie, incident.io, or ServiceNow. The Kubernetes dashboard gathers cluster health and capacity, workloads, resource relationships, recent changes, Helm releases, and GitOps status, and a DevOps chat agent in the web UI answers questions against the connected systems while responders work. The admin dashboard reviews learned patterns, shadow events, and raised incidents, so the agent's judgment stays inspectable. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Benefits
- Incidents Without Alert Rules
- The agent learns normal behavior from your logs and opens incidents only for brand-new errors and anomalies, so detection coverage grows without a rule file someone must maintain forever.
- Triage Before The Page
- Each detected incident arrives with an AI-written summary, severity, and suggested next steps plus the underlying evidence, so the responder starts investigating instead of gathering context from scratch.
- Every Channel, One Fan-Out
- Incidents from the agent or your existing webhooks are templated once and delivered to Slack, Teams, Telegram, Viber, email, and Lark, with on-call escalation when nobody acknowledges.
- Trust Built In Stages
- Training mode only watches, shadow mode logs what it would have alerted, and detect mode goes live, letting you verify the agent's judgment against your systems before it pages anyone.
Features
- AI SRE Detection Agent
- Continuously reads logs, metrics, and traces through configurable sources, catalogs learned patterns, and flags novel anomalies, with Redis tracking reading positions across restarts.
- Kubernetes Harness Dashboard
- One view of cluster health and capacity, workloads, resource relationships, recent changes, Helm releases, and GitOps status, plus a DevOps chat agent for interrogating connected systems.
- Webhook Alert Intake
- A single POST endpoint accepts alerts from Alertmanager, Grafana, Sentry, CloudWatch SNS, Fluent Bit, and custom scripts, normalized through your own Go message templates.
- On-Call Escalation Chain
- Acknowledgment windows with per-request overrides escalate unacknowledged incidents to PagerDuty, AWS Incident Manager, Opsgenie, incident.io, or ServiceNow through Redis-backed state.