Categories
Self-Hosted Privacy File Sharing Secret Sharing End-to-End Encryption Secure Notes Self-Destructing Notes Password SharingStars
Forks
Watchers
Developer links
Enclosed
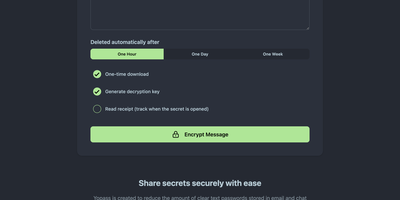
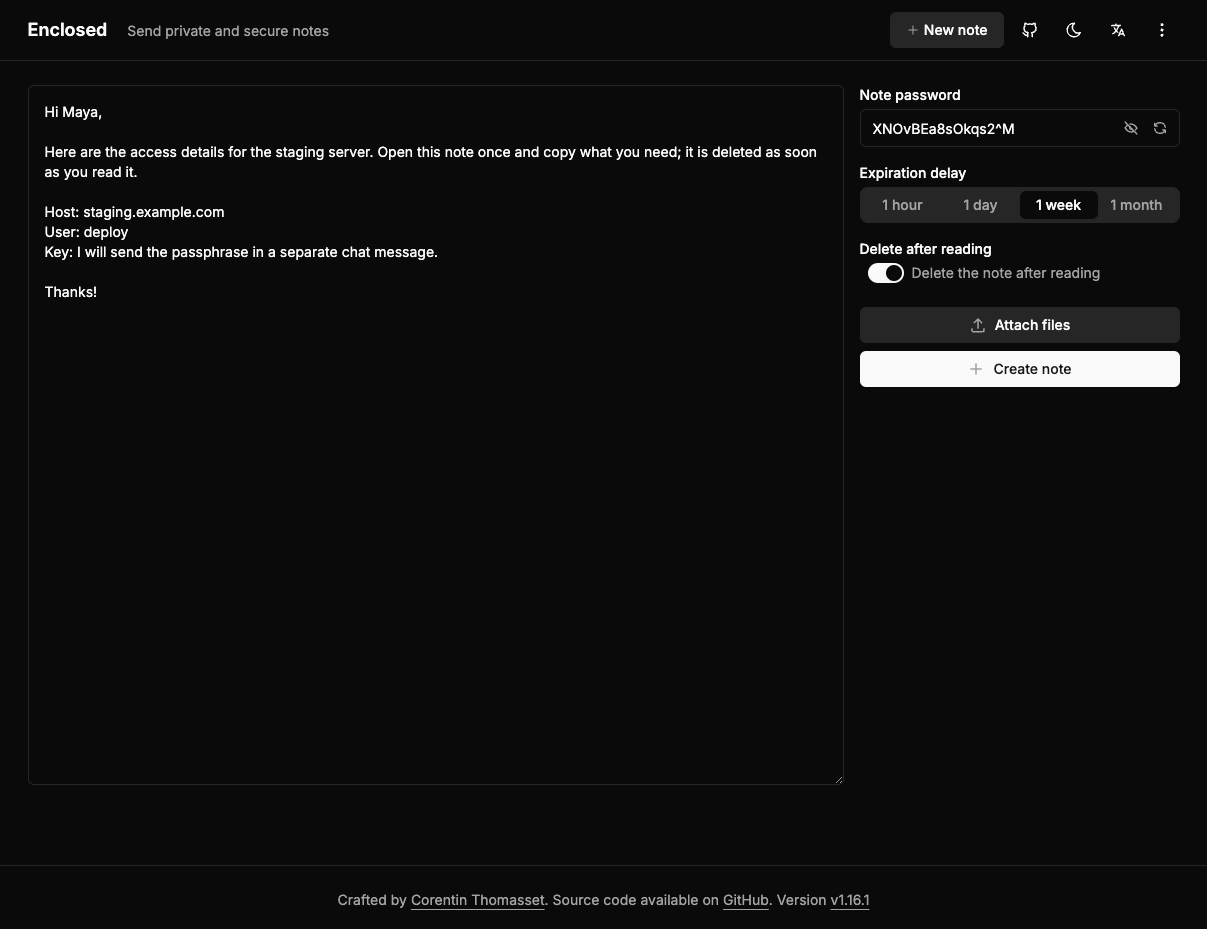
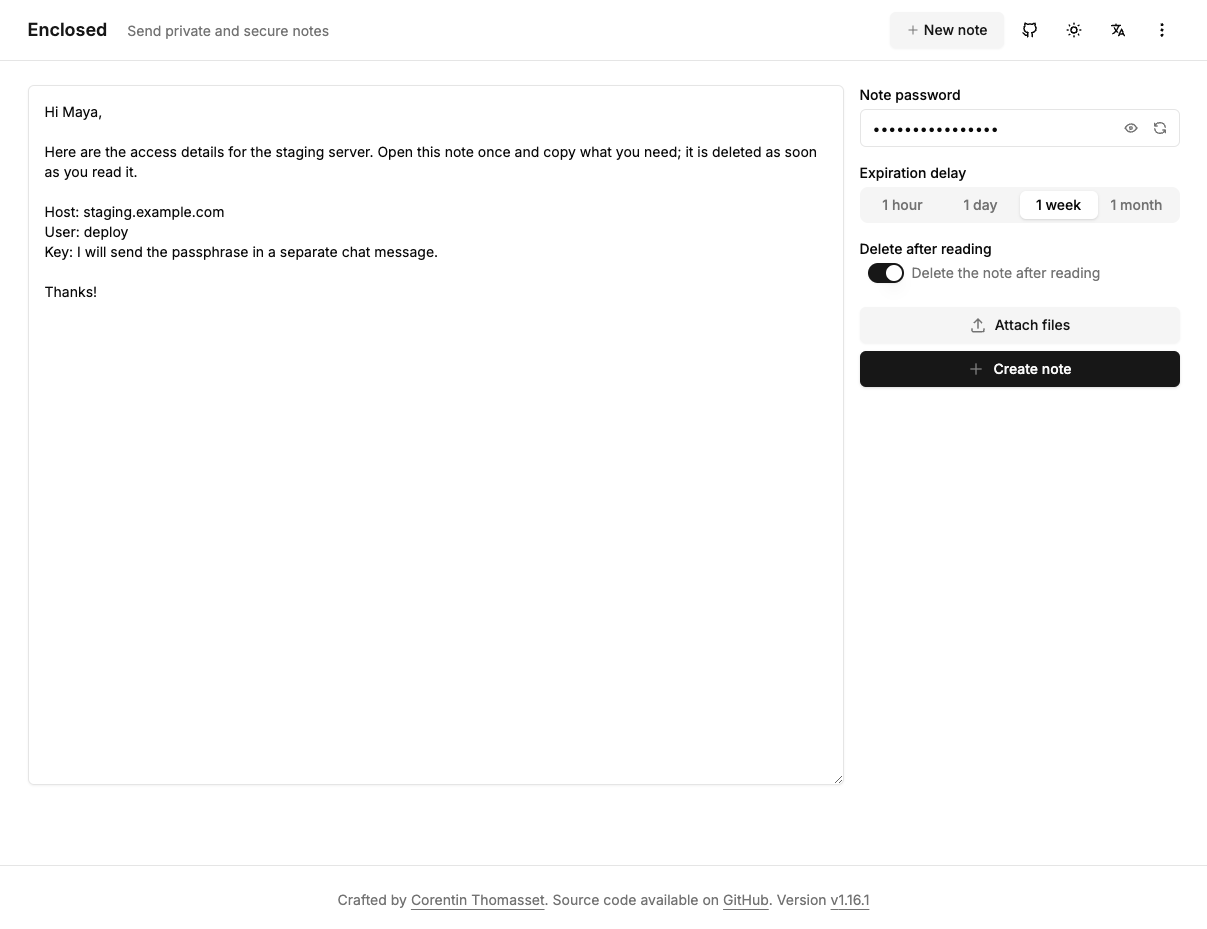
Private text, encrypted before it leaves the browser: Enclosed turns passwords, keys, and other secrets into a link that only its holder can open, with no third-party service in between. Can the server read the note? No. It stores only ciphertext and settings, because the decryption key rides in the part of the link after the # sign, which browsers never send. Want a second lock? Add a password, or generate a random one with a click, and share it by another route. Worried about links lingering in chat history? Pick one hour, one day, one week, or one month, and tick Delete after reading so the first view removes the note, with a warning shown to the recipient beforehand. Need more than text? Attach files by button or drag and drop, and recipients download them one by one or all at once. Sending to a phone? Every finished note offers a QR code, downloadable as SVG or PNG. Setting it up for a team? Restrict note creation to signed-in users, create notes from the command line, and let people read the interface in 17 languages with light, dark, or system themes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- The server never sees your note
- Notes and attachments are encrypted in the browser, and the key sits in the link fragment that browsers never send, so a compromised host exposes nothing readable.
- Links that clean up after themselves
- Pick an expiry from one hour to one month and tick Delete after reading; the instance also purges expired notes on an hourly schedule by default.
- A second lock when you need one
- Add a password that is combined with the link secret to derive the encryption key, or generate a random one with a single click and share it separately.
- Your own private note service
- Run one instance for your team: restrict note creation to signed-in users defined by email and bcrypt hash, set default expiry, and store everything in one data folder.
Features
- Browser-Side Encryption
- Notes and files are encrypted client-side with AES-GCM using a 256-bit key; a PBKDF2 with SHA-256 step derives the master key from the link secret and any password.
- Password and Expiry Controls
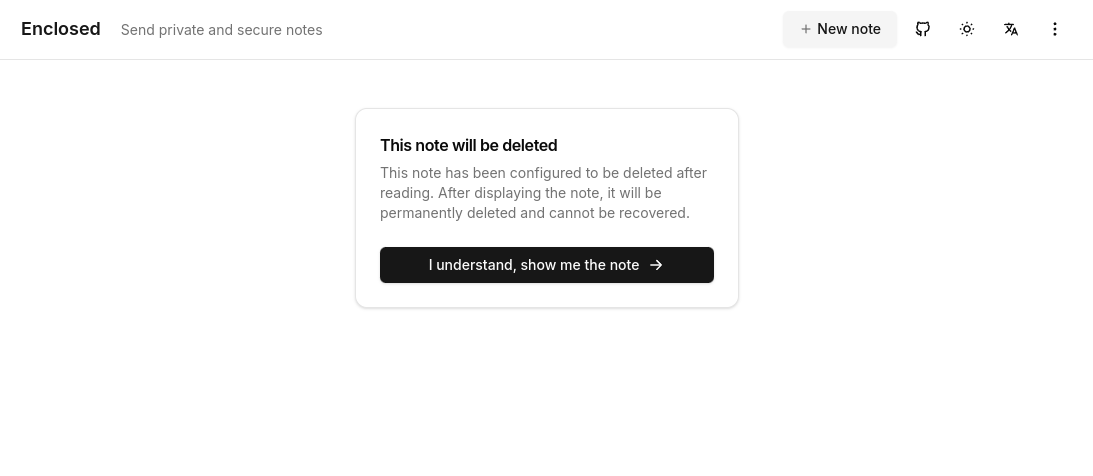
- Set an optional password, choose 1 hour, 1 day, 1 week, or 1 month (or no expiry where allowed), and enable Delete after reading with a confirmation screen.
- File Attachments
- Attach files with a button or drag and drop; recipients see a file list with per-file Download buttons and a Download all files action.
- Link and QR Code Sharing
- A finished note shows a copyable link, a Share note button, and a QR code that can be downloaded as SVG or PNG or copied as SVG code.
- Command-Line Client
- The @enclosed/cli package, installed through npm, yarn, or pnpm, creates notes from arguments or stdin with password and TTL options, views notes, and can target any instance.
- Themes and 17 Languages
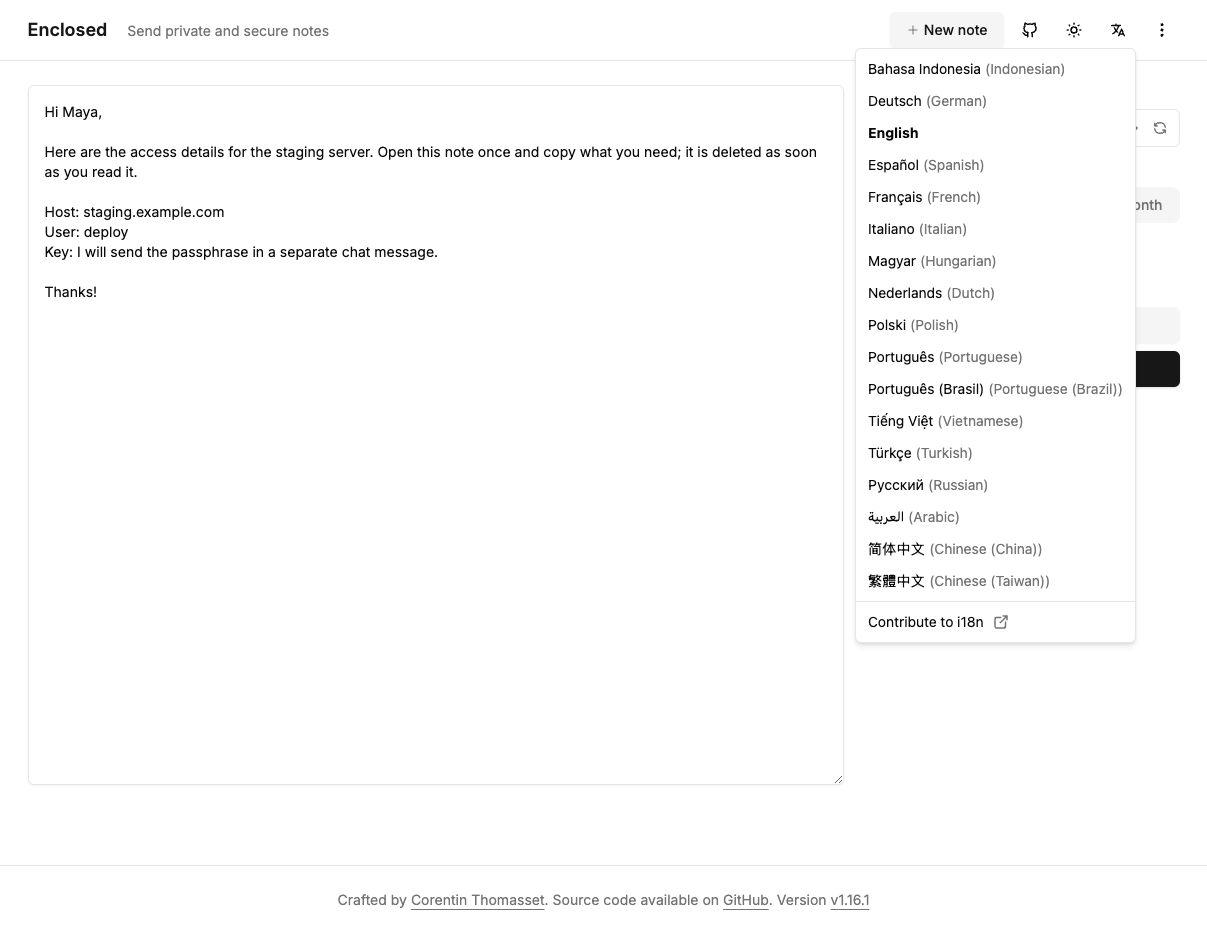
- Light, dark, and system themes plus 17 interface languages, including Arabic, Chinese, German, and Vietnamese, in a responsive layout that works on phones and desktops.