Stars
Forks
Watchers
Developer links
ISMS Builder
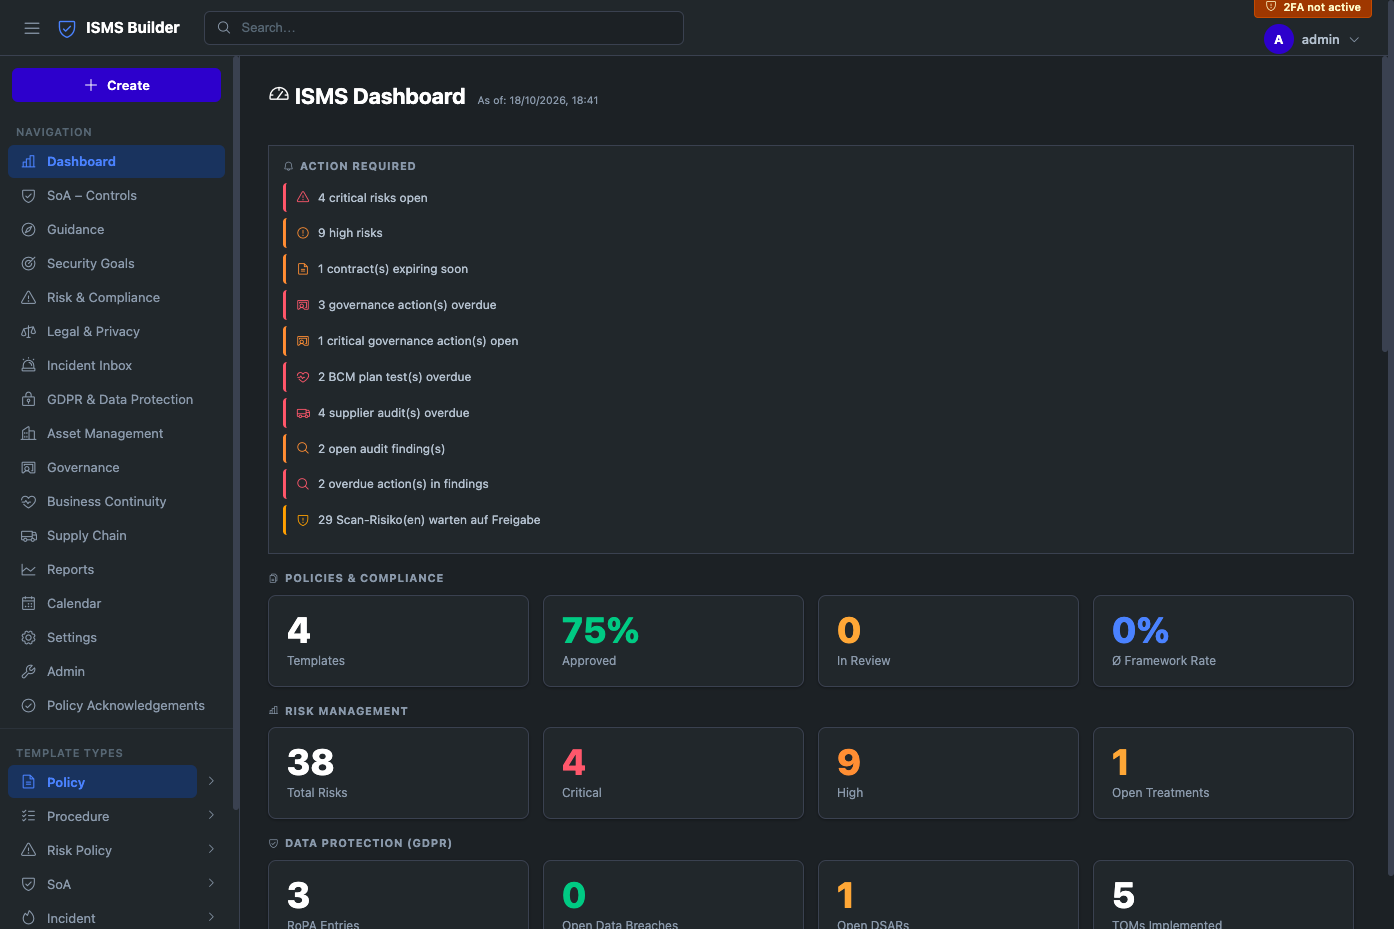
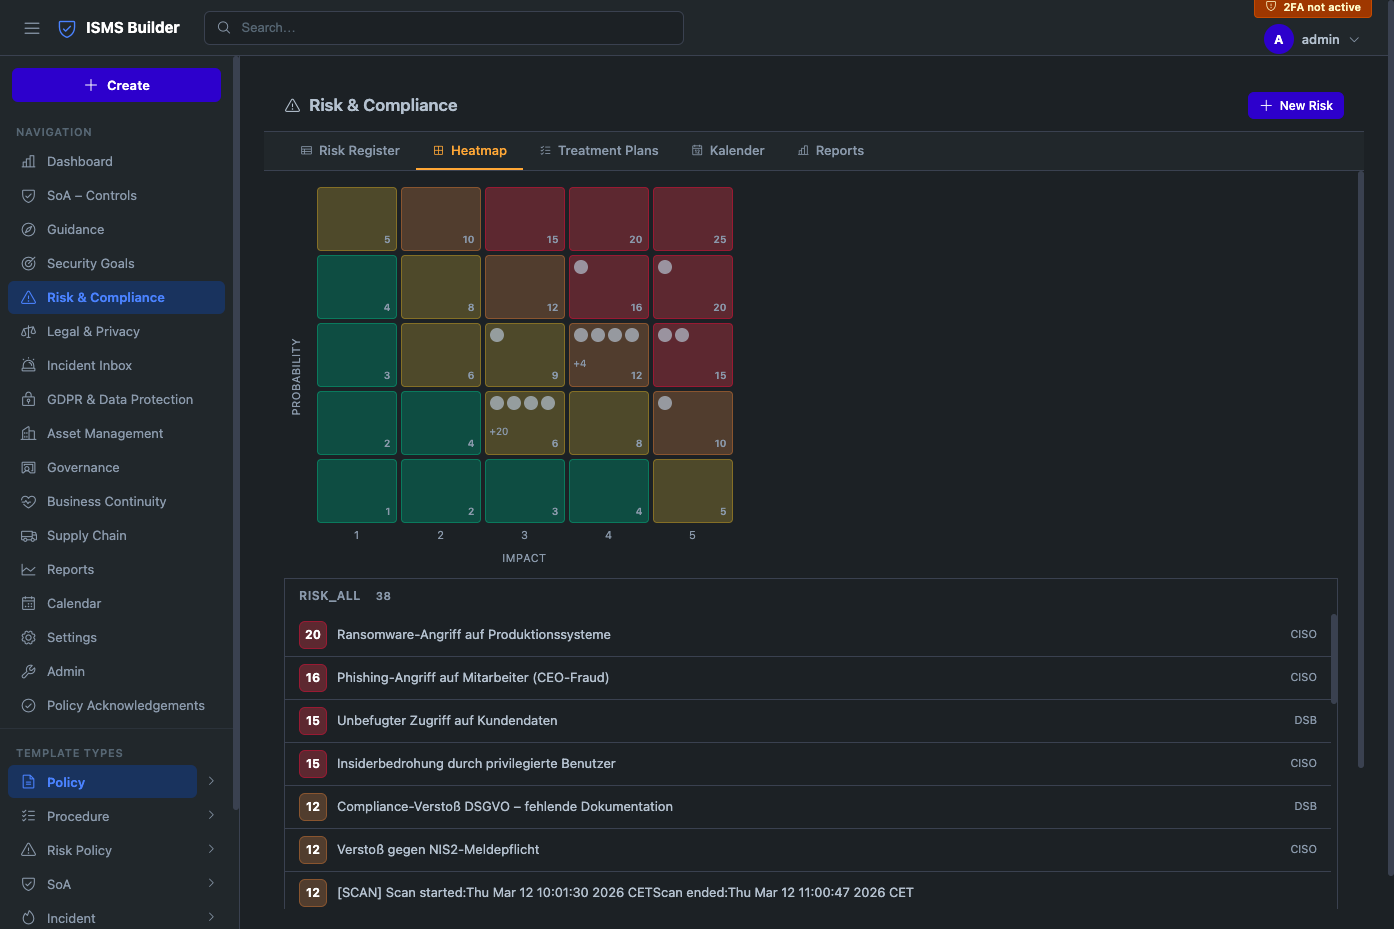
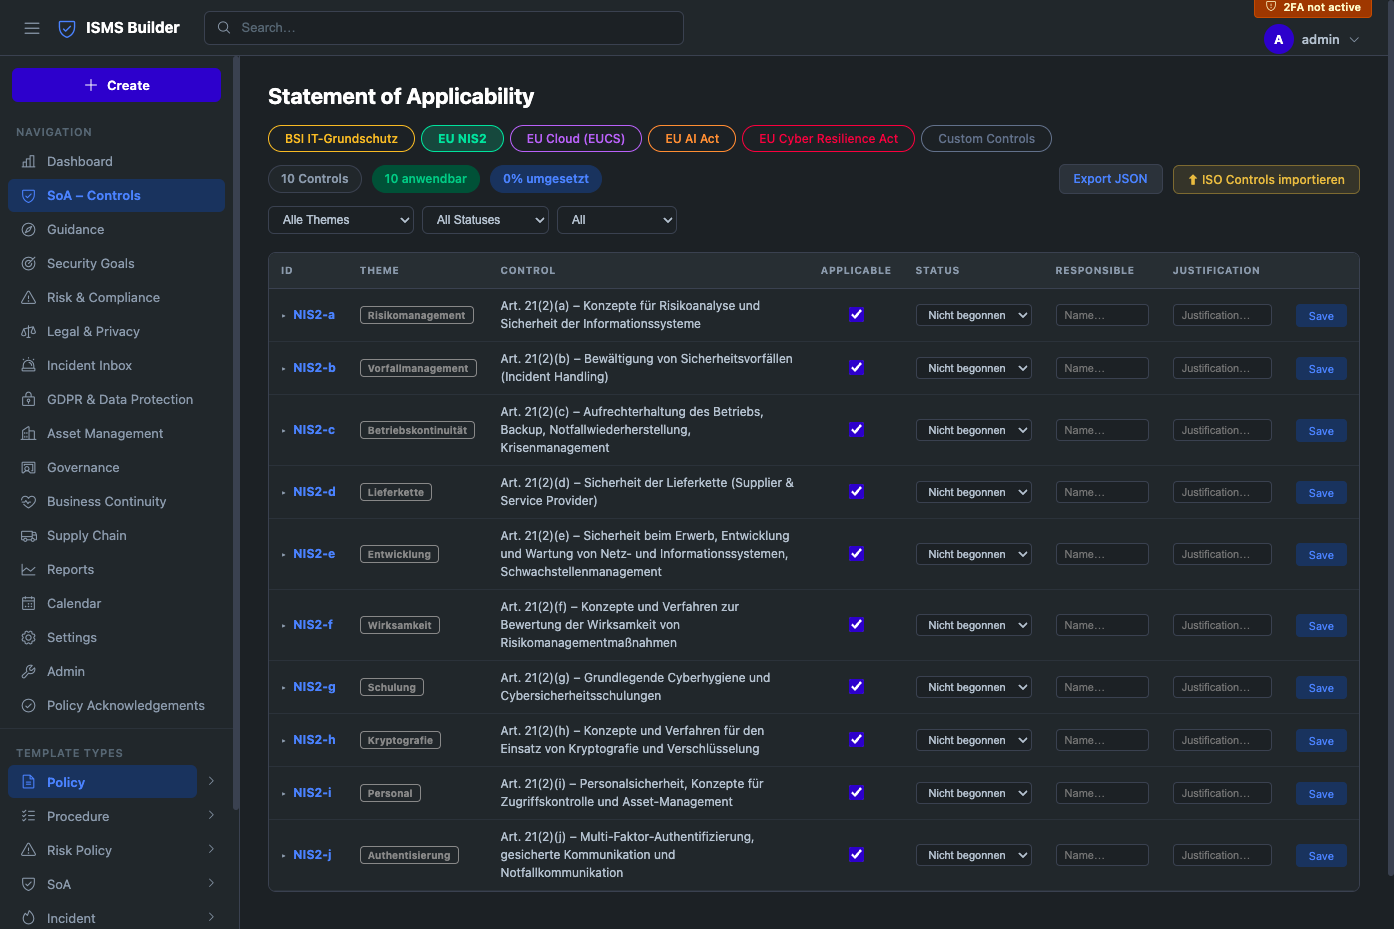
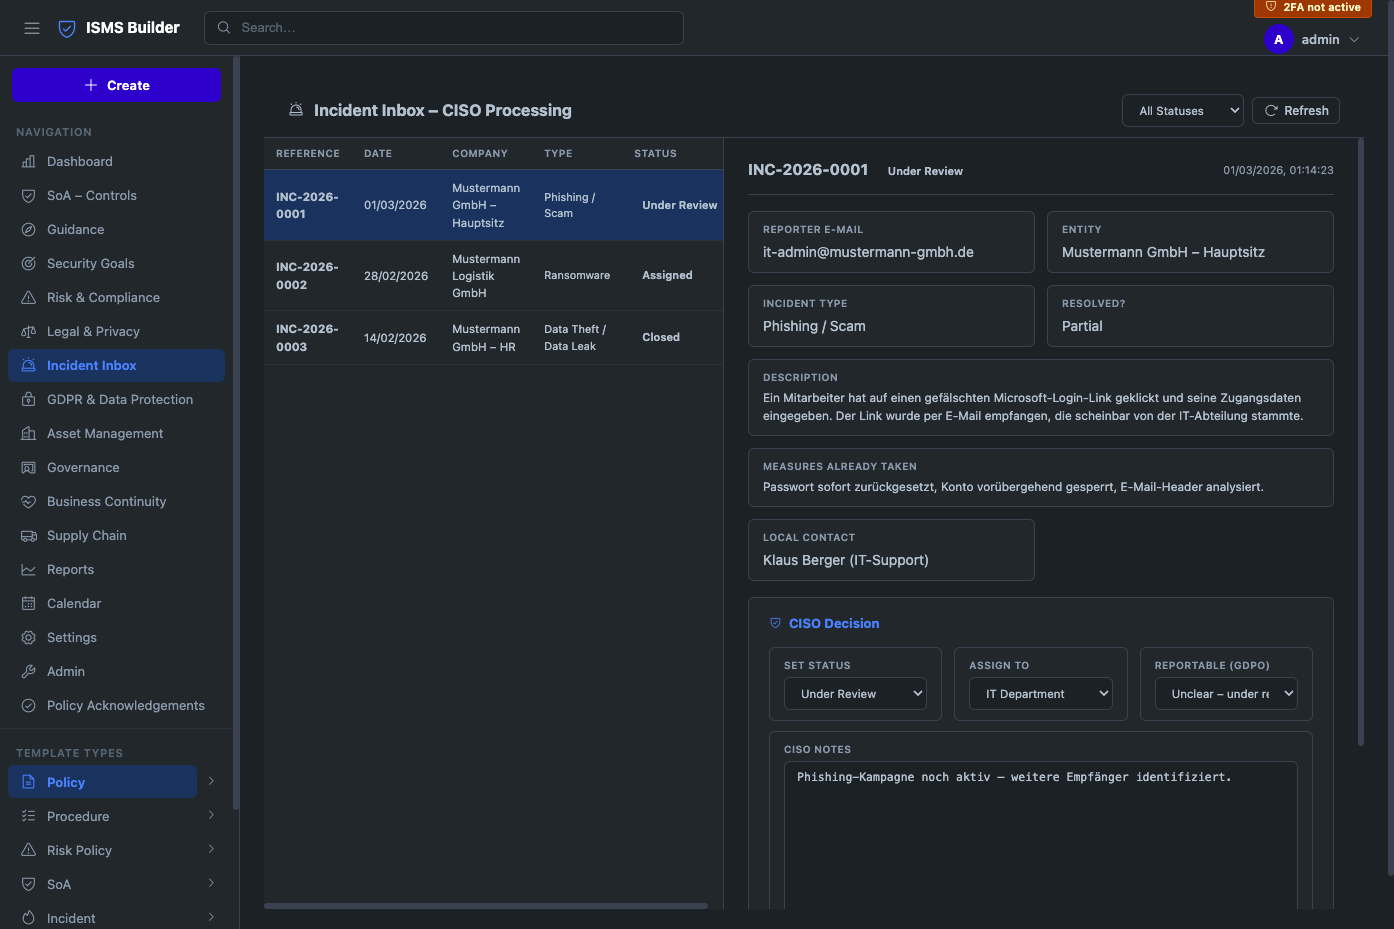
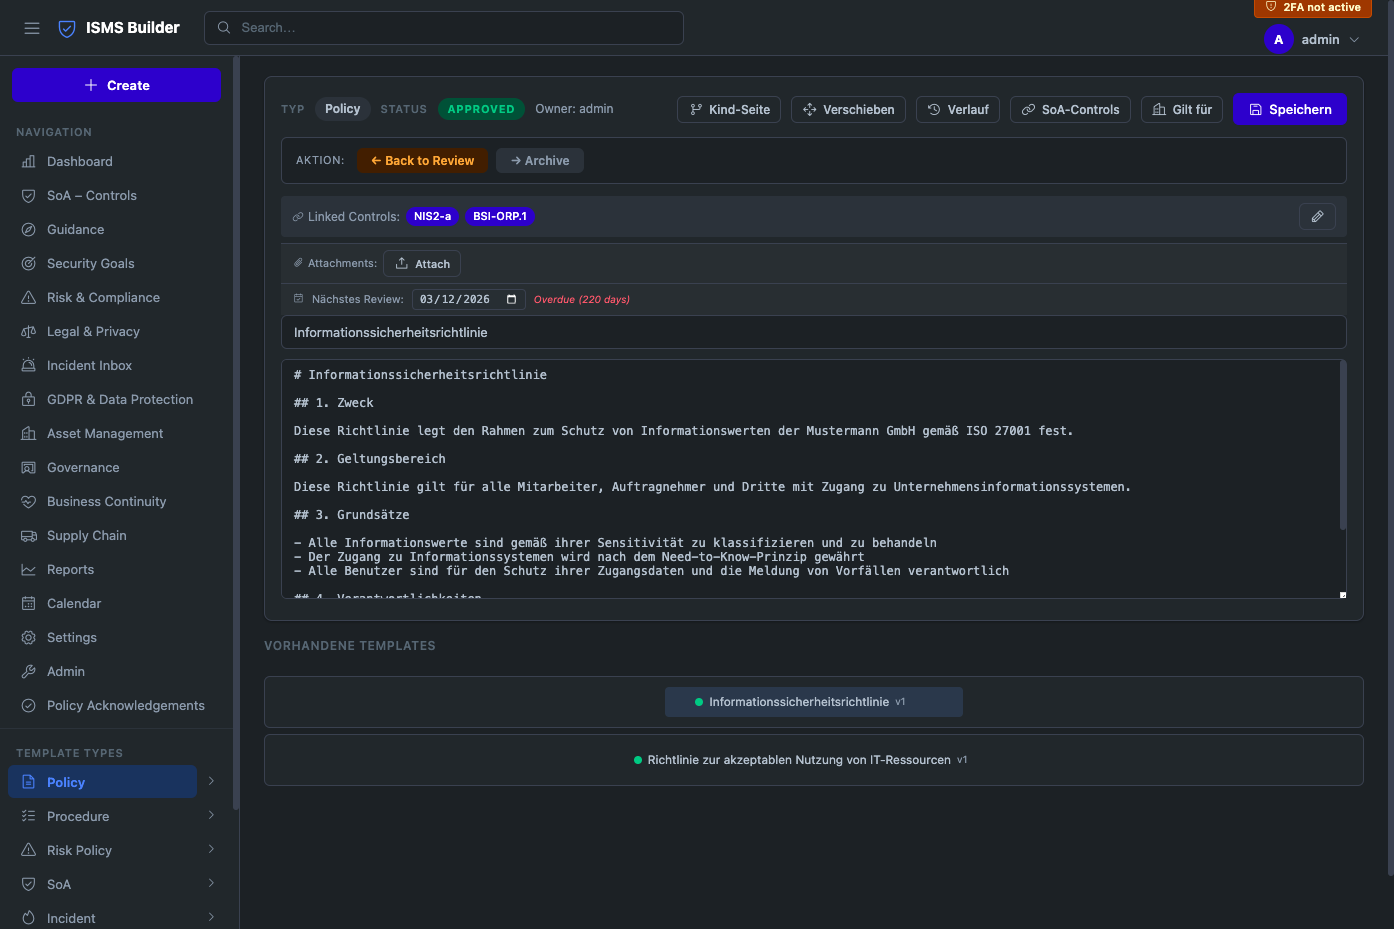
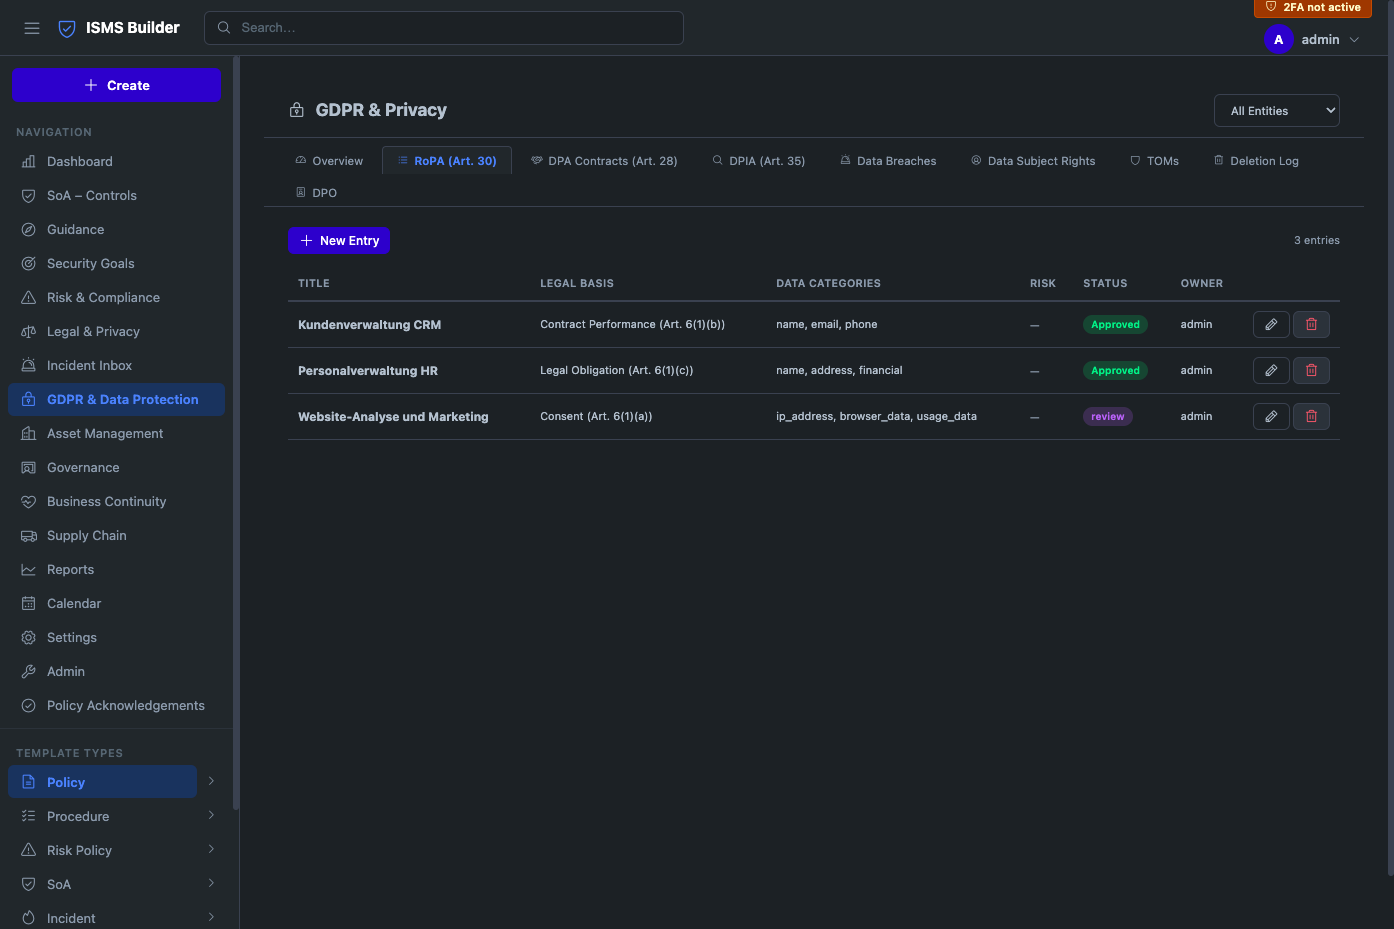
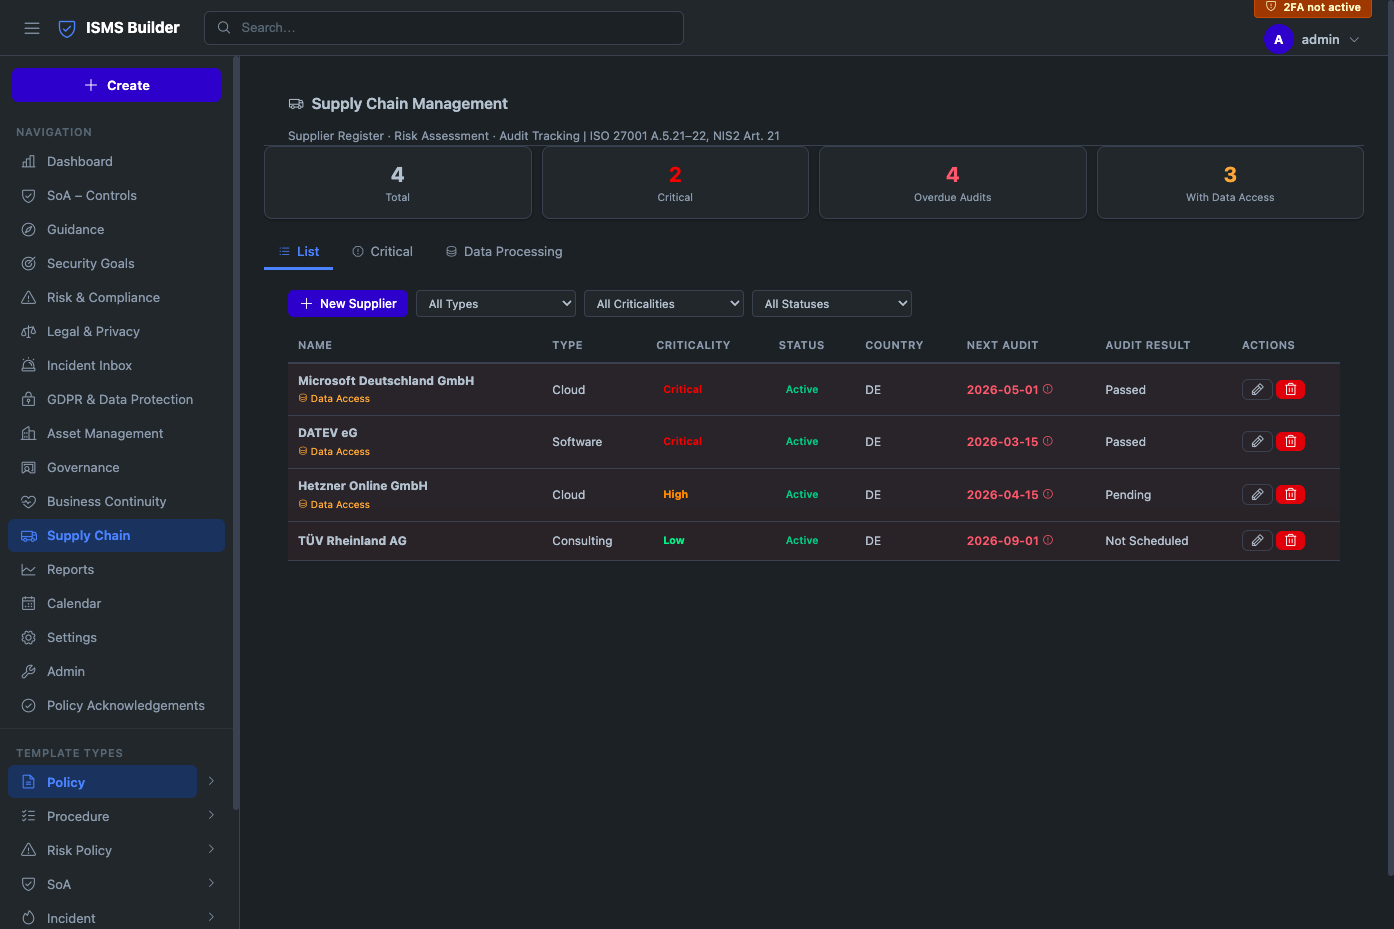
For teams that need ISO 27001, NIS2, and GDPR evidence without handing compliance data to a SaaS vendor, ISMS Builder is a self-hosted information security management system for policies, risks, assets, audits, and incidents. Compliance managers move policies from draft through review to approved and archived, and recipients confirm each one through a token link that needs no login. Security officers close gaps in a Statement of Applicability that cross-maps BSI IT-Grundschutz, NIS2, EUCS, the EU AI Act, and the Cyber Resilience Act, with ISO 27001 controls imported from their own licensed copy. Risk owners keep treatment plans, turn Greenbone and OpenVAS reports into risk drafts, and score assets for confidentiality, integrity, availability, and authenticity. Data protection officers run records of processing, processor agreements, impact assessments, data subject requests, a 72-hour timer, and a deletion log with email alerts. The CISO inbox collects incidents, including reports from a public form that needs no login, beside a 30-item NIS2 Article 21 checklist and Article 23 deadline alerts. Auditors work from a findings register, a compliance matrix, and an exportable audit log of every create, update, delete, and login. Administrators enforce TOTP two-factor sign-in, choose among German, English, French, and Dutch, run semantic search locally through Ollama, and publish approved policies to Nextcloud or ownCloud as PDFs. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Benefits
- Keep Compliance Data On Your Server
- Policies, risks, evidence, and audit logs stay on your own server with no subscription, and semantic search can run locally through Ollama with a keyword fallback.
- See Gaps Across Every Framework
- Cross-mapping and gap analysis connect BSI IT-Grundschutz, NIS2, EUCS, EU AI Act, and CRA controls, while every record links to SoA controls and policy documents in both directions.
- Start Without A Database Server
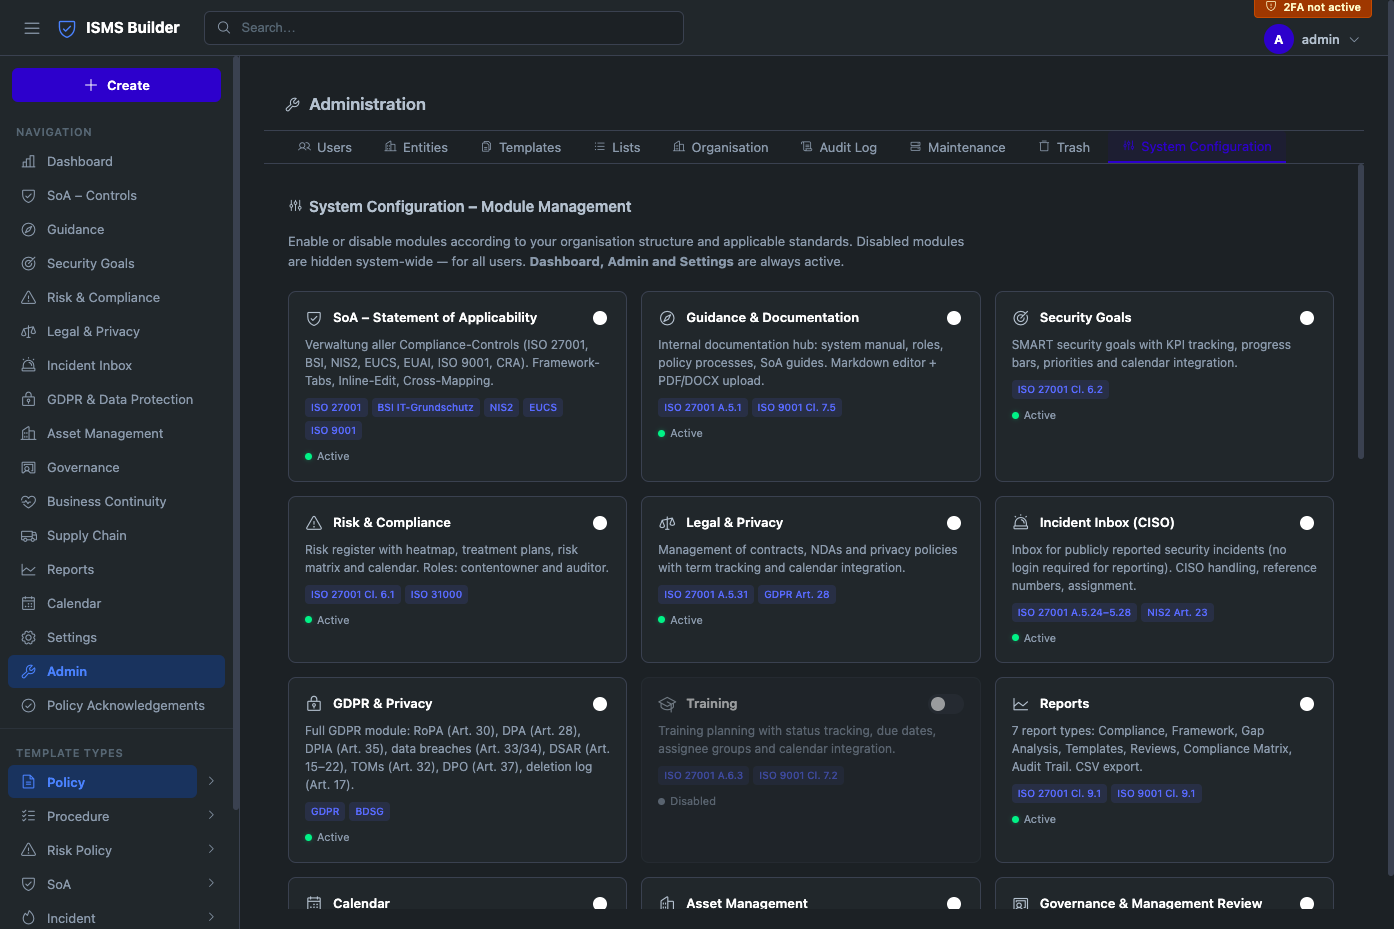
- The container starts with plain JSON files and no database server to run, while SQLite, PostgreSQL, or MariaDB storage can be switched on through environment variables for production use.
- Meet NIS2 And GDPR Deadlines
- Automatic alerts track NIS2 Article 23 reporting deadlines, GDPR tools add a 72-hour timer and deletion-log email alerts, and a public form lets anyone report an incident without logging in.
Features
- Policy Lifecycle And Acknowledgement
- Versioned policy templates move through draft, review, approved, and archived states with space hierarchy and attachments, while token-link acknowledgements need no login and keep an audit trail.
- Multi-Framework Statement Of Applicability
- Inline-editable controls across BSI IT-Grundschutz, NIS2, EUCS, EU AI Act, and CRA, plus gap analysis and cross-mapping; ISO 27001 controls load from your licensed JSON via an import script.
- Risk And Asset Registers
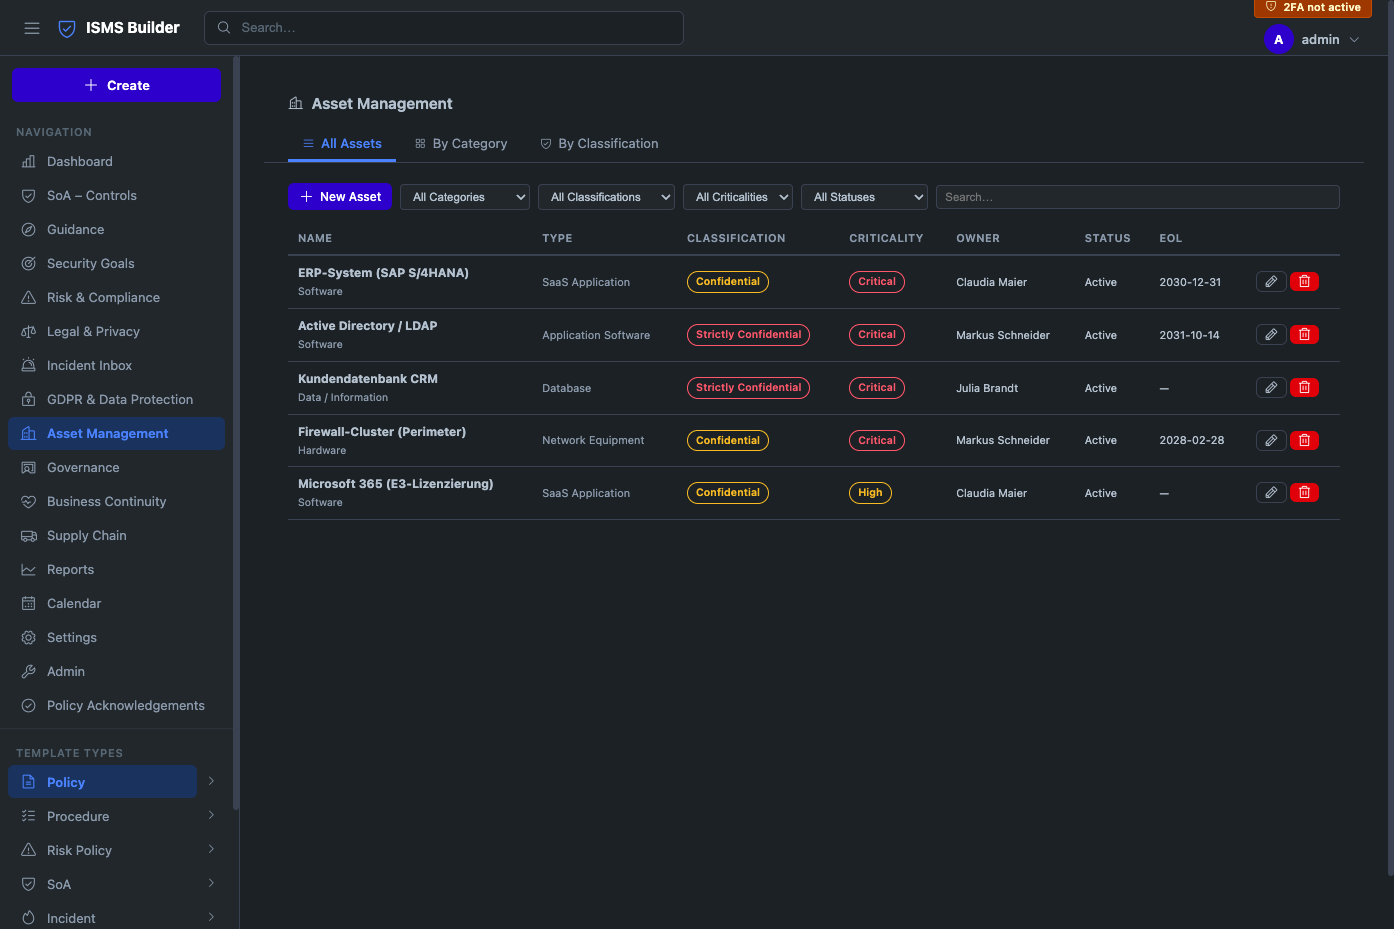
- Risk treatment plans and an auditor role sit beside an asset register with CIA plus authenticity protection goals, dependency inheritance, classification levels, and end-of-life tracking.
- GDPR And NIS2 Workflows
- Records of processing, processor agreements, DPIAs, TOMs, data subject requests, and breach tracking sit beside a 30-item NIS2 Article 21 checklist and Article 23 deadline alerts.
- Scanner Import And Findings
- Greenbone and OpenVAS XML or PDF reports become risk drafts, and a findings register tracks actual versus target gaps, recommendations, and action plans under FIND-YYYY-NNNN references.
- Secure Access And Audit Log
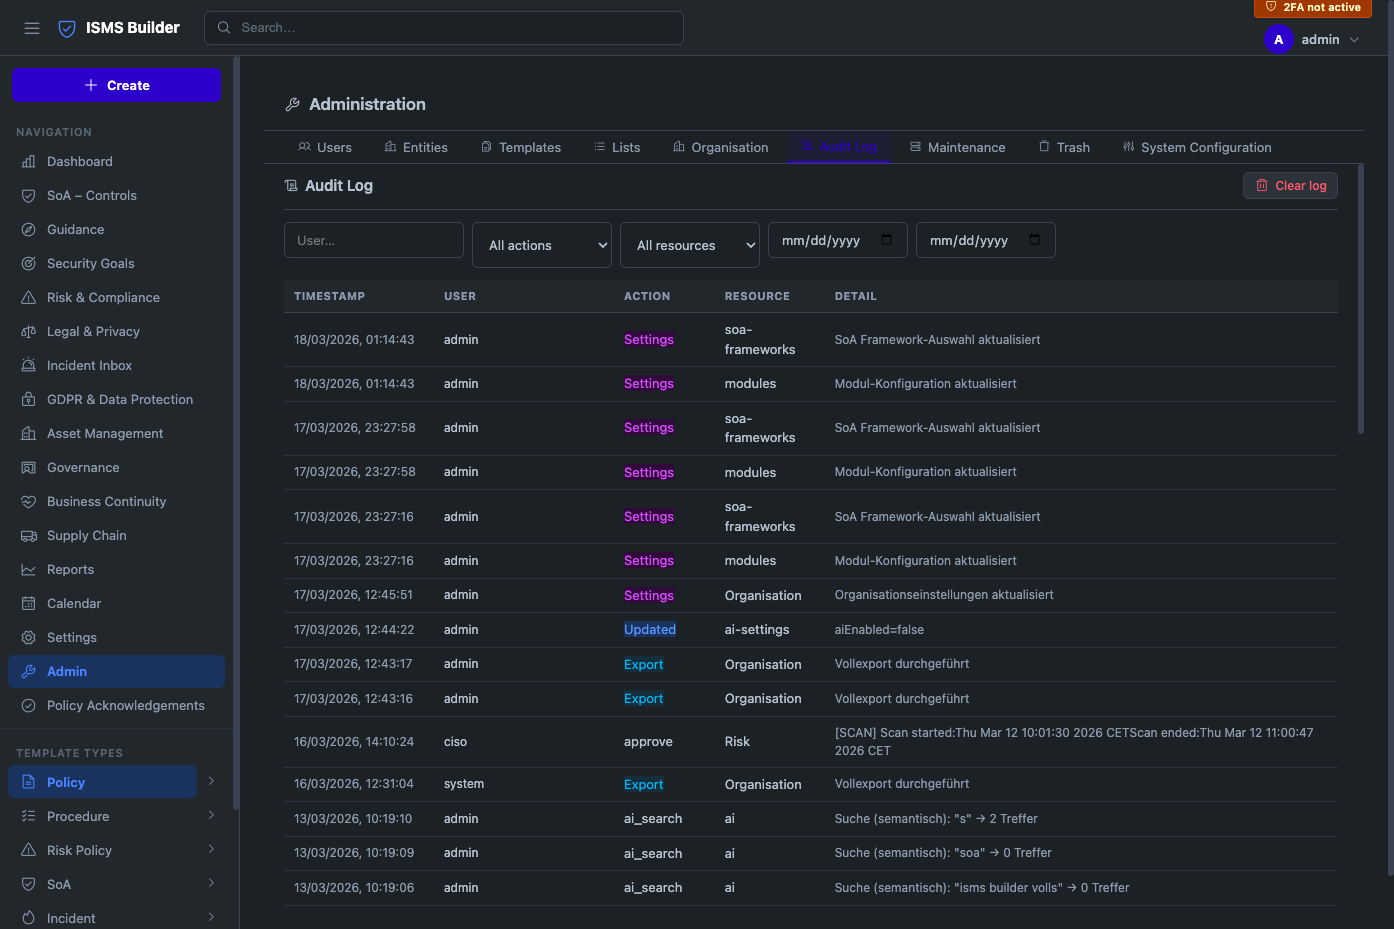
- JWT cookie sessions with bcrypt hashing, TOTP two-factor authentication enforceable organization-wide, six user roles, and a filterable, exportable audit log of every create, update, delete, and login.