Categories
Self-Hosted Security Monitoring Threat Hunting CVE Tracking Cyber Threat Intelligence Brand Protection AI Threat Analysis Data Leak DetectionStars
Forks
Watchers
Developer links
Watcher
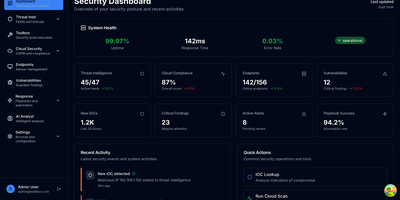
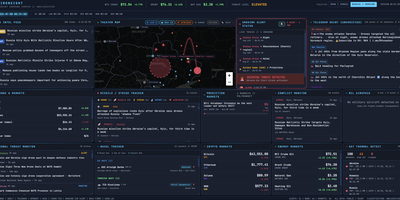
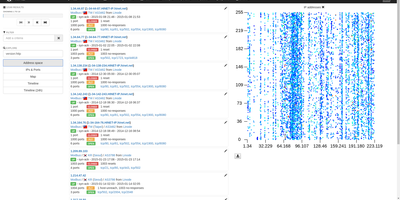
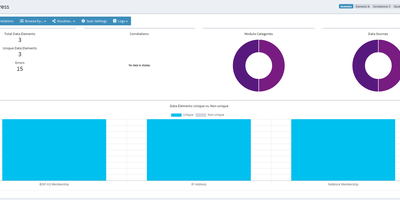
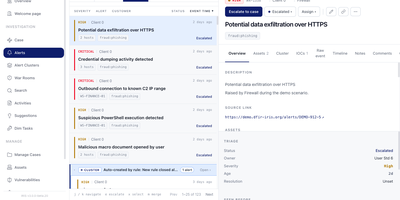
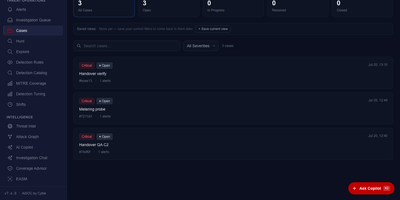
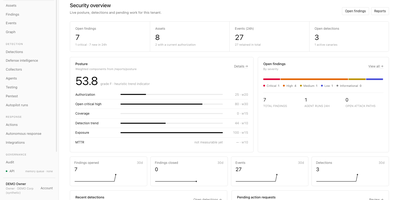
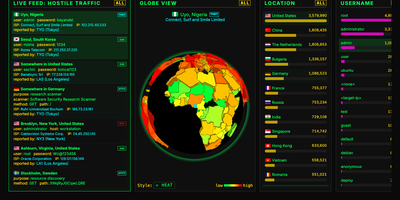
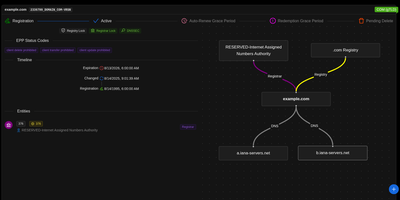
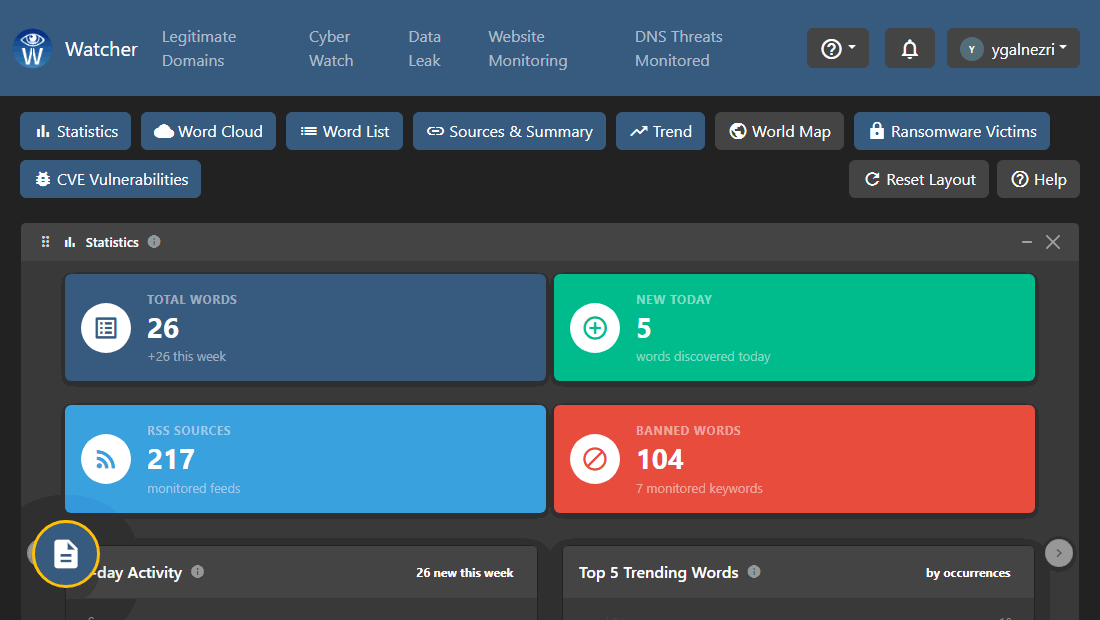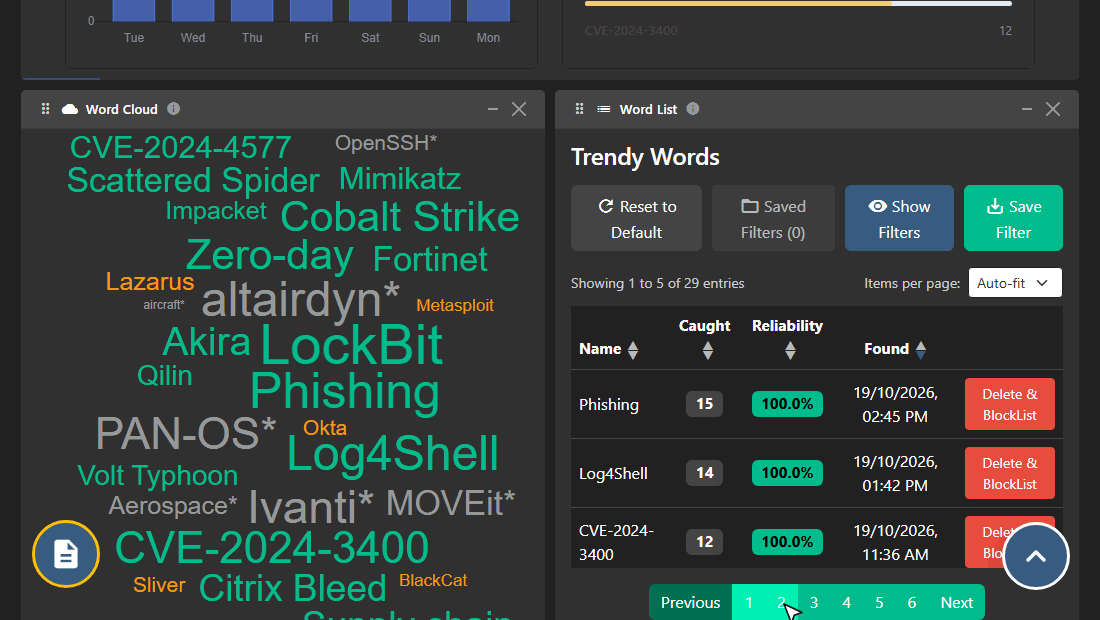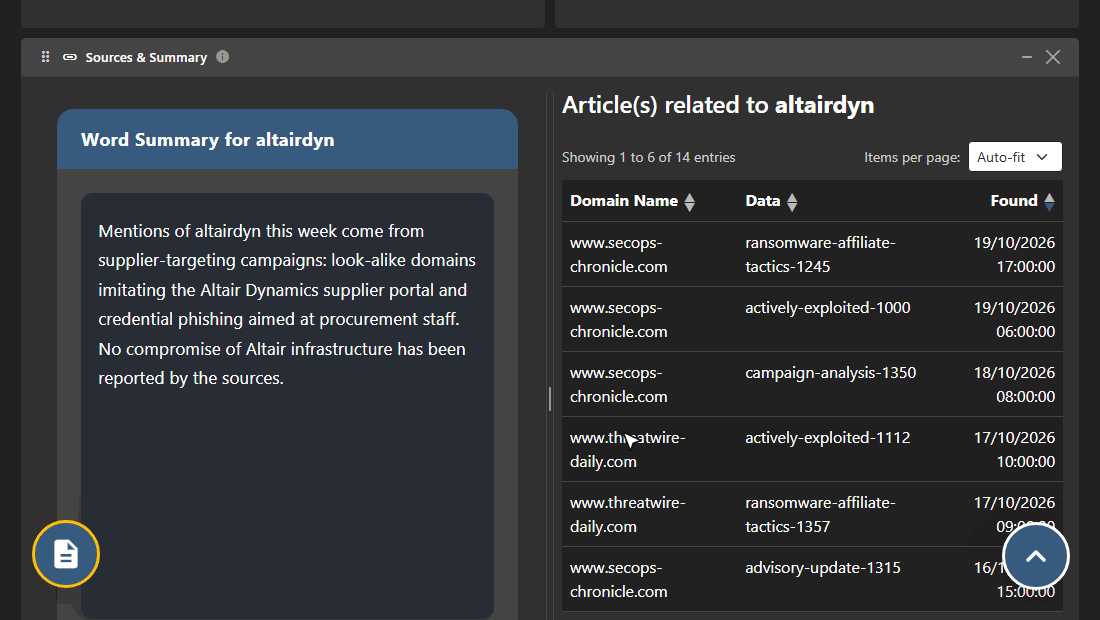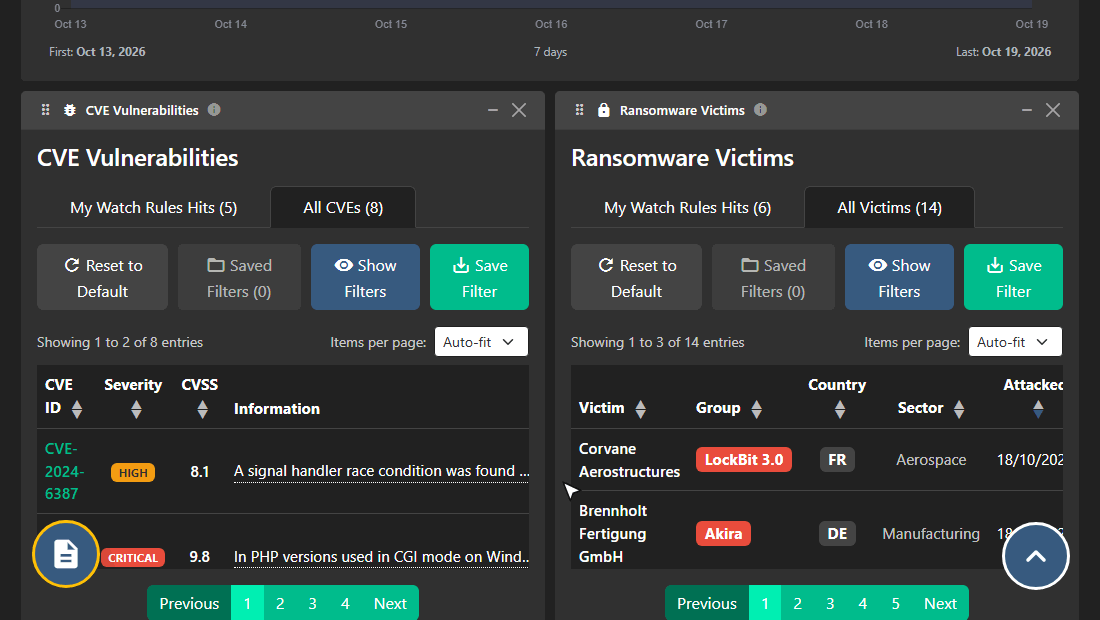
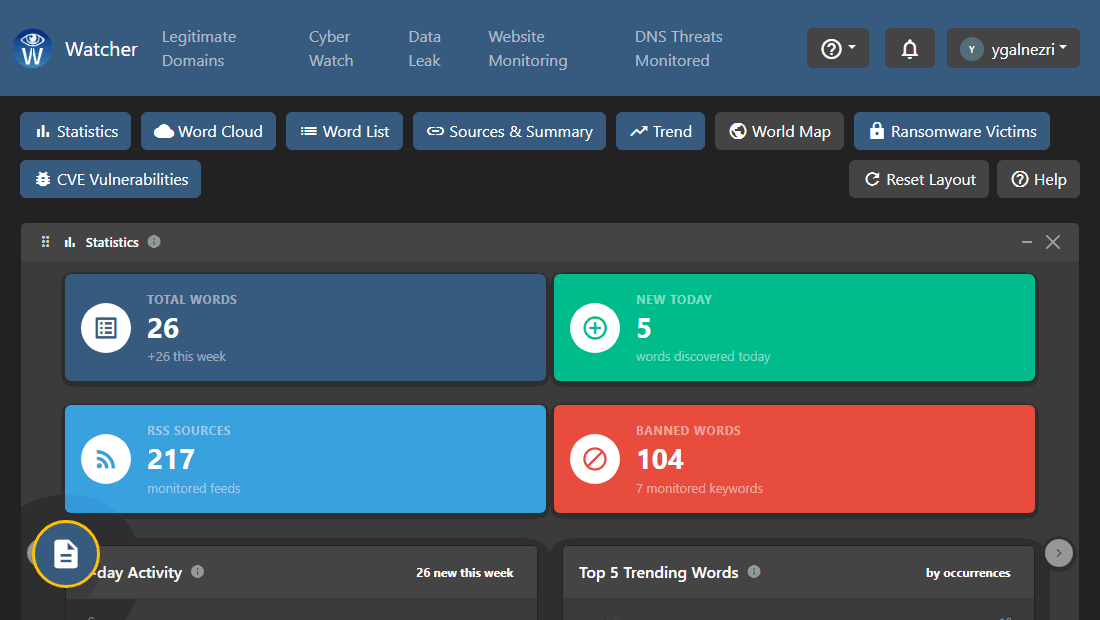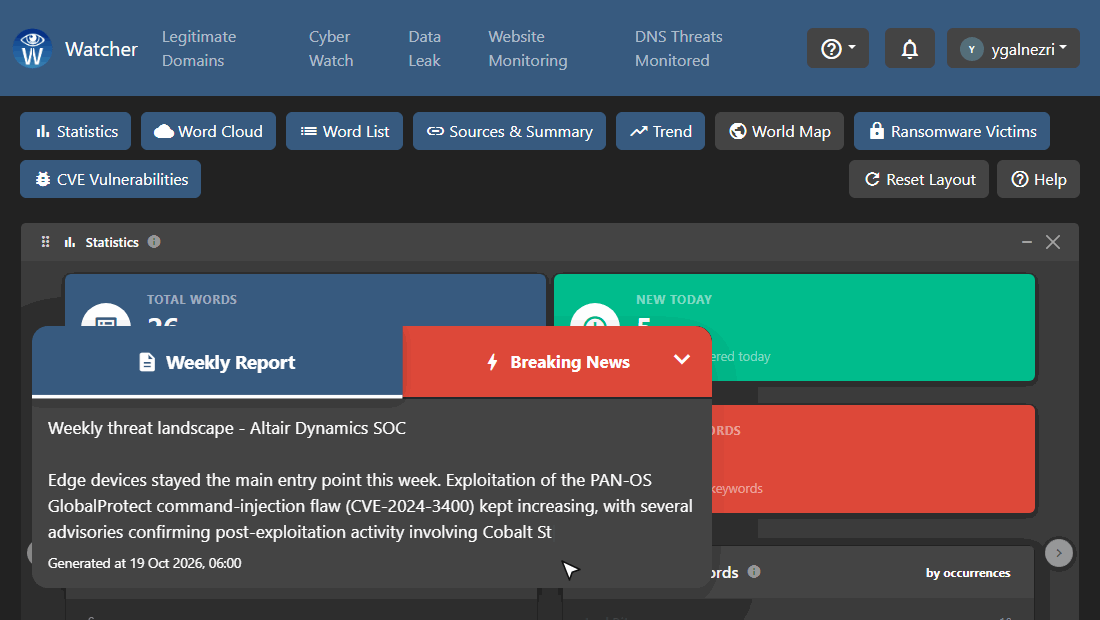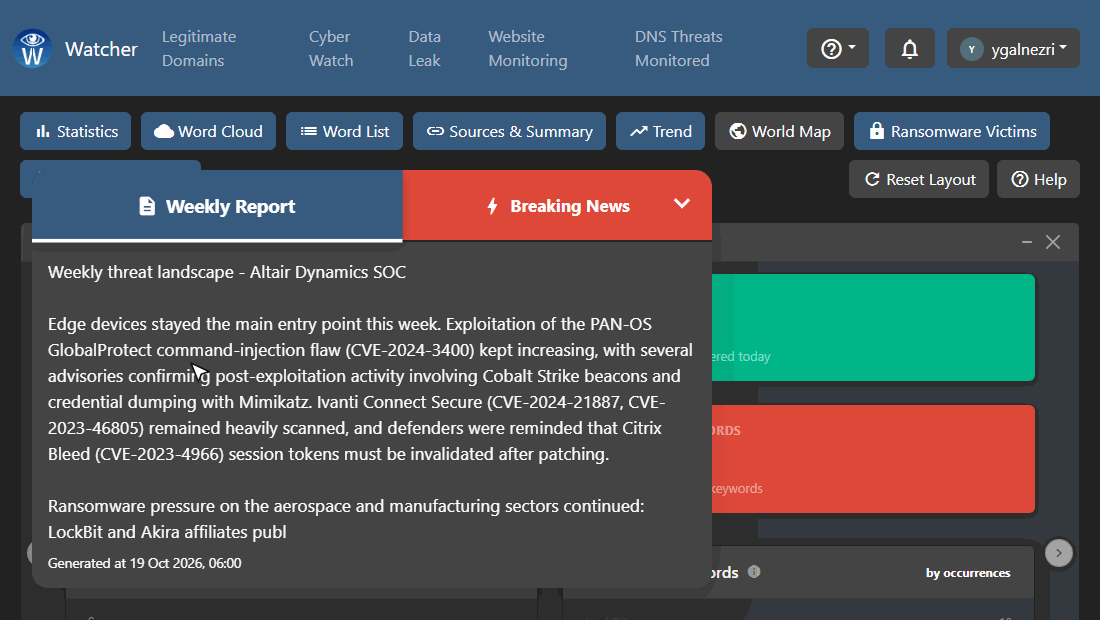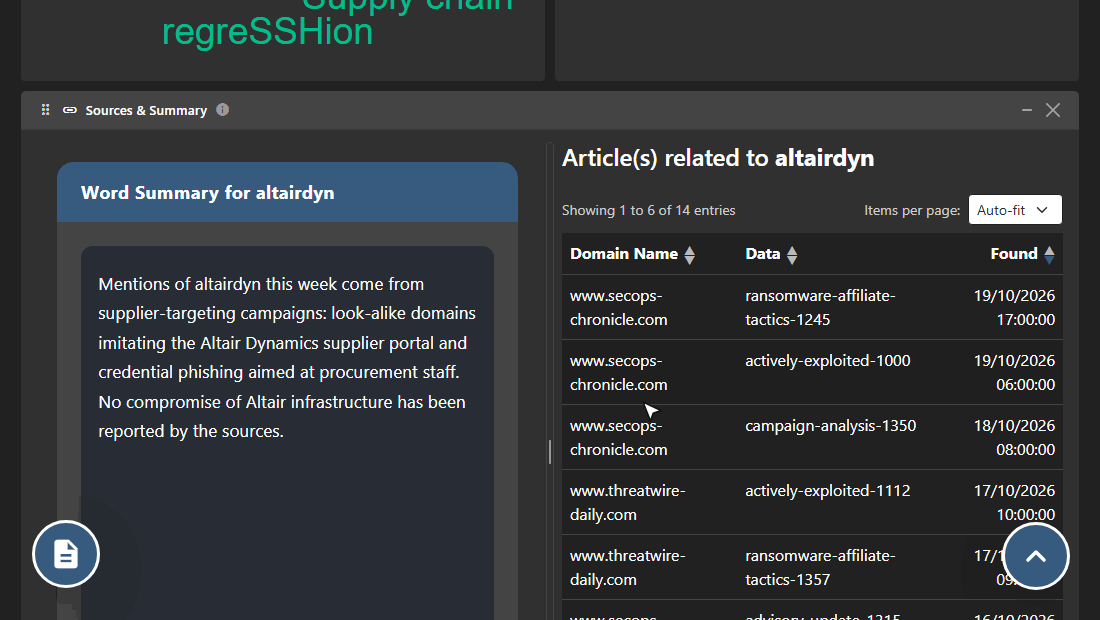
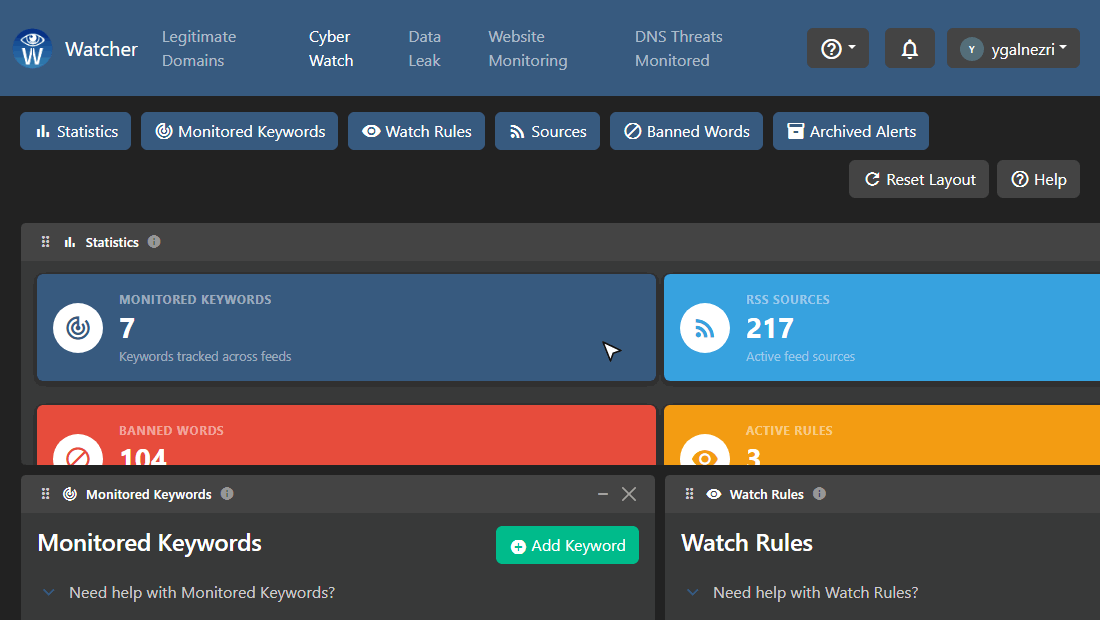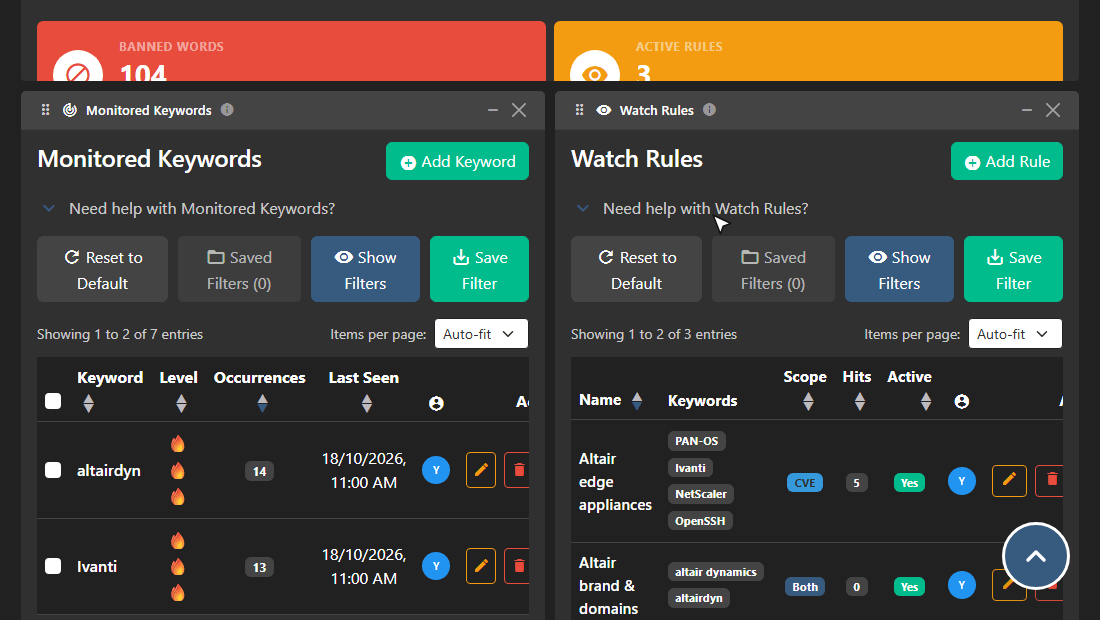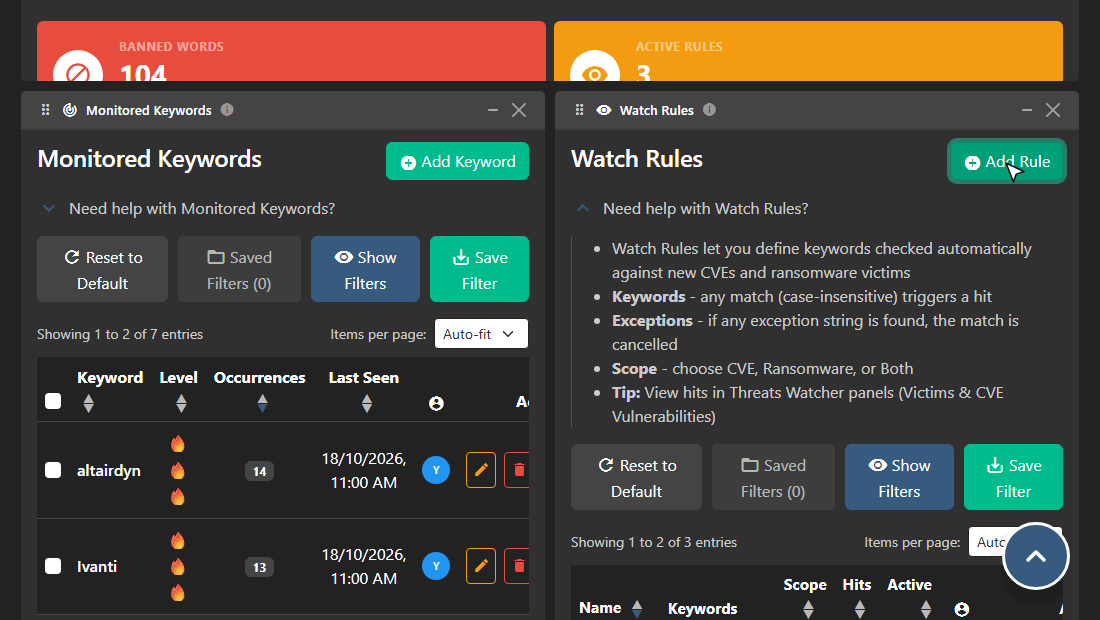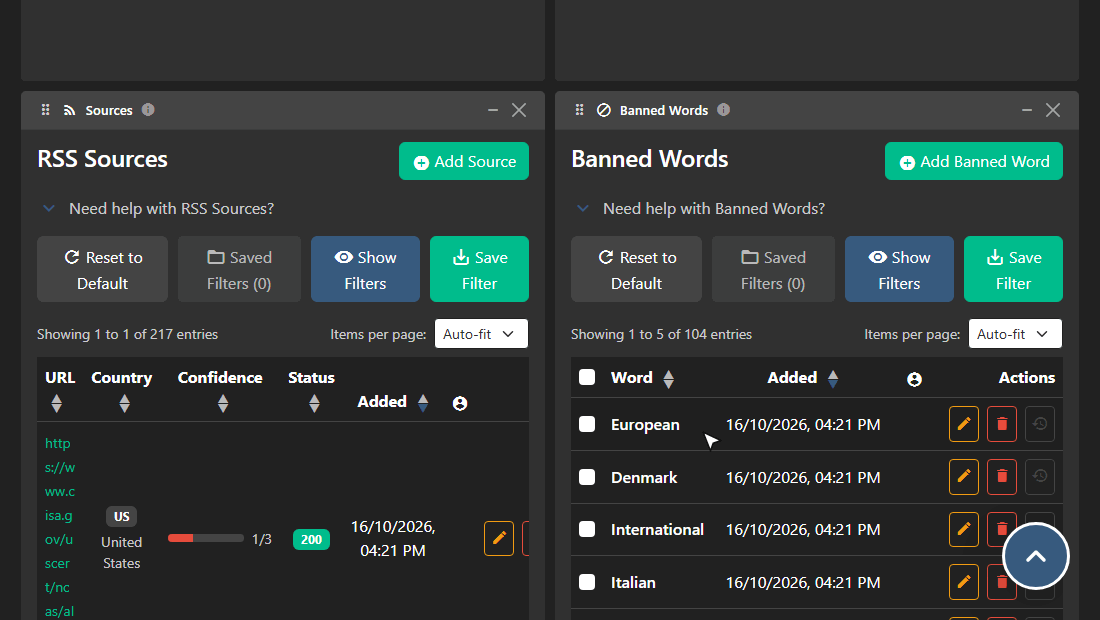
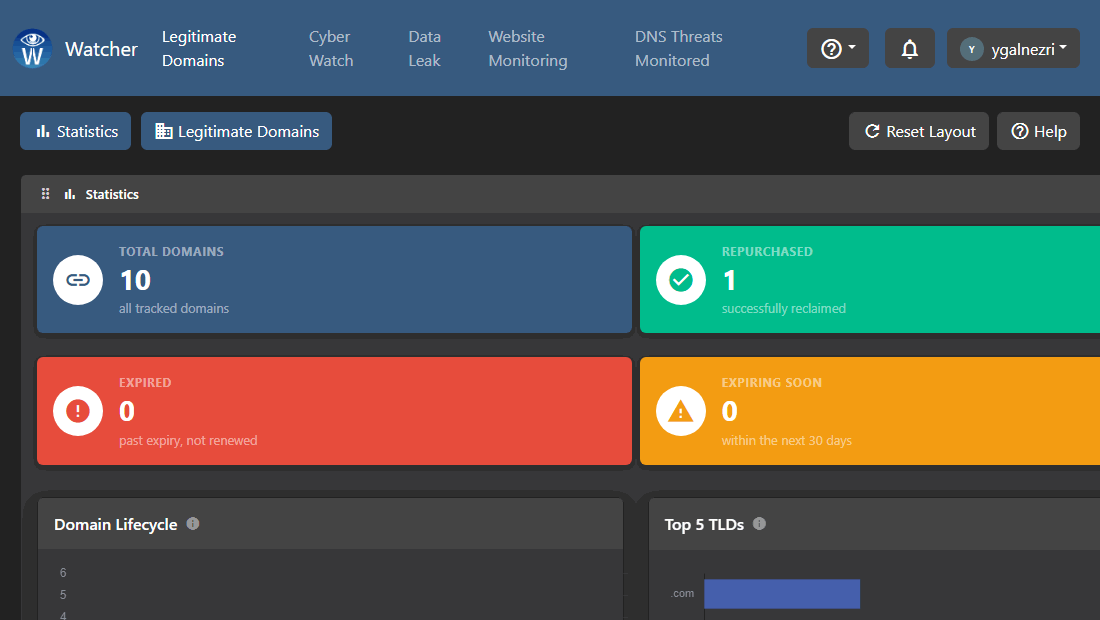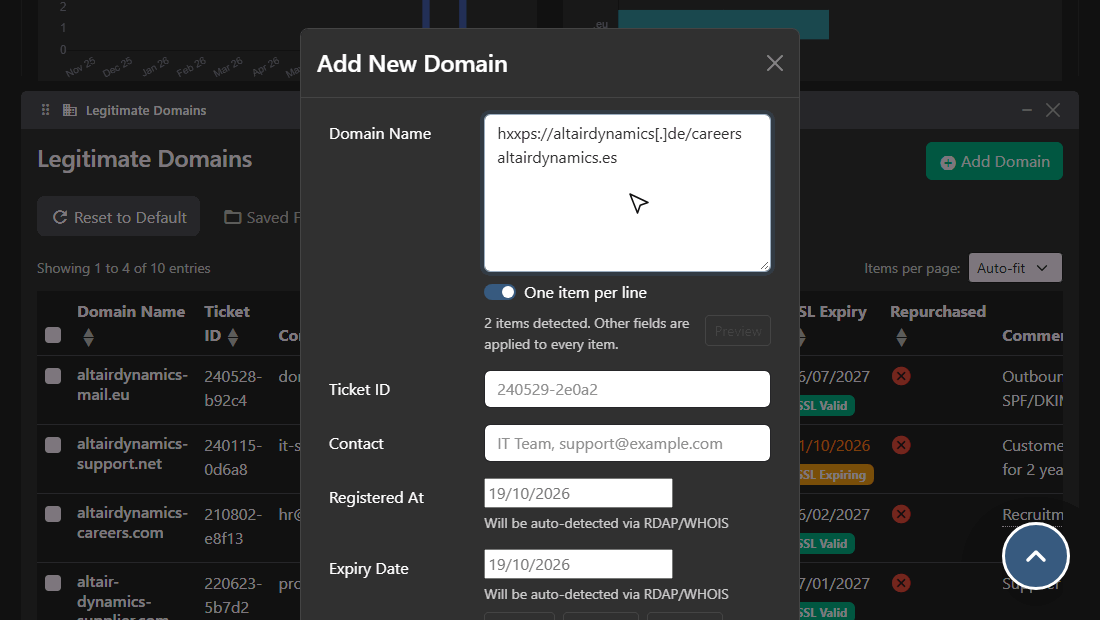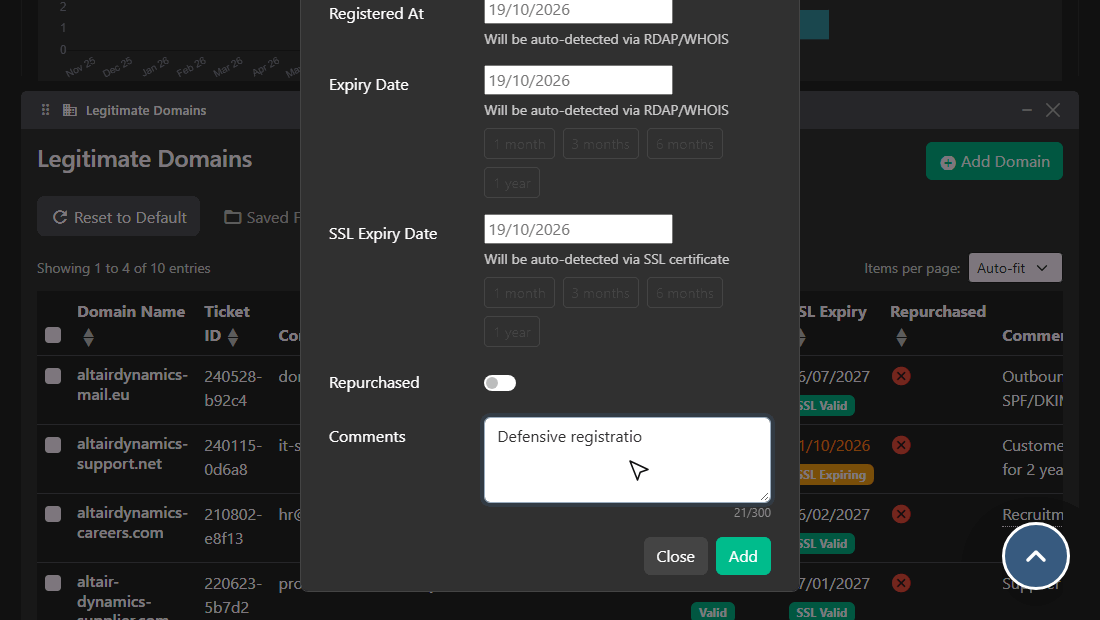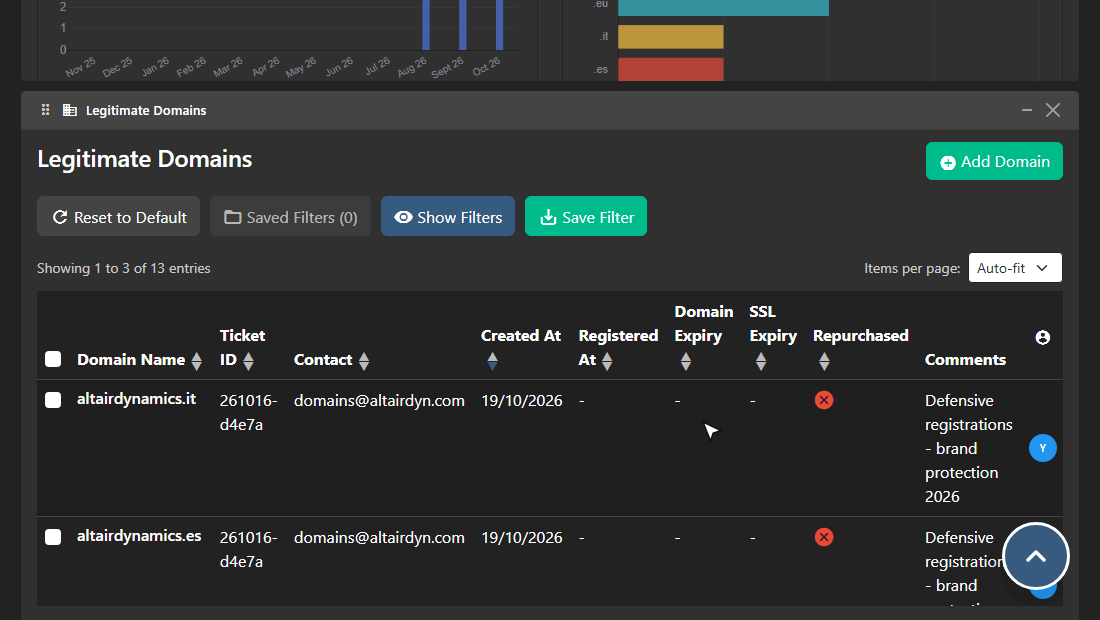
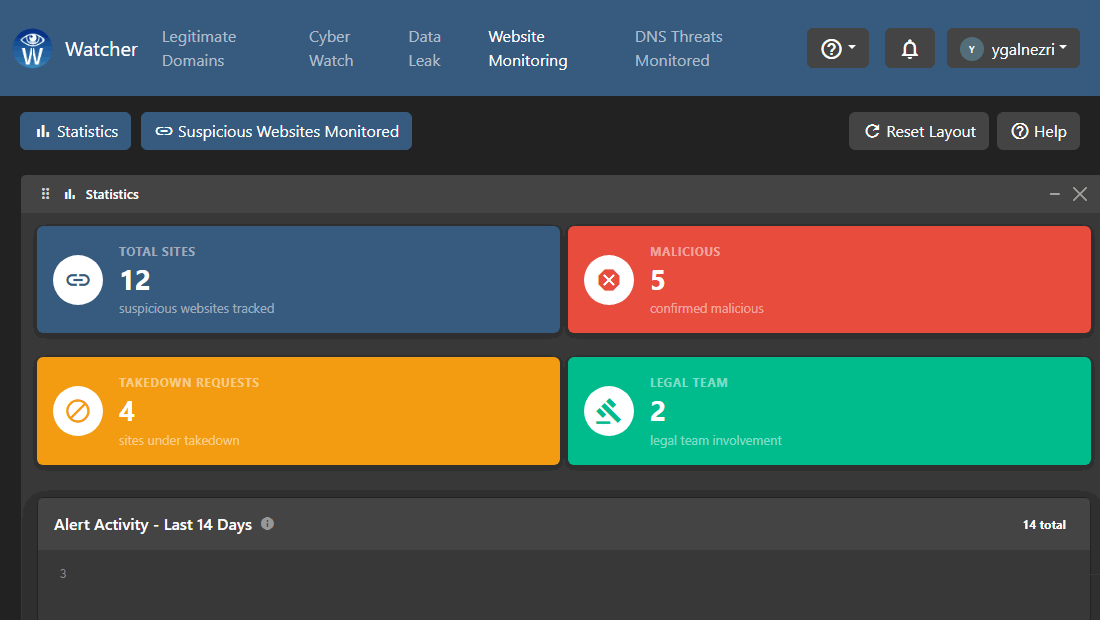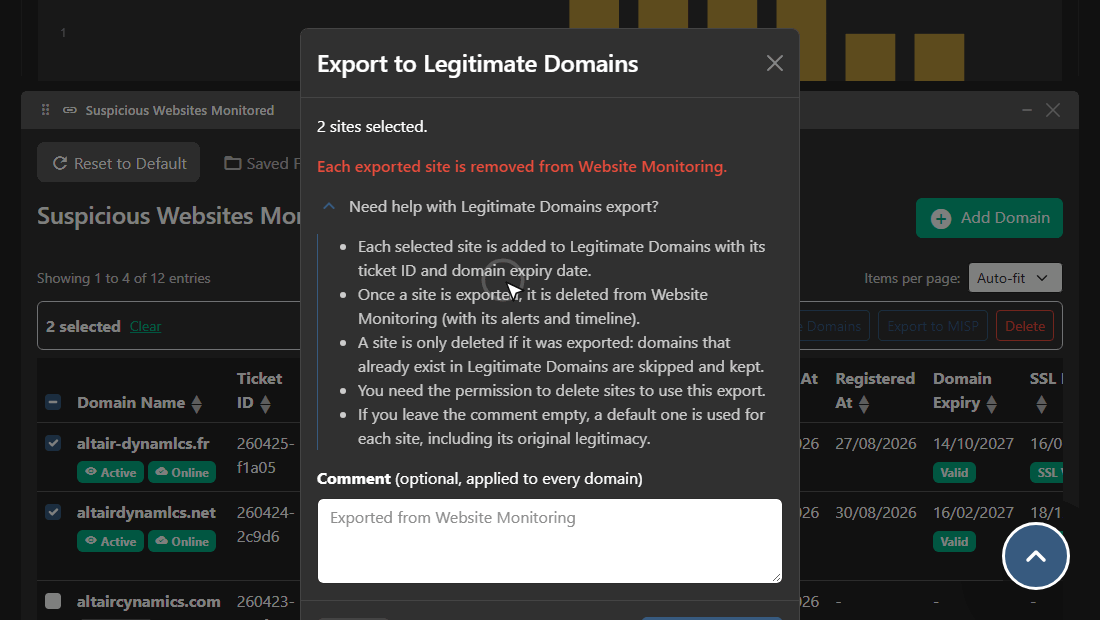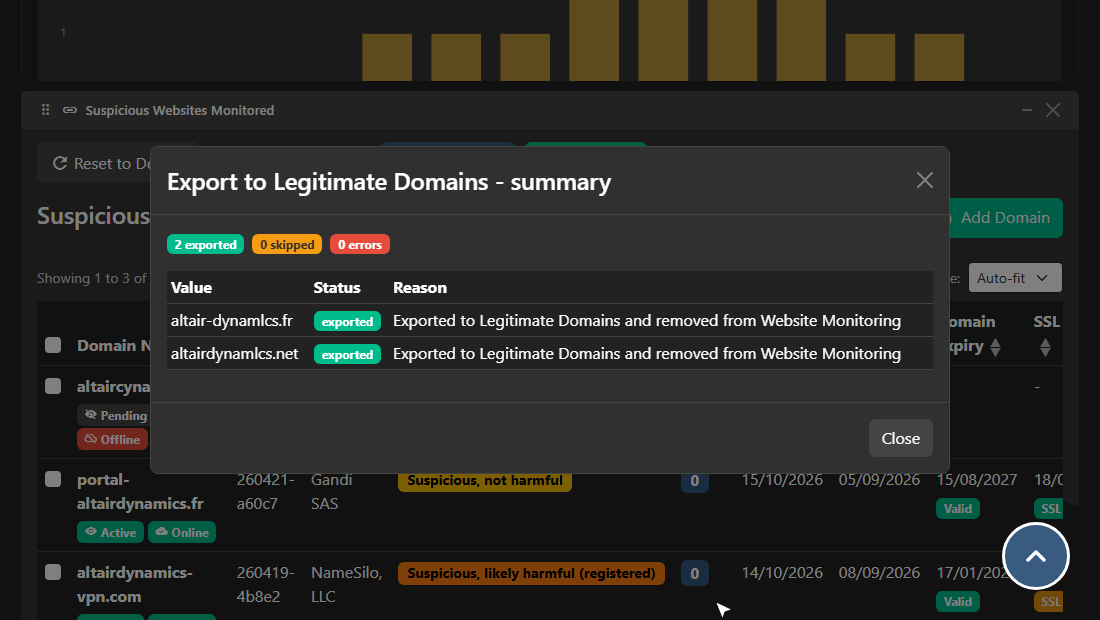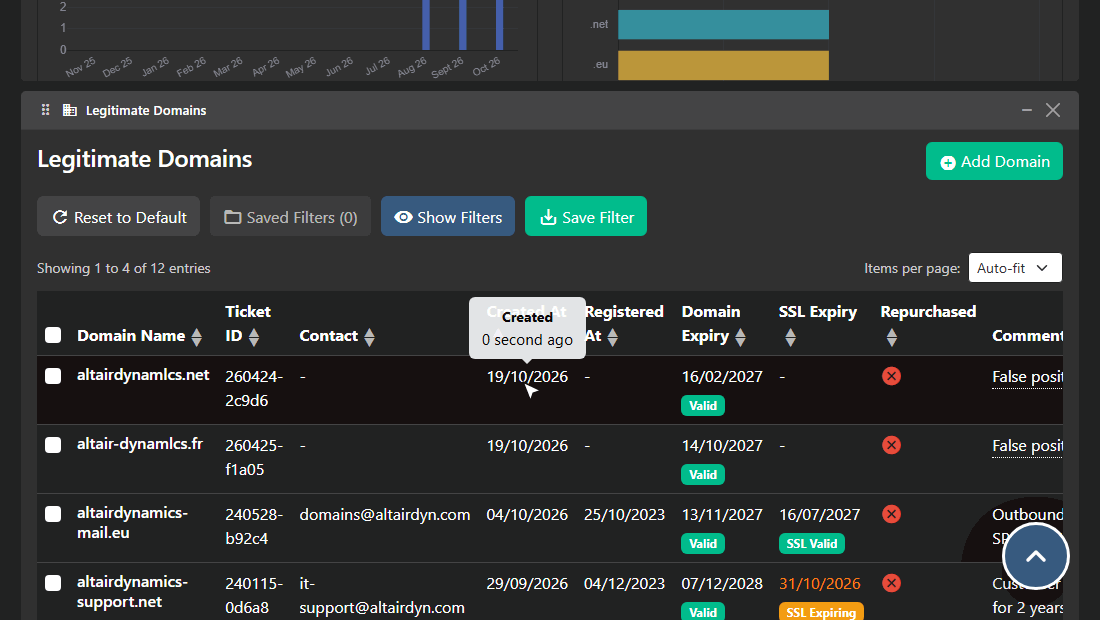
Six cyber threat monitoring modules share one dashboard in Watcher, covering trending advisories, CVEs and ransomware victims, leaked credentials, suspicious websites, DNS lookalikes, and approved domains. Threats Watcher reads RSS advisories from CERT-FR, CERT-EU, US-CERT, and the Australian Cyber Security Centre, ranks trending words, and raises a breaking-news alert when a keyword crosses a configurable threshold. An AI weekly digest condenses the top five topics, and on-demand summaries list the CVEs, threat actors, and organizations behind any keyword. Cyber Watch matches your watch rules against CVE and ransomware feeds from cve.circl.lu, ransomware.live, and ransomlook.io. Data Leak searches Pastebin, StackOverflow, GitHub, GitLab, Bitbucket, APKMirror, and npm for credentials and API keys matching your patterns. Website Monitoring tracks malicious domains for IP, mail record, and page-content changes using TLSH fuzzy hashes plus RDAP and WHOIS expiry checks, while DNS Threats hunts typosquatting and homograph lookalikes with dnstwist and Certificate Transparency streams. The Legitimate Domains register stores registrar, expiry, repurchase status, and UDRP cases, with a one-item-per-line bulk add that previews results before saving. Findings export to TheHive and MISP, alerts arrive by email, Slack, or Citadel, and sign-in works through LDAP, local accounts, or OpenID Connect. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Benefits
- Spot Brand Abuse Before Customers
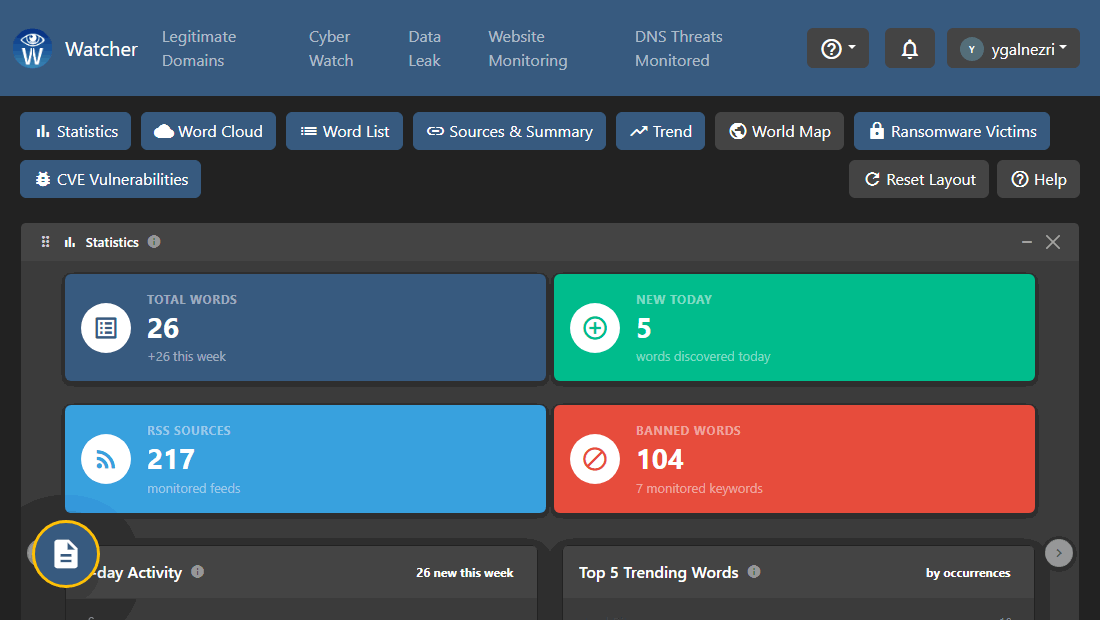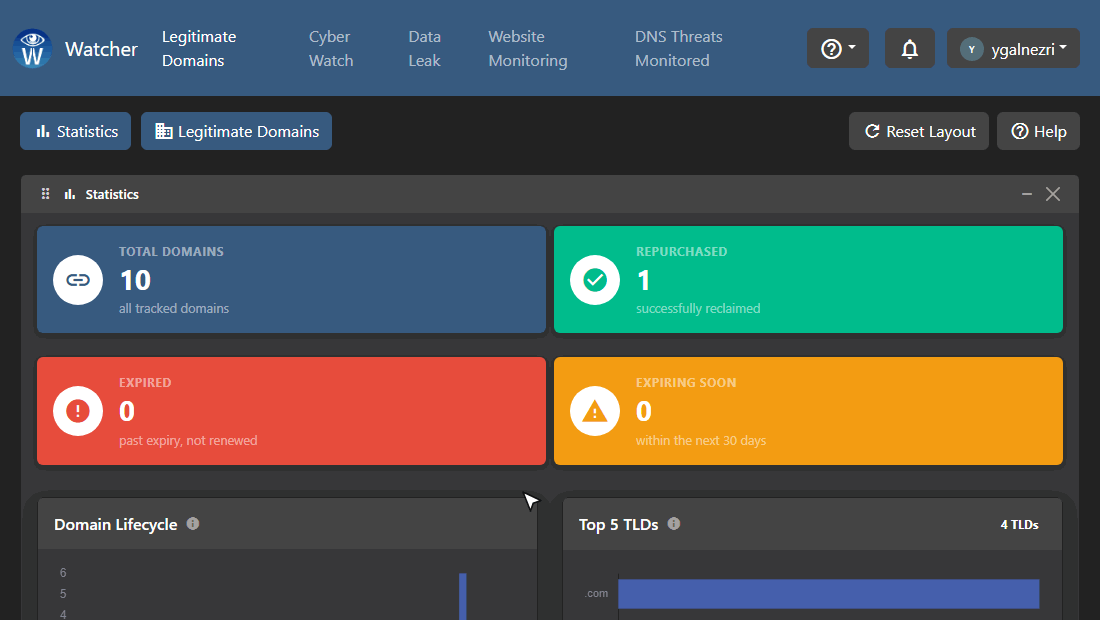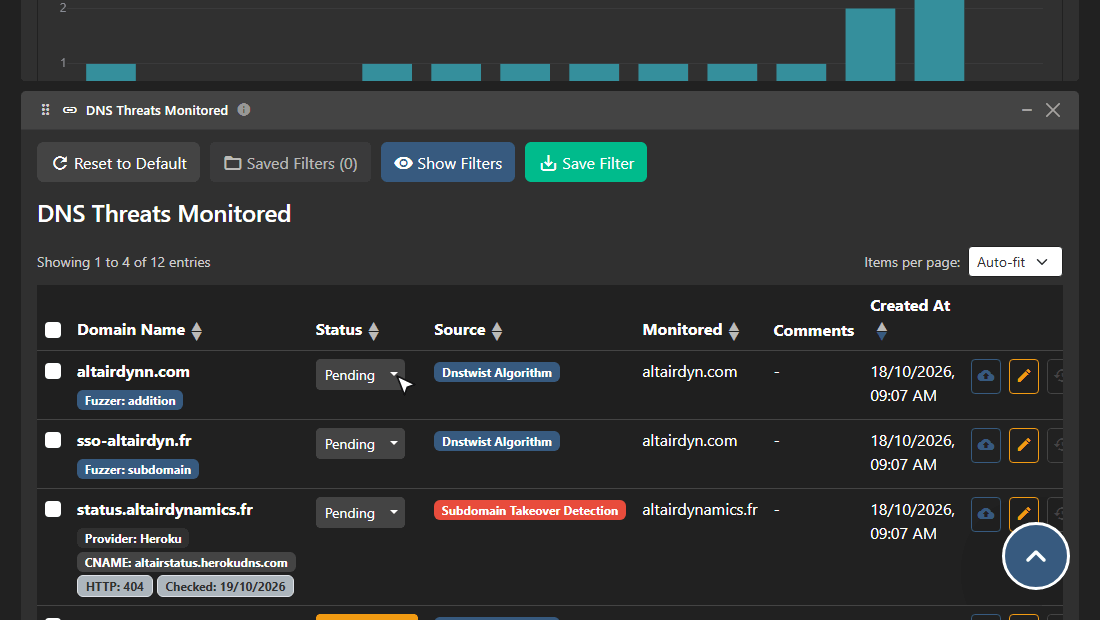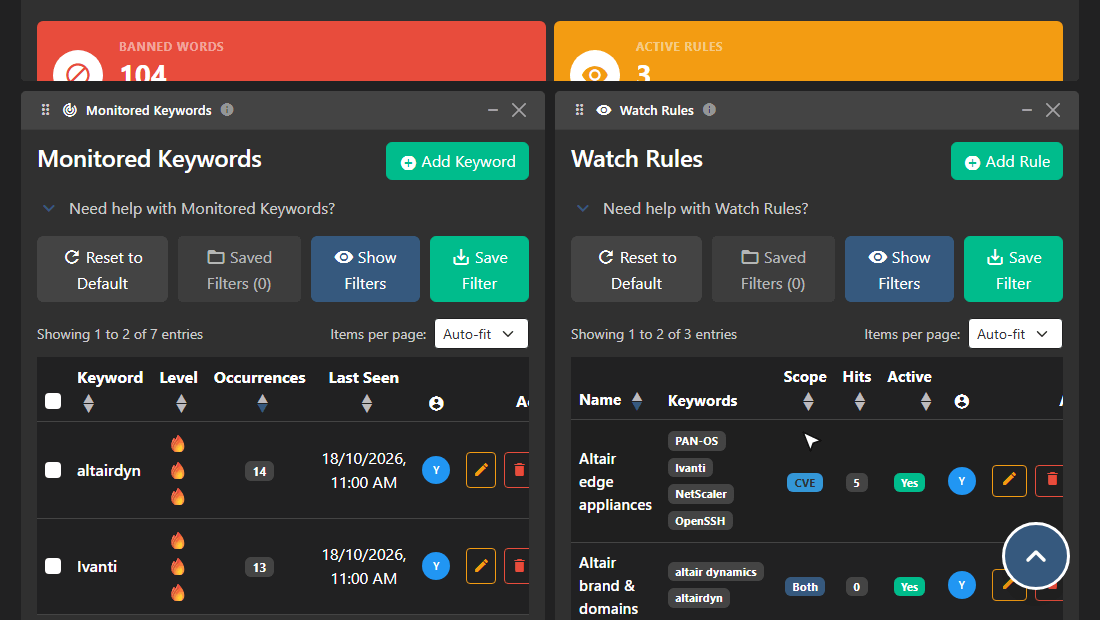
- Certificate Transparency monitoring and dnstwist permutations surface typosquatted and homograph domains as they appear, with takeover and legal-team flags so analysts can act before phishing campaigns reach customers.
- Turn Feed Noise Into Summaries
- A Hugging Face model writes the weekly top-five digest and keyword summaries that name related CVEs, threat actors, and organizations, so analysts read one paragraph instead of dozens of advisories.
- Catch Leaked Secrets Early
- Search patterns scan Pastebin, GitHub, GitLab, Bitbucket, StackOverflow, npm, and APKMirror for credentials and API keys, then queue alerts you can bulk-archive or pass to a ticketing system.
- Plug Into Your Security Stack
- TheHive cases, MISP indicator exports, and email, Slack, or Citadel notifications connect Watcher to existing workflows, while LDAP or OIDC single sign-on and group permissions keep access controlled.
Features
- Threat Trend Dashboard
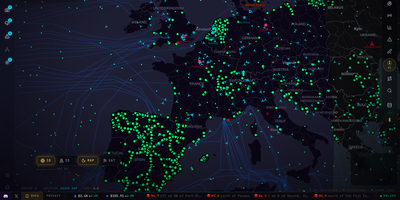
- Word cloud, trending-word list, trend chart, world map, CVE table, and ransomware victim table fill from advisories and feeds, with resizable panels and a layout saved in your profile.
- AI Threat Summaries
- Hugging Face flan-t5-base writes summaries and dslim/bert-base-NER extracts entities, producing weekly digests, breaking-news alerts, and on-demand keyword briefings with CVEs and threat actors.
- Lookalike Domain Detection
- dnstwist permutations and CertStream Certificate Transparency monitoring flag typosquatted domains, with status tracking from pending to confirmed, subdomain takeover checks, and export to monitoring or approved lists.
- Data Leak Search Patterns
- Search patterns query paste sites and code registries with SearXNG as the metasearch engine, creating alerts with source links and bulk status changes that end in a per-item summary.
- Connectors And Integrations
- A superuser Connectors page edits and health-checks SMTP, Slack, Citadel, TheHive, MISP, LDAP, OIDC, CertStream, and SearXNG settings, with credentials stored encrypted.
- Docker Compose Deployment
- Make targets initialize configuration, start the stack, run migrations, create a superuser, and seed data, while the web interface listens on port 9002 behind a Traefik TLS reverse proxy.