Categories
self-hosted soar siem cybersecurity threat-intelligence incident-response security-operationsStars
Forks
Watchers
Developer links
AiSOC
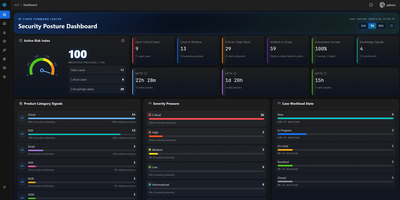
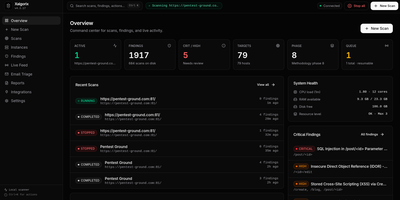
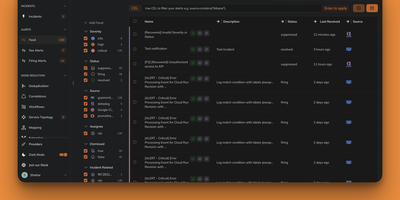
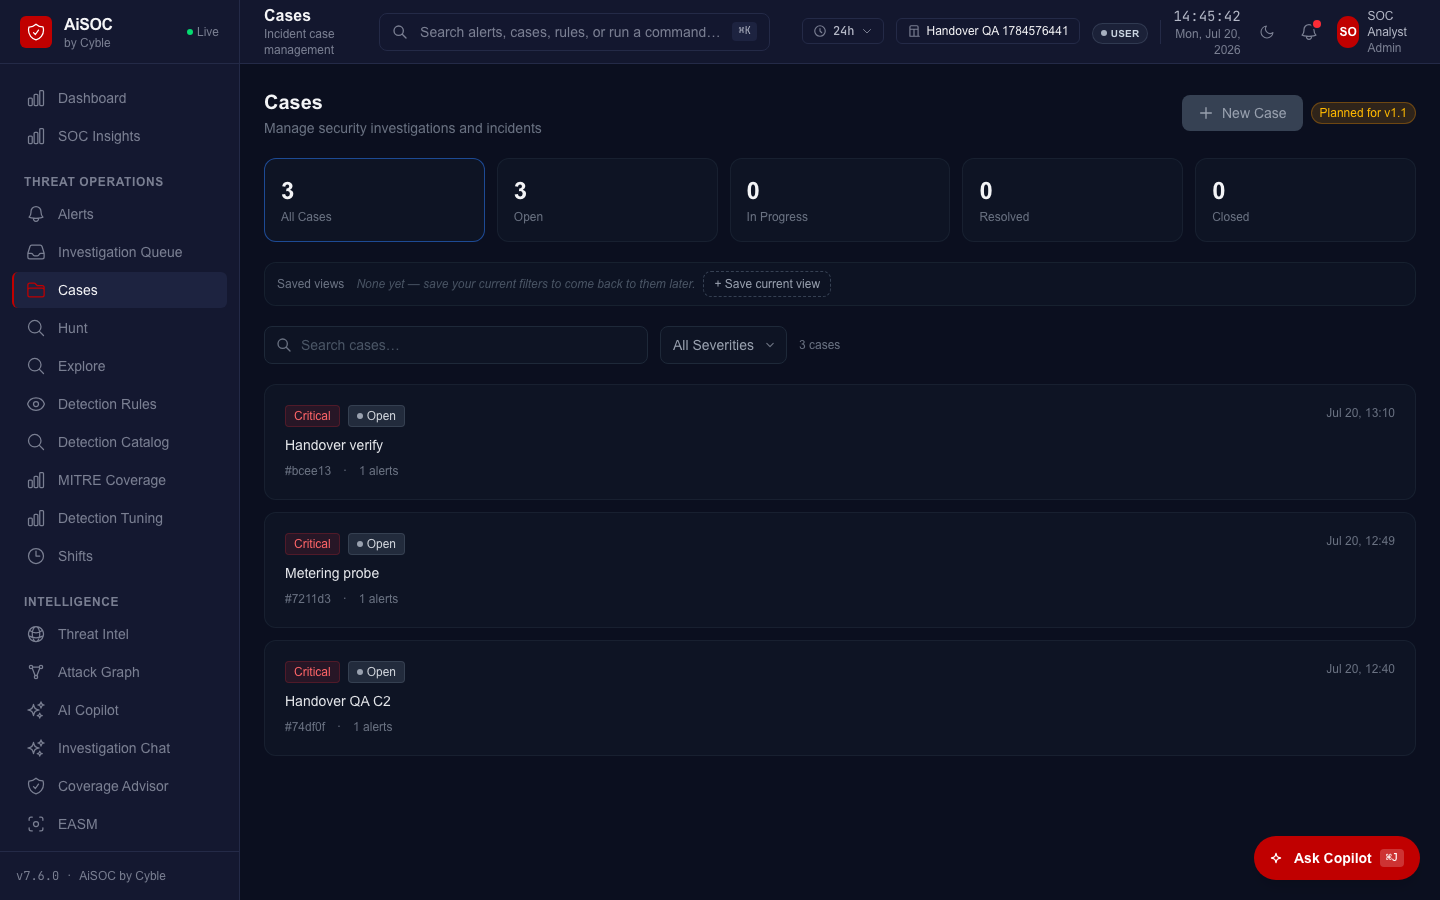
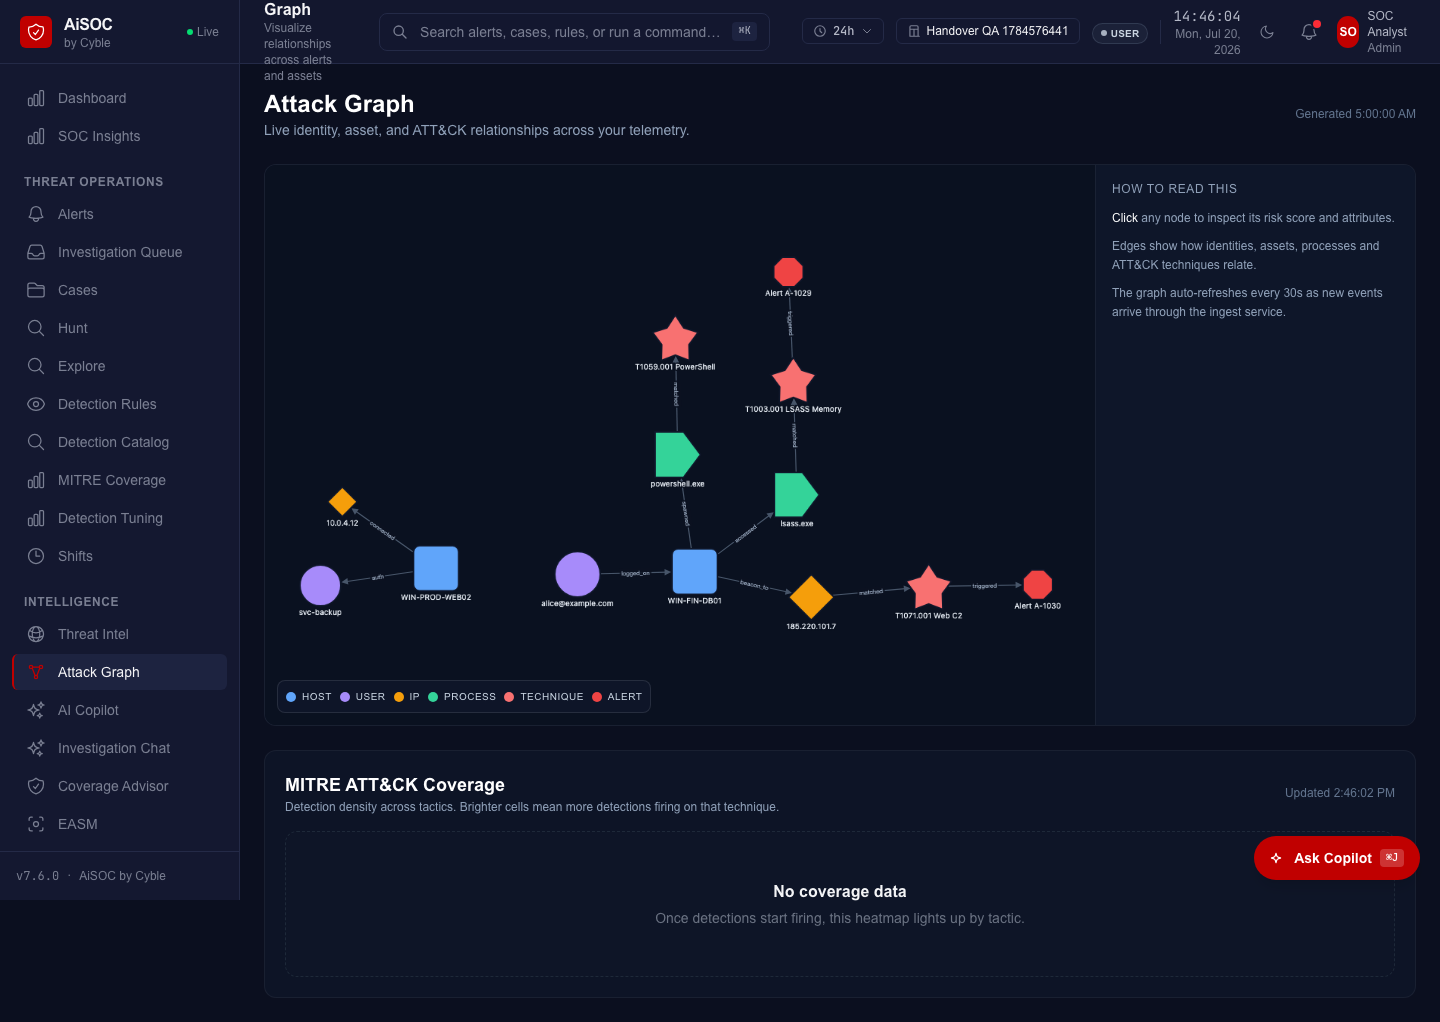
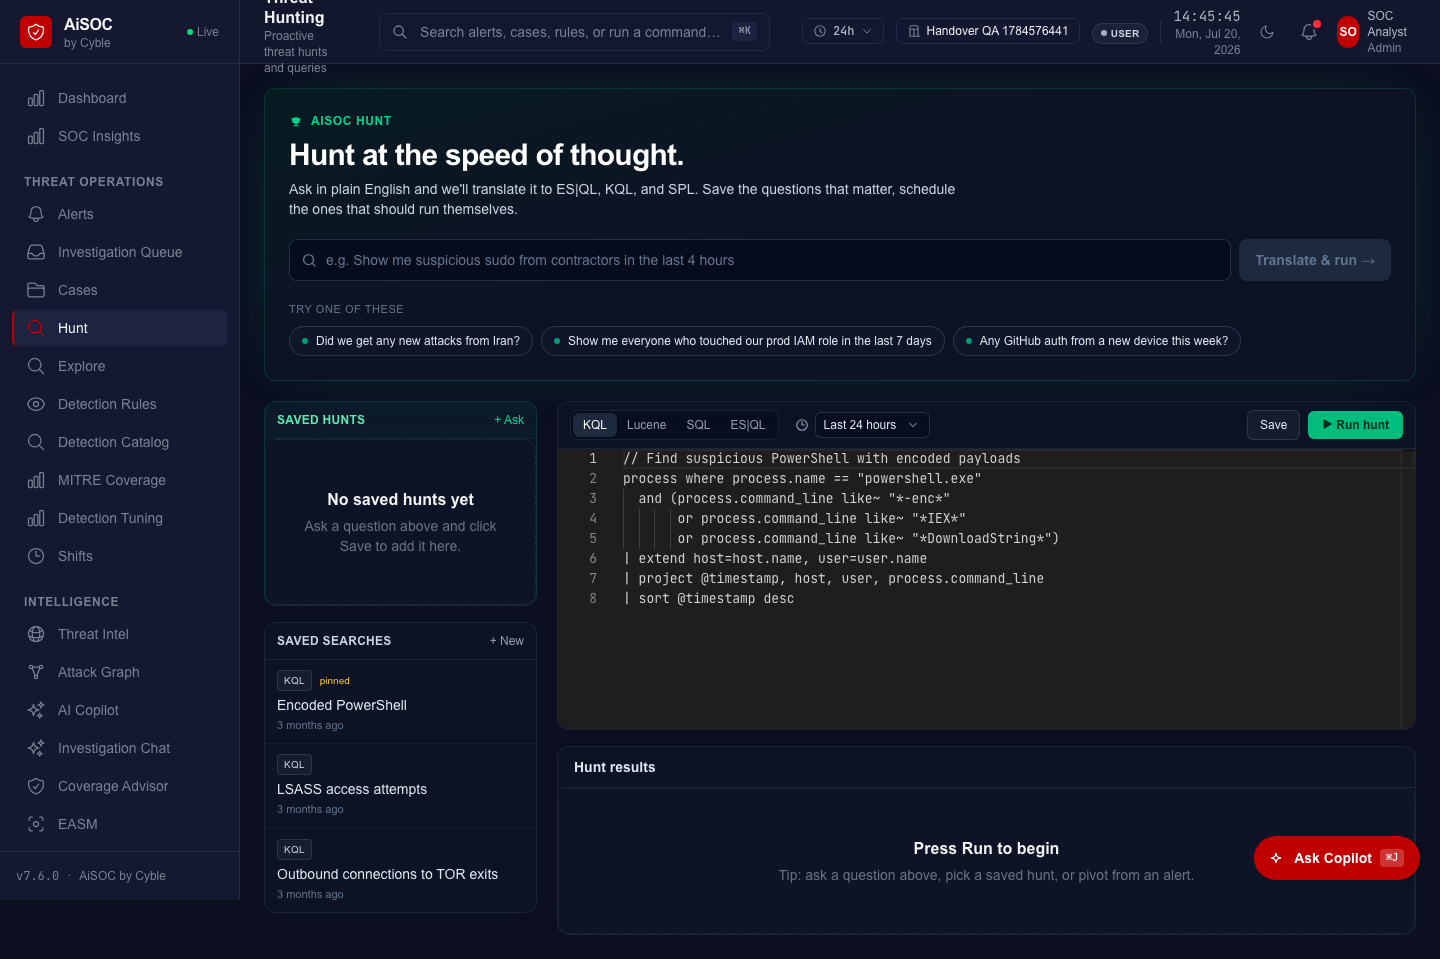
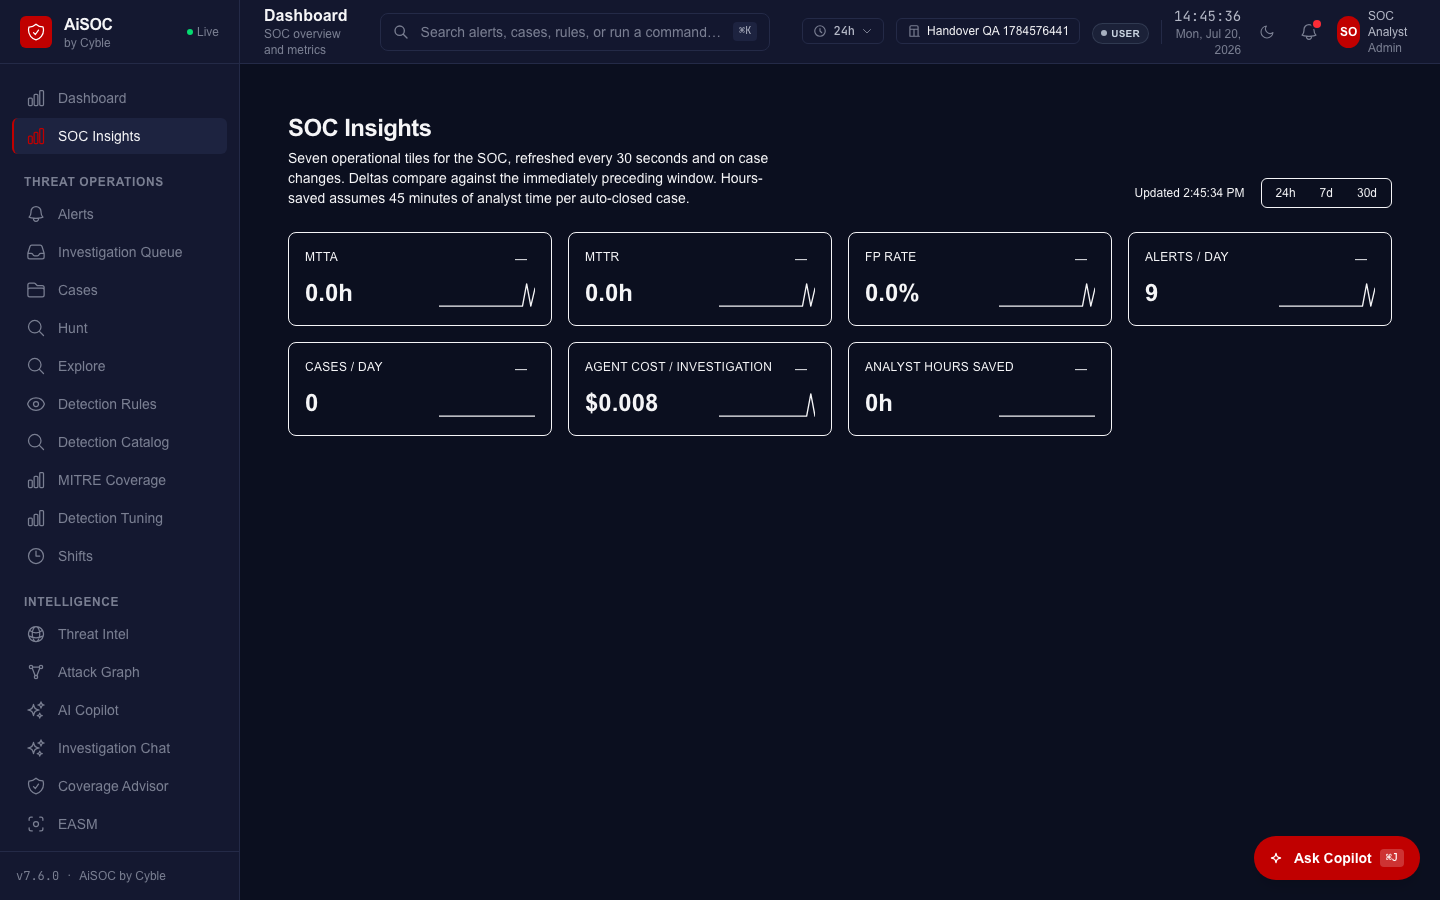
AiSOC delivers an open-source AI Security Operations Center that unifies event ingestion, graph correlation, autonomous triage, and purple-team adversary emulation into a single self-hosted console. Security analysts triage alerts across an interactive Investigation Rail that visualizes six-event attack timelines, pivot-path entity graphs, and recommended containment steps. The underlying LangGraph agentic engine reasons over ingested telemetry, querying MITRE ATT&CK frameworks, CISA Known Exploited Vulnerabilities catalogs, and Shodan intelligence while recording every prompt, tool execution, and evidentiary citation in an immutable Investigation Ledger. Incident responders execute automated containment playbooks, including host network isolation, credential revocation in identity providers, and firewall blocklist updates with human-in-the-loop sign-offs. Threat hunters input plain-English hypotheses into the natural-language hunt workbench to generate and execute ES|QL, SPL, and KQL queries against historical telemetry stores. Platform operators connect over seventy vendor connectors spanning CrowdStrike, SentinelOne, Microsoft Defender, AWS Security Hub, Okta, and Cloudflare to normalize streaming events into Open Cybersecurity Schema Framework standards. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Benefits
- Immutable AI Investigation Ledger
- Records every LLM prompt, tool invocation, evidence citation, and decision rationale inside an auditable ledger, enabling complete forensic replayability and regulatory compliance across all triaged security incidents.
- Extensive Enterprise Telemetry Connectors
- Ingests security events from seventy-eight native connectors spanning EDR, SIEM, cloud infrastructure, and identity providers, normalizing incoming streams into standard OCSF formats via high-throughput Kafka message pipelines.
- Natural Language Threat Hunting
- Converts plain-English threat hypotheses directly into optimized ES|QL, Splunk SPL, or Microsoft KQL queries, allowing analysts to search petabyte-scale event lakes without mastering specialized syntax.
- Ingest-Time Entity Graph Correlation
- Maps lateral movement, asset ownership, and identity relationships into Neo4j graph stores during ingestion, surfacing hidden attack paths across complex cloud and enterprise network topologies.
Features
- Investigation Rail Console
- Visualizes chronological attack paths, MITRE ATT&CK technique tags, and affected asset nodes alongside one-click automated remediation triggers.
- LangGraph Agentic Investigator
- Orchestrates specialized triage, detection, hunt, and response autonomous agents using structured multi-step reasoning workflows with human-in-the-loop oversight.
- Automated SOAR Action Engine
- Executes containment actions such as host isolation, session termination, and IP blocklisting across integrated firewalls and endpoint security tools.
- Adversary Emulation Suite
- Conducts purple-team simulation drills against live detection pipelines to benchmark organizational mean-time-to-detect and validate defensive configurations.
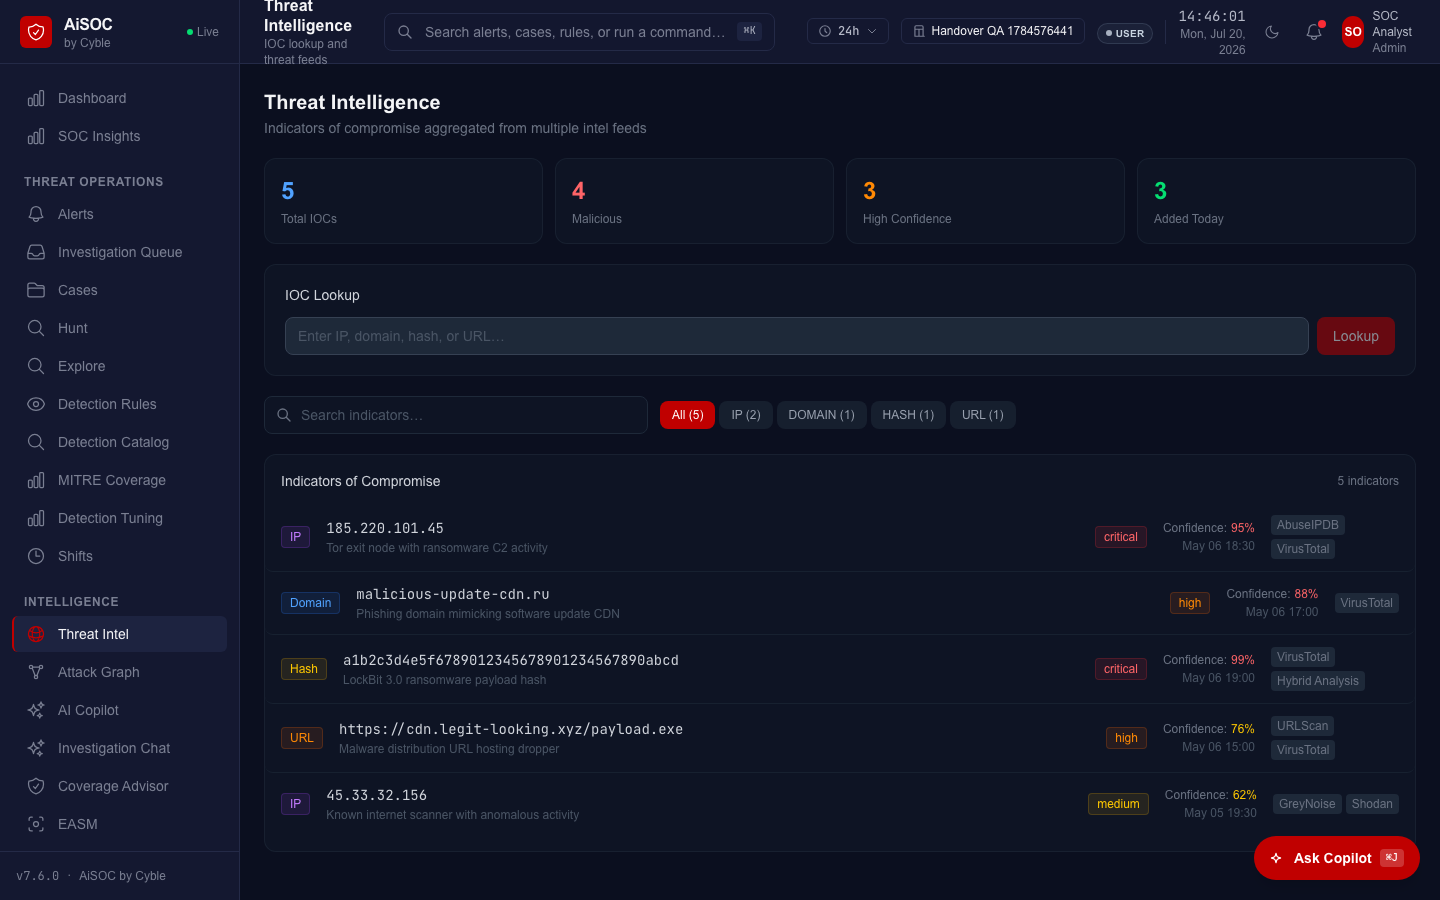
- Comprehensive Threat Intelligence Feeds
- Enriches raw alerts using integrated TAXII, MISP, AlienVault OTX, and CISA KEV feeds to score indicators of compromise in real time.