Categories
Self-Hosted AI Agents Security Incident Response Compliance Threat Detection Cloud Security SecOpsStars
Forks
Watchers
Developer links
Argus
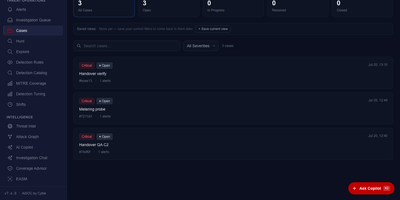
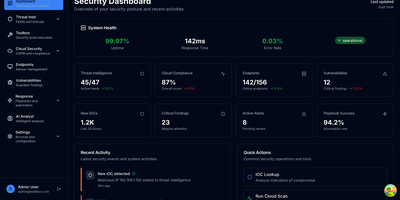
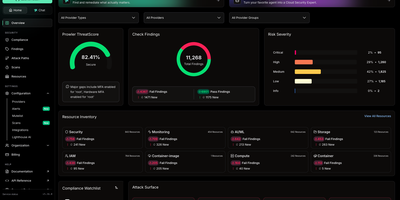
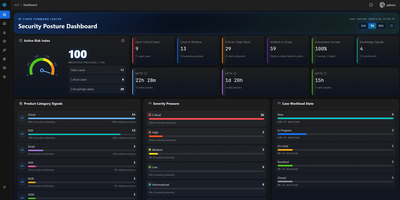
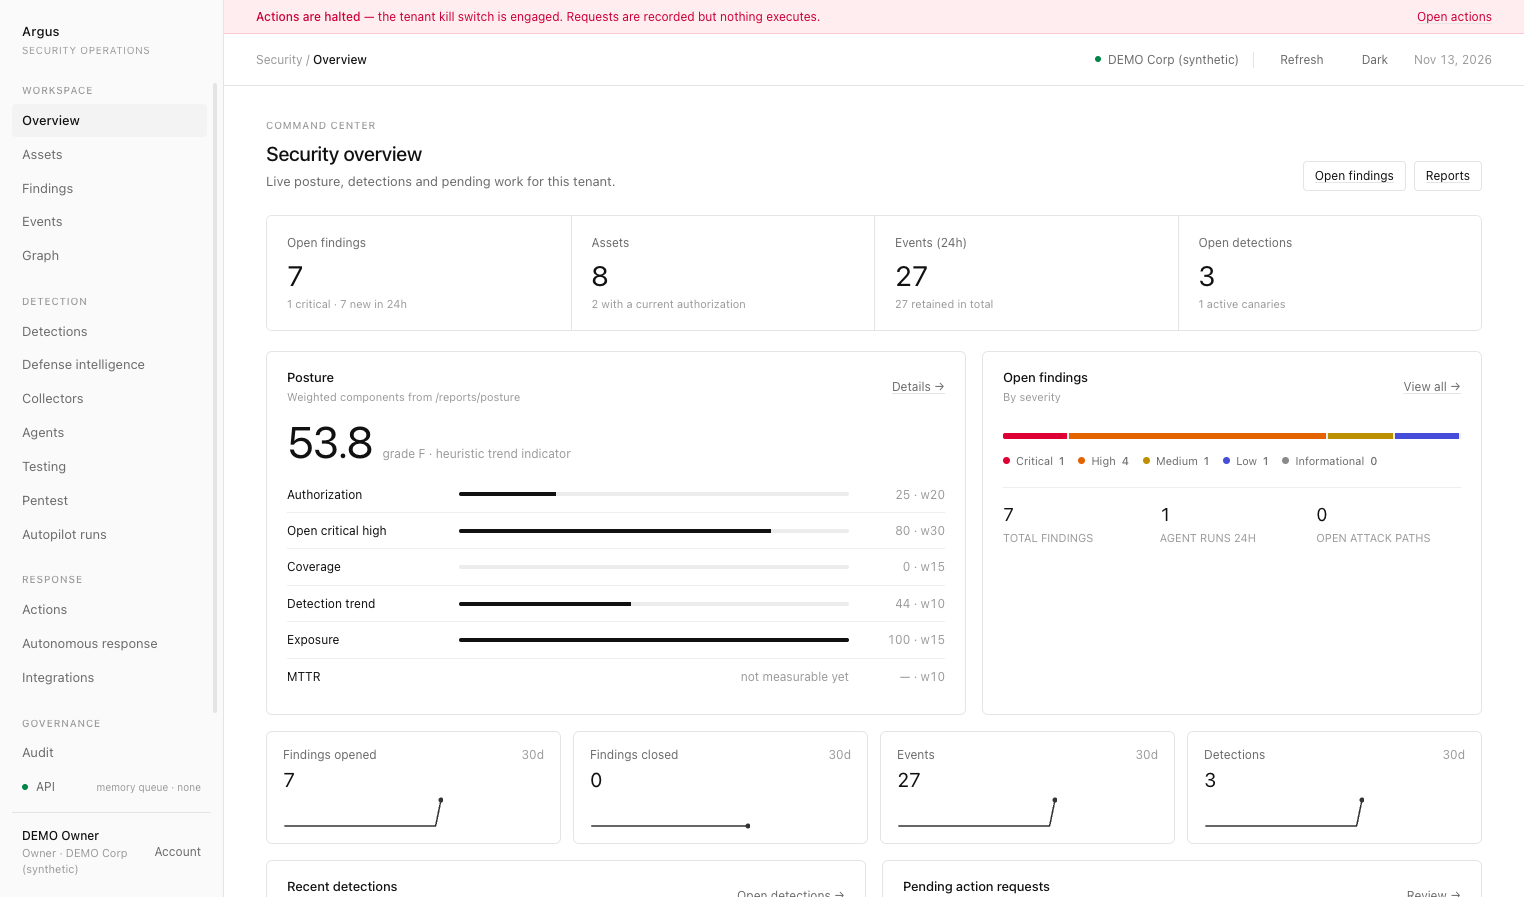
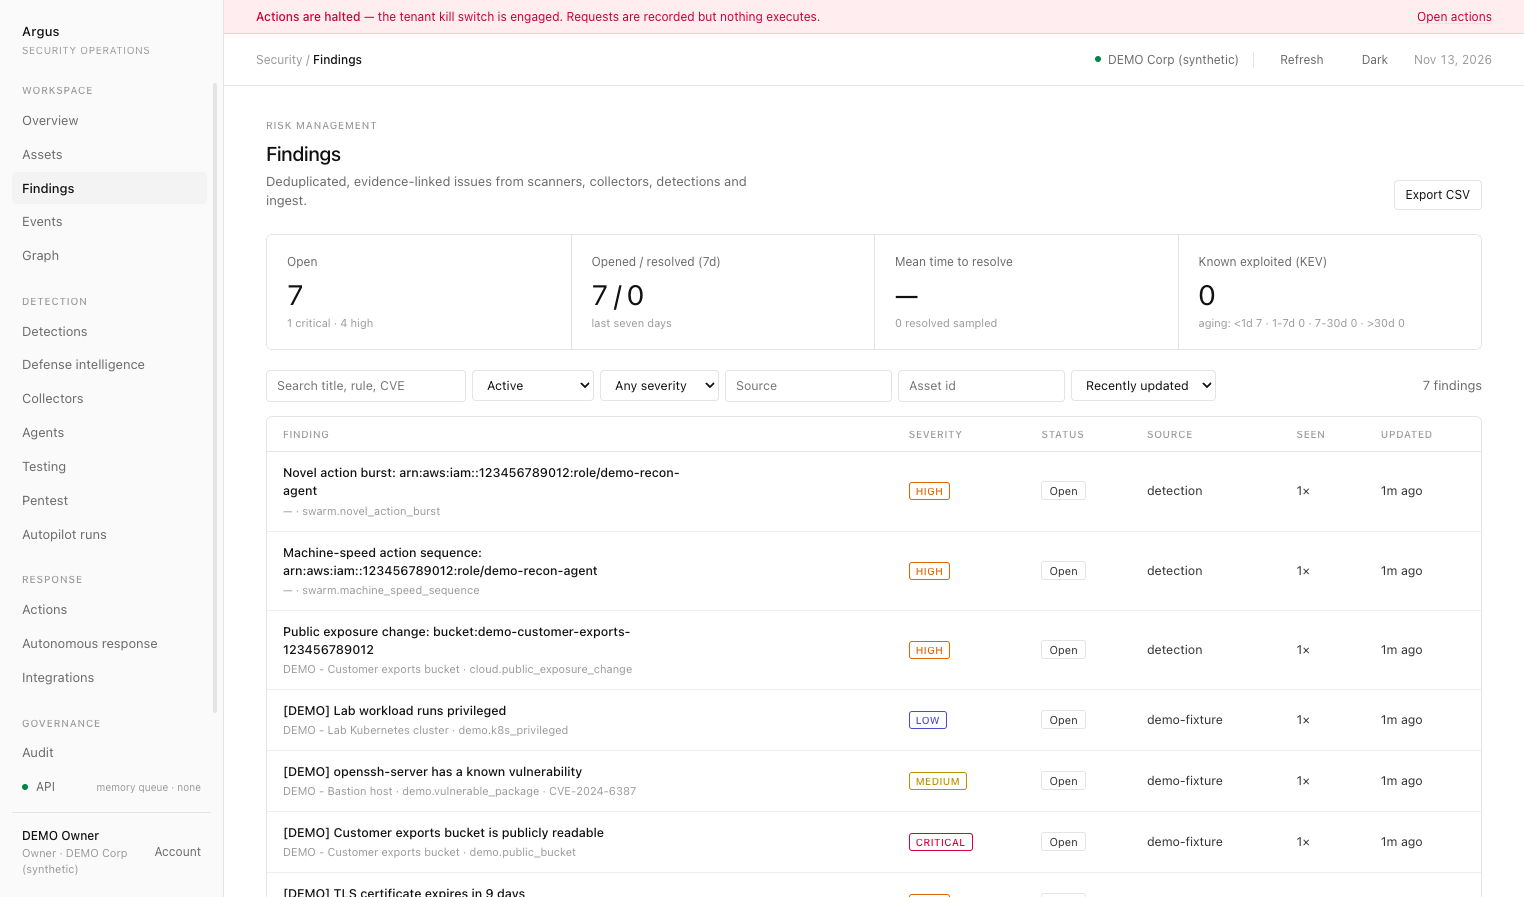
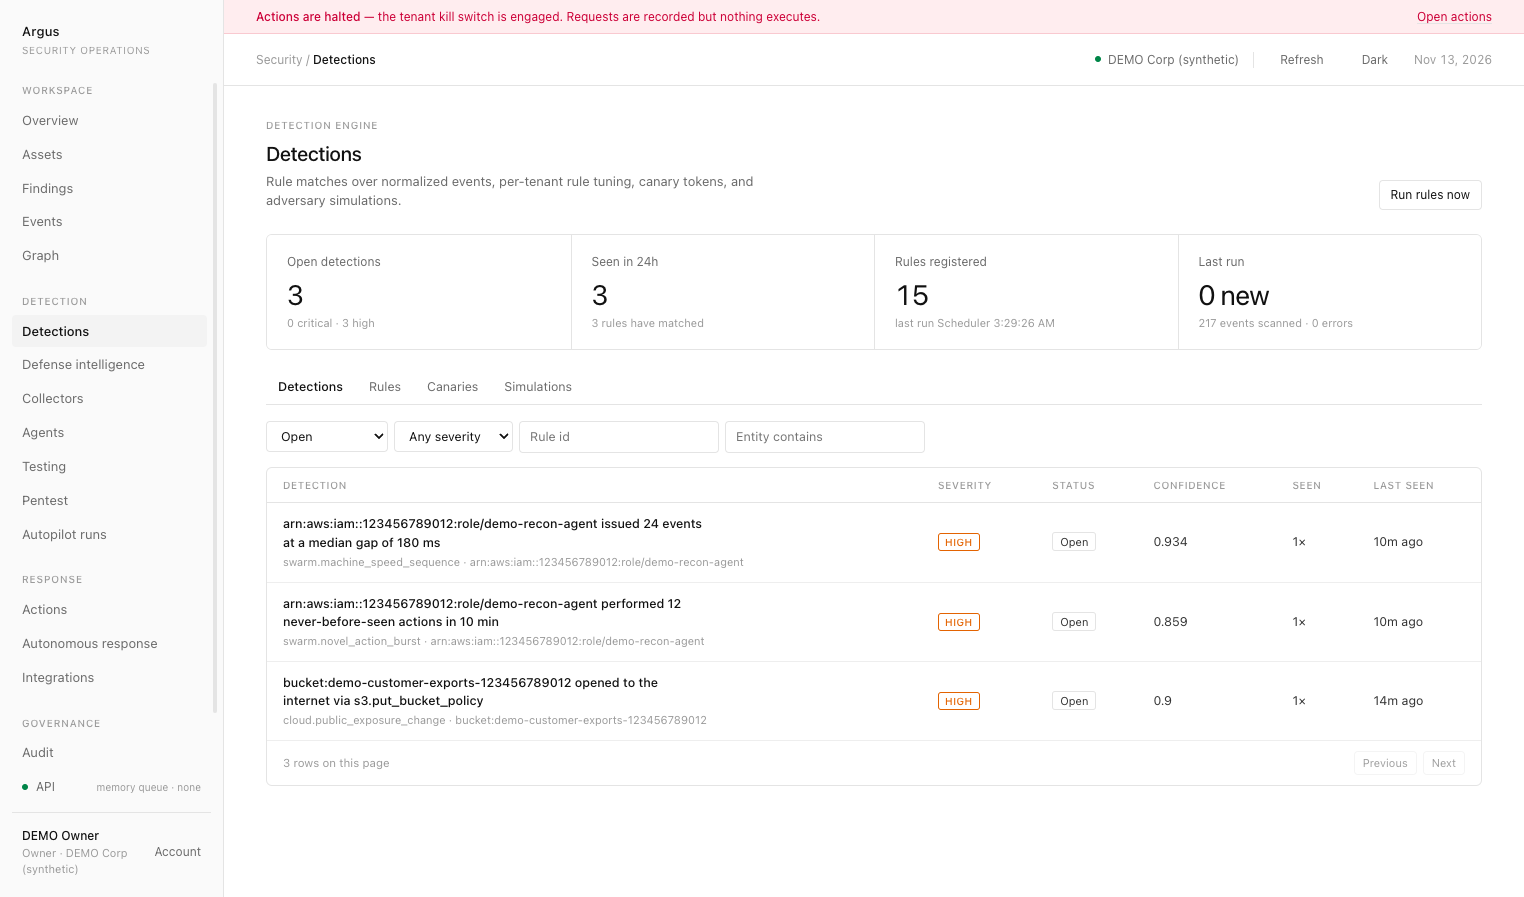
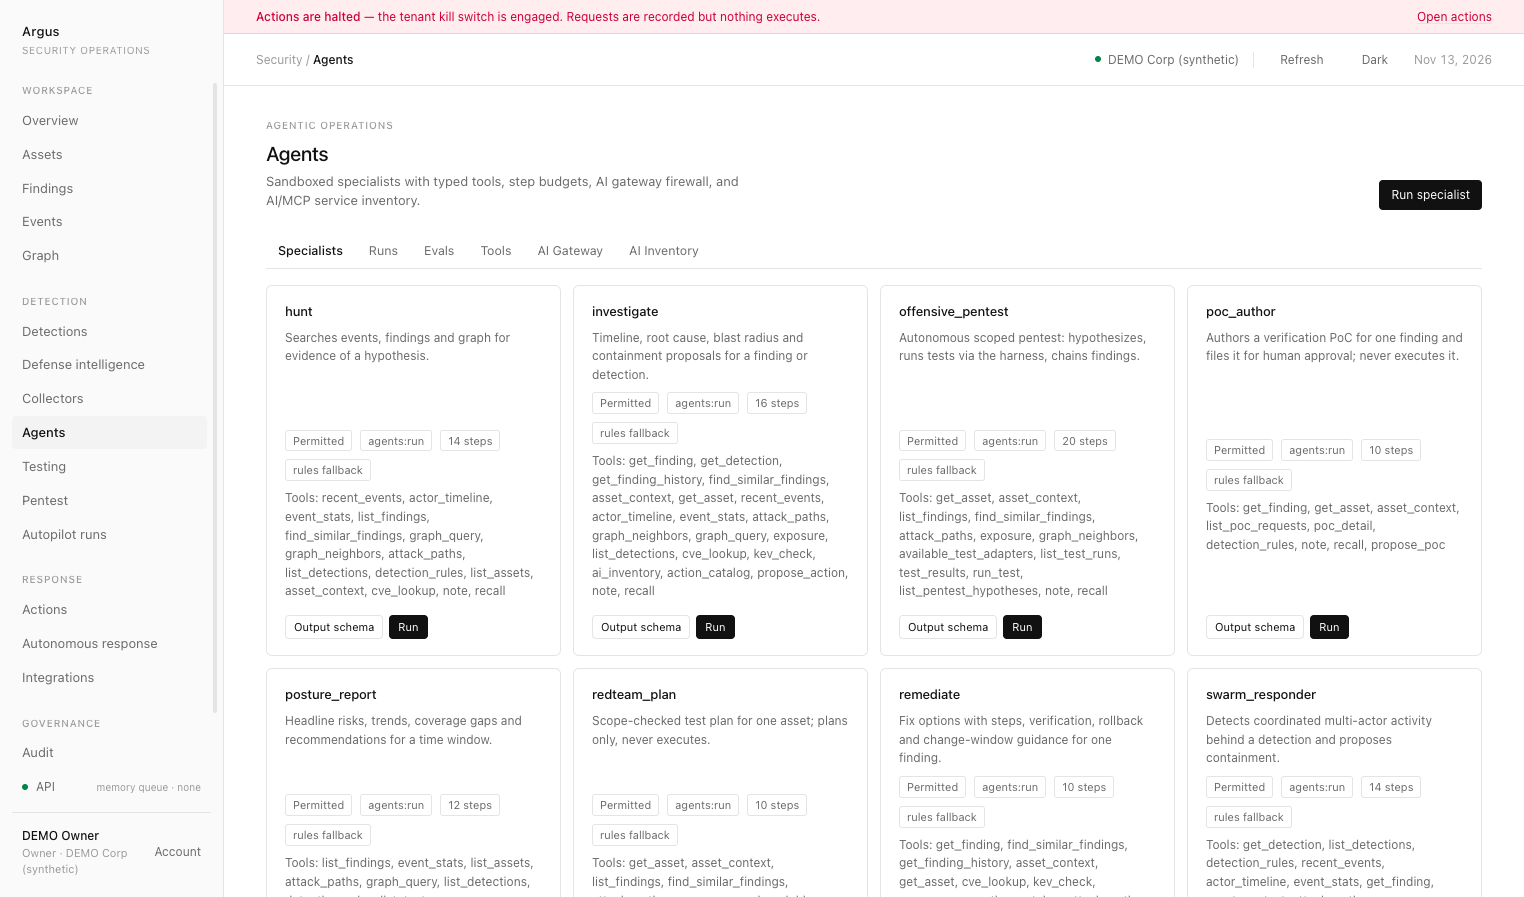
Hand your security alerts to a team of AI specialists and keep the final say on every action. Argus pulls events from cloud, identity, code, endpoint, and Kubernetes sources, runs fifteen detection rules, and turns matches into deduplicated findings enriched with CISA KEV and EPSS scores. Nine specialist agents hunt for evidence, build timelines, estimate blast radius, and propose fixes, but their only write path is a pending request that waits for human approval. Response playbooks can block an attacker or isolate a laptop through a catalog of 27 typed actions, starting in shadow mode with dry runs, caps, automatic rollback, and a tenant kill switch. Plant canary tokens aimed at rogue AI agents, replay eight simulated agent-driven attacks, and route OpenAI and Anthropic traffic through a gateway with model allowlists and budgets. Every step is written to a signed audit chain. A self-hosted command center with roles, TOTP sign-in, and Slack approvals fits small teams that have no SOC of their own. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Benefits
- Agents Investigate, Humans Decide
- Nine specialist agents triage, hunt, and propose fixes using read-only tools, and their only write path is a pending request that waits for a person to approve it.
- Reversible Automated Response
- Autonomous playbooks start in shadow mode, use only reversible actions inside hourly caps, and roll themselves back unless someone keeps the change. A tenant kill switch halts everything.
- Tamper-Evident Audit Trail
- Every action, approval, and agent step lands in a hash-linked, signed audit chain that can be mirrored to S3 Object Lock or Azure immutable storage for compliance reviews.
- Governed AI Usage Visibility
- An AI gateway fronts OpenAI and Anthropic with org-held keys, model allowlists, and budgets, and shadow-AI discovery flags unsanctioned services from network, cloud, and SSO telemetry.
Features
- Findings And Detection Rules
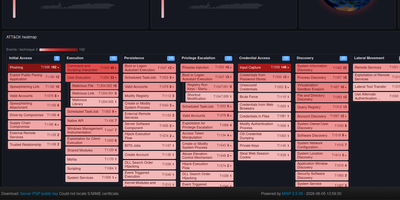
- Fifteen detection rules cover cloud, identity, Kubernetes, code, and agent-driven attacks, and deduplicated findings gain KEV and EPSS enrichment that raises severity automatically.
- Evidence Graph And Assets
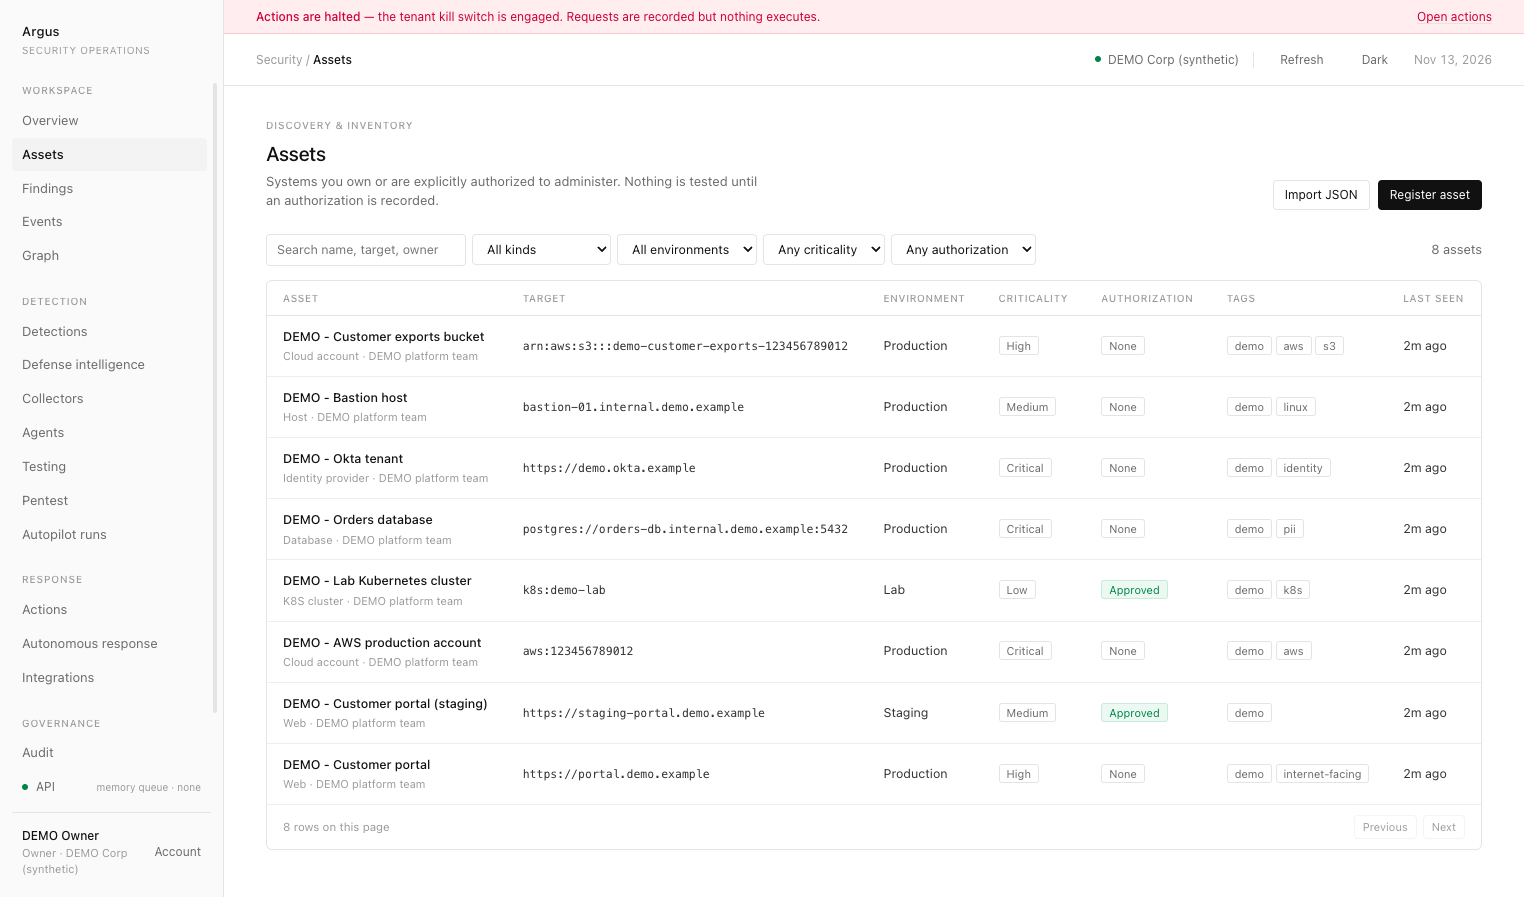
- Track assets, identities, and relations in an evidence graph with attack paths, and record an authorization before any active test may touch a system.
- Specialist AI Agents
- Run hunt, investigate, remediate, and posture-report agents with typed tools and step budgets, backed by Anthropic, OpenAI, Ollama, or a rules-only fallback.
- Canaries For AI Agents
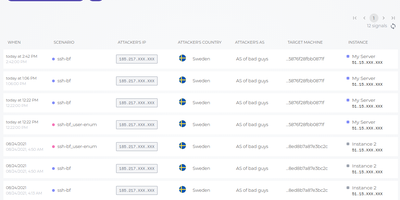
- Plant canary tokens, including hidden prompt injections, fake MCP servers, and fake LLM keys, so a rogue agent trips a detection with its IP, model, and prompt recorded.
- Attack Simulator
- Replay eight agent-driven attack scenarios in an isolated sandbox tenant and see which detections fired, which attacks slipped past, and which rules were switched off.
- Integrations And Alerts
- Ingest from fifteen sources and notify through webhooks, Slack, Jira, ServiceNow, PagerDuty, or email, with Slack buttons to approve, deny, or roll back an action.