Stars
Forks
Watchers
Developer links
OneTimeSecret
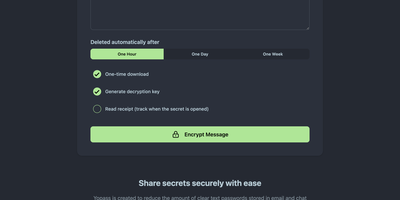
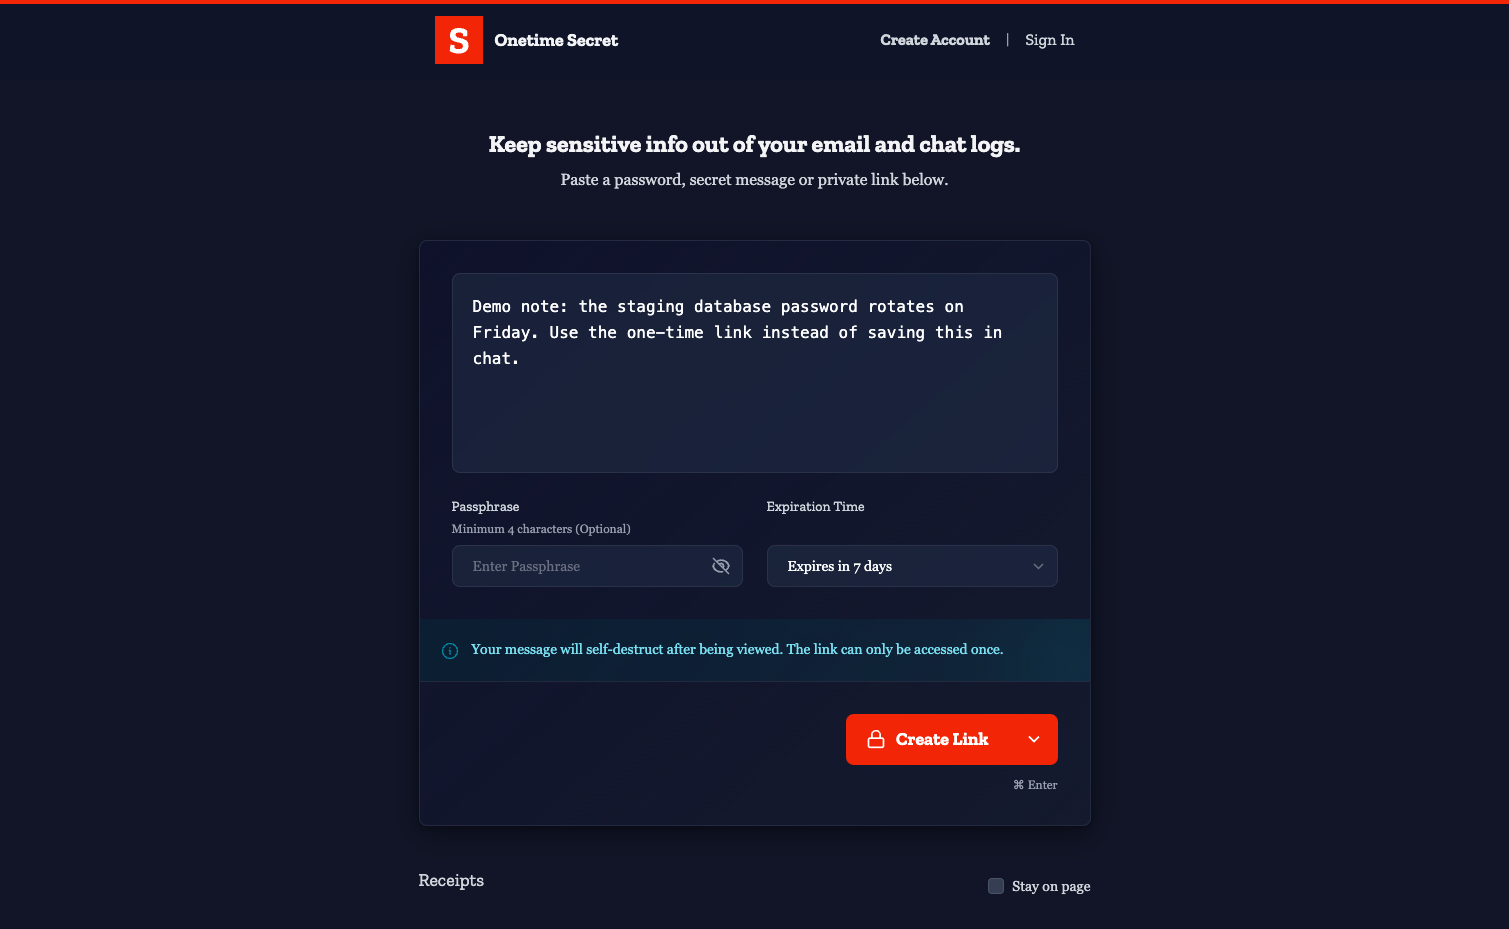
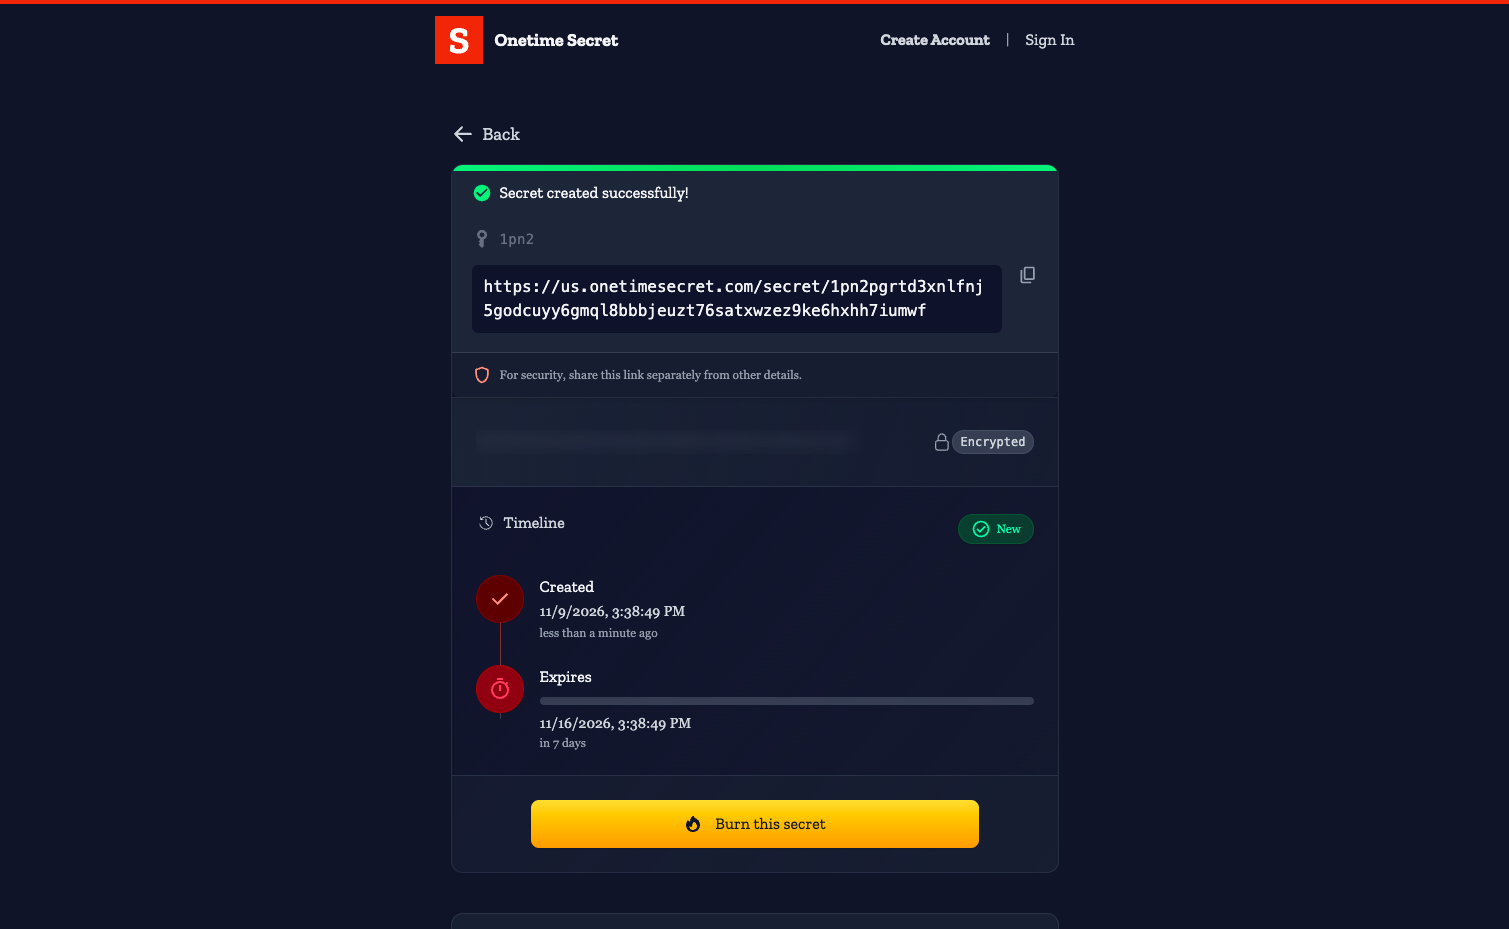
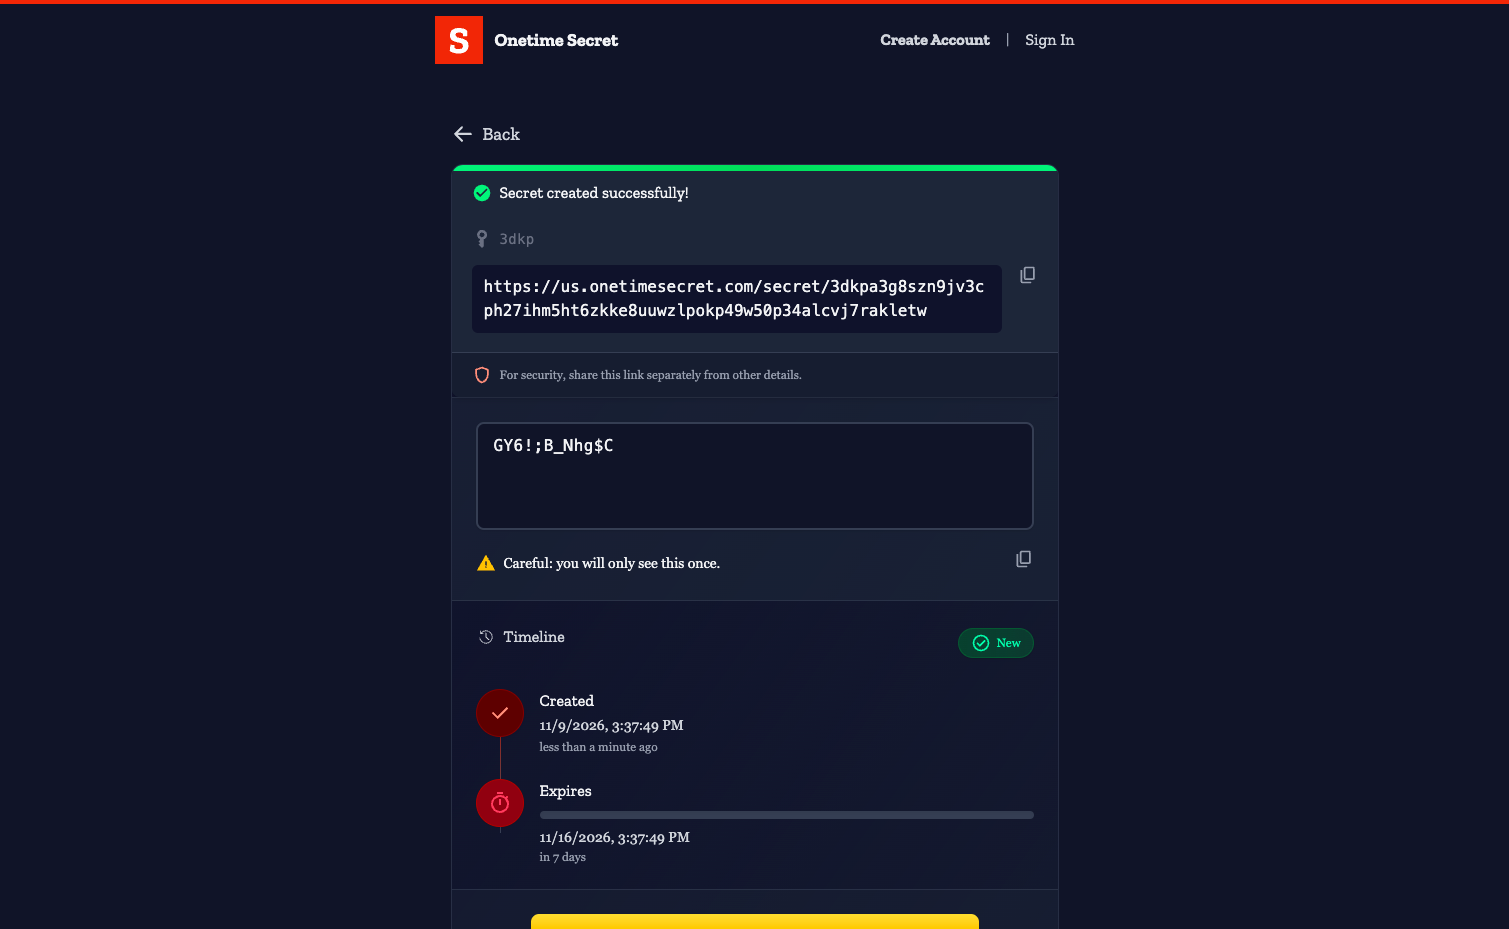
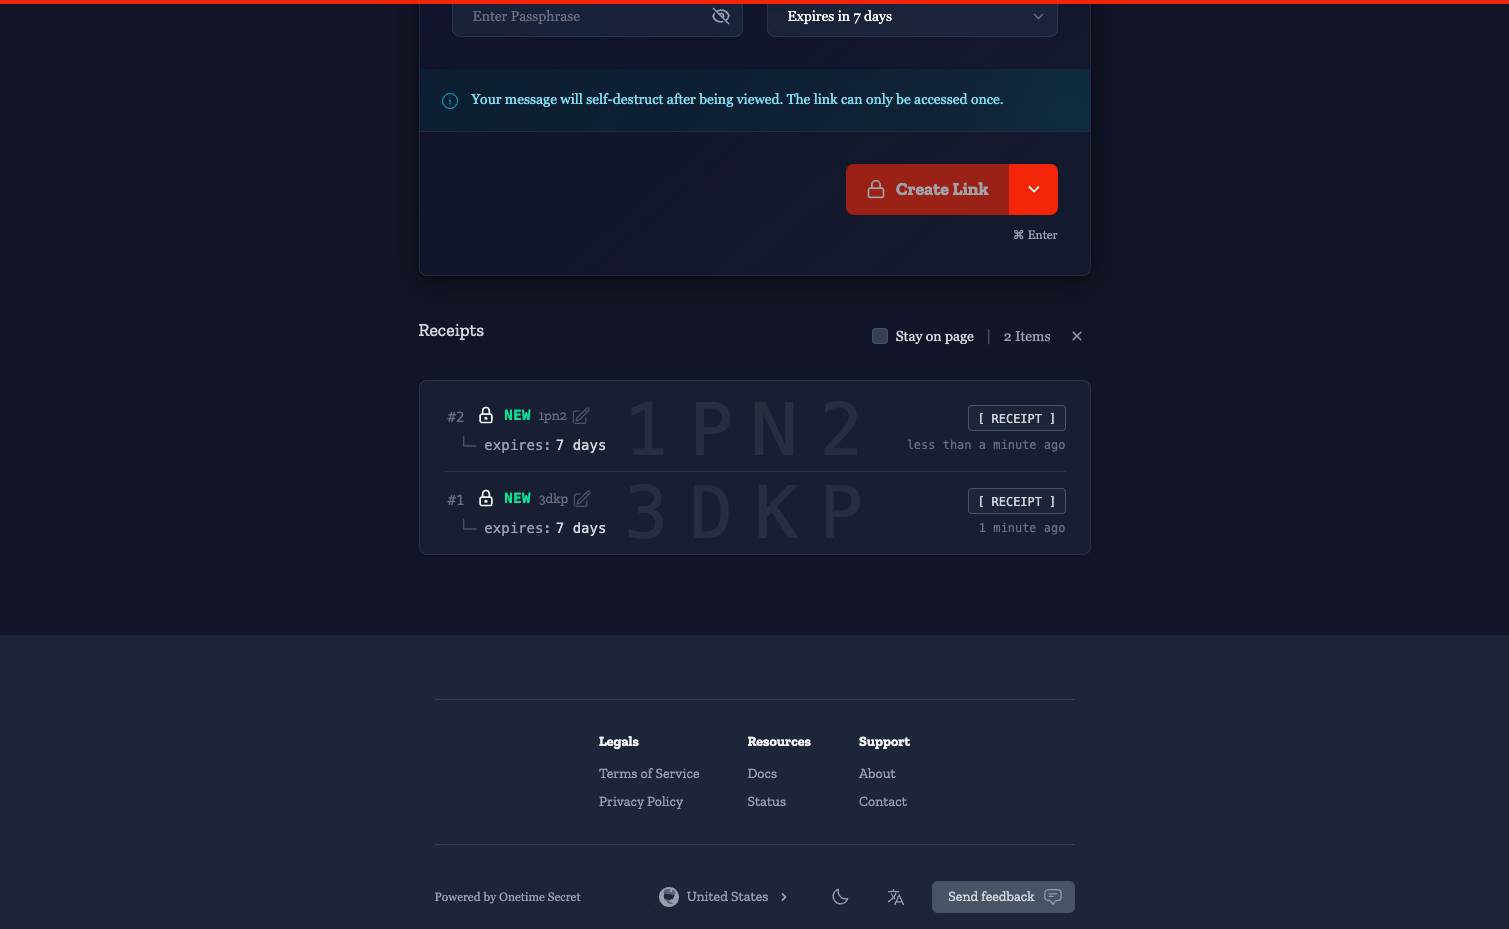
OneTimeSecret turns a password or private note into a single-use link that destroys itself the moment the recipient opens it. Create a secret in seconds from the web form: paste the text, optionally lock it behind a passphrase, and pick how long the link stays alive, from minutes to days. Send the generated link by email straight from the app, or drop it into any chat or ticket where a credential needs to change hands. Because the link burns after one view, a forwarded message or an old thread search cannot leak what was shared; once the recipient reads it, the content is gone for good. An API issues secrets programmatically, so scripts can hand database passwords or access tokens to teammates without writing them into CI logs or shell histories. Use it anonymously for quick one-off shares, or switch on full authentication with accounts, multi-factor authentication, and WebAuthn keys for a controlled internal service. Custom domains let the links carry your own hostname, so recipients see a service your organization operates rather than a public website. Admins manage users, domains, and access from a built-in console suited to teams that hand over credentials every day. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Benefits
- Secrets That Self-Destruct
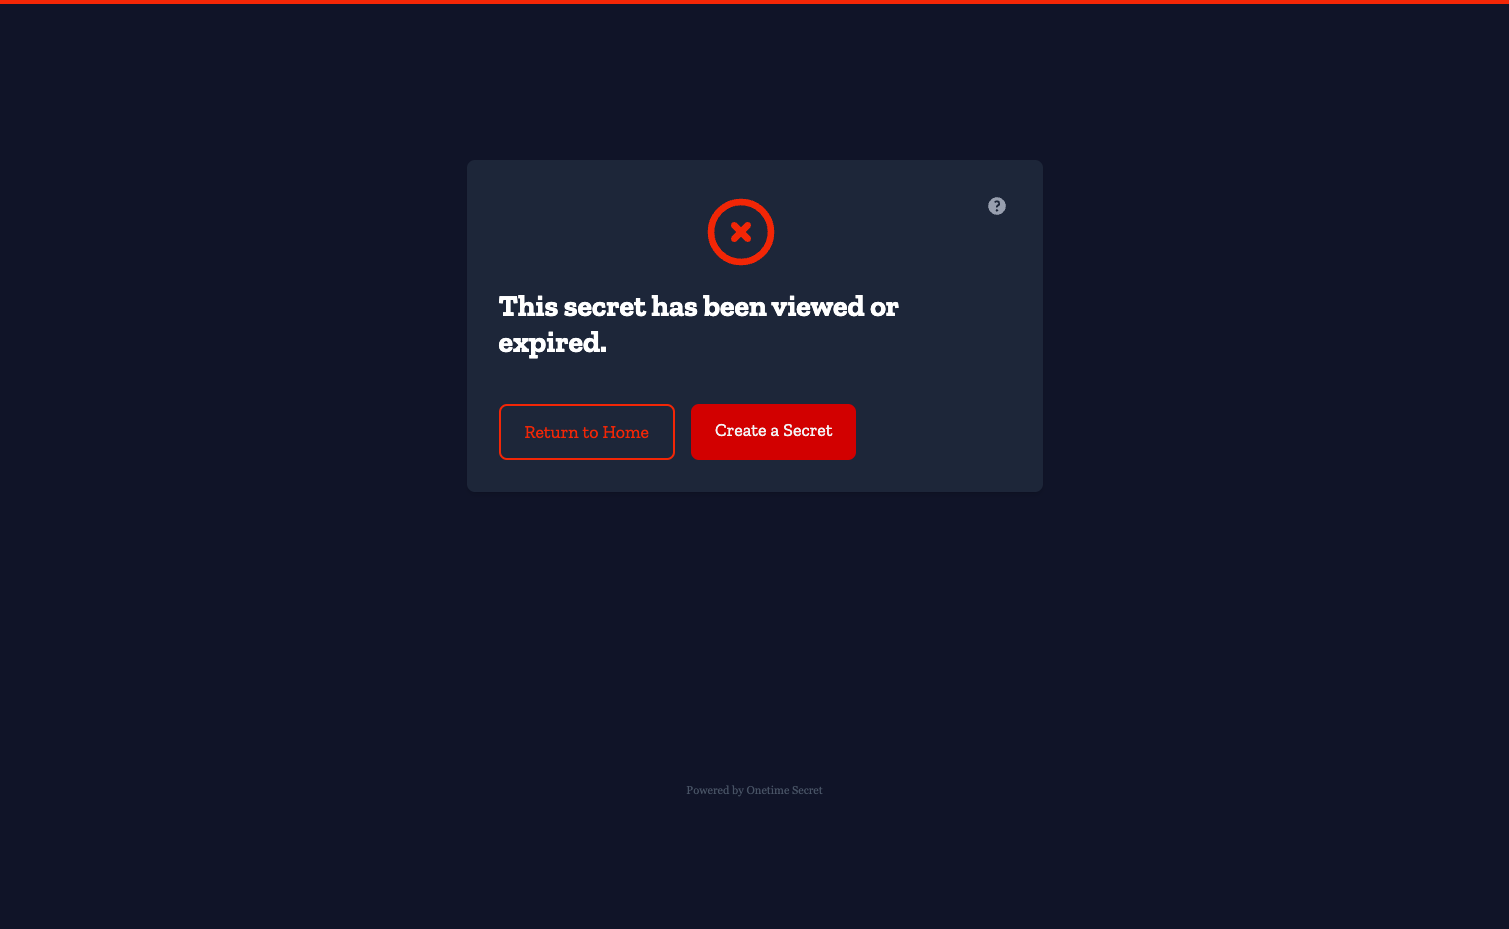
- Each link opens exactly once and then deletes its contents permanently, so credentials shared in chat or email cannot be rediscovered later by anyone browsing old threads.
- Passphrase Locked Links
- An optional passphrase adds a second factor the recipient must know separately, protecting the secret even when the link itself gets forwarded to the wrong inbox or channel.
- API Driven Delivery
- Scripts and pipelines create secrets through the API and hand teammates a one-time link, keeping passwords and tokens out of build logs, shell histories, and ticket comments.
- Your Domain, Your Server
- Custom domains put your own hostname on every link, and self-hosting keeps the whole exchange on infrastructure you control, with optional accounts, MFA, and WebAuthn sign-in.
Features
- One-Time Links
- Secrets are stored encrypted, burn permanently after the first view, and expire automatically when their timer runs out, so a copied link is worthless after the recipient opens it.
- Passphrase Protection
- Lock any secret behind a passphrase the recipient enters before viewing; the passphrase is folded into the encryption, so the link alone never reveals the contents.
- Configurable Expiry
- Choose lifetimes from minutes to days per secret, with the link and the stored content deleted automatically the moment the chosen window closes without a view.
- Email Delivery
- Send the generated link to a recipient by email from inside the app, or copy it into chat, tickets, and docs wherever a credential needs to travel.
- Custom Domains
- Attach your own domain so shared links carry a hostname recipients recognize and trust, with separate domains possible for teams, clients, or internal groups.
- Full Authentication Mode
- Optional full mode adds user accounts, multi-factor authentication, and WebAuthn keys, backed by PostgreSQL and RabbitMQ, for deployments that need controlled access and administration.