Categories
self-hosted devops kubernetes oci-registry container-registry image-storage docker-registryStars
Forks
Watchers
Developer links
Zot
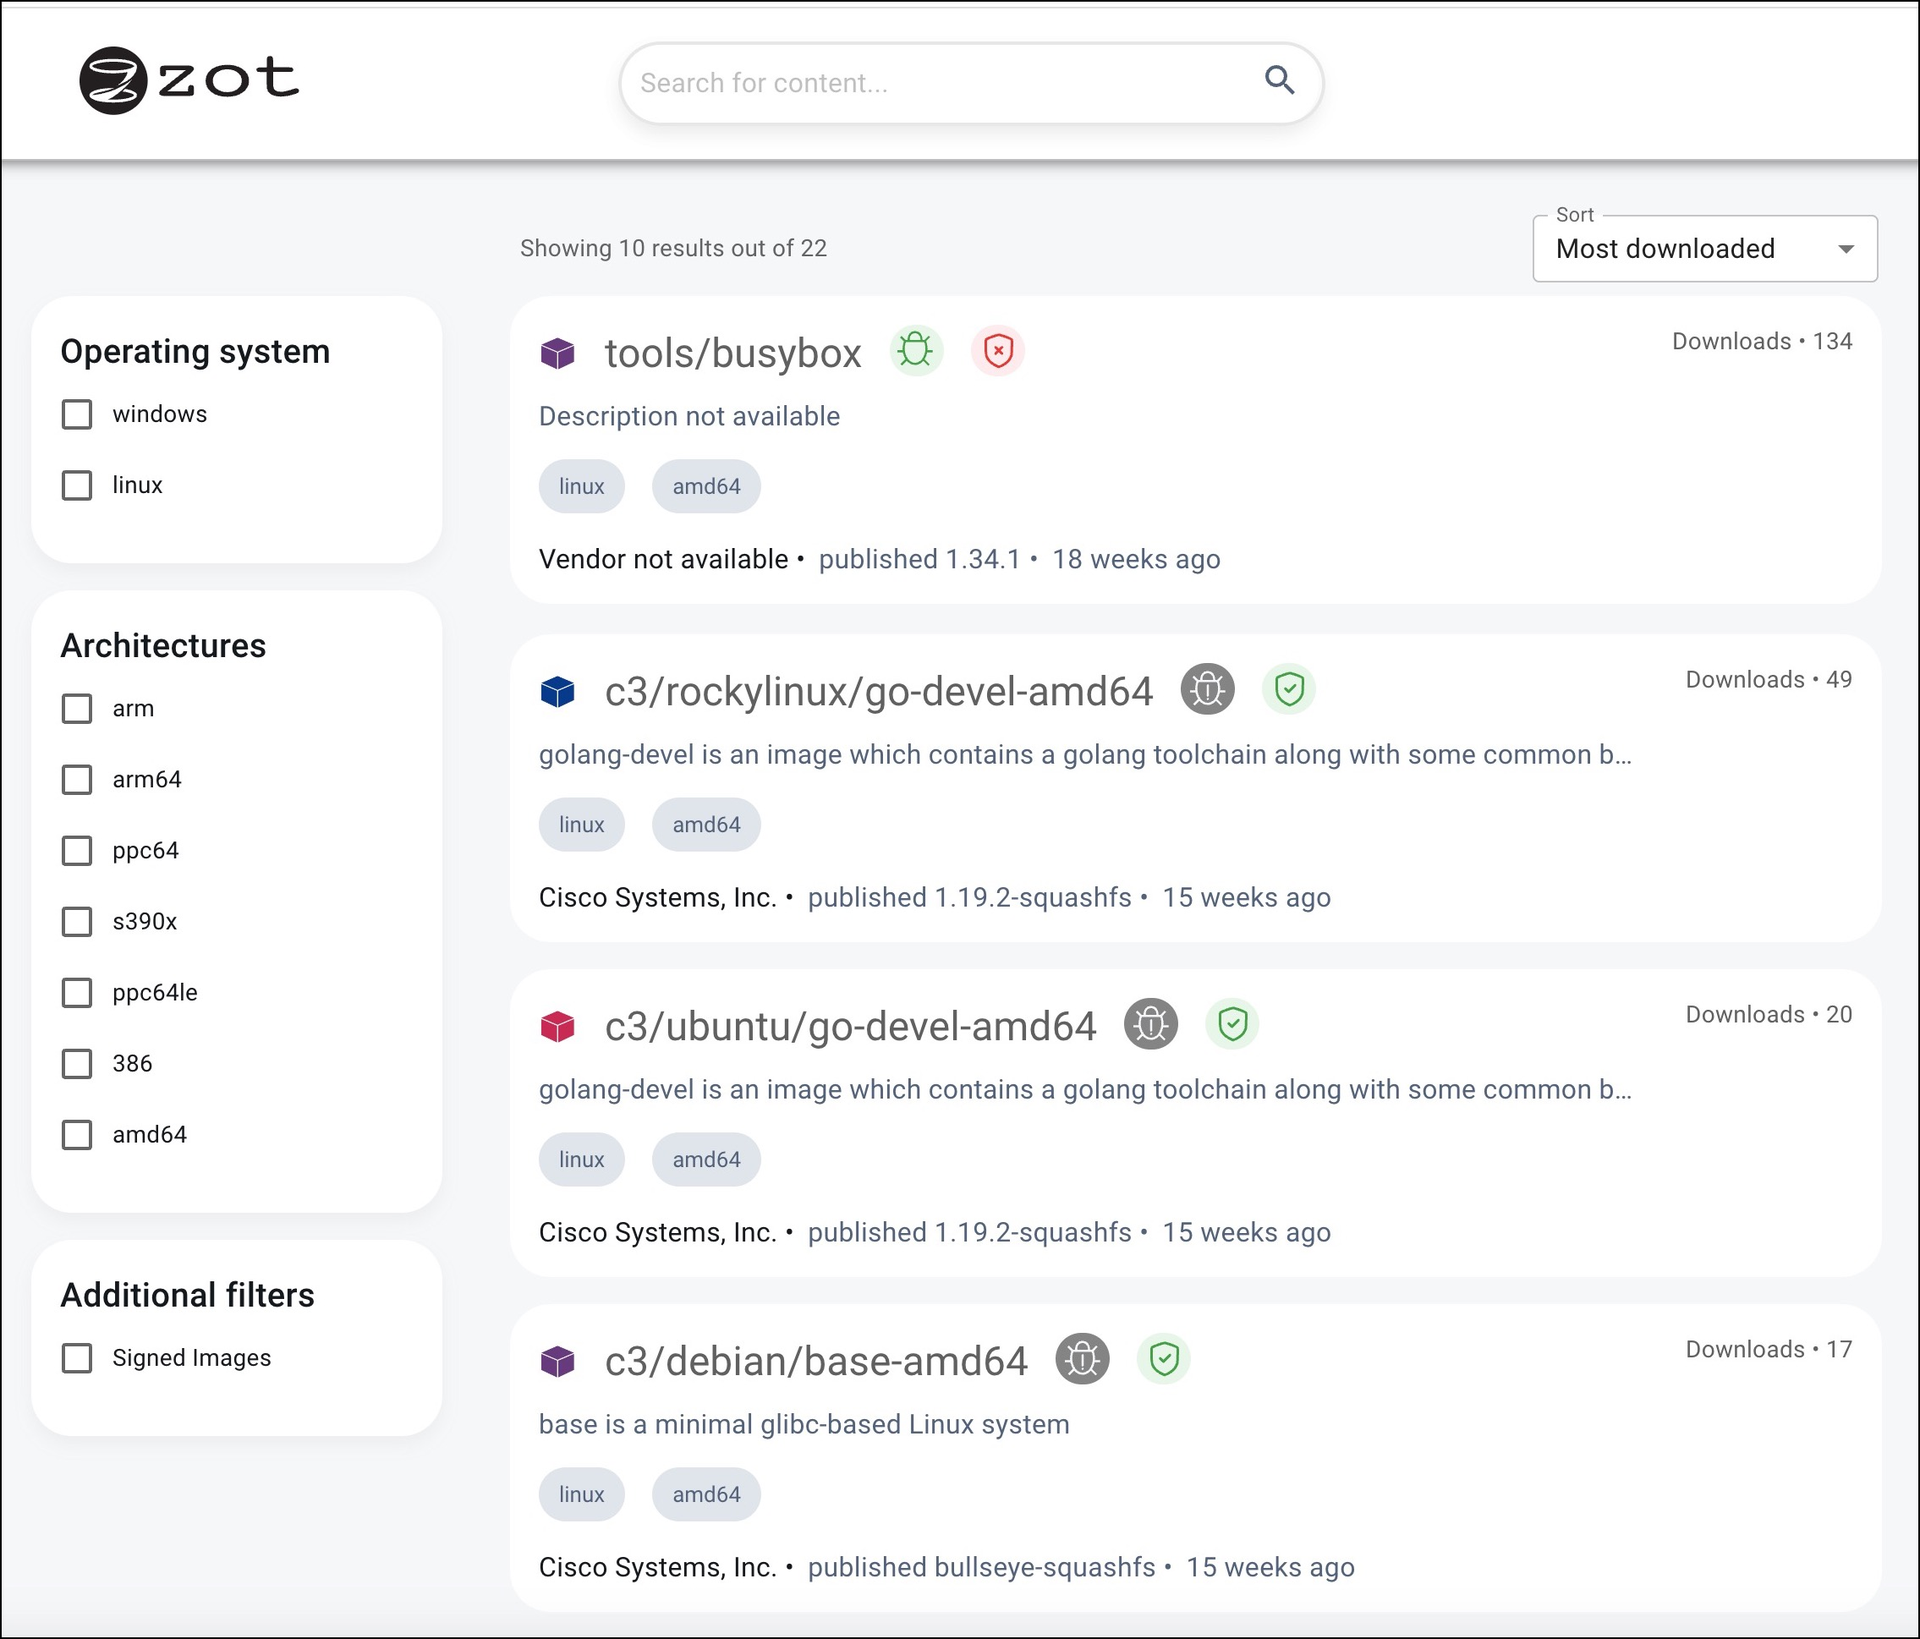
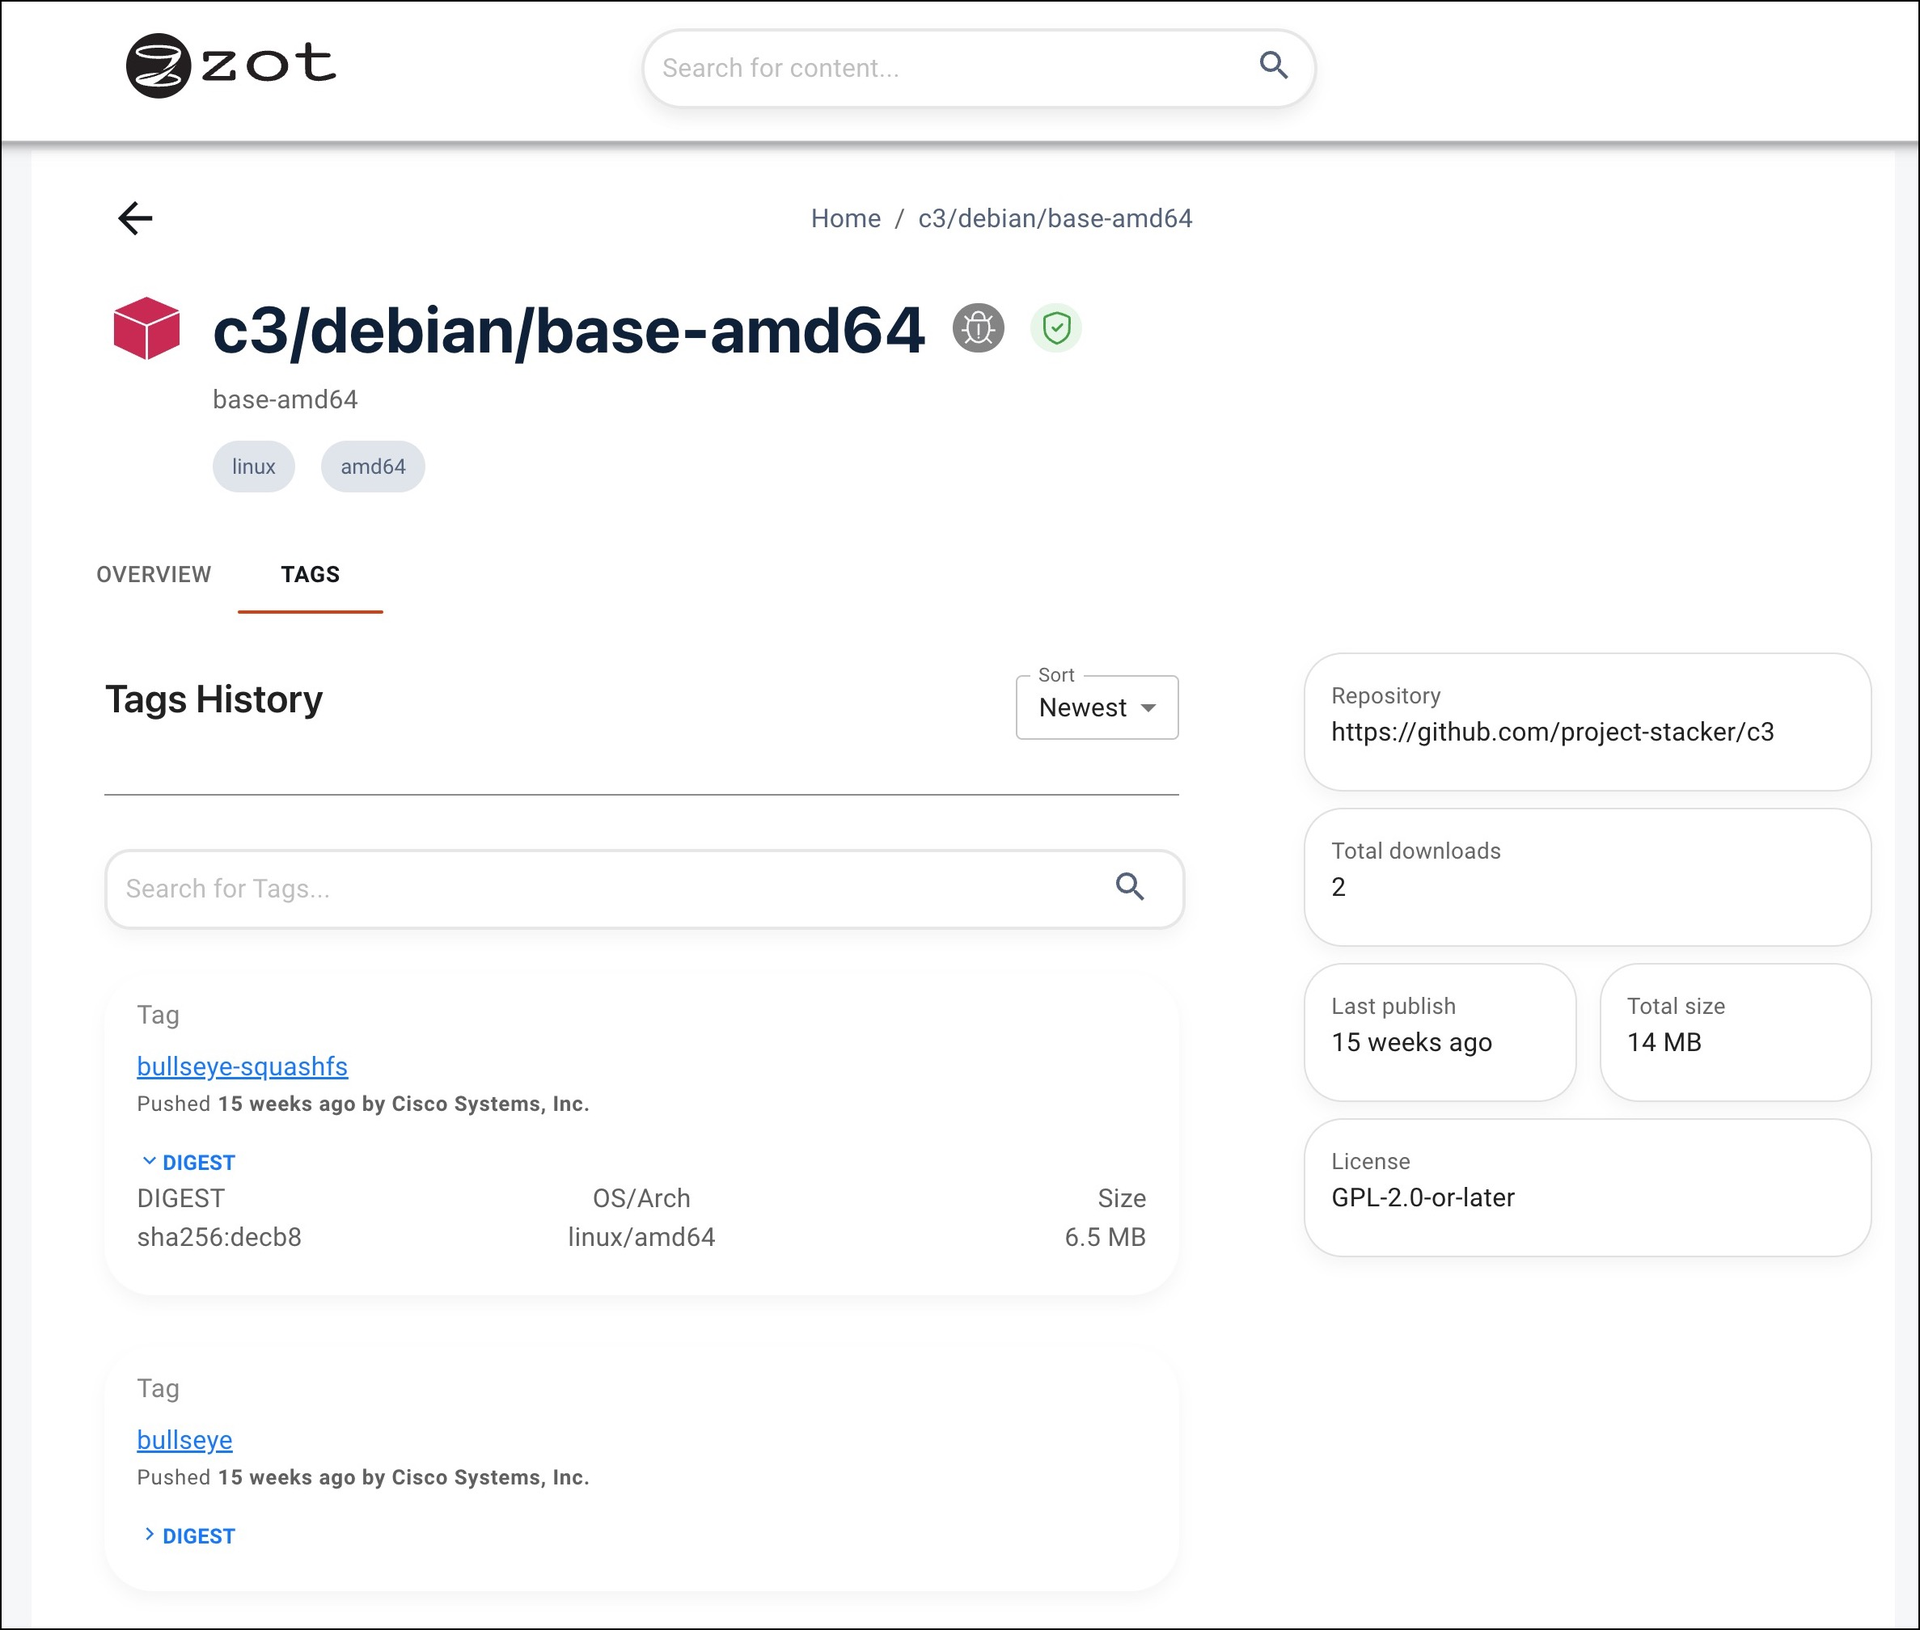
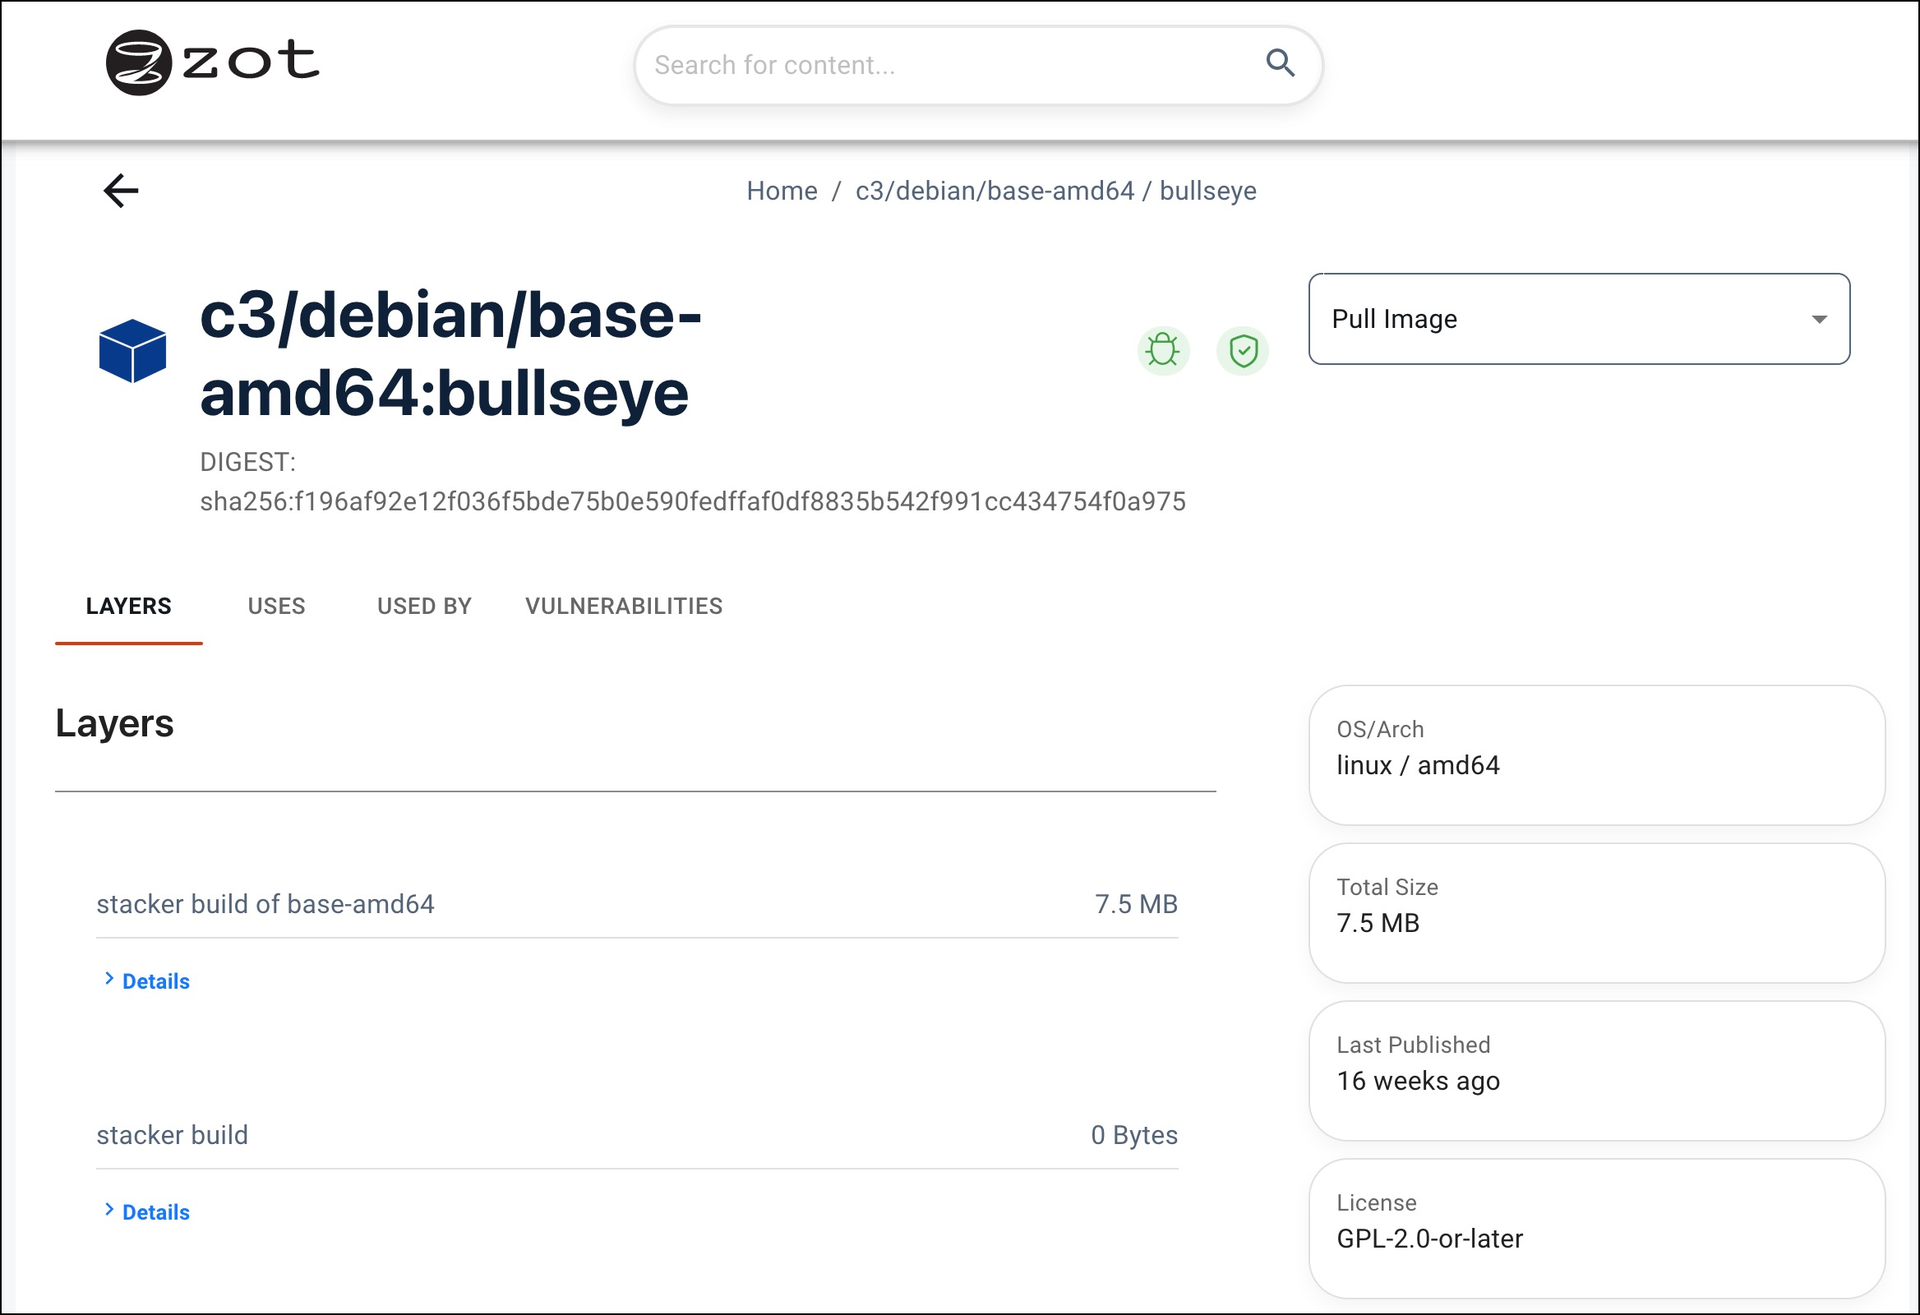
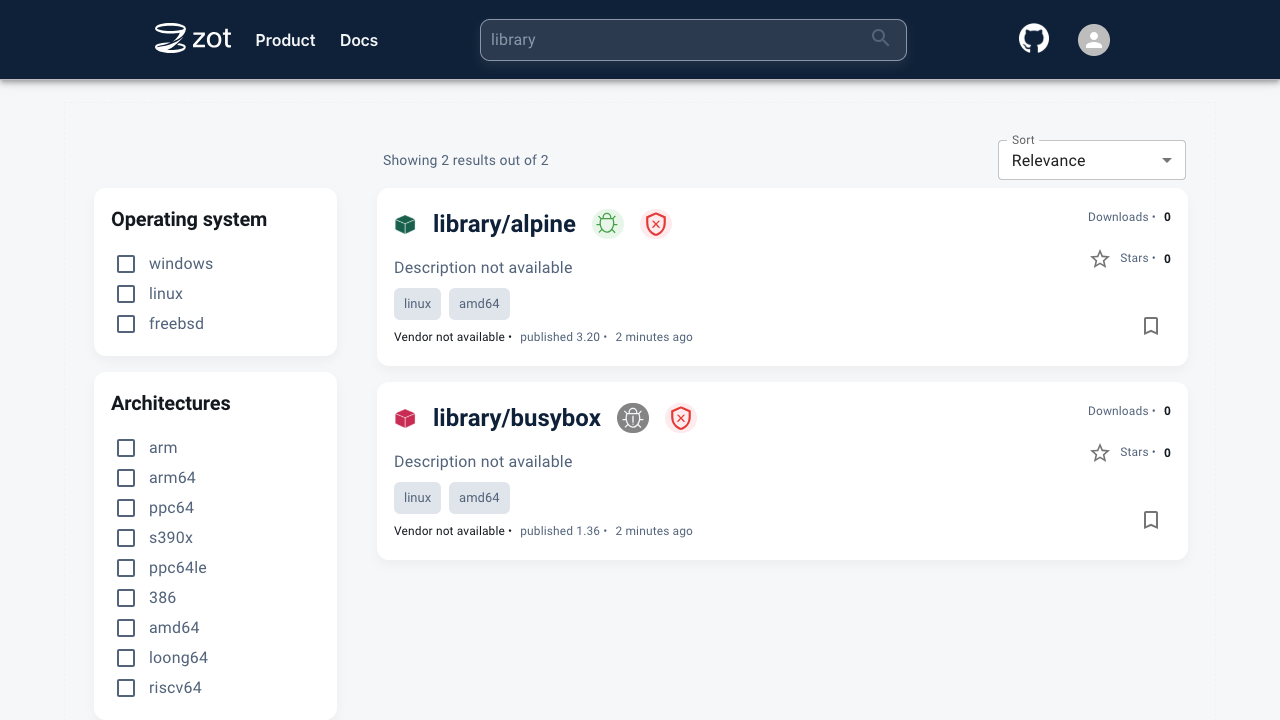
Think of Zot as the registry equivalent of a well-run warehouse: OCI images and artifacts come in, get cataloged, checked, and shipped back out to any compliant client. The bundled web interface lets you browse repositories and tags, inspect image details, and copy ready-made pull commands for Docker, Podman, and Skopeo instead of memorizing registry URLs. Sync extensions mirror upstream registries such as Docker Hub on a schedule or on demand, which keeps air-gapped and rate-limited environments supplied without manual image ferrying. Scrubbing walks the storage in the background comparing blocks against their SHA-256 checksums, so silent bit-rot gets caught by the registry instead of by a failed production deploy. Signature verification with Cosign and Notation checks that images came from who they claim, search answers queries across the catalog, and CVE scanning flags vulnerable images before they spread. Prometheus metrics, a management API, and webhook events cover the operations side, while the minimal image strips everything but the distribution spec for embedded or high-security deployments. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- Any OCI client just works
- Zot implements the OCI distribution specification faithfully, so Docker, Podman, Skopeo, Kubernetes, and Helm charts push and pull without plugins, proxies, or vendor-specific workarounds.
- Mirror upstream registries automatically
- The sync extension mirrors Docker Hub and other OCI registries on a schedule or on demand, keeping disconnected or rate-limited clusters supplied with fresh images.
- Bit-rot caught before deploys
- Background scrubbing continuously verifies stored blocks against their checksums, surfacing silent storage corruption while it is still a maintenance task instead of a broken release.
- Only signed images trusted
- Cosign and Notation signature verification checks image provenance at the registry, so clusters can refuse artifacts that were not signed by keys and certificates you uploaded.
Features
- Built-in web interface
- The bundled GUI browses repositories, tags, and image details, and copies pull commands for Docker, Podman, and Skopeo directly from the browser.
- Sync and mirroring extension
- Mirror one or more upstream OCI registries, including Docker Hub, with periodic polling or on-demand pulls and per-repository download policies.
- Scrub integrity checks
- A scheduled scrub traverses storage verifying every block against its SHA-256 checksum, proactively detecting corruption in images that sit unused for months.
- Cosign and Notation trust
- The trust extension verifies image signatures with Cosign public keys and Notation certificates, storing verification results queryable through the GraphQL API.
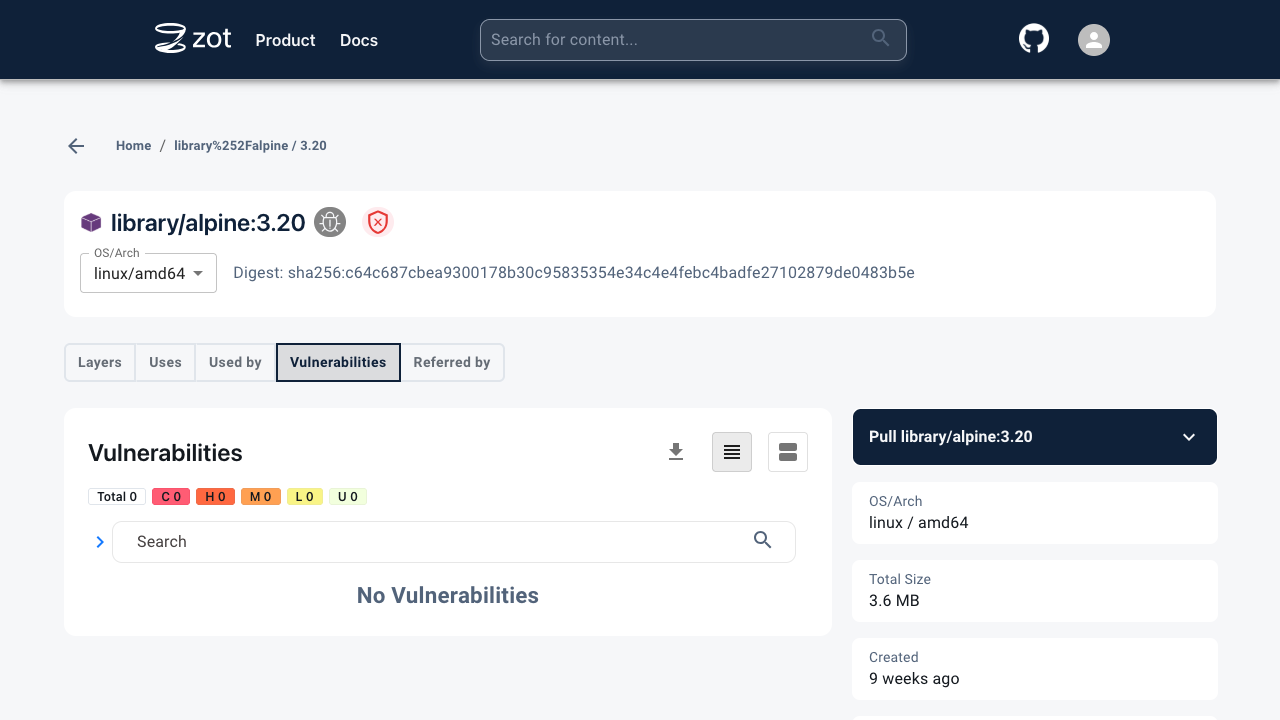
- Search with CVE scanning
- The search extension answers catalog-wide queries and scans images for known vulnerabilities, so risky tags are visible before they get deployed anywhere.
- Metrics, events, management API
- Prometheus-compatible metrics, webhook event notifications, and a management API expose registry operations to the rest of your observability and automation stack.