Stars
Forks
Watchers
Developer links
BugTraceAI
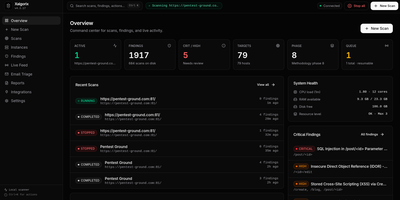
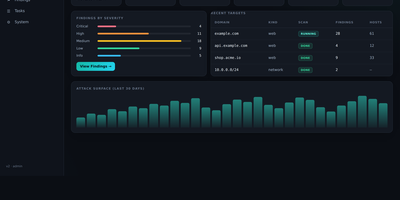
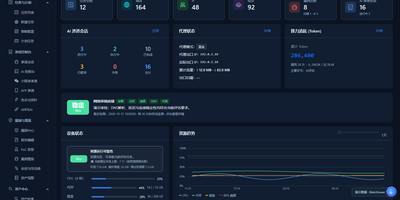
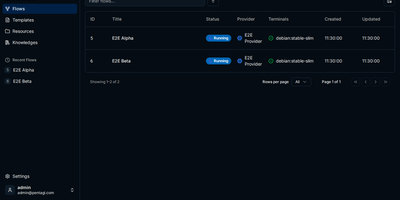
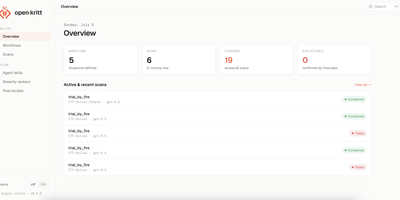
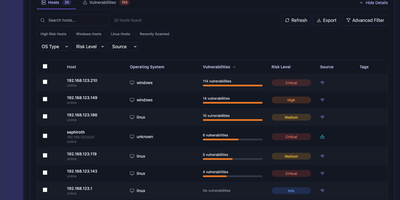
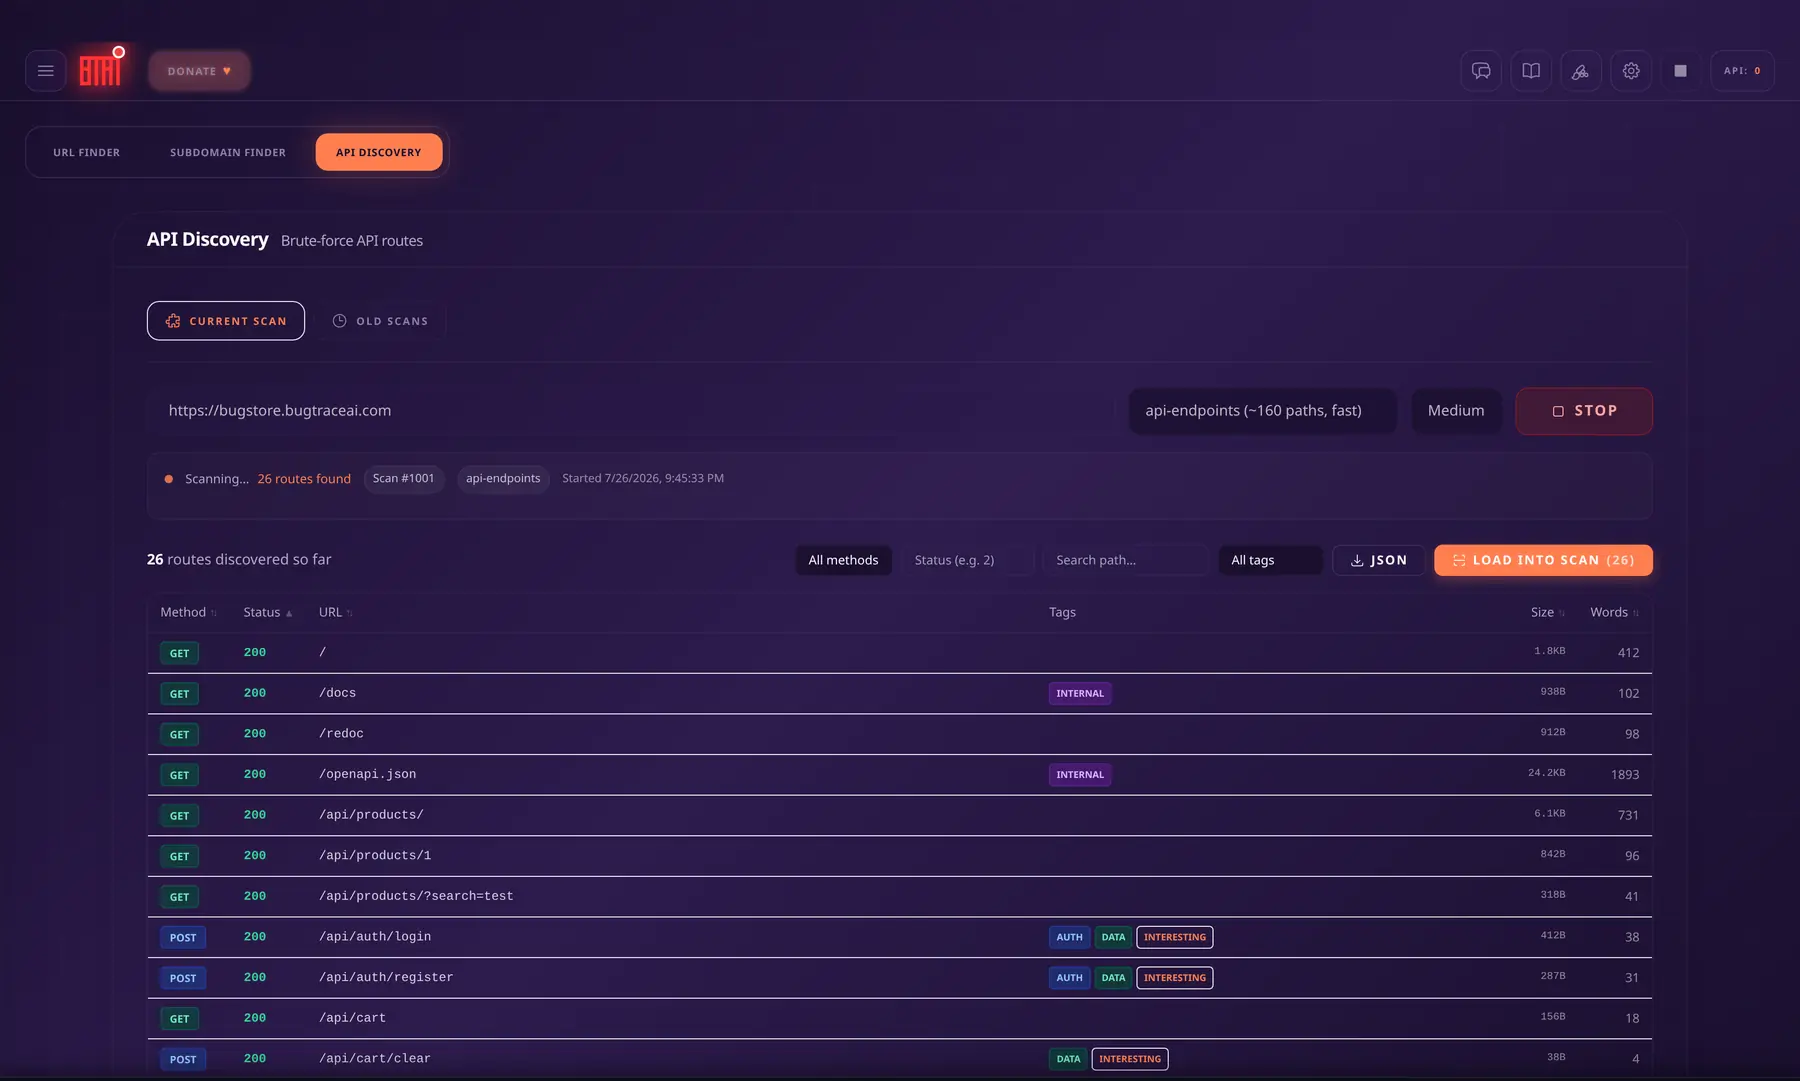
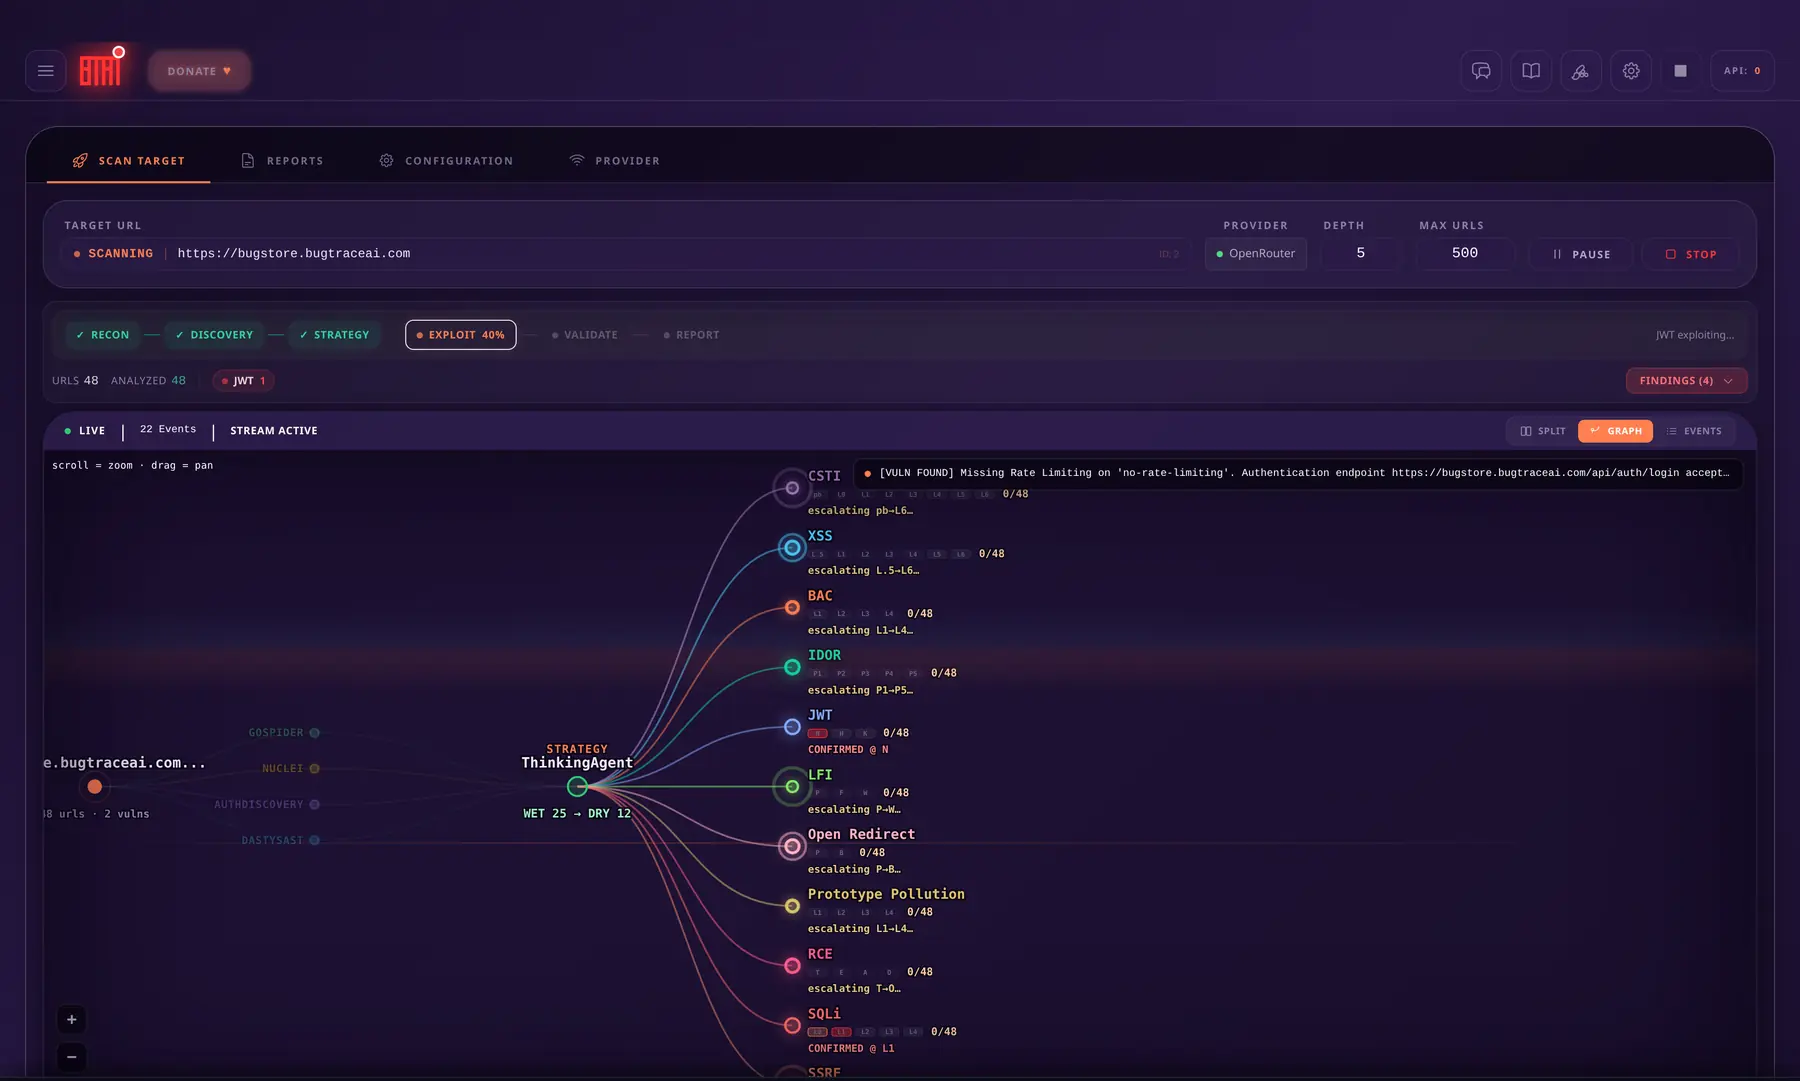
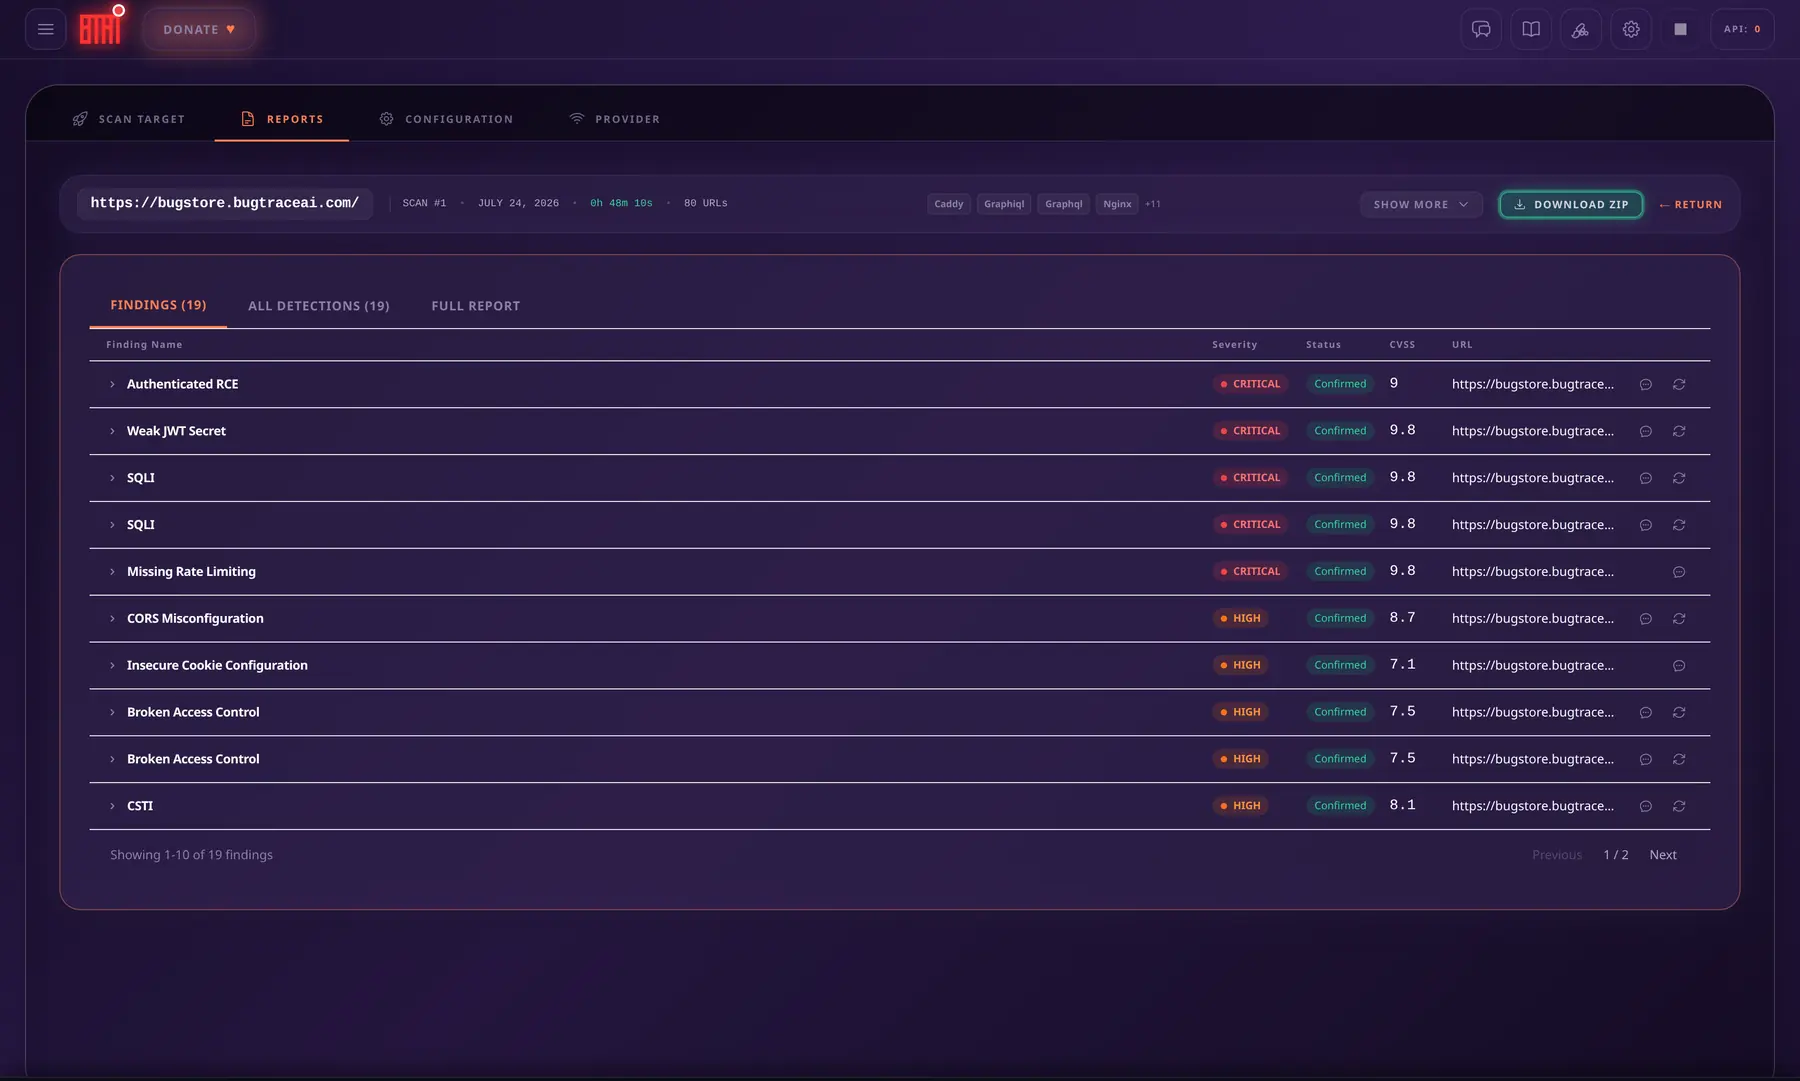
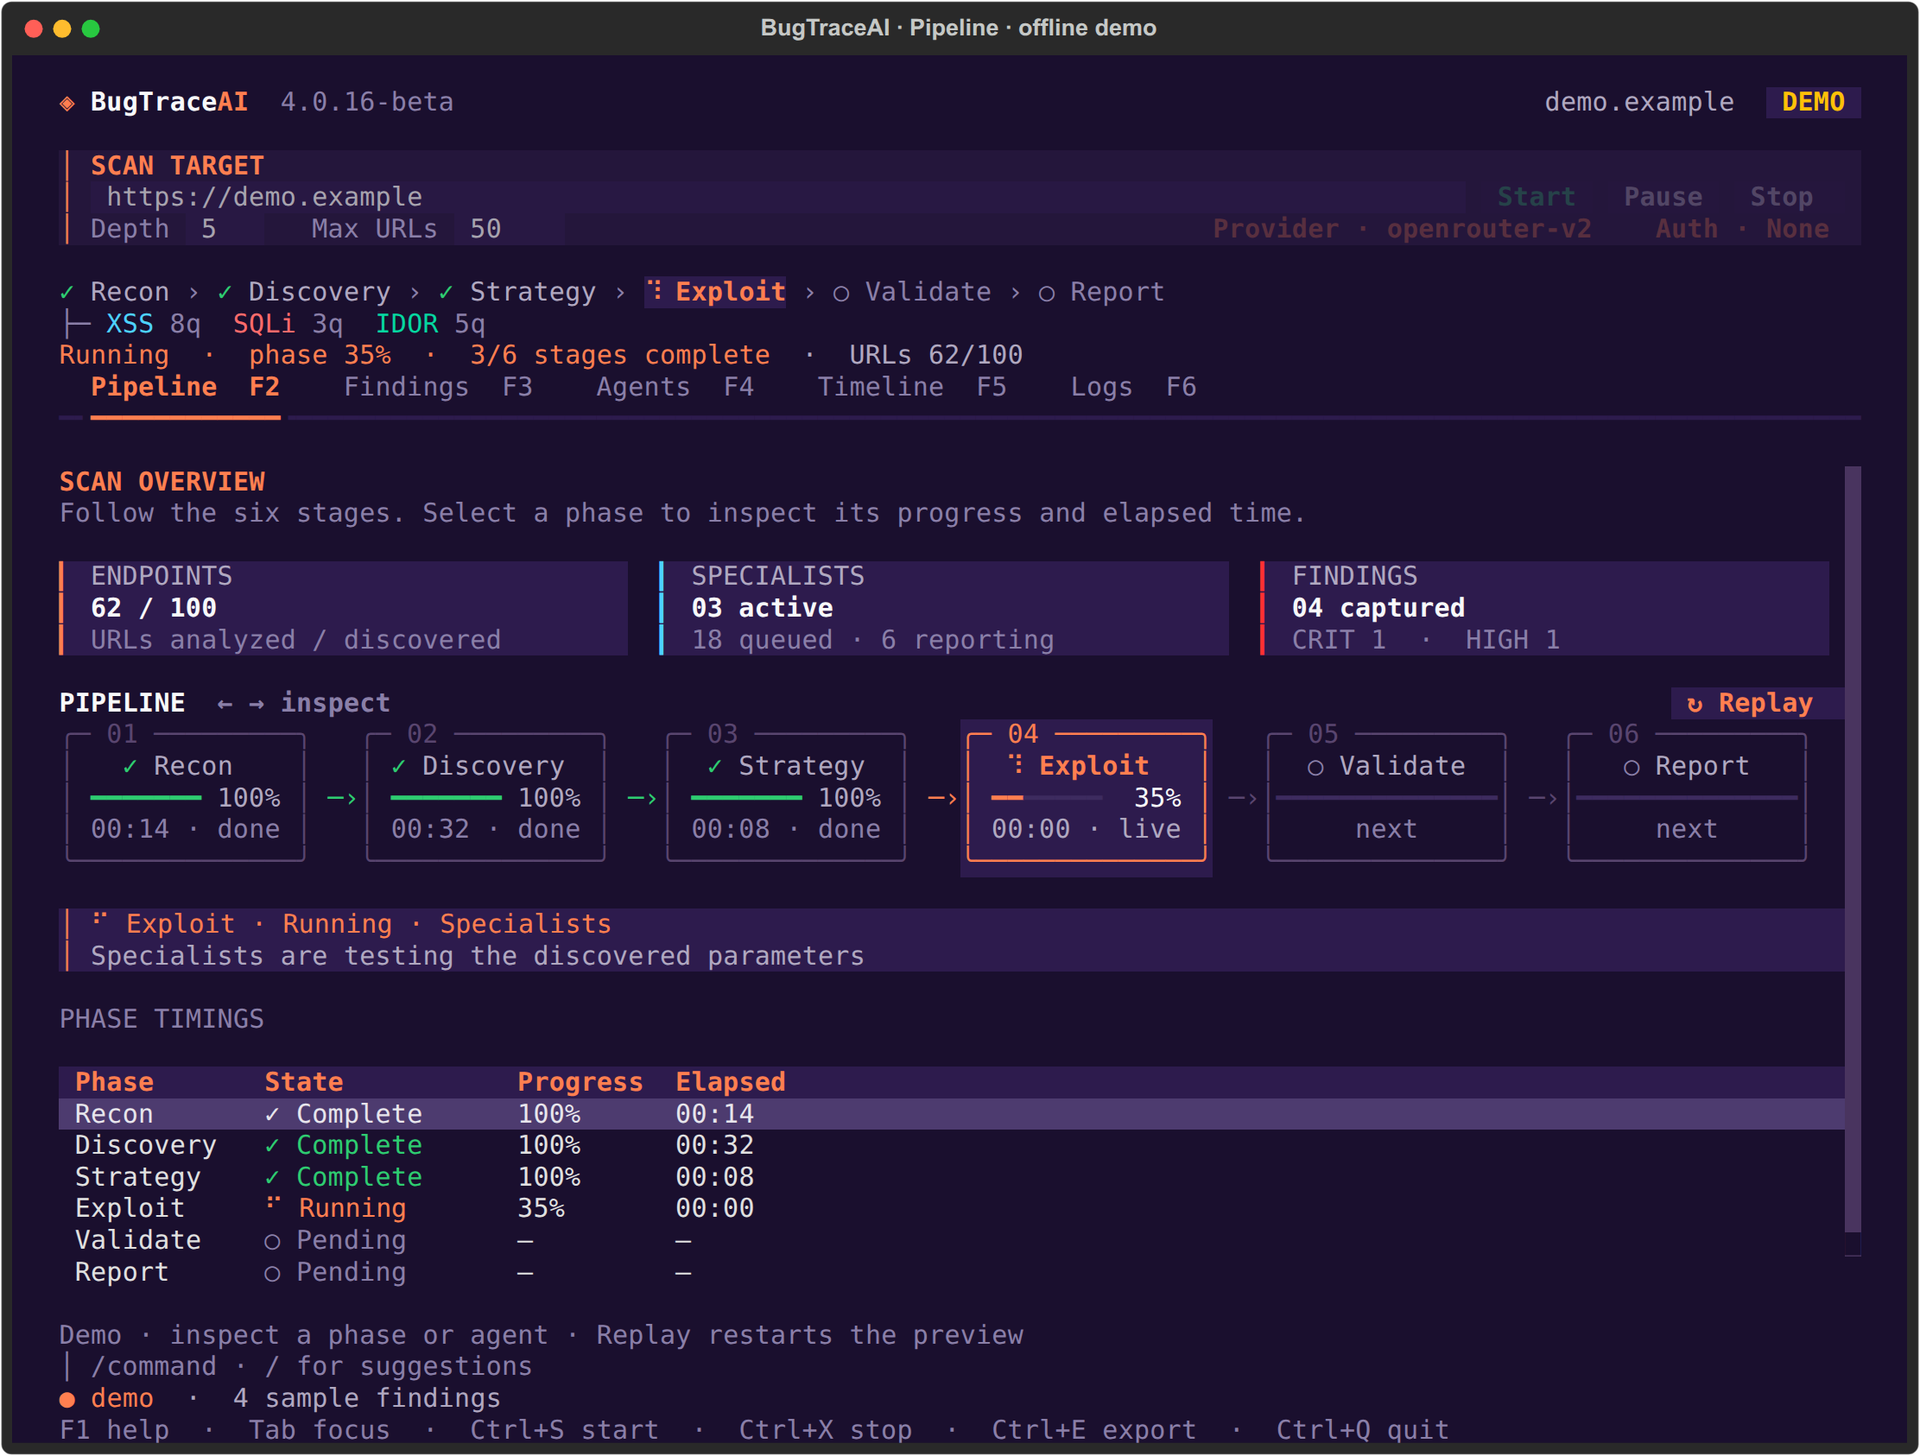
Point an AI pentesting crew at a web app you own and watch it hunt: BugTraceAI plans the checks, sends specialist agents after each weakness class, and brings back evidence you can inspect. A scan moves through six visible phases, from crawling and endpoint discovery through strategy, exploitation and validation, and ends in a findings table where every result carries a severity, a CVSS score and a confirmed status. The web dashboard follows the hunt live as a graph of specialists branching from a coordinating agent, and its API discovery workspace brute-forces routes and loads the interesting ones straight into a scan. Analysts get their own toolbox of more than twenty utilities for poking HTTP traffic by hand, an AI repeater for replaying requests, and ModelLab for comparing models on cost and results. Findings download as a ZIP with the full report, and a terminal workspace with pipeline, findings, agents, timeline and logs views suits keyboard-driven work. Bring your own model through OpenRouter, Anthropic, Z.ai or a local endpoint, and aim the whole suite at the bundled BugStore practice shop when you want to rehearse safely. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- Agents Hunt, Evidence Decides
- Specialist agents chase XSS, SQL injection, IDOR, JWT and other weakness classes in parallel, and every candidate passes a validation stage, so reports list confirmed issues with proof attached instead of scanner noise.
- Your Targets, Your Infrastructure
- Scans run from your own server against apps you are authorized to test, with reports and evidence stored locally, so sensitive vulnerability data never sits in a third-party cloud waiting to leak.
- Terminal, Browser Or Automation
- Drive scans from the terminal workspace, watch them in the web dashboard, or call the REST and MCP interfaces from CI, choosing the surface that fits a quick check or a scheduled pipeline.
- Practice Without Production Risk
- The included BugStore shop ships with 32 planted OWASP vulnerabilities, giving your team a legal target to learn the suite, rehearse triage and demo the workflow before touching real systems.
Features
- Six-Phase Scan Pipeline
- Recon crawls the target, discovery maps endpoints, strategy routes work to specialists, exploit gathers evidence, validate confirms each finding, and report generates structured deliverables.
- Live Specialist Graph
- The dashboard draws the scan as a living graph with specialist agents branching from a coordinator, phase progress, event stream and a findings counter updating in real time.
- API Discovery Workspace
- Brute-force API route discovery lists methods, status codes, sizes and tags for every path found, and loads selected routes directly into a full scan with one action.
- Evidence-Rich Reports
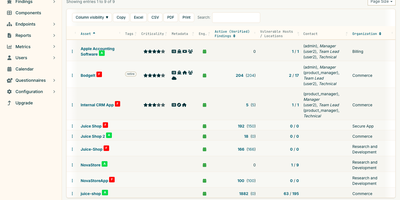
- Findings explorers show severity, CVSS and confirmation state per issue, and one download produces a ZIP containing the report, validated findings JSON and specialist traces.
- Modular Suite Components
- A launcher installs the CLI engine, WEB dashboard and API testing service in any combination, with MCP integrations for ReconFTW and other security tools and published security model checkpoints.