Developer links
Email OAuth 2.0 Proxy
Your scanner still emails PDFs, your backup scripts still send nightly reports, and none of them will ever learn OAuth 2.0: Email OAuth 2.0 Proxy learns it on their behalf. It listens on local IMAP, POP, and SMTP ports on your server, and when a client logs in the old-fashioned way with a username and password, the proxy swaps that exchange for a modern SASL XOAUTH2 token before the connection ever reaches the provider. The client never knows anything changed, so ancient mail apps, embedded devices, monitoring tools, and hand-rolled scripts keep sending and fetching mail through Outlook, Office 365, Gmail, Google Workspace, Fastmail, Yahoo, AOL, and any other provider that demands OAuth 2.0. The hop from your client to the proxy stays simple, while the proxy opens a fully encrypted TLS connection upstream, including STARTTLS negotiation for SMTP relays that require it. One proxy instance serves many accounts at once, with each mailbox mapped to its own local port and its tokens cached under a password you control. Optional plugins can even rewrite traffic in flight: strip Microsoft Defender Safe Links back to their real URLs, stop duplicate sent messages, or swallow test mail into a black hole. Setup is a single configuration file covering server ports, per-account scopes, and token endpoints, and the proxy then runs quietly as a headless service. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- Legacy clients keep working
- Scanners, NAS boxes, monitoring scripts, and older mail apps keep using plain username and password logins while the proxy performs OAuth 2.0 for them, so forced provider migrations stop breaking working setups.
- Every major provider covered
- Works with Outlook, Office 365, Hotmail, Gmail, Google Workspace, Fastmail, Yahoo, Comcast, and AOL, plus any service exposing standard OAuth 2.0 endpoints for IMAP, POP, or SMTP access.
- Encrypted where it matters
- The local hop stays unencrypted so unmodified clients can connect, but the proxy always opens a secure TLS session to the real server, handling implicit SSL and SMTP STARTTLS negotiation automatically.
- Many accounts, one service
- A single daemon on your server hosts separate local ports per provider and account, caches each mailbox's tokens under your password, and runs headless as a background system service.
Features
- Transparent XOAUTH2 translation
- Intercepts IMAP, POP, and SMTP login and authenticate commands and replaces them with SASL XOAUTH2 credentials, leaving the client application completely unaware of the upgrade.
- Per-account local ports
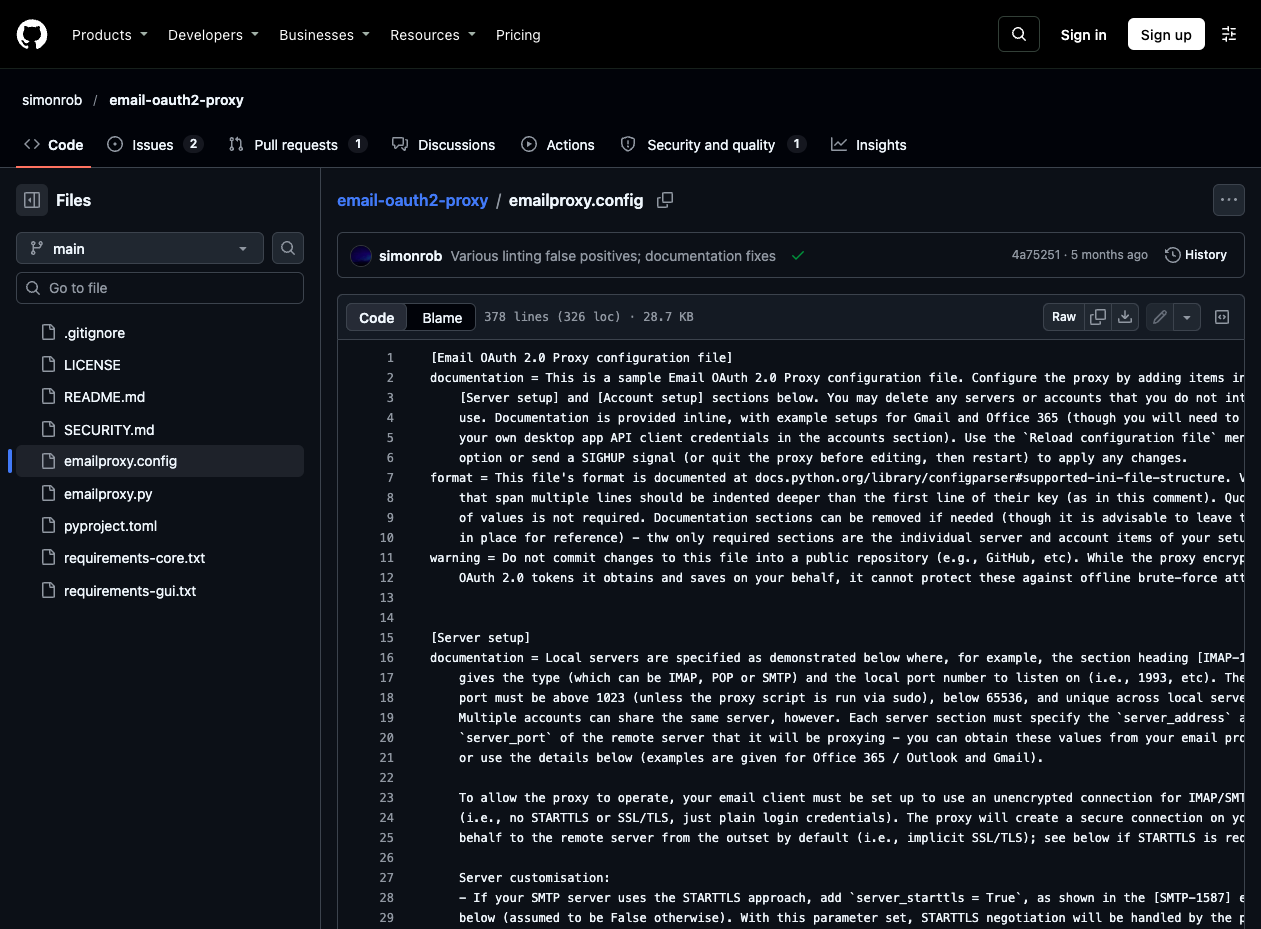
- Configuration maps each provider and mailbox to its own listening port, such as IMAP on 1993, POP on 1995, and SMTP on 1587, all defined in one INI file.
- Unattended server authentication
- Supports the OAuth 2.0 client credentials flow alongside interactive authorisation, so scripts and services on a headless machine can authenticate without any browser sign-in.
- Traffic-rewriting plugins
- Optional plugin scripts modify commands in flight: restore URLs rewritten by Microsoft Defender Safe Links, prevent duplicated sent mail, regex-replace message content, or black-hole test sends.
- Password-protected token cache
- Access and refresh tokens are stored encrypted behind a password you choose, and accounts can inherit shared provider settings to keep large configurations small.