HeadlessX
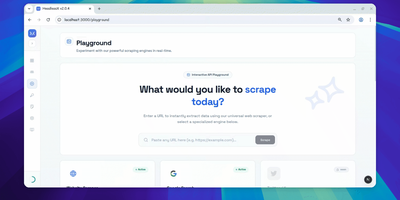
With 2,000 GitHub stars and 10 releases since its September 2025 launch, HeadlessX delivers a self-hosted browser automation platform that replaces Chromium-based scraping with Camoufox — a Firefox fork performing kernel-level fingerprint spoofing to achieve 0% detection across Cloudflare, DataDome, PerimeterX, and other anti-bot systems where Puppeteer and Playwright regularly fail. The web dashboard provides workspace-based job organization with a visual interface for configuring scrape targets, managing browser profiles, monitoring queue status, and viewing extracted results in real time. The protected REST API accepts requests with API key authentication for programmatic access, supporting HTML extraction, screenshot capture, PDF generation, and structured data parsing with configurable stealth parameters. Profile-based scraping maintains persistent browser contexts with cookie jars, localStorage, and fingerprint configurations that survive between requests — reducing cold-start latency from 25 seconds to under 2 seconds on subsequent requests. Queue-backed workflows enable batch processing of URLs with configurable concurrency, retry logic, and webhook notifications on completion. The Google AI Search integration provides AI-assisted web research workflows through dedicated endpoints. Remote MCP support exposes automation capabilities as tool endpoints for AI agent integration. Deploy via the official CLI with `headlessx init` and `headlessx start` commands, scaffolding a Docker Compose stack with Caddy reverse proxy for automatic HTTPS. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
GitLab
Used by over 100,000 organizations and ranked first in the Gartner Magic Quadrant for DevOps Platforms, GitLab is the open-core DevSecOps platform that delivers the complete software development lifecycle — from planning and source code management through CI/CD, security scanning, and monitoring — in a single self-managed application. The built-in CI/CD engine executes pipelines defined in YAML with parallel jobs, directed acyclic graph scheduling, multi-project pipelines, and auto-scaling runners on Docker, Kubernetes, or bare metal. Merge requests provide inline code review with approval rules, code owners, merge trains for serialized merging, and five merge strategies including fast-forward and semi-linear history. The integrated container registry stores Docker images alongside code, while the package registry supports npm, Maven, NuGet, PyPI, Conan, Go, and generic packages. Issue boards with epics, milestones, and labels enable agile planning, while the built-in wiki and GitLab Pages provide documentation hosting and static site publishing. Security scanning in the Community Edition includes basic SAST, secret detection, and container scanning running as pipeline jobs. The Omnibus installer bundles Rails, Puma, Gitaly, Workhorse, Nginx, PostgreSQL, Redis, Sidekiq, and Prometheus into a single package installable in minutes, while Docker and Helm chart options support containerized and Kubernetes deployments. GitLab Duo AI assists with code suggestions, merge request summaries, and vulnerability resolution. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Unleash
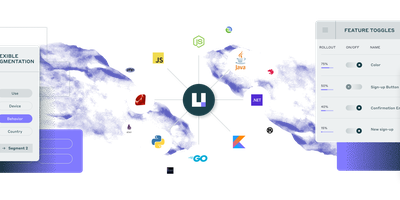
Deployment decoupled from release: Unleash, the most popular open-source feature management platform on GitHub, is a Node.js server backed by PostgreSQL. Ship code dark, then control who sees it through activation strategies: gradual percentage rollouts, targeting by user ID, IP, hostname, or application name, custom constraints against your own context fields, and scheduled or time-limited releases. Strategies stack - a flag activates if any strategy matches - and strategy variants layer A/B versions on top of the on/off decision. Each flag carries per-environment configurations, so a feature can run at 100% in staging while canarying at 5% in production. Backend SDKs (Node.js, Java, Go, Python, Ruby, .NET, PHP, Rust, and more) fetch configuration and evaluate flags locally, so a flag check adds zero network latency to request paths; frontend SDKs for React, Vue, Svelte, iOS, Android, and Flutter evaluate through a proxy layer. Flag hygiene is built in: flags are typed (release, experiment, operational, kill-switch, permission) with expected lifetimes, and Unleash marks overdue flags as potentially stale and surfaces unknown flags your SDKs request but that don't exist. Self-hosting via Docker keeps flag data, targeting rules, and evaluation infrastructure entirely on your side.
PowerDNS-Admin
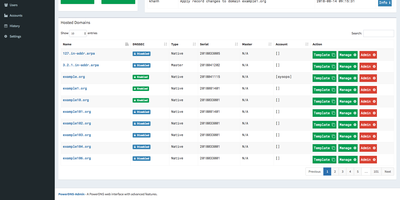
Raw zone files and API calls become something a whole team can operate safely once PowerDNS-Admin puts its web interface in front of a PowerDNS authoritative server. It's a Python/Flask application covering full forward and reverse zone management, with the touches that matter in daily DNS work: zone templates for stamping out consistent new domains, easy IPv6 PTR record editing (reverse zones by hand are misery), full IDN/Punycode support for internationalized domains, and DynDNS 2 protocol support so routers and scripts can update records the way they would against a commercial dynamic-DNS service. Access control is enterprise-grade: local users, LDAP against OpenLDAP or Active Directory, SAML, and OAuth via Google, GitHub, Azure, or OpenID Connect, hardened with TOTP two-factor authentication. Role-based permissions extend to zone-specific access control - hand a developer their project's zone without exposing the rest of your namespace - and activity logging records who changed which record when, the audit trail bare PowerDNS never gives you. The dashboard monitors PDNS service configuration and statistics, and its own API exposes zone and record management for automation on top of the UI. Runs against MySQL/MariaDB or PostgreSQL, talking to PowerDNS through its REST API. MIT-licensed.
LeafWiki
Engineering teams and technical writers maintain operational runbooks, system documentation, and knowledge bases using LeafWiki, an open-source self-hosted wiki that stores page contents directly as human-readable Markdown files on the local filesystem. Authors can compose documentation through a dual-pane editor equipped with live HTML preview, keyboard navigation, autocomplete for internal links, and native rendering for Mermaid diagrams, KaTeX mathematical formulas, and collapsible callout containers. The navigational tree organizes complex documentation into explicit directory hierarchies and custom drag-and-drop page sequences tracked in lightweight configuration files rather than arbitrary alphabetical lists. An integrated SQLite engine indexes page content and custom taxonomy tags for fast full-text searches, automatic incoming backlink tracking, and automated broken link detection. System operators can deploy the single-binary application without external database servers or runtime dependencies, backing up the entire repository by copying the data directory. Administrators can provision granular user roles, configure reverse proxy header authentication for single sign-on gateways, and manage read-only API access keys for automated documentation scripts and continuous integration pipelines. Public viewers can browse technical notes without authentication or switch between dark and light high-contrast themes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Portabase
Portabase takes a zero-trust approach to database backups: lightweight Rust/Tokio agents deploy next to each database, encrypt dumps with AES-GCM before data ever leaves the host, and poll the Next.js control plane outbound every five seconds requiring zero inbound firewall rules. This architecture contains blast radius if the dashboard is compromised while supporting ten engines with stable backup and restore: PostgreSQL 12 through 18, MySQL 5.7 through 9, MariaDB 10 and 11, MongoDB 4 through 8, SQLite 3.x, Redis 2.8+, Valkey 7.2+, Firebird 3.0 through 5.0, Microsoft SQL Server 2017 through 2022 including Azure SQL, and Docker volumes on Engine 20.10+. Encrypted backups store on configurable backends including local filesystems, any S3-compatible provider (AWS, MinIO, RustFS), Google Cloud Storage, and Azure Blob Storage. Cron-based scheduling with Grandfather-Father-Son retention policies automates backup lifecycle management, while on-demand restore targets any compatible server for cross-environment recovery. The CLI installs agents with a single command and auto-updates when new versions ship. A RESTful API with MCP server integration enables automation from CI/CD pipelines and AI agent workflows. Developed by a non-profit under Apache-2.0. 1,270+ stars and 174 releases since October 2024. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console.
Plandex
With 15,500 GitHub stars and over 1,100 forks, Plandex delivers a terminal-based AI coding agent purpose-built for the complex, multi-file tasks that overwhelm single-file AI assistants. The Go-powered server maintains a cumulative diff review sandbox that quarantines all AI-generated changes from your project files until you explicitly approve them — enabling 20-file refactors where you cherry-pick good changes and reject bad ones without touching git. A 2M token effective context window loads only what each step requires, while tree-sitter project maps index repositories exceeding 20M tokens across 30+ programming languages, providing structural awareness of class hierarchies, function signatures, and import graphs without burning tokens on full file content. The configurable model pack system assigns different models to different roles — Claude for planning, GPT for coding, Gemini for summarization — supporting Anthropic, OpenAI, Google, OpenRouter, Azure OpenAI, AWS Bedrock, DeepSeek, Perplexity, and Ollama for local models. Full auto mode handles end-to-end autonomous workflows including high-level planning, context loading, implementation, terminal command execution, and automated debugging of both terminal and browser applications. The interactive REPL provides fuzzy auto-complete, version-controlled sandbox branching, rewind to any previous point, and Git integration for commit message generation. The Plandex Server exposes 60+ REST API endpoints for programmatic orchestration across organizations, projects, plans, and branches. Deploy via Docker Compose for self-hosted operation with your own API keys. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Nimbus
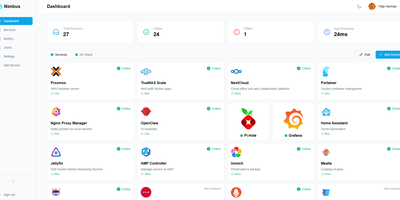
Nimbus is a self-hosted homelab dashboard that turns your scattered pile of services into a polished, organized command center with real-time health monitoring for every endpoint you care about. The dashboard displays live status cards for each registered service, tracking response times down to the millisecond and graphing uptime history so you can spot degradation before it becomes an outage. Health checks run on configurable intervals with smart self-signed certificate handling, meaning your internal services with self-issued TLS do not trigger false alarms. Multi-user support comes standard: local accounts authenticate via JWT, while OAuth2 integration with Google, GitHub, and Discord lets team members sign in with existing credentials. Role-based access control and a built-in admin panel give you granular authority over who sees what. Each user personalizes their view with custom backgrounds, light or dark mode, accent color themes, and drag-and-drop service tile arrangement. Services group into named categories and cards resize to fit your preferred layout, with both grid and list view modes available. Prometheus metrics export feeds your existing Grafana stack, and webhook notifications alert you instantly when a service goes offline. Custom service icons upload directly or auto-fetch from the Dashboard Icons collection. Zero-config Docker deployment gets you running in under 30 seconds with a single docker-compose command. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Flipt
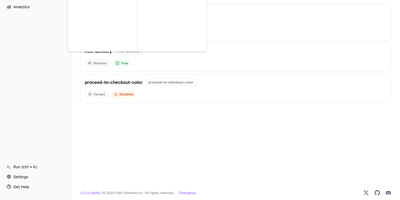
Backed by 4,800+ GitHub stars and trusted by teams replacing LaunchDarkly and Split with a self-hosted solution, Flipt v2 delivers the first truly Git-native feature management platform that treats feature flags as code stored in your own repositories. The architecture eliminates all database dependencies by building immutable in-memory snapshots from YAML flag definitions on every Git commit, delivering sub-millisecond evaluation latency with zero external runtime dependencies beyond the single Go binary. Multi-environment support maps directly to Git abstractions — separate repositories per environment, different directories within the same repository, or different branches — enabling teams to use their existing branching strategy, pull request workflows, and code review processes for flag changes. The evaluation engine supports boolean flags, multivariate string and numeric variants, segment-based targeting with constraint rules, percentage rollouts, and namespace isolation. Native SCM integration with GitHub, GitLab, BitBucket, Azure DevOps, and Gitea creates merge proposals directly from the UI with GPG-signed commits. Flipt implements the OpenFeature Remote Evaluation Protocol with official providers for Go, Node.js, Python, Java, C#, Ruby, and Web SDKs, enabling vendor-agnostic flag evaluation across all services. The gRPC API with REST HTTP gateway exposes flag management, evaluation, and analytics endpoints. Offline mode continues serving flags when the source repository is temporarily unavailable. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Fair Core License (server) / MIT (client SDKs).
ServerBee
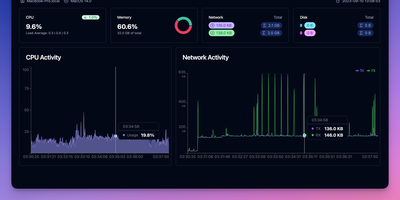
ServerBee delivers complete fleet monitoring from a single Rust binary that embeds both the server and web UI, requiring no external database or heavy runtime. Lightweight agents installed on each node stream CPU, memory, disk, network, load, temperature, GPU, and disk I/O metrics over persistent WebSocket connections to a central server backed by embedded SQLite. The real-time React dashboard presents 17 drag-and-drop widget types across custom layouts, with historical charts spanning one hour to 30 days and monthly traffic statistics with billing-cycle prediction and cost insights including burn rate and per-resource unit cost scoring. Network monitoring covers ICMP, TCP, and HTTP ping probes, service monitors for SSL certificates, DNS records, HTTP keyword matching, TCP ports, and WHOIS expiration, plus network-quality probing across 96 China 3-ISP and international presets with IP-quality and streaming-unlock detection. Remote management features include a web terminal with sandboxed file manager, Docker container stats with logs and events, firewall configuration, and agent auto-update capabilities. Public status pages display 90-day uptime timelines, while alerting supports email and webhook notifications with flexible trigger expressions. A native iOS companion app provides mobile monitoring access. Deploy via Docker or download the single binary for Linux, macOS, or Windows, running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Statping-ng
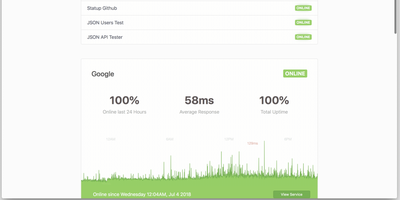
A status page and uptime monitor in one Go binary: Statping-ng - the actively maintained fork of Statping - replaces the UptimeRobot-plus-Statuspage combo with a ~20 MB Docker image using under 50 MB of RAM. It checks services over HTTP, TCP, UDP, ICMP ping, and gRPC health checks on configurable intervals, with per-service timeouts, expected status codes, POST requests with custom JSON bodies, SSL verification, and failure thresholds before alerting. The public status page is the differentiator against plain monitors: visitors see live status, uptime percentages, and latency charts grouped into service categories, with incident announcements and scheduled-maintenance messages you publish from the dashboard - and Sass-based custom styling matches the page to your brand rather than a vendor template. When something fails, notifiers fire immediately: Slack, Discord, Telegram, SMTP email, PagerDuty, Twilio SMS, Pushover, and custom webhooks, each testable before saving. Because notifiers are single Go files, the plugin system makes new channels straightforward. A RESTful API manages services and reads uptime data programmatically, and the free Statping mobile app connects to your server via QR code for on-the-go monitoring. Data persists to SQLite, MySQL, or PostgreSQL. Point it at internal services too - anything the container can reach is monitorable.
Stormkit
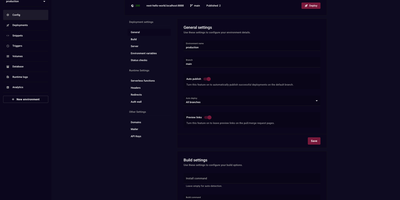
Stormkit delivers a self-hostable PaaS that eliminates vendor lock-in while providing Vercel-class deployment workflows. The Go backend handles build orchestration, hosting, and background job processing while the React frontend provides a complete management dashboard for applications, environments, and team collaboration. Git integration with GitHub, GitLab, and Bitbucket enables push-to-deploy workflows where every commit triggers automated builds with preview links posted directly to pull requests. Serverless functions use filesystem-based routing — each TypeScript or Node.js file in the API directory becomes an endpoint automatically, deploying to AWS Lambda with configurable timeouts. PostgreSQL database schemas ship with automatic migrations, isolated credentials per environment, and secure environment variable injection preventing credential leakage between staging and production. Custom domains provision TLS certificates automatically through Let's Encrypt with support for custom certificates and headers. The environment system creates isolated deployment contexts for production, staging, and development with independent variables, domain bindings, and auto-publish rules per branch. Privacy-respecting server-side analytics track visitors, referrers, and top paths without client cookies or third-party scripts. Role-based access control manages team permissions across applications. Docker Compose deployment provisions the full stack including the API server, hosting service, build runner, and worker server. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Nixopus
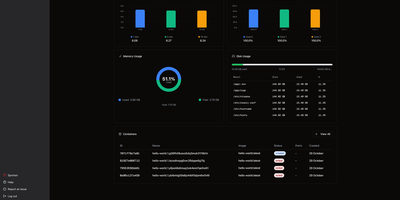
Tell an AI agent to deploy your app and watch it actually happen. Nixopus connects to your GitHub repo, analyzes the codebase to detect your framework, generates the right Docker configuration, resolves dependency conflicts, and ships the whole thing to your server with HTTPS enabled. When something breaks, the agent reads the logs, creates a pull request with a fix, and redeploys without waking you up. The chat interface lets you deploy, add custom domains, check logs, roll back, and troubleshoot in plain English from the web dashboard or directly from your VS Code or Cursor editor. Extensions bring one-click installs for 100+ self-hostable apps like Appwrite, Excalidraw, and Ollama, each showing you exactly what it runs on your server before installation. Connect multiple servers and monitor CPU, memory, disk, and running containers across your entire fleet from a single dashboard with draggable widget layouts. The built-in terminal opens SSH sessions right in the browser with split-pane support, so you can watch logs in one pane while running commands in another. Framework detection covers Next.js, Django, Rails, Go, FastAPI, and anything else that fits a container image. Every deployment gets automatic TLS via Caddy with Let's Encrypt certificates provisioned and renewed silently. Previous container images are retained so rollbacks skip the rebuild step entirely. Deploy on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Apprise-API
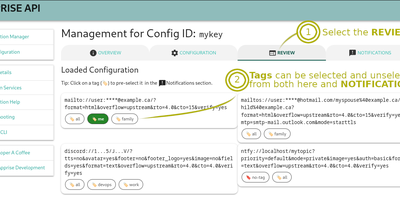
One REST call, 130+ notification services: Apprise API wraps the well-known Apprise library in a lightweight Django/Gunicorn microservice, so "send an alert" works the same whether it goes to Slack, Discord, Telegram, Teams, email, SMS, Pushover, or PagerDuty - each addressed by a simple URL scheme. It solves the credential-sprawl problem cleanly: instead of embedding provider tokens in every app, cron job, and CI pipeline, you centralize them here and everything else just POSTs a body and title. Two modes cover every workflow. Stateless calls to /notify carry target URLs in the payload (or fall back to a default set via APPRISE_STATELESS_URLS); stateful mode stores named configurations server-side under keys, so /notify/{KEY} fans out to everything registered - with tag-based routing (comma for OR, space for AND) selecting which endpoints fire per message. Messages take info, success, warning, or failure types in text, Markdown, or HTML, with attachments up to a configurable size. A built-in web UI manages and tests configurations, APPRISE_CONFIG_LOCK makes the store read-only, service allow/deny lists restrict which schemes work, webhook remapping adapts third-party payloads, and a Prometheus /metrics endpoint watches the gateway itself.
HolyClaude
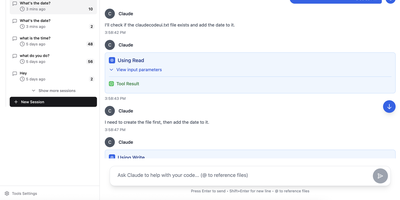
With 2,400+ GitHub stars, HolyClaude replaces a two-hour manual setup process with a single docker compose up command that launches a fully configured AI coding workstation. The container ships with Claude Code pre-installed alongside seven additional AI CLIs — Gemini CLI, OpenAI Codex, Cursor, TaskMaster AI, Junie, OpenCode with OpenRouter multi-provider support, and Pi Coding Agent — all accessible through the CloudCLI browser-based web interface on port 3001. A headless Chromium browser running on Xvfb display :99 comes pre-configured with Playwright 1.61 for automated screenshots, testing, and web scraping without additional setup. The development toolchain includes Node.js 26, Python 3, TypeScript, git, GitHub CLI, database clients for PostgreSQL, SQLite, and Redis, plus deployment CLIs for Vercel, Wrangler, Netlify, and Azure. Process management uses s6-overlay for automatic restarts and graceful shutdown, while bind mounts to ./data/claude and ./workspace ensure credentials, configuration, and project files persist across container rebuilds. The full image supports AMD64 and ARM64 architectures, running on Linux, macOS with Docker Desktop, Windows with WSL2, and Synology or QNAP NAS hardware. A slim tag at roughly 2GB omits the browser stack for environments that do not need it, while the full image at 4GB includes everything. Users authenticate with their existing Anthropic account directly through Claude Code with no credential relay or proxy involved. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
KrakenD
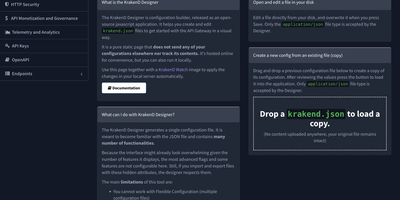
KrakenD processes over 18,000 requests per second on a single instance while consuming under 50MB of RAM at 1,000 concurrent connections, operating as a stateless API gateway that requires no database whatsoever. The Community Edition has earned over 2,600 GitHub stars by outperforming database-dependent alternatives like Kong and Tyk in independent benchmarks. Written entirely in Go, it uses declarative JSON or YAML configuration files that integrate directly into GitOps workflows for version-controlled infrastructure management. The gateway aggregates responses from multiple backend services into a single API call, transforms request and response payloads with field filtering, grouping, and mapping, and applies zero-trust security policies including JWT validation, OAuth 2.0, CORS, HSTS, clickjacking protection, and XSS prevention. Traffic management features include multi-layer rate limiting at both the router and proxy levels, circuit breakers for backend fault isolation, spike arrest policies, and concurrent call support that requests the same data from multiple backends in parallel for improved response times. Telemetry integrates with OpenTelemetry, Prometheus, Grafana dashboards, Datadog, Zipkin, and Jaeger for distributed tracing and metrics collection. The gateway extends through Go plugins, Lua scripting, Martian modifiers, and Google CEL expressions for custom request processing logic. AI workload routing supports OpenAI, Anthropic, Gemini, and other model endpoints with built-in fallback, retries, and load balancing. Deploy via Docker with the devopsfaith/krakend image as a single binary. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Verdaccio
Private npm packages without shipping code to the public registry or paying for npm Enterprise: Verdaccio is the standard lightweight, zero-config private registry and caching proxy. It runs as a single Node.js process with its own tiny embedded database; no external database is required to start. Point npm, yarn, or pnpm at it and everything behaves as expected: install, publish, unpublish, dist-tags, and deprecation all work against the standard npm endpoints. The uplink system is where it earns its keep: packages not found locally are fetched from configured upstreams (npmjs.org, yarn, JFrog, Nexus, or another Verdaccio), cached as tarballs, and served locally thereafter - cutting CI latency and surviving registry outages. Multiple uplinks chain for failover, and per-package glob patterns in config.yaml route scopes to specific upstreams while controlling access, publish, and unpublish rights per group. You can even override a public package by publishing a patched version under the same name locally. A plugin architecture swaps in auth backends (htpasswd default, LDAP and others available), storage drivers (S3, Google Cloud Storage), middleware routes, and metadata filters. With official Docker images and a Kubernetes Helm chart, it slots into any pipeline in minutes.
Kener
A polished public status page without Statuspage prices or a heavyweight observability suite: Kener is a status and uptime monitoring system built with SvelteKit and Node.js. It runs 11 monitor types - API, Ping, TCP, DNS, SSL certificate, SQL query, Heartbeat, gRPC, and GameDig game-server checks among them - each with configurable intervals and thresholds. Incident management covers the full lifecycle: structured timelines from investigation through resolution, acknowledgements, and subscriber-visible updates, plus maintenance windows with RRULE-based recurring schedules and automatic status transitions. Notifications reach email, Slack, Discord, and custom webhooks through trigger-based workflows with template-driven messaging. One instance can serve multiple branded status pages - per product, team, or region - with custom logos, colors, and CSS, localization into 21 languages, timezone-aware displays, and server-rendered pages that stay fast and SEO-friendly. Operations tooling includes role-based access for teams, API key management, a secrets vault, analytics integrations (Google Analytics, Plausible, Umami, and others), and a REST API with 17+ endpoints for automating incidents and monitors from CI/CD. MIT-licensed; Docker deployment with Redis, SQLite by default, PostgreSQL or MySQL for production.