Mira
The fastest tool on the public Martian Code Review Bench at 77 seconds per PR with competitive F1 scores — while every higher-scoring competitor takes 5 to 14 times longer — Mira is the fully open-source AI code reviewer that ships the entire feature surface other tools gate behind per-seat subscriptions: indexed PR reviews with full-repo context, streaming walkthroughs posted within seconds, inline vulnerability scanning from hourly OSV.dev polls, org-wide package inventory answering "which repos use [email protected]?" in one query, interactive dependency graphs with blast-radius SVG rendering via ReactFlow, a learning loop that synthesizes rules from rejected comments and human review patterns on merged PRs, and cost telemetry showing actual spend per repo and per model. Unlike CodeRabbit, Greptile, and GitHub Copilot code review which are SaaS-only with per-seat pricing, Mira runs as a single Docker image on your infrastructure with your LLM key through OpenRouter (fronting Anthropic, OpenAI, Google Gemini, DeepSeek) or direct to Ollama and vLLM for fully air-gapped deployments. The engine indexes Python, TypeScript, Go, Rust, Java, C/C++, C#, Swift, Kotlin, Scala, and PHP with per-file symbol extraction, enabling multi-file reasoning across diffs rather than isolated line-by-line review. Integrates with GitHub, GitLab, and Forgejo via webhook with full feature parity. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
ZTNET
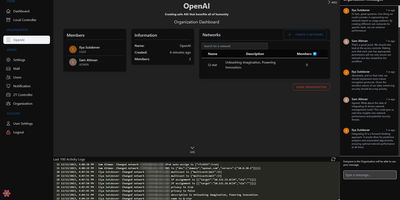
ZTNET provides a polished web dashboard for running your own ZeroTier network controller, covering network creation, member authorization, IP assignment, flow rule editing, and real-time node monitoring entirely from the browser. The organization system supports multi-tenant deployments where teams manage separate network pools with role-based permissions and customizable email notification templates for events like member joins, departures, IP changes, and authorization updates. Each network view displays connected members with their ZeroTier addresses, assigned IPs, last-seen timestamps, physical endpoints, and protocol versions in a clean tabular layout. The admin panel provides platform-wide user management, SMTP configuration for transactional emails, and system-level settings. Built on the T3 stack with Next.js, Prisma ORM, tRPC, TypeScript, and Tailwind CSS with DaisyUI components, the application supports both PostgreSQL and SQLite for persistence and communicates directly with the ZeroTier controller daemon through its native API. Dark and light themes adapt to user preference, and responsive layouts make network management practical from any device. Docker Compose bundles the web application alongside the ZeroTier controller service. Over 100,000 Docker pulls confirm steady community adoption. GPL-3.0 licensed.
Netdata
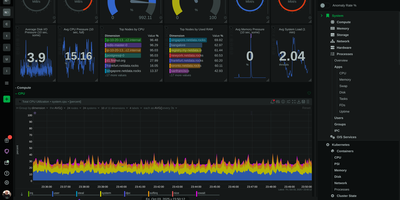
Trusted by millions of engineers and deployed on over 80,000 GitHub stars worth of community confidence, Netdata delivers true real-time monitoring at per-second granularity — 10-60x faster than Prometheus, Datadog, or any conventional monitoring stack that averages away the transient anomalies lasting 2-10 seconds where most production incidents originate. A single installation command deploys the agent with zero configuration, automatically discovering every running process, container, systemd service, network connection, disk, and application on the host within seconds. Unsupervised machine learning trains multiple models per metric directly at the edge, detecting anomalies without thresholds, baselines, or manual tuning. The distributed Parent-Child architecture scales horizontally from a single Raspberry Pi to fleets exceeding 100,000 nodes while maintaining sub-2-second visualization latency and storing metrics at approximately 0.5 bytes per sample through tiered compression. Native network monitoring provides live topology maps, NetFlow and sFlow analytics, SNMP device polling across 200+ profiles, and trap handling — capabilities that typically require a separate NPM product. Hundreds of pre-configured alerts cover systems and applications out of the box, with AI-powered root cause analysis surfacing correlated metrics through natural language via MCP-compatible AI assistants. The agent supports Linux, macOS, FreeBSD, Kubernetes, and Docker with eBPF-based kernel observability requiring no application instrumentation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL v3+ licensed.
Kopia
Engineers who have outgrown Duplicati or rsync scripts tend to appreciate Kopia's design: encrypted, compressed, content-deduplicated snapshots in Go, stored in a repository on any storage you control - S3, Google Cloud Storage, Azure Blob, Backblaze B2, SFTP, WebDAV, or a plain filesystem. Encryption is mandatory and end-to-end: every block is encrypted client-side with AES-256-GCM or ChaCha20-Poly1305 using keys derived from your repository password, and even file names never leave the machine in plaintext. Blocks are packed into 20-40 MB blobs with random names, so the storage provider learns nothing about content or structure. Deduplication is automatic and content-based - identical data across files, snapshots, and even multiple machines backing up to the same repository is stored once. Policies govern everything per-directory: compression choice, retention (hourly through annual), scheduling, and ignore rules. Incremental snapshots are point-in-time records you can mount and browse like a filesystem. This deployment runs the Kopia repository server with its web UI, centralizing backups from multiple client machines over an authenticated API - each client connects with the server URL and certificate fingerprint, and users only see their own snapshots. Error correction, high-latency-tolerant caching, and both CLI and GUI round it out.
Backstage
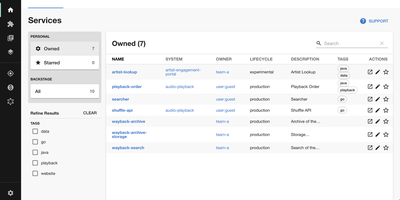
Adopted by over 3,400 companies and backed by 34,000 GitHub stars, Backstage is the open-source developer portal framework created by Spotify and now hosted by the Cloud Native Computing Foundation. The centralized Software Catalog registers every service, library, data pipeline, website, and ML model in your organization using YAML metadata files stored alongside code in GitHub, GitHub Enterprise, or GitLab, tracking ownership, lifecycle status, and dependency relationships across your entire ecosystem. Software Templates provide self-service infrastructure provisioning where developers fill out a form and Backstage automatically scaffolds new repositories, CI/CD pipelines, and cloud resources following your organization's standardized best practices. TechDocs renders Markdown documentation directly alongside the services it describes using a docs-like-code approach powered by MkDocs, with the TechDocs Addon Framework for extending the reading experience. The Search Platform indexes content across the catalog, TechDocs, Confluence, and Stack Overflow through configurable search backends. Kubernetes monitoring built specifically for service owners rather than cluster admins displays pod health, logs, and deployment status across any cloud provider or managed Kubernetes service. The plugin ecosystem includes over 230 open-source integrations covering CI/CD systems like GitHub Actions and GitLab Pipelines, monitoring platforms like Datadog and Grafana, cloud providers including AWS and Azure, plus specialized plugins for security scanning, cost management, API documentation, PagerDuty incident management, and Lighthouse website auditing. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Grafana OnCall
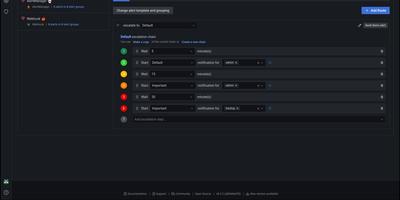
With 3,900 GitHub stars, 140 contributors, and 380 releases since its 2022 launch, Grafana OnCall delivers developer-friendly incident response that routes alerts from any monitoring system to the right engineer at the right time through the right channel. The platform accepts alerts via unique API URLs from Alertmanager, Grafana Alerting, Zabbix, Datadog, Pagerduty-compatible sources, Jira, inbound email, and generic HTTP webhooks, then applies routing templates to direct each alert to the appropriate escalation chain. Escalation chains define notification sequences — notify the primary on-call via Slack, wait 5 minutes, escalate to SMS and phone, wait 10 minutes, page the secondary on-call and notify the engineering manager — continuing until acknowledgment or resolution. On-call schedules support multi-layer rotations with overrides, shift swaps, and timezone-aware handoffs rendered directly inside Grafana dashboards. ChatOps integration publishes alert groups to Slack channels and Telegram groups with interactive buttons for acknowledge, resolve, and silence actions. Template engines based on Jinja2 control alert grouping, appearance rendering, and behavioral automation. The REST API enables programmatic management of integrations, schedules, and escalation policies. Deploy via Docker Compose with PostgreSQL, Redis, and Celery workers alongside your existing Grafana instance. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GNU AGPL v3 licensed.
VictoriaMetrics
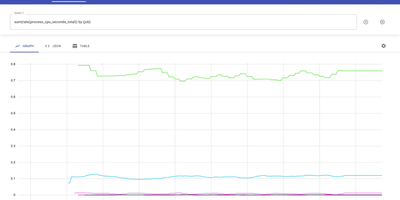
Trusted by thousands of organizations processing billions of time series data points and backed by 17,000+ GitHub stars, VictoriaMetrics delivers a monitoring and time series database that outperforms Prometheus by 16x on query speed while consuming 2.5x less disk space through its optimized compression and storage engine. The architecture supports both single-node deployments handling 10M+ active time series and a horizontally scalable cluster version with vminsert, vmstorage, and vmselect components providing multi-tenancy, replication, and independent namespace isolation. Data ingestion accepts both push protocols including InfluxDB line protocol, Graphite plaintext, OpenTSDB HTTP, CSV, and OpenTelemetry OTLP alongside pull-based Prometheus scraping and remote write, enabling drop-in replacement of existing monitoring stacks without reconfiguring exporters. MetricsQL extends standard PromQL with additional functions, subqueries, and implicit time range alignment while maintaining full backward compatibility with existing Prometheus alerts and Grafana dashboards. The vmalert component processes recording and alerting rules with Alertmanager integration, while vmbackup and vmrestore enable point-in-time snapshots to S3, GCS, and Azure Blob Storage. Stream aggregation operates as a StatsD alternative for pre-aggregating high-cardinality metrics before storage. NFS-compatible storage backends including Amazon EFS and Google Filestore allow shared persistent volumes across cluster nodes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
GoAccess
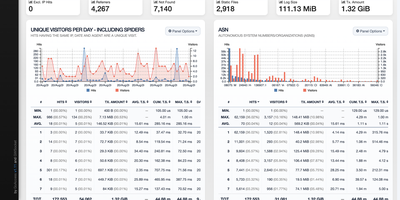
GoAccess processes millions of web log entries in seconds and renders the results as interactive dashboards that update every 200 milliseconds in the terminal or every second via WebSocket-connected HTML reports. Written entirely in C with only ncurses as a dependency, it achieves exceptional performance even on resource-constrained servers, reducing memory usage by approximately 20% and parsing time by 35% in recent releases through optimized in-memory hash tables with on-disk persistence support. The analyzer parses virtually every web log format out of the box (Apache Combined and Common, Nginx, Amazon CloudFront, Amazon S3, AWS Elastic Load Balancing, Google Cloud Storage, Squid, W3C IIS, Caddy JSON, and Traefik) while supporting fully custom log format strings for non-standard configurations. The self-contained HTML dashboard displays 15+ interactive panels covering unique visitors, requested files, static files, 404 errors, referring sites, search keyphrases, geographic location with city-level GeoIP resolution, operating systems, browsers, HTTP status codes, time distribution, and virtual host metrics. WebSocket authentication via JWT provides secure remote access, and incremental log processing ensures data continuity across daemon restarts. Docker deployment requires a single command with volume-mapped access logs. Over 20,800 stars with active development since 2010. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Sourcebot
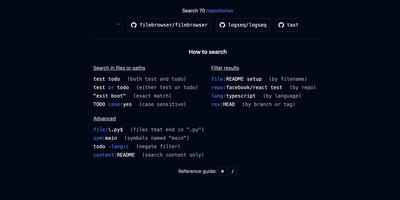
Point Sourcebot at your GitHub, GitLab, Bitbucket, Azure DevOps, Gerrit, or Gitea repositories and get regex, symbol, and filtered search results in under a second across thousands of repos and branches. Backed by Y Combinator with production deployments at NVIDIA, Shutterstock, SeatGeek, Arista, and Red Hat, the Zoekt-powered engine deploys as a single Docker container with zero external data transmission. Ask Sourcebot connects reasoning models like Claude Opus to your entire codebase, enabling natural language questions that return structured answers grounded with inline citations and navigable code snippets, backed by automatic tool calls that search code, follow references, and read files across all indexed repositories. Ask connectors extend this to Jira, Slack, Linear, and Confluence via MCP, pulling external context alongside code for debugging and documentation. IDE-level code navigation provides goto definition and find all references across repository boundaries without local cloning. The built-in file explorer renders any indexed file with syntax highlighting, breadcrumb navigation, and git blame showing per-line commit attribution. An analytics dashboard tracks daily, weekly, and monthly search activity. Permission syncing from GitHub and GitLab enforces access control lists so users only see repositories they are authorized to access. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Other licensed.
Dokku
With over 32,000 GitHub stars and a decade of production use since 2013, Dokku is the original self-hosted Heroku alternative — a Docker-powered PaaS that turns any single Ubuntu server into a full application platform with a simple git push. Deploy applications written in Node.js, Python, Ruby, Go, Java, PHP, Scala, and Clojure using Heroku-compatible buildpacks, Cloud Native Buildpacks via pack-cli, standard Dockerfiles, or pre-built Docker images, with automatic language and framework detection handling the rest. Every deployment runs through zero-downtime checks that health-test new containers before routing traffic via the built-in Nginx reverse proxy, which handles virtual host configuration, WebSocket proxying, and HTTP/2 support automatically. The official plugin ecosystem provides managed datastores including PostgreSQL, MySQL, MariaDB, MongoDB, Redis, RabbitMQ, and Elasticsearch, each provisioned with a single CLI command and linked to apps via environment variables. Automated TLS certificates arrive through the Let's Encrypt plugin with auto-renewal, while persistent storage volumes, cron job scheduling, user ACL management, and process scaling round out the platform capabilities. The entire system is CLI-driven — no web dashboard — keeping resource overhead minimal enough to run multiple applications on a $5/month VPS. Dokku also supports Lambda function builds, custom builder plugins, and app.json-based healthcheck configuration for advanced deployment workflows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
MeterSphere
MeterSphere is the open-source continuous testing platform that brings test management, API testing, and AI-powered automation into a single self-hosted environment. The Spring Boot Java backend handles test execution with the JMeter engine while the Vue.js frontend delivers a responsive interface for managing test cases, plans, defects, and reports across projects. The built-in AI assistant leverages large language models to auto-generate functional test cases and API interface definitions, reducing manual test creation effort. Test management covers the complete lifecycle from writing and reviewing cases in list or mind-map views, through test plan creation with single plans and plan groups, to defect tracking with customizable templates and workflow rules. API testing combines Postman-like ease of use with JMeter-level flexibility, supporting interface debugging with server-side and local execution, API definition with visual request and response editors, interface mocking with configurable headers and body parameters, scenario automation with visual orchestration, and detailed test reports with automatic generation. The system-organization-project hierarchy supports up to 30 users in the community edition with role-based access control, file management, and configurable notification channels. MySQL stores application data, Kafka handles message queuing, MinIO provides S3-compatible object storage, and Redis manages caching. The plugin marketplace extends testing capabilities and enables DevOps pipeline integration. On RepoCloud, deploy MeterSphere on a dedicated VPS with Docker, root SSH access, and complete control over your testing infrastructure, all under the GPLv3 license.
Auto Company
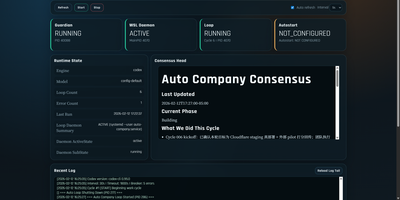
With over 2,700 GitHub stars, Auto Company is the first open-source framework that runs a fully autonomous AI company 24/7 — 14 specialized agents modeled after Jeff Bezos (CEO strategy), Werner Vogels (CTO architecture), Charlie Munger (critical analysis), DHH (full-stack engineering), Kelsey Hightower (DevOps), Seth Godin (marketing), and eight more domain experts collaborate through dynamic squad formation to ideate products, write code, deploy infrastructure, and execute marketing campaigns without human intervention. The five-layer architecture separates execution, orchestration, cognition, workflow routing, and observability, while the consensus memory pattern uses a single markdown file as a relay baton between cycles — no vector databases, no Redis, no embeddings required. A bash loop invokes Claude Code or OpenAI Codex CLI every 30 seconds, each cycle selecting 2-5 agents from the 14-person pool based on task context. Over 30 reusable skills handle specialized tasks from frontend design to competitive analysis and deployment automation. Circuit breakers trigger cooldown after consecutive errors, rate-limit detection auto-sleeps on API throttling, and sandbox rollback protects against destructive changes. The Python-powered web dashboard displays real-time cycle status, cost tracking per cycle averaging under $2, and agent activity visualization, with CLI control via make start, stop, monitor, pause, and resume. Supports macOS via launchd, Windows via WSL with systemd, and native Linux deployment. The npx create-auto-co command scaffolds a new AI company in seconds. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Pulse
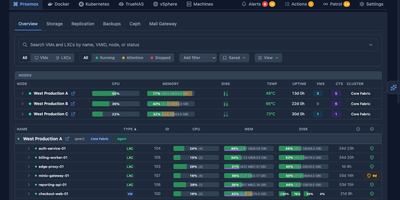
Pulse monitors your entire heterogeneous infrastructure from one screen: Proxmox VE, Proxmox Backup Server, Proxmox Mail Gateway, Docker, Podman, Docker Swarm, Kubernetes, TrueNAS SCALE/CORE, VMware vSphere, and standalone Linux/Windows/macOS machines. The Go binary embeds a SolidJS/TypeScript frontend, delivering WebSocket-driven dashboards with sub-second metric updates on port 7655. A unified agent auto-detects Docker, Podman, Kubernetes, and Proxmox on each host without manual configuration and self-updates silently, while Proxmox nodes need only API credentials with zero agent installation. Smart alerts use adaptive hysteresis-based thresholds to prevent notification floods, pushing to Discord, Slack, Telegram, Teams, email, ntfy.sh, Gotify, and generic webhooks with per-resource overrides. The standout feature is Pulse Patrol: scheduled AI health checks running every ten minutes to seven days using OpenAI, Anthropic, Gemini, or local Ollama models. Patrol catches silent backup failures, capacity creep, restart loops, unhealthy containers, and clock drift that dashboards miss when nobody is watching. Platform-specific views render Proxmox nodes, Ceph clusters, Docker Compose projects, Kubernetes workloads, TrueNAS pools, and vSphere VMs in familiar layouts. OIDC, SSO, and SAML authentication with credential encryption at rest secures access. 6,500+ stars and 441 releases since February 2025. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Kite
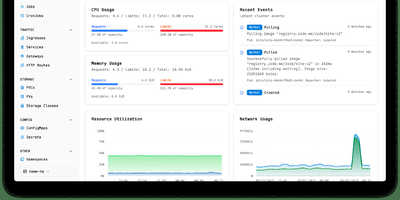
With nearly 3,000 GitHub stars and 14 releases since its June 2025 launch, Kite delivers a lightweight Kubernetes dashboard that replaces the fragmented workflow of switching between kubectl, Lens, and separate monitoring tools with a unified multi-cluster management platform. The dashboard automatically discovers clusters from kubeconfig files and supports independent Prometheus configurations per cluster, providing real-time CPU, memory, and network charts alongside live pod log streaming with filtering and search. A built-in web terminal opens shells directly into pods and nodes without kubectl port-forward, while the Monaco-based YAML editor offers syntax highlighting and validation for in-place resource editing. The integrated AI agent, powered by OpenAI or Anthropic models via native Go SDK integrations, translates natural language into precise client-go API calls — querying cluster health, analyzing pod logs, scaling deployments, patching resources, and cleaning up failed jobs — all operating strictly within the logged-in user's RBAC permissions. Enterprise governance includes OAuth 2.0 single sign-on, multi-factor authentication, FIDO2 passkeys, granular role-based access control with per-namespace permissions, and comprehensive audit logging. Helm chart management enables browsing, installing, and upgrading releases directly from the UI, while the Docker registry integration provides quick image tag selection. Deploy via a single Docker container with SQLite or use the official OCI Helm chart with PostgreSQL or MySQL for production. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Agent Gateway
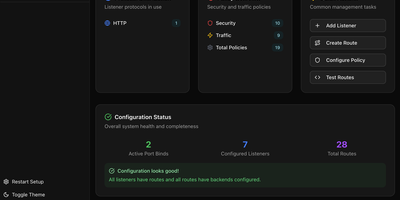
Backed by the Linux Foundation with contributions from AWS, Cisco, IBM, Microsoft, Red Hat, and Shell, Agentgateway is the first data plane built from the ground up for AI agent workloads — providing a unified Rust-based proxy that handles conventional HTTP and gRPC traffic alongside MCP tool servers, A2A agent communication, and LLM inference endpoints through a single deployment. The LLM gateway routes requests to OpenAI, Anthropic, Gemini, AWS Bedrock, and other providers through an OpenAI-compatible unified API with per-tenant budget controls, spend tracking, prompt enrichment, load balancing across multiple model endpoints, and automatic failover when providers experience outages. The MCP gateway federates multiple tool servers behind one endpoint, supporting stdio, HTTP/SSE, and Streamable HTTP transports with built-in OAuth authentication compliant with the MCP auth specification, integrating Auth0 and Keycloak out of the box. OpenAPI integration exposes existing REST APIs as MCP-native tools without code changes, enabling legacy services to participate in agent workflows. Policy-based RBAC controls which agents access which tools, while OpenTelemetry integration provides distributed tracing across agent communication chains. Deploy as a standalone binary with flat YAML configuration or on Kubernetes using the built-in controller with Gateway API support for declarative infrastructure-as-code management. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Dockge
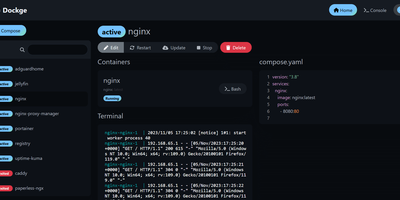
Created by the developer behind Uptime Kuma and carrying over 23,000 GitHub stars, Dockge brings the same clean, reactive design philosophy to Docker Compose stack management with a web interface that makes Portainer's compose handling feel like editing YAML in a terminal over SSH. The interactive editor provides syntax highlighting, inline validation, and a live preview of your compose.yaml files while keeping every stack stored as a standard file on disk in /opt/stacks by default, meaning you can seamlessly switch between the web UI and the docker compose CLI without lock-in or proprietary database formats. Real-time WebSocket updates stream pull progress, container start/stop transitions, and build output directly to the browser with no polling delays. The built-in web terminal opens a shell session inside any running container for quick debugging, while the docker-run-to-compose converter transforms single-container run commands into proper compose.yaml definitions with one click. Multi-agent support introduced in version 1.4.0 connects multiple Docker hosts to a single Dockge dashboard, enabling centralized management of stacks distributed across different servers. Image update detection shows which stacks have newer versions available, and one-click updates pull the latest images and recreate containers without manual intervention. The stack is a single Docker container running on Node.js with Socket.IO for reactivity and stores no external database. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Unkey
Unkey is the open-source platform that unifies API key management, rate limiting, deployment, and observability into a single control plane. The Go API service validates keys with sub-millisecond latency using regional Redis caches and MySQL 8.0 persistent storage, while ClickHouse captures every verification event for per-key and per-keyspace analytics with filterable time-series charts, request counters, and active key tracking. Keyspaces organize API keys by product, environment, or tier, each configurable with custom prefixes, byte lengths, IP whitelists, encrypted key recovery, and delete protection. Per-key settings include expiration dates, rate limit quotas with configurable windows, RBAC roles and permissions, owner identities linking multiple keys to a single user or organization, and key rotation with grace periods from immediate revocation through 24-hour overlap. The deployment pipeline connects GitHub repositories for automatic Docker container builds, generates preview environments per commit, promotes tested versions to production, and validates releases with OpenAPI diff detection flagging breaking changes before production. The edge gateway authenticates and rate-limits requests at the closest region before routing to the nearest API instance. Immutable audit logs track every key creation, verification, deletion, and configuration change with actor, timestamp, and event metadata. The CLI provides terminal access to key management, analytics queries, and deployment operations. On RepoCloud, deploy Unkey on a dedicated VPS with Docker, root SSH access, and complete control over your API infrastructure, all under the AGPL license.
NetsGo
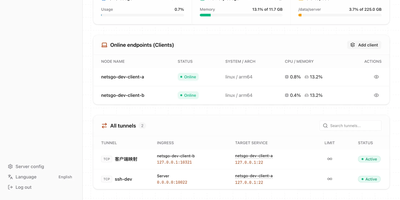
Created to eliminate the configuration fragmentation plaguing multi-device Homelab setups and small-team infrastructures, NetsGo merges what typically requires three separate tools — a tunnel daemon, a management panel, and a monitoring stack — into a single Go binary that starts with one command and listens on one port. The server exposes HTTP, TCP, and UDP tunnels, a built-in Web console for node management, a REST API for automation, and real-time traffic statistics with per-client bandwidth limiting, all sharing default port 9527 so firewalls and reverse proxies need only a single rule. Version 0.1.11 introduced Client-to-Client P2P tunnels via WebRTC DataChannel with three selectable transport strategies — Server relay, Prefer P2P with automatic fallback, and P2P only — reducing latency for direct connections while maintaining the centralized control plane. The management console displays every connected client's online status, authentication tokens, tunnel configuration, active transport mode, P2P candidate gathering progress, and cumulative byte-level traffic counters updated every second. Unlike frp or rathole which delegate management to external plugins or configuration files, NetsGo provides built-in client key generation, tunnel target migration between nodes, SOCKS5 proxying, IP-whitelist console access, and one-command server upgrades. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.