Rancher
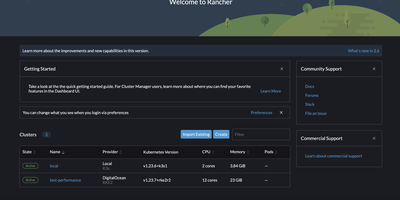
Used by over 30,000 teams and 650+ enterprise customers managing more than 5.2 million containers, Rancher has earned recognition as a Leader in the Gartner Magic Quadrant for Container Management and the Forrester Wave for Multicloud Container Platforms. The platform provides a single pane of glass for provisioning, upgrading, and securing Kubernetes clusters across Amazon EKS, Google GKE, Microsoft AKS, RKE2, K3s, and any CNCF-conformant distribution. Multi-Cluster Management enables centralized authentication via Active Directory, LDAP, SAML, GitHub, and OpenID Connect with granular role-based access control at the cluster, project, and namespace levels. Fleet, the built-in GitOps engine, delivers continuous deployment across hundreds of clusters simultaneously using Helm charts, Kustomize, or raw YAML manifests from any Git repository. The integrated app catalog provides one-click deployment of Prometheus monitoring, Grafana dashboards, Longhorn persistent storage, Istio service mesh, and hundreds of community Helm charts. Rancher supports air-gapped installations for disconnected environments, CIS benchmark scanning for security compliance, and automated backup and restoration of cluster configurations. The dashboard offers real-time workload monitoring, log aggregation, pod shell access, and namespace-scoped resource quotas. Cluster templates enforce organizational standards through Helm-based provisioning policies that ensure consistent configurations across environments. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Kestra
With over 27,000 GitHub stars and an ecosystem of 1,900+ plugins covering every major cloud provider, database, and SaaS platform, Kestra is the orchestration engine that brings Infrastructure as Code principles to workflow automation — defining complex multi-step pipelines in readable YAML that execute across any language, runtime, or infrastructure boundary. The built-in VS Code-style editor provides syntax highlighting, auto-completion, real-time validation, and an AI Copilot that generates workflow YAML from natural language descriptions. Tasks execute in Python, Node.js, Go, R, Shell, SQL, or any Docker container, with event-driven triggers listening for file arrivals on SFTP and cloud storage, messages from Kafka, Redis, Pulsar, AMQP, MQTT, NATS, AWS SQS, Google Pub/Sub, and Azure Event Hubs in real time. The topology view visualizes workflow DAGs with execution state, duration, and output artifacts for each task node. Namespaces organize workflows into isolated environments with configurable secrets, while subflows enable modular composition with inputs, outputs, and conditional branching. Retry policies, timeouts, error handlers, and automatic backfills for missed schedules ensure reliability across production workloads. Git integration pushes workflows directly to branches from the UI with CI/CD pipeline support for automated deployment. The REST API enables programmatic workflow management, execution triggering, and resource provisioning. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
MeshCentral
With over 7,000 GitHub stars and continuous development since 2017 by former Intel engineer Ylian Saint-Hilaire, MeshCentral has become the go-to self-hosted alternative to ConnectWise Control and Splashtop for managing devices remotely without per-seat licensing fees. The Node.js server installs via a single npm command and manages Windows, macOS, Linux, and FreeBSD endpoints through lightweight agents that maintain persistent WebSocket connections for real-time remote desktop, terminal access, and file transfer directly in the browser. Intel AMT integration provides out-of-band hardware management including power control and BIOS access even when the operating system is unresponsive. Device groups organize endpoints by location, customer, or function with granular role-based access control for multi-technician environments. Session recording captures remote desktop interactions for compliance auditing, while Wake-on-LAN powers on machines remotely across subnets. The server supports MongoDB for production deployments handling thousands of agents or the embedded NeDB for smaller setups under 200 devices, with a single 8GB VPS comfortably managing 1,500 concurrent agents. Security features include mandatory TLS with automatic Let's Encrypt certificate provisioning, multi-factor authentication via TOTP and FIDO2, SAML-based single sign-on, IP filtering, and HashiCorp Vault integration for secrets management. The web console provides real-time device monitoring with hardware and software inventory, network topology visualization, and customizable branding. TacticalRMM uses MeshCentral as its remote access layer. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Gotify
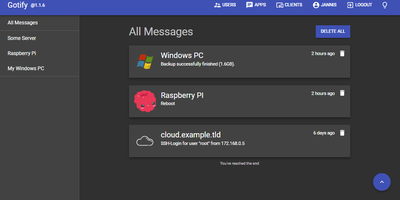
Real-time alerts from your own infrastructure to your phone, with no Firebase, Pushover, or third-party push service in the path: Gotify is a simple, self-hosted notification server written in Go. The model is deliberately minimal: senders push messages with a single HTTP POST to the REST API, receivers subscribe over a WebSocket stream, and a clean React web UI manages the pieces. Senders are namespaced as "applications," each with its own token, so your backup script, Uptime Kuma, CI pipeline, and cron jobs each get an identity, an icon, and independently revocable credentials - centralized alerting from many services with per-source management. Messages carry a title, body, and priority level that maps to notification importance on the client. The official Android app (on both F-Droid and Google Play, notable for working entirely without Google Play Services) shows push notifications for new messages; the web UI itself supports Web Push in the browser; and gotify/cli pushes messages from shell scripts with one command. A server-side plugin system adds custom behavior, and the whole thing runs as a single small binary with SQLite by default - near-zero resource footprint. Because dozens of tools (and Apprise) speak Gotify natively, it slots in as the notification hub for an entire homelab or ops stack.
Vaultwarden
The Bitwarden server, reimplemented in Rust: Vaultwarden (formerly bitwarden_rs) is the unofficial lightweight edition. It speaks the same wire protocol as the official server, so every official Bitwarden client - browser extensions, iOS, Android, desktop, and the bw CLI - connects without modification, while the server itself runs as a single container against SQLite (or MySQL/MariaDB/PostgreSQL) instead of the official multi-container stack that wants gigabytes of RAM. Features Bitwarden gates behind paid tiers ship free: organizations with collections, groups, member roles, and policies; TOTP code storage; file attachments; Bitwarden Send; Emergency Access; event logs; and admin password reset. Two-factor options cover authenticator apps, email, FIDO2 WebAuthn, YubiKey, and Duo, and OIDC-based SSO landed natively in v1.35.0. Zero-knowledge encryption is unchanged - vault data is encrypted client-side and the master password never reaches the server. Attachments and Sends store on local disk or S3-compatible backends, an admin panel manages users and server settings, and backup is copying one data directory. Suited to individuals and teams up to roughly 50 users.
xyOps
With 4,500+ GitHub stars and version 1.0.92 released August 2026, xyOps delivers a complete operations platform that unifies workflow automation, job scheduling, server monitoring, alerting, and incident response in one self-hosted system. The platform uses a distributed architecture where a central conductor coordinates lightweight xySat satellite agents running on Linux, macOS, or Windows worker nodes via persistent WebSocket connections. The visual workflow builder lets you chain events, triggers, actions, and monitors into multi-step pipelines with conditional logic, fan-out/fan-in parallelism, multiplex controllers for fleet-wide execution, and configurable resource limits. QuickMon provides per-second CPU, memory, disk, and network visibility streamed live to the web UI, while user-defined monitor plugins sample metrics every minute with time-series storage at hourly, daily, monthly, and yearly resolutions. Alert triggers evaluate expressions against live data and fire notifications via email, webhook, or custom actions, with full server snapshots attached showing every running process, network connection, and resource utilization at the moment of detection. Failed jobs and alerts automatically create tickets with linked logs, metrics history, and context for end-to-end incident tracking. The plugin marketplace supports extensions written in any language, and the Docker plugin enables container-based job execution. Deploy via Docker with persistent volumes on port 5522 for the web UI and 5523 for API access, running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD-3-Clause licensed.
Databasus
With over 7,500 GitHub stars and 1 million Docker pulls — making it the most popular open-source database backup tool on GitHub ahead of pgBackRest and WAL-G — Databasus delivers production-grade backup management through a designer-polished web interface that replaces complex configuration files and CLI-only workflows. The platform supports PostgreSQL 14-18, MySQL 5.7-8, MariaDB 10-12, and MongoDB 4.2-8 with logical backups via pg_dump and mysqldump, while PostgreSQL 17+ enables physical backups using the native pg_basebackup engine with block-level incremental support via pg_basebackup --incremental and continuous WAL streaming via pg_receivewal for Point-in-Time Recovery to any second between backups. Storage destinations include local disk, AWS S3, CloudFlare R2, Google Drive, Azure Blob Storage, SFTP, NAS, and rclone-backed targets, while built-in AES-256-GCM encryption secures both backup files and stored credentials. Restore verification runs automated recovery into throwaway Docker containers, validating backups by comparing schema counts, table structure, and row counts against the source database — proving recoverability rather than merely checking checksums. The notification system integrates with Slack, Discord, Telegram, email, and webhooks for real-time backup status alerts. Deployment options span a single Docker container, Docker Compose with Caddy for automatic HTTPS, Helm charts for Kubernetes clusters, or a one-line install script. SSH tunnel support reaches databases in closed networks through bastion hosts without public exposure. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
OpenStatus
Trusted by Cal.com, WhiteBIT, and Documenso and backed by 8,800+ GitHub stars, OpenStatus delivers the open-source status page and uptime monitoring platform that replaces Atlassian Statuspage, Better Stack, and Instatus with a single self-hosted deployment. The monitoring engine runs Go-based probes across 28 global regions on three cloud providers checking HTTP, TCP, and DNS endpoints in parallel with configurable intervals and multi-region consensus to eliminate false-positive alerts. Status pages ship with custom domain support, password and email-domain access controls, maintenance windows, grouped monitor components, and subscriber notifications via email and RSS. Incident management provides structured status reports with investigating, identified, monitoring, and resolved timeline phases that publish automatically to affected status pages. The monitoring-as-code workflow supports YAML configuration synced through the CLI, a GitHub Actions integration for CI/CD pipelines, and a Terraform provider for infrastructure-as-code deployments. The typed ConnectRPC JSON-over-HTTP API exposes a published OpenAPI specification with a Node SDK for programmatic access, while an MCP server connects AI assistants like Claude, ChatGPT, and Cursor directly to workspace data. The tech stack combines Next.js with shadcn/ui for the dashboard, Hono for the API server, Drizzle ORM over Turso for application data, and Tinybird for analytics. Private monitoring locations deploy as a single 8.5MB Docker image behind firewalls to check internal services. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Dagu
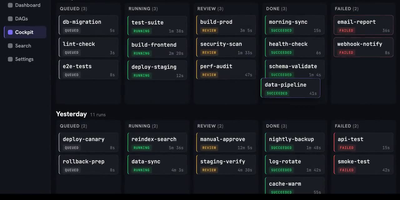
With over 3,700 GitHub stars and growing adoption among teams tired of managing complex orchestration platforms, Dagu delivers a complete workflow engine as a single Go binary that requires no external database, message broker, or framework installation. Define directed acyclic graphs in declarative YAML — specifying dependencies, schedules, retries, timeouts, approvals, and notifications — while keeping existing shell scripts, containers, and tools completely unchanged. The built-in Web UI provides live pipeline visualization, per-step log streaming, run history browsing, artifact previewing, manual retry controls, and workflow YAML editing without SSHing into servers. Execute steps as shell commands, Docker containers, Kubernetes Jobs, SSH remote commands, SQL queries, or HTTP requests, with conditional branching and parallel execution handled natively. The integrated Model Context Protocol server exposes dagu_read, dagu_change, and dagu_execute tools, enabling AI agents like Claude, Codex, and Cursor to inspect workflow state, preview YAML modifications, and control runs through authenticated endpoints. The harness.run executor lets external coding-agent CLIs operate inside DAG steps with full scheduling and approval gate support. Scale beyond a single machine with the distributed worker mode, which dispatches tasks to remote nodes via gRPC with automatic label-based routing and worker selection. Deploy with Docker, the official Helm chart for Kubernetes, or a simple binary download requiring only a Linux, macOS, or Windows host. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPLv3 licensed.
Healthchecks
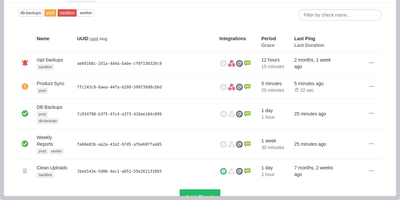
With 10,100+ GitHub stars and 75 releases over a decade of continuous development, Healthchecks is the open-source cron job monitoring service that catches failures your other monitoring tools miss — the jobs that silently stop running, the backups that never completed, the nightly reports that disappeared without error. The dead man's switch architecture requires zero agent installation: your cron jobs, scripts, and services ping a unique URL via HTTP request or email, and Healthchecks alerts you only when a ping does not arrive within the configured Period and Grace Time window. Each check supports cron expression scheduling, optional start, success, and failure signals for measuring execution time, and HTTP body keyword filtering for intelligent alert routing. Twenty-five notification integrations cover every channel teams actually use: Slack, Discord, Microsoft Teams, PagerDuty, Opsgenie, Splunk On-Call, Telegram, Signal, WhatsApp, SMS, email, webhooks, GitHub Issues, Pushover, ntfy, Gotify, Matrix, Mattermost, Zulip, Pushbullet, PagerTree, Spike.sh, and Trello. The web dashboard provides a visual grid showing real-time status with color-coded badges and per-check integration toggles. Monthly, weekly, and daily email reports summarize uptime trends with checks sorted by downtime duration. Team management supports projects with member roles and read-only access. Prometheus metrics expose check health and grace state for Grafana dashboards. WebAuthn and TOTP two-factor authentication secure accounts. Deploy via Docker images available for amd64, arm/v7, and arm64 architectures. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD 3-Clause licensed.
Gitea
With over 57,000 GitHub stars and deployment across thousands of organizations worldwide, Gitea is the most popular self-hosted Git service, delivering a complete software development platform in a single Go binary that runs on as little as 512MB of RAM. The platform provides full repository management with pull requests featuring inline code review, branch protection rules, merge strategies including squash, rebase, and merge commit, and automated status checks through Gitea Actions. The built-in CI/CD system uses the same YAML workflow syntax as GitHub Actions and can directly reuse over 20,000 existing Actions plugins, allowing teams to migrate from GitHub with minimal pipeline rewrites using the open-source act_runner executor. The integrated package registry supports over 20 formats including npm, PyPI, Maven, NuGet, Cargo, Helm, Composer, Conda, RubyGems, Pub, and an OCI-compatible Container registry for Docker images with no additional configuration required. Project management features include issue tracking with labels, milestones, dependencies, and time tracking, alongside kanban project boards for visual workflow management. Gitea supports LFS for large file storage, built-in wiki pages per repository, webhook integrations with Slack, Discord, Telegram, Microsoft Teams, and custom HTTP endpoints, and OAuth2 authentication with LDAP, SAML, and PAM backend support. Repository mirroring enables bidirectional synchronization with GitHub, GitLab, and Bitbucket, while the comprehensive REST and GraphQL APIs power external integrations and the official tea CLI tool. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Kubero
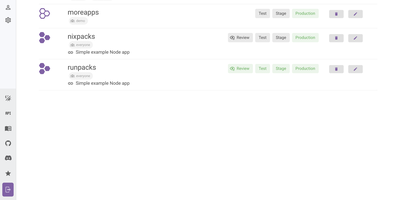
With over 4,300 GitHub stars and a v3 release adding built-in user management, team views, and multi-language support, Kubero has established itself as the most feature-complete open-source Heroku alternative running natively on Kubernetes. The platform operates as a Kubernetes operator with two containers — kubero-ui and the operator — storing all state in etcd without an external database. Developers push code via Git integration with GitHub, GitLab, Bitea, or Gitea, and Kubero automatically builds using Buildpacks, Nixpacks, Runpacks, or Dockerfiles, then deploys to the configured domain with SSL via cert-manager. CI/CD pipelines support up to four staging environments — review, test, staging, and production — with per-stage environment variable isolation and ephemeral review apps that spin up on pull request open and tear down on close. The template catalog includes over 170 pre-configured applications like WordPress, Grafana, and PostgreSQL deployable in one click, while managed add-ons provide highly available PostgreSQL, Redis, MySQL, Kafka, CouchDB, Elasticsearch, and MongoDB alongside your applications. Security features include Trivy vulnerability scanning, GitHub and OAuth2 single sign-on, basic auth, and a role-based permission system with API tokens. The NestJS backend with Vue.js and Vuetify frontend provides application metrics, real-time logs, a built-in web console for container access, scheduled cronjob management, and deployment notifications via Discord, Slack, or webhooks. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
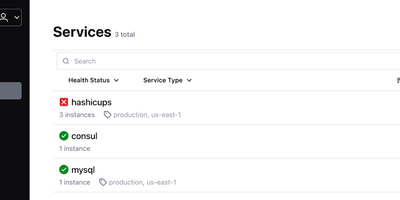
HashiCorp Consul
With nearly 30,000 GitHub stars and deployment across organizations including Criteo, Pandora, and Barclays, HashiCorp Consul is the industry-standard platform for service discovery, service mesh, and distributed configuration across dynamic multi-cloud and multi-datacenter infrastructure. Services register themselves and become discoverable via a built-in DNS interface on port 8600 or an HTTP API on port 8500, with health checks ensuring only healthy instances receive traffic through automatic catalog deregistration and service-level circuit breaking. The service mesh capabilities use Envoy sidecar proxies with Transparent Proxy mode to establish automatic mTLS encryption for all service-to-service communication, while identity-based intentions define fine-grained authorization rules controlling which services can communicate. The integrated API Gateway manages north-south traffic into the mesh with configurable routing rules, TLS termination, and header-based matching policies. Consul's distributed key-value store provides hierarchical configuration storage accessible via CLI, HTTP API, and the built-in web UI, with blocking queries enabling watch-based configuration updates without polling. Multi-datacenter federation connects Consul clusters across regions through WAN gossip and RPC forwarding, enabling cross-datacenter service discovery and failover with configurable prepared queries. The Raft consensus protocol provides strong consistency for the service catalog and KV store, with anti-entropy mechanisms ensuring agent state converges with the server catalog. Consul integrates natively with Kubernetes via Helm charts with automatic sidecar injection, Nomad for workload orchestration, Vault for secrets management, and Terraform for infrastructure provisioning. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BUSL 1.1 licensed.
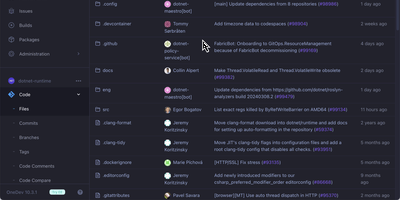
OneDev
With over 15,100 GitHub stars and seven years of battle-tested production use, OneDev replaces entire DevOps toolchains — GitLab, Jenkins, Jira, Artifactory — with a single Java application that runs comfortably on a 1-core 2GB server for medium-sized projects. The platform unifies Git hosting with ANTLR-powered language-aware code search and symbol navigation, pull request workflows with configurable branch protection rules and required reviewers, and customizable issue tracking with scripted state transitions that automatically advance issues when code is committed, builds pass, or deployments complete. The GUI-based CI/CD editor creates pipelines without writing YAML, supporting typed parameters, matrix builds, job templates, cache management, and artifact publishing in a single visual interface. Jobs execute via Docker containers, bare metal shell, Kubernetes pods, or distributed agent pools, with web terminal access for live debugging and the ability to pause running jobs for inspection. Built-in package registries handle Docker images, npm packages, Maven artifacts, NuGet libraries, PyPI wheels, and RubyGems without external infrastructure. AI users can be assigned to issues and pull requests to autonomously implement features, review code, fix CI/CD failures, and resolve merge conflicts. The automated Kanban board supports rule-based card movement, time tracking, timesheets, and service desk ticket creation via email. Cluster deployment enables project replication across servers for high availability and horizontal distribution for scalability. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Cockpit
Cockpit puts Linux server administration in a web browser, rendering storage, networking, containers, and virtual machines as visual panels you click through instead of command-line syntax you memorize. It ships in every major Linux distribution and activates through systemd socket activation, consuming zero resources until someone connects on port 9090. What makes it different from other admin panels: every change through the web interface appears instantly at the command line, and every terminal change reflects in the browser in real time. No abstraction layer sits between the UI and the operating system, which means no configuration drift. Storage management covers disk partitioning, RAID arrays, LUKS encryption, LVM volumes, and NFS shares. Network configuration handles bonds, bridges, VLANs, and firewall zones through visual editors. Native Podman integration pulls images, creates containers, manages pods, and provides terminal access into running processes. KVM/libvirt support handles VM creation, cloning, snapshots, and live migration with console access. A built-in terminal provides shell access when the web interface is not enough, and the journal viewer filters systemd logs by severity and unit. Multi-server management connects additional hosts over SSH, presenting a unified dashboard across your entire infrastructure from one browser tab. Runs on a dedicated RepoCloud VPS with full root SSH access and browser serial console. LGPL licensed.
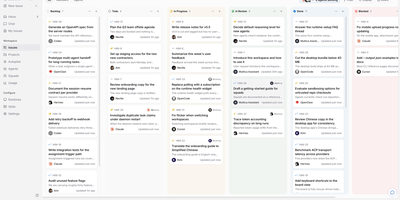
Multica
Reaching 45,000 GitHub stars within seven months of launch, Multica is the fastest-growing open-source platform for managing AI coding agents as first-class teammates — assign an issue to Claude Code, Codex, Cursor, Copilot, Kimi, or any of 21 supported agent CLIs and it picks up the work, comments progress in real time via WebSocket, raises blockers, and hands the result back for human review before anything merges. The Go backend (Chi router, sqlc-generated type-safe queries, gorilla/websocket) connects to PostgreSQL 17 with pgvector for semantic search across workspace history, while the Next.js 16 App Router frontend delivers workspace dashboards showing per-agent token spend, execution time, daily cost charts, and runtime status across unlimited connected machines. Agent Skills provide reusable methods, reference material, and supporting files that compound across runs — a persistent knowledge layer that makes each subsequent task faster and more accurate. Squads let a leader agent select the right specialist for subtasks, creating multi-agent workflows without manual orchestration. Review gates ensure no AI-generated code ships to main without explicit human approval. Self-host via Docker Compose or Kubernetes with full Git integration across GitHub, GitLab, Gitea, and Forgejo including self-hosted instances. The CLI and REST API make every surface scriptable, and Autopilot automations trigger agent runs from events. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed with additional conditions.
Mira
The fastest tool on the public Martian Code Review Bench at 77 seconds per PR with competitive F1 scores — while every higher-scoring competitor takes 5 to 14 times longer — Mira is the fully open-source AI code reviewer that ships the entire feature surface other tools gate behind per-seat subscriptions: indexed PR reviews with full-repo context, streaming walkthroughs posted within seconds, inline vulnerability scanning from hourly OSV.dev polls, org-wide package inventory answering "which repos use [email protected]?" in one query, interactive dependency graphs with blast-radius SVG rendering via ReactFlow, a learning loop that synthesizes rules from rejected comments and human review patterns on merged PRs, and cost telemetry showing actual spend per repo and per model. Unlike CodeRabbit, Greptile, and GitHub Copilot code review which are SaaS-only with per-seat pricing, Mira runs as a single Docker image on your infrastructure with your LLM key through OpenRouter (fronting Anthropic, OpenAI, Google Gemini, DeepSeek) or direct to Ollama and vLLM for fully air-gapped deployments. The engine indexes Python, TypeScript, Go, Rust, Java, C/C++, C#, Swift, Kotlin, Scala, and PHP with per-file symbol extraction, enabling multi-file reasoning across diffs rather than isolated line-by-line review. Integrates with GitHub, GitLab, and Forgejo via webhook with full feature parity. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
ZTNET
ZTNET provides a polished web dashboard for running your own ZeroTier network controller, covering network creation, member authorization, IP assignment, flow rule editing, and real-time node monitoring entirely from the browser. The organization system supports multi-tenant deployments where teams manage separate network pools with role-based permissions and customizable email notification templates for events like member joins, departures, IP changes, and authorization updates. Each network view displays connected members with their ZeroTier addresses, assigned IPs, last-seen timestamps, physical endpoints, and protocol versions in a clean tabular layout. The admin panel provides platform-wide user management, SMTP configuration for transactional emails, and system-level settings. Built on the T3 stack with Next.js, Prisma ORM, tRPC, TypeScript, and Tailwind CSS with DaisyUI components, the application supports both PostgreSQL and SQLite for persistence and communicates directly with the ZeroTier controller daemon through its native API. Dark and light themes adapt to user preference, and responsive layouts make network management practical from any device. Docker Compose bundles the web application alongside the ZeroTier controller service. Over 100,000 Docker pulls confirm steady community adoption. GPL-3.0 licensed.