MongoDB
Used by over 46,800 companies including Forbes, Toyota, and Cisco, MongoDB stores data as flexible JSON-like BSON documents that eliminate rigid table schemas and support rapid application iteration. Its aggregation pipeline processes complex data transformations through composable stages including $match, $group, $lookup for joins, $unwind, and $project, operating directly within the database engine. Horizontal scaling is built in through automatic sharding, which distributes data across nodes using range-based, hashed, or zone-based shard keys, while replica sets provide automatic failover with configurable read preferences and write concerns. Multi-document ACID transactions span multiple collections and shards since version 4.0, enabling relational-style consistency guarantees within a document model. Starting with Community Edition 8.2, native full-text search and vector search are available directly in the database through $search and $vectorSearch aggregation stages, supporting RAG patterns, semantic retrieval, and hybrid search without external dependencies. Change streams provide real-time event-driven data access by tailing the oplog through the aggregation framework, enabling reactive architectures without polling. Time series collections offer optimized columnar storage for IoT sensor data and metrics with automatic bucketing and compression. Official drivers exist for Python, Node.js, Java, Go, C#, C++, Rust, Swift, and PHP, with MongoDB Compass providing a GUI for visual schema exploration and query building. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. SSPL v1 licensed.
Pulse
Pulse monitors your entire heterogeneous infrastructure from one screen: Proxmox VE, Proxmox Backup Server, Proxmox Mail Gateway, Docker, Podman, Docker Swarm, Kubernetes, TrueNAS SCALE/CORE, VMware vSphere, and standalone Linux/Windows/macOS machines. The Go binary embeds a SolidJS/TypeScript frontend, delivering WebSocket-driven dashboards with sub-second metric updates on port 7655. A unified agent auto-detects Docker, Podman, Kubernetes, and Proxmox on each host without manual configuration and self-updates silently, while Proxmox nodes need only API credentials with zero agent installation. Smart alerts use adaptive hysteresis-based thresholds to prevent notification floods, pushing to Discord, Slack, Telegram, Teams, email, ntfy.sh, Gotify, and generic webhooks with per-resource overrides. The standout feature is Pulse Patrol: scheduled AI health checks running every ten minutes to seven days using OpenAI, Anthropic, Gemini, or local Ollama models. Patrol catches silent backup failures, capacity creep, restart loops, unhealthy containers, and clock drift that dashboards miss when nobody is watching. Platform-specific views render Proxmox nodes, Ceph clusters, Docker Compose projects, Kubernetes workloads, TrueNAS pools, and vSphere VMs in familiar layouts. OIDC, SSO, and SAML authentication with credential encryption at rest secures access. 6,500+ stars and 441 releases since February 2025. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Kite
With nearly 3,000 GitHub stars and 14 releases since its June 2025 launch, Kite delivers a lightweight Kubernetes dashboard that replaces the fragmented workflow of switching between kubectl, Lens, and separate monitoring tools with a unified multi-cluster management platform. The dashboard automatically discovers clusters from kubeconfig files and supports independent Prometheus configurations per cluster, providing real-time CPU, memory, and network charts alongside live pod log streaming with filtering and search. A built-in web terminal opens shells directly into pods and nodes without kubectl port-forward, while the Monaco-based YAML editor offers syntax highlighting and validation for in-place resource editing. The integrated AI agent, powered by OpenAI or Anthropic models via native Go SDK integrations, translates natural language into precise client-go API calls — querying cluster health, analyzing pod logs, scaling deployments, patching resources, and cleaning up failed jobs — all operating strictly within the logged-in user's RBAC permissions. Enterprise governance includes OAuth 2.0 single sign-on, multi-factor authentication, FIDO2 passkeys, granular role-based access control with per-namespace permissions, and comprehensive audit logging. Helm chart management enables browsing, installing, and upgrading releases directly from the UI, while the Docker registry integration provides quick image tag selection. Deploy via a single Docker container with SQLite or use the official OCI Helm chart with PostgreSQL or MySQL for production. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Agent Gateway
Backed by the Linux Foundation with contributions from AWS, Cisco, IBM, Microsoft, Red Hat, and Shell, Agentgateway is the first data plane built from the ground up for AI agent workloads — providing a unified Rust-based proxy that handles conventional HTTP and gRPC traffic alongside MCP tool servers, A2A agent communication, and LLM inference endpoints through a single deployment. The LLM gateway routes requests to OpenAI, Anthropic, Gemini, AWS Bedrock, and other providers through an OpenAI-compatible unified API with per-tenant budget controls, spend tracking, prompt enrichment, load balancing across multiple model endpoints, and automatic failover when providers experience outages. The MCP gateway federates multiple tool servers behind one endpoint, supporting stdio, HTTP/SSE, and Streamable HTTP transports with built-in OAuth authentication compliant with the MCP auth specification, integrating Auth0 and Keycloak out of the box. OpenAPI integration exposes existing REST APIs as MCP-native tools without code changes, enabling legacy services to participate in agent workflows. Policy-based RBAC controls which agents access which tools, while OpenTelemetry integration provides distributed tracing across agent communication chains. Deploy as a standalone binary with flat YAML configuration or on Kubernetes using the built-in controller with Gateway API support for declarative infrastructure-as-code management. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Dockge
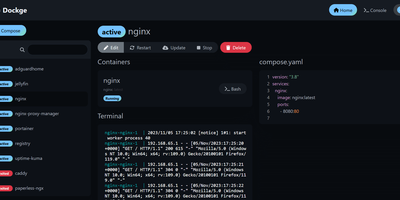
Created by the developer behind Uptime Kuma and carrying over 23,000 GitHub stars, Dockge brings the same clean, reactive design philosophy to Docker Compose stack management with a web interface that makes Portainer's compose handling feel like editing YAML in a terminal over SSH. The interactive editor provides syntax highlighting, inline validation, and a live preview of your compose.yaml files while keeping every stack stored as a standard file on disk in /opt/stacks by default, meaning you can seamlessly switch between the web UI and the docker compose CLI without lock-in or proprietary database formats. Real-time WebSocket updates stream pull progress, container start/stop transitions, and build output directly to the browser with no polling delays. The built-in web terminal opens a shell session inside any running container for quick debugging, while the docker-run-to-compose converter transforms single-container run commands into proper compose.yaml definitions with one click. Multi-agent support introduced in version 1.4.0 connects multiple Docker hosts to a single Dockge dashboard, enabling centralized management of stacks distributed across different servers. Image update detection shows which stacks have newer versions available, and one-click updates pull the latest images and recreate containers without manual intervention. The stack is a single Docker container running on Node.js with Socket.IO for reactivity and stores no external database. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
MetaMCP
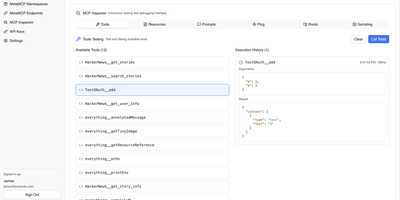
With 2,600+ GitHub stars, MetaMCP solves the MCP server sprawl problem by aggregating any number of upstream servers into a single authenticated endpoint that any MCP client connects to once. Group servers into namespaces — development tools in one, data sources in another — then publish each namespace as its own SSE, Streamable HTTP, or OpenAPI endpoint with API-key authentication in headers or query parameters, or full OAuth per the MCP Spec 2025-06-18 standard. The aggregation engine discovers tools, resources, and prompts from all active servers in parallel, prefixes tool names with server identifiers to prevent collisions, and applies configurable middleware including tool filtering to reduce context-window bloat and description overrides to improve LLM comprehension. The web management UI lets you configure MCP servers with stdio, SSE, or Streamable HTTP transports, toggle servers active or inactive per namespace, create and revoke API keys per endpoint, and inspect discovered tools with their schemas. Nested MetaMCP support enables hierarchical architectures where one MetaMCP instance consumes another, creating multi-level tool organization with automatic name resolution. Compatible with Claude Desktop, Claude Code, Cursor, Open WebUI, and any MCP-compatible client through a single connection URL. The Docker container packages the TypeScript backend with PostgreSQL for configuration persistence, exposing the management UI on port 12005 and MCP endpoints on configurable ports. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.

CubeSandbox
CubeSandbox gives every AI agent its own hardware-isolated MicroVM with a dedicated Linux kernel — not a shared-kernel container but a true KVM virtual machine — booting in under 60ms with less than 5MB of memory overhead per instance, enabling thousands of concurrent sandboxes on a single server via kernel sharing and Copy-on-Write memory. The Rust-built CubeProxy exposes an E2B SDK-compatible REST API on Axum, so existing E2B Cloud applications switch by changing one environment variable with zero client code changes. CubeMaster orchestrates cluster-level scheduling in Go while Cubelet manages node-local sandbox lifecycles including create, run, pause, resume, snapshot, and destroy operations. CubeVS, the eBPF-powered network layer, enforces per-sandbox isolation with LPM trie-based egress policies entirely in kernel space — no userspace context switches — while CubeEgress provides an L7 security proxy with per-domain, per-path, and per-method allowlists plus automatic credential injection that keeps secrets invisible to sandbox code. Hundred-millisecond-granularity snapshots enable checkpoint, rollback, and parallel fork from any saved state. The volume framework supports E2B-compatible pluggable storage with independent lifecycle and cross-sandbox sharing. Production deployment uses Terraform on Tencent Cloud or Helm charts on Kubernetes, K3s, or TKE, with full ARM64 support alongside x86_64 and AutoPause/AutoResume for cost optimization. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
OpenLLM
OpenLLM serves any large language model as an OpenAI-compatible API endpoint from a single CLI command, handling model download, backend selection, quantization, and port binding automatically. It supports the full spectrum of popular models including Llama 3.3, Qwen2.5, DeepSeek, Mistral, and Phi3, choosing between vLLM and PyTorch inference backends based on hardware capabilities. When vLLM is available, continuous batching with PagedAttention achieves up to 23x throughput improvement over naive serving, while GPTQ and bitsandbytes quantization reduces memory requirements for GPU-constrained deployments. The server exposes a RESTful API on port 3000 with full OpenAI client library compatibility, enabling drop-in replacement for commercial providers in any application using the standard chat completions format. A built-in web chat UI at the /chat endpoint provides immediate interactive testing without external clients. Custom model repositories allow teams to maintain private catalogs of fine-tuned models alongside the default repository that tracks the latest releases. Deployment workflows generate production-ready Docker images automatically, with Kubernetes manifest support for orchestrated scaling. Native integration with LangChain and LlamaIndex supports RAG pipelines, Transformers Agents enables tool-calling workflows, and HuggingFace Hub handles model discovery. Server-Sent Events enable real-time token streaming across all API endpoints. Backed by BentoML's production ML infrastructure. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
PowerDNS-Admin
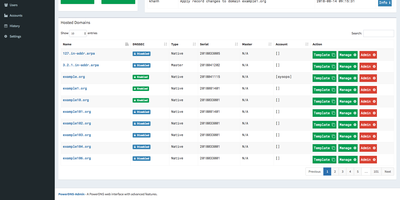
Raw zone files and API calls become something a whole team can operate safely once PowerDNS-Admin puts its web interface in front of a PowerDNS authoritative server. It's a Python/Flask application covering full forward and reverse zone management, with the touches that matter in daily DNS work: zone templates for stamping out consistent new domains, easy IPv6 PTR record editing (reverse zones by hand are misery), full IDN/Punycode support for internationalized domains, and DynDNS 2 protocol support so routers and scripts can update records the way they would against a commercial dynamic-DNS service. Access control is enterprise-grade: local users, LDAP against OpenLDAP or Active Directory, SAML, and OAuth via Google, GitHub, Azure, or OpenID Connect, hardened with TOTP two-factor authentication. Role-based permissions extend to zone-specific access control - hand a developer their project's zone without exposing the rest of your namespace - and activity logging records who changed which record when, the audit trail bare PowerDNS never gives you. The dashboard monitors PDNS service configuration and statistics, and its own API exposes zone and record management for automation on top of the UI. Runs against MySQL/MariaDB or PostgreSQL, talking to PowerDNS through its REST API. MIT-licensed.
UWAS
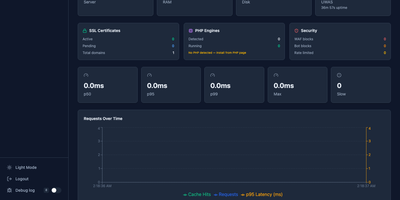
One 18 MB Go binary does the job of Apache, Nginx, Varnish, Caddy, and cPanel combined. Point UWAS at your /var/www directory and it auto-detects sites, provisions Let's Encrypt certificates, enables HTTP/3 via QUIC, and activates a two-tier caching engine with L1 memory shards and L2 disk storage, all before you write a single line of configuration. The React 19 admin dashboard provides 42 management pages for domains, PHP versions, databases, cron jobs, DNS records, file management, backup and restore, SFTP users, and uptime monitoring with real-time SSE updates. PHP sites run through FastCGI with connection pooling and full .htaccess compatibility, so WordPress, Laravel, and legacy applications work without migration effort. The built-in WAF catches SQL injection, XSS, path traversal, and shell exploits, while per-domain rate limiting and bandwidth caps protect against abuse. Reverse proxy mode supports five load balancing algorithms, circuit breakers, canary deployments, and mirroring for blue-green rollouts. Git deploy clones your repository, runs the build, checks health, and restarts the service with rollback on failure. An MCP server lets AI agents manage domains, cache, and deployments through natural language. The Nginx and Apache migration CLI converts existing configurations to UWAS format automatically. Deploy on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Portabase
Portabase takes a zero-trust approach to database backups: lightweight Rust/Tokio agents deploy next to each database, encrypt dumps with AES-GCM before data ever leaves the host, and poll the Next.js control plane outbound every five seconds requiring zero inbound firewall rules. This architecture contains blast radius if the dashboard is compromised while supporting ten engines with stable backup and restore: PostgreSQL 12 through 18, MySQL 5.7 through 9, MariaDB 10 and 11, MongoDB 4 through 8, SQLite 3.x, Redis 2.8+, Valkey 7.2+, Firebird 3.0 through 5.0, Microsoft SQL Server 2017 through 2022 including Azure SQL, and Docker volumes on Engine 20.10+. Encrypted backups store on configurable backends including local filesystems, any S3-compatible provider (AWS, MinIO, RustFS), Google Cloud Storage, and Azure Blob Storage. Cron-based scheduling with Grandfather-Father-Son retention policies automates backup lifecycle management, while on-demand restore targets any compatible server for cross-environment recovery. The CLI installs agents with a single command and auto-updates when new versions ship. A RESTful API with MCP server integration enables automation from CI/CD pipelines and AI agent workflows. Developed by a non-profit under Apache-2.0. 1,270+ stars and 174 releases since October 2024. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console.
ServerBee
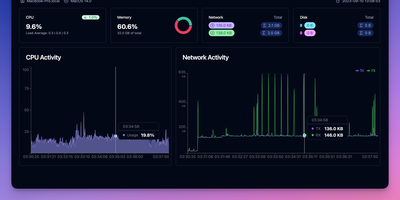
ServerBee delivers complete fleet monitoring from a single Rust binary that embeds both the server and web UI, requiring no external database or heavy runtime. Lightweight agents installed on each node stream CPU, memory, disk, network, load, temperature, GPU, and disk I/O metrics over persistent WebSocket connections to a central server backed by embedded SQLite. The real-time React dashboard presents 17 drag-and-drop widget types across custom layouts, with historical charts spanning one hour to 30 days and monthly traffic statistics with billing-cycle prediction and cost insights including burn rate and per-resource unit cost scoring. Network monitoring covers ICMP, TCP, and HTTP ping probes, service monitors for SSL certificates, DNS records, HTTP keyword matching, TCP ports, and WHOIS expiration, plus network-quality probing across 96 China 3-ISP and international presets with IP-quality and streaming-unlock detection. Remote management features include a web terminal with sandboxed file manager, Docker container stats with logs and events, firewall configuration, and agent auto-update capabilities. Public status pages display 90-day uptime timelines, while alerting supports email and webhook notifications with flexible trigger expressions. A native iOS companion app provides mobile monitoring access. Deploy via Docker or download the single binary for Linux, macOS, or Windows, running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Statping-ng
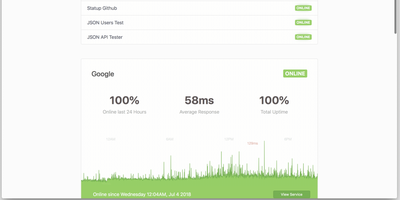
A status page and uptime monitor in one Go binary: Statping-ng - the actively maintained fork of Statping - replaces the UptimeRobot-plus-Statuspage combo with a ~20 MB Docker image using under 50 MB of RAM. It checks services over HTTP, TCP, UDP, ICMP ping, and gRPC health checks on configurable intervals, with per-service timeouts, expected status codes, POST requests with custom JSON bodies, SSL verification, and failure thresholds before alerting. The public status page is the differentiator against plain monitors: visitors see live status, uptime percentages, and latency charts grouped into service categories, with incident announcements and scheduled-maintenance messages you publish from the dashboard - and Sass-based custom styling matches the page to your brand rather than a vendor template. When something fails, notifiers fire immediately: Slack, Discord, Telegram, SMTP email, PagerDuty, Twilio SMS, Pushover, and custom webhooks, each testable before saving. Because notifiers are single Go files, the plugin system makes new channels straightforward. A RESTful API manages services and reads uptime data programmatically, and the free Statping mobile app connects to your server via QR code for on-the-go monitoring. Data persists to SQLite, MySQL, or PostgreSQL. Point it at internal services too - anything the container can reach is monitorable.
Nixopus
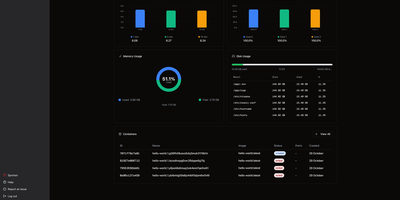
Tell an AI agent to deploy your app and watch it actually happen. Nixopus connects to your GitHub repo, analyzes the codebase to detect your framework, generates the right Docker configuration, resolves dependency conflicts, and ships the whole thing to your server with HTTPS enabled. When something breaks, the agent reads the logs, creates a pull request with a fix, and redeploys without waking you up. The chat interface lets you deploy, add custom domains, check logs, roll back, and troubleshoot in plain English from the web dashboard or directly from your VS Code or Cursor editor. Extensions bring one-click installs for 100+ self-hostable apps like Appwrite, Excalidraw, and Ollama, each showing you exactly what it runs on your server before installation. Connect multiple servers and monitor CPU, memory, disk, and running containers across your entire fleet from a single dashboard with draggable widget layouts. The built-in terminal opens SSH sessions right in the browser with split-pane support, so you can watch logs in one pane while running commands in another. Framework detection covers Next.js, Django, Rails, Go, FastAPI, and anything else that fits a container image. Every deployment gets automatic TLS via Caddy with Let's Encrypt certificates provisioned and renewed silently. Previous container images are retained so rollbacks skip the rebuild step entirely. Deploy on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
CoreObs
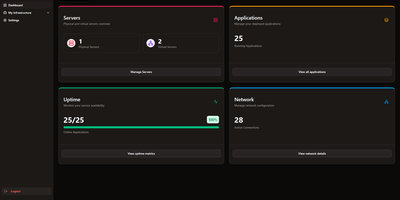
CoreObs delivers a unified self-hosted dashboard that replaces the typical combination of Uptime Kuma, Homer, and separate monitoring tools with a single interface for managing your entire server infrastructure. The Next.js frontend with shadcn components provides a modern dark-themed UI displaying server hardware metrics collected by a lightweight Go agent that leverages Glances for hardware abstraction — streaming real-time per-core CPU load, RAM utilization, NVIDIA GPU statistics, disk usage, system uptime, and load averages via WebSocket connections. The application registry tracks all self-hosted services with configurable uptime monitoring, availability history charts, and instant notifications through Discord, Telegram, Pushover, and email when services go down or recover. Quick-access links provide one-click navigation to each application's management panel directly from the dashboard. The network visualization module built on React Flow enables creating visual topology maps of your infrastructure with drag-and-drop nodes representing servers, switches, and services connected by labeled edges. Server data can be organized with tags, copied between entries, and monitored with configurable pagination and compact view modes. Deploy via Docker Compose with three containers — the Next.js web interface, the Go monitoring agent, and PostgreSQL 17 for persistent storage. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Yacht
Docker deployment reimagined as an app store: browse a visual catalog of applications, click to deploy with sensible defaults, and customize ports, volumes, and environment variables only when you need to. Point Yacht at any Portainer-compatible template JSON URL and it parses every application into a browsable, searchable interface with pre-configured settings ready for one-click launch. The template framework is fully decentralized — anyone can host template files on GitHub, a personal server, or any URL, creating a community-driven ecosystem of deployment packages without central gatekeeping. Template variables prefixed with ! automatically substitute server-level settings, so !config resolves to your configured path across every deployment without repetitive manual editing. The Python backend handles container lifecycle — start, stop, restart, kill, removal — while streaming real-time logs, providing browser-based shell access, and monitoring resource statistics through the Vuetify dashboard. Docker Compose stacks sit alongside individual containers in the same management interface. Advanced editing lets you modify port mappings, volumes, environment variables, and restart policies on running containers without redeployment. The develop branch introduces agent-managed remote host support for expanding management to additional Docker hosts. Authentication can be disabled for environments behind external proxies like Authelia or Traefik forward auth. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. CC-BY-4.0 licensed.
Vigil
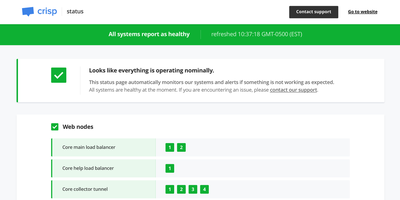
Vigil monitors your entire distributed infrastructure and generates a public status page from a single Rust binary small enough to run on a Raspberry Pi, consuming minimal CPU and memory while providing crash-free reliability. Four distinct monitoring modes cover every topology: poll probes check HTTP, TCP, SSH, and ICMP endpoints for reachability with configurable intervals and thresholds; push probes receive health reports from Vigil Reporter libraries embedded in your application code across Node.js, Python, Golang, Rust, TypeScript, Dart, and C#; local probes delegate monitoring to Vigil Local slave daemons running behind firewalls on separate LANs; and script probes execute custom shell commands for specialized health checks. Each monitored service transitions through healthy, sick, and dead states based on consecutive probe failures, with configurable thresholds controlling state transition sensitivity. When services change state, Vigil dispatches notifications through twelve alert channels including Slack, Email, Twilio SMS, Telegram, Pushover, Gotify, XMPP, Matrix, Zulip, Cisco Webex, and generic webhooks. The generated status page displays service groups organized by category with real-time replica status, system load metrics from reporter probes, and a maintenance announcement system for communicating planned downtime through the Manager HTTP API. Configuration uses a single TOML file defining all probes, services, and notification channels with no database dependency. Docker deployment pulls the official image with volume-mounted configuration. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MPL-2.0 licensed.
Usulnet
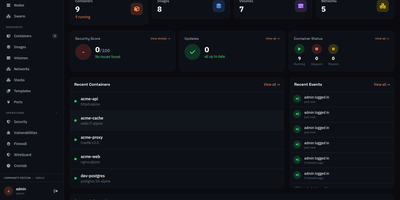
Usulnet packs container management, Trivy security scanning, Nginx reverse proxy, scheduled backups, WireGuard VPN, firewall rules, and multi-node orchestration into a single 70MB Go binary with zero external runtime dependencies. Every module ships in one download with no paid tiers, no telemetry, and no edition gating. Container lifecycle management covers creation, start, stop, restart, pause, kill, and removal with bulk operations, real-time resource statistics, filesystem browsing, and settings editing. Trivy integration scans images and running containers for CVEs with severity scoring, generates SBOMs, and validates CIS benchmarks. The multi-node architecture supports standalone, master, or agent modes where agents connect over NATS JetStream with mTLS encryption, enabling remote Docker host management from a central dashboard. Reverse proxy configuration handles Nginx with automatic Let's Encrypt certificates, TCP/UDP stream proxying, access lists, and dead host detection. Backup operations capture container volumes and Compose stacks on configurable schedules with retention policies and full restore capabilities. A built-in application catalog provides 60+ one-click templates for common services. JWT license validation uses an RSA-4096 public key embedded in the binary, requiring no call-home and working entirely offline. For teams tired of maintaining separate tools for each infrastructure concern, Usulnet collapses the entire stack into a single point of management with Docker Compose deployment alongside PostgreSQL, Redis, and NATS.