Tugtainer
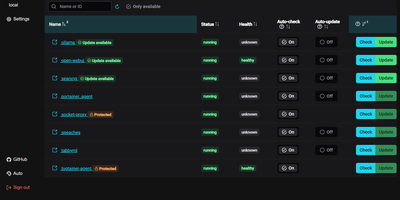
Tugtainer delivers a visual command center for Docker environments that automates container image updates, monitors registry releases, and manages application lifecycles across multiple servers without command-line intervention. System administrators can inspect running containers across all connected hosts, trigger immediate image pulls, and configure automated cron schedules for recurring health and registry checks. Flexible update policies allow teams to flag production databases as notification-only while automatically updating stateless web applications whenever new image tags publish. When updating linked services, the platform analyzes Docker Compose project definitions and custom dependency labels to stop and restart containers in strict dependency order, preventing broken network links and orphaned volume mounts. Administrators can authenticate private container registries, browse image layers and tags, and view real-time container log streams directly within the browser console. Automated pruning jobs continuously reclaim server disk space by deleting obsolete, untagged images and dangling build layers after successful deployments. Multi-channel alerting integrates with over fifty notification providers, delivering real-time update summaries and error warnings directly to Discord, Telegram, Slack, and email webhooks. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Dagger
With 16,100 GitHub stars and created by Solomon Hykes (co-founder of Docker), Dagger eliminates proprietary YAML DSLs from CI/CD by letting developers write pipelines as real programs in their preferred language — then executing them identically on a laptop, in GitHub Actions, in GitLab CI, or on any machine with a container runtime. The BuildKit-based Dagger Engine runs every pipeline operation inside OCI containers, constructing a directed acyclic graph where each node is cached by default, parallelized automatically, and produces bit-for-bit reproducible outputs regardless of execution environment. Native SDKs generated from the GraphQL API schema provide Go, Python, TypeScript, PHP, Java, .NET, Elixir, and Rust developers with full type safety, IDE autocomplete, and the ability to unit-test CI pipelines using the same testing frameworks as application code. The module ecosystem enables cross-language composition where a Python team can invoke a Go team's build functions without learning Go, while filesystems, secrets, git repositories, and network tunnels are passed between functions as strongly-typed objects. Pipeline operations cache at container-layer granularity with content-addressed deduplication, and the interactive REPL enables step-by-step pipeline debugging with live container inspection. Host dependencies are explicit and strictly typed, eliminating implicit environment coupling that causes "works on my machine" failures. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Conductor
Originally built at Netflix to orchestrate microservices powering 230 million subscribers and now trusted in production at Tesla, LinkedIn, and J.P. Morgan, Conductor is the most battle-tested open-source workflow engine available — with 32,000 GitHub stars and horizontal scalability to billions of executions. The architecture cleanly separates orchestration from business logic: workflows are defined in declarative JSON while workers execute tasks in any of seven supported languages (Java, Python, Go, JavaScript, C#, Ruby, Rust) with zero framework constraints. Durable execution persists every state transition, enabling automatic retries, configurable timeouts, crash recovery, and instant replay from any failure point without re-executing completed tasks. Native AI agent orchestration supports 14+ LLM providers (Anthropic, OpenAI, Google Gemini, AWS Bedrock, Mistral, Cohere, HuggingFace, Ollama), MCP tool calling, function calling, human-in-the-loop approval gates, and vector database integration (Pinecone, pgvector, MongoDB Atlas) for RAG pipelines. Deploy with your choice of five persistence backends (PostgreSQL, Redis, MySQL, Cassandra, SQLite), six message brokers, and Elasticsearch or OpenSearch for workflow indexing — all configurable via Docker Compose files included in the repository. The built-in web UI provides workflow visualization, execution monitoring, task queue inspection, and manual intervention controls. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
phpMyAdmin
Since 1998, phpMyAdmin has been the standard web interface for MySQL and MariaDB - the tool millions of developers, DBAs, and hosting companies reach for when a database needs inspecting, fixing, or migrating. Written in PHP, it covers effectively the entire administration surface: create, browse, alter, and drop databases, tables, views, columns, and indexes; insert and edit rows through a tabular editor; manage user accounts and granular privileges; and maintain stored procedures, triggers, and events - all without touching a command line. The SQL editor executes arbitrary queries with syntax highlighting, autocompletion, history, and bookmarkable statements, including batch queries. Import/export is a migration workhorse: read SQL, CSV, XML, and OpenDocument spreadsheets in; write out to SQL dumps, CSV, JSON, XML, PDF, Word, LaTeX, and more - the fastest path for moving a WordPress database or handing a schema to a colleague. The Designer view renders your schema as an interactive ER diagram with drag-and-drop relationship editing, and data transformations display BLOBs as images or download links inline. Server maintenance views surface configuration suggestions. Multi-server support, dark mode, and translations into 72 languages round out a tool that earns its ubiquity. GPL-licensed.
HyperDX
HyperDX correlates logs, metrics, traces, session replays, and errors in a single interface so engineers can resolve production incidents in minutes instead of hours. Nearly 10,000 GitHub stars reflect its role as the integrated UI layer for the ClickStack blueprint endorsed by ClickHouse. The platform connects to any ClickHouse cluster as its storage backend, working with existing table structures without requiring data migration or proprietary ingestion formats. An intuitive Lucene-like search syntax supports full-text queries and property filtering like level:err or service.name:api without needing SQL, while native JSON string querying and event delta analysis surface anomalies in high-cardinality datasets. One-click cross-signal correlation lets you jump from a log line to its distributed trace, from a slow span to associated logs, or from a frontend session replay to the backend errors it triggered. The OpenTelemetry Collector accepts telemetry via OTLP on gRPC port 4317 and HTTP port 4318, supporting automatic instrumentation for Node.js, Python, Java, Go, Ruby, and browser applications. APM tracks HTTP request latency, database query duration, and external service calls with trace waterfall visualizations. Configurable alerts trigger via webhook, Slack, PagerDuty, or email when thresholds are breached. Deploys via Docker Compose with ClickHouse, MongoDB, Redis, and the OpenTelemetry Collector. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
HashiCorp Vault
With over 36,000 GitHub stars and adoption by organizations including Adobe, Shopify, and Roblox, HashiCorp Vault is the industry-standard platform for secrets management, encryption services, and privileged access control across hybrid and multi-cloud infrastructure. The key/value secrets engine stores arbitrary secrets with full versioning, soft-delete, and metadata tracking, while dynamic secrets engines generate on-demand, short-lived credentials for AWS, Azure, GCP, databases including PostgreSQL, MySQL, MongoDB, and MSSQL, and SSH access with automatic revocation after configurable lease periods. The PKI secrets engine dynamically issues X.509 certificates on demand with automatic rotation and ACME protocol support, eliminating manual certificate management workflows entirely. Encryption as a service through the transit secrets engine lets applications encrypt, decrypt, sign, verify, and generate HMACs without managing cryptographic keys directly, supporting AES-GCM-256, ChaCha20-Poly1305, RSA-2048/4096, ECDSA-P256/P384, and ED25519 algorithms. Authentication integrates with LDAP, OIDC/OAuth2, SAML, AppRole for machine-to-machine access, Kubernetes service accounts, AWS IAM, Azure Active Directory, and GitHub tokens. Fine-grained ACL policies use path-based rules with glob patterns and sentinel policies for programmatic enforcement. The integrated Raft storage backend provides high-availability clustering without external dependencies, while alternative backends include Consul, S3, DynamoDB, PostgreSQL, and MySQL. The built-in web UI provides a visual interface for browsing secrets, managing policies, configuring auth methods, and monitoring cluster health. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSL 1.1 licensed.
Databasement
Databasement puts scheduled backup and restore for nine database engines behind one polished web interface, deployed as a single Docker container on port 2226. The Laravel and Livewire backend uses native CLI tools for MySQL 5.6 through 9.x, PostgreSQL 12 through 18, MariaDB 10.x through 12.x, Microsoft SQL Server 2017 through Azure SQL, MongoDB 4.2 through 8.0, SQLite 3.x, Firebird 3.x through 5.x, Redis 2.8+, and Valkey 7.2+ with full restore support including cross-server recovery. SSH tunnel connectivity reaches databases behind firewalls via bastion servers with password or private key authentication, and remote agents handle isolated networks by connecting outbound over HTTPS without inbound ports. Scheduling supports arbitrary cron expressions with GFS grandfather-father-son retention alongside simple time-based cleanup. Storage spans local disk, S3-compatible services including AWS and MinIO, Azure Blob, Samba/SMB shares, and SFTP/FTP servers. Scheduled restores automate production-to-staging synchronization on recurring intervals. Failure notifications alert via Email, Slack, Discord, Telegram, Pushover, Gotify, and webhooks with detailed job logs. The REST API and built-in MCP server enable CI/CD pipeline integration and AI assistant access from Claude, Cursor, and VS Code Copilot. 1,700+ stars since November 2025. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
OneUptime
With 7,400+ GitHub stars and a feature set that replaces seven separate SaaS subscriptions — Pingdom for monitoring, StatusPage.io for status pages, PagerDuty for on-call, Incident.io for incident management, Datadog for APM, Loggly for logs, and Sentry for error tracking — OneUptime delivers every tool your reliability team needs in a single open-source platform that is genuinely 100% open source under Apache 2.0 (not open-core). Uptime monitoring runs synthetic checks against websites, APIs, ports, SSL certificates, and DNS records from distributed global probes with configurable intervals and thresholds. Branded status pages publish automatically when monitors detect issues, notifying subscribers via email, SMS, webhook, or RSS without manual intervention during an outage. On-call scheduling routes alerts through escalation policies to the right engineer via phone call, SMS, push notification, Slack, or Microsoft Teams. The incident management workflow handles declaration, triage, communication, resolution, and post-mortem generation in a unified timeline. APM collects traces and metrics via native OpenTelemetry integration — no proprietary agents required — while log management provides full-text search and alerting. An AI agent continuously monitors telemetry data, identifies root causes, and opens GitHub pull requests with proposed fixes for review. Deploy via Docker Compose or Kubernetes Helm charts with a Terraform provider for infrastructure-as-code configuration. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Orbit
Orbit is a free, realtime project management platform that unifies issue tracking, kanban boards, sprint cycles, and collaborative documents into a keyboard-driven workspace with native AI agent integration. Engineers can manage backlog items across customizable kanban boards, execute timeboxed sprint cycles with automated burndown charts, and link pull requests directly to the tasks they resolve. Team members compose specifications and meeting notes in rich-text documents with nested collections, inline comment threads, public sharing links, and self-contained interactive web pages that render alongside active project milestones. The built-in standup board aggregates workspace activity into an interactive kanban filtered to individual assignees, while comprehensive analytics dashboards report issue throughput, scope modifications, churn rates, and team distributions. Autonomous coding assistants connect directly through the integrated Model Context Protocol server to inspect project status, triage incoming tickets, file detailed bug reports, and trigger automated notifications across workspace channels. Custom views allow teams to filter issues by priority, estimate, or assignee and save shared workspace perspectives for recurring planning sessions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Harbor
The first container registry to reach CNCF graduated status with over 29,000 GitHub stars since VMware open-sourced it in 2016, Harbor transforms the basic Docker Distribution into a hardened enterprise registry with vulnerability scanning, supply chain signing, multi-datacenter replication, and project-level access control out of the box. Trivy scans every pushed image against the NVD, GitHub Advisory Database, and distribution-specific vulnerability feeds, with scan-on-push policies that block deployment of images exceeding configurable severity thresholds. Artifact signing through Cosign keyless signatures and Notation enforces content trust policies ensuring only cryptographically verified images reach production clusters. Policy-based replication synchronizes images and Helm charts between Harbor instances across multiple datacenters using repository, tag, and label filters with automatic retry and bandwidth throttling — enabling hybrid-cloud and disaster-recovery topologies. The RBAC model isolates projects with per-project quotas, robot accounts for CI/CD automation, webhook notifications, and audit logging that tracks every pull, push, delete, and configuration change. LDAP, Active Directory, and OIDC authentication integrate with existing identity providers, while the proxy cache transparently caches images from Docker Hub, Quay, and other upstream registries to reduce pull latency and rate-limit exposure. The RESTful API with embedded Swagger UI, tag retention policies, garbage collection scheduling, and immutable artifact rules complete the lifecycle management. Deploy via Docker Compose or Helm Chart on Kubernetes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Omnigent
Open-sourced by the Databricks AI team under Apache 2.0 and reaching over 8,500 GitHub stars within two months of launch, Omnigent introduces the meta-harness concept: a common orchestration layer that sits above existing AI coding agents and makes them interoperable parts of a governed, collaborative system. The platform wraps Claude Code, Codex, Cursor, OpenCode, Hermes, Pi, and any custom agent defined in a simple YAML configuration file into sandboxed sessions with a uniform API, then exposes each session through the terminal, a web UI, a native desktop application, mobile interfaces, and a REST API. Built-in multi-agent workflows include Polly, a coding orchestrator that delegates tasks to parallel sub-agents in separate git worktrees and routes each diff to a reviewer from a different vendor, and Deep Research, which plans sub-queries, searches the live web through MCP servers, reads full pages, and cross-checks claims across independent sources. Contextual security policies go beyond static allow/deny rules by maintaining per-session state to enforce spend caps, model routing, approval gates for destructive actions, PII blocking, and repository-scoped write restrictions across server-wide, per-agent, and per-session levels. The OS sandbox restricts filesystem and network access while intercepting egress requests to inject credentials only on approved calls. Cloud sandbox providers including Modal, Daytona, E2B, CoreWeave, Kubernetes, and Databricks launch disposable execution environments per session. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
OpenObserve
With 20,500+ GitHub stars and over 6,000 organizations running it in production — including a Fortune 100 company ingesting more than 4 PB per day — OpenObserve is the open-source observability platform that replaces your entire Datadog, Splunk, or ELK stack with a single Rust binary deploying in under two minutes. Apache Parquet columnar storage with zstd compression on S3-compatible object storage delivers 140x lower storage costs than Elasticsearch while providing better query performance on a quarter of the hardware. Ingest logs, metrics, and distributed traces via native OpenTelemetry OTLP endpoints with no vendor lock-in. Query logs and traces with standard SQL, metrics with SQL or PromQL — no proprietary query language to learn. The built-in dashboard builder offers 19 chart types including time-series graphs, heatmaps, gauges, tables, and top-K lists with drag-and-drop layout combining data from all signal types. Data pipelines process, enrich, redact, or normalize ingestion streams using Vector Remap Language for real-time transformations including PII redaction and logs-to-metrics conversion. Real User Monitoring captures frontend performance with session replay. The Service Catalog provides topology-based trace analysis with side-panel drill-downs into database queries and error details. Alerting supports real-time and scheduled rules with SQL and PromQL conditions. Native multi-tenancy isolates organizations and streams with complete data separation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPLv3 licensed.
Rancher
Used by over 30,000 teams and 650+ enterprise customers managing more than 5.2 million containers, Rancher has earned recognition as a Leader in the Gartner Magic Quadrant for Container Management and the Forrester Wave for Multicloud Container Platforms. The platform provides a single pane of glass for provisioning, upgrading, and securing Kubernetes clusters across Amazon EKS, Google GKE, Microsoft AKS, RKE2, K3s, and any CNCF-conformant distribution. Multi-Cluster Management enables centralized authentication via Active Directory, LDAP, SAML, GitHub, and OpenID Connect with granular role-based access control at the cluster, project, and namespace levels. Fleet, the built-in GitOps engine, delivers continuous deployment across hundreds of clusters simultaneously using Helm charts, Kustomize, or raw YAML manifests from any Git repository. The integrated app catalog provides one-click deployment of Prometheus monitoring, Grafana dashboards, Longhorn persistent storage, Istio service mesh, and hundreds of community Helm charts. Rancher supports air-gapped installations for disconnected environments, CIS benchmark scanning for security compliance, and automated backup and restoration of cluster configurations. The dashboard offers real-time workload monitoring, log aggregation, pod shell access, and namespace-scoped resource quotas. Cluster templates enforce organizational standards through Helm-based provisioning policies that ensure consistent configurations across environments. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Kestra
With over 27,000 GitHub stars and an ecosystem of 1,900+ plugins covering every major cloud provider, database, and SaaS platform, Kestra is the orchestration engine that brings Infrastructure as Code principles to workflow automation — defining complex multi-step pipelines in readable YAML that execute across any language, runtime, or infrastructure boundary. The built-in VS Code-style editor provides syntax highlighting, auto-completion, real-time validation, and an AI Copilot that generates workflow YAML from natural language descriptions. Tasks execute in Python, Node.js, Go, R, Shell, SQL, or any Docker container, with event-driven triggers listening for file arrivals on SFTP and cloud storage, messages from Kafka, Redis, Pulsar, AMQP, MQTT, NATS, AWS SQS, Google Pub/Sub, and Azure Event Hubs in real time. The topology view visualizes workflow DAGs with execution state, duration, and output artifacts for each task node. Namespaces organize workflows into isolated environments with configurable secrets, while subflows enable modular composition with inputs, outputs, and conditional branching. Retry policies, timeouts, error handlers, and automatic backfills for missed schedules ensure reliability across production workloads. Git integration pushes workflows directly to branches from the UI with CI/CD pipeline support for automated deployment. The REST API enables programmatic workflow management, execution triggering, and resource provisioning. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
MeshCentral
With over 7,000 GitHub stars and continuous development since 2017 by former Intel engineer Ylian Saint-Hilaire, MeshCentral has become the go-to self-hosted alternative to ConnectWise Control and Splashtop for managing devices remotely without per-seat licensing fees. The Node.js server installs via a single npm command and manages Windows, macOS, Linux, and FreeBSD endpoints through lightweight agents that maintain persistent WebSocket connections for real-time remote desktop, terminal access, and file transfer directly in the browser. Intel AMT integration provides out-of-band hardware management including power control and BIOS access even when the operating system is unresponsive. Device groups organize endpoints by location, customer, or function with granular role-based access control for multi-technician environments. Session recording captures remote desktop interactions for compliance auditing, while Wake-on-LAN powers on machines remotely across subnets. The server supports MongoDB for production deployments handling thousands of agents or the embedded NeDB for smaller setups under 200 devices, with a single 8GB VPS comfortably managing 1,500 concurrent agents. Security features include mandatory TLS with automatic Let's Encrypt certificate provisioning, multi-factor authentication via TOTP and FIDO2, SAML-based single sign-on, IP filtering, and HashiCorp Vault integration for secrets management. The web console provides real-time device monitoring with hardware and software inventory, network topology visualization, and customizable branding. TacticalRMM uses MeshCentral as its remote access layer. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Gotify
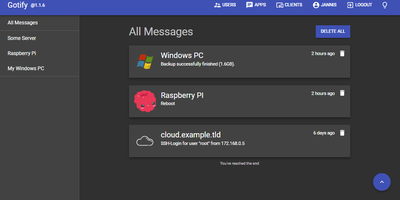
Real-time alerts from your own infrastructure to your phone, with no Firebase, Pushover, or third-party push service in the path: Gotify is a simple, self-hosted notification server written in Go. The model is deliberately minimal: senders push messages with a single HTTP POST to the REST API, receivers subscribe over a WebSocket stream, and a clean React web UI manages the pieces. Senders are namespaced as "applications," each with its own token, so your backup script, Uptime Kuma, CI pipeline, and cron jobs each get an identity, an icon, and independently revocable credentials - centralized alerting from many services with per-source management. Messages carry a title, body, and priority level that maps to notification importance on the client. The official Android app (on both F-Droid and Google Play, notable for working entirely without Google Play Services) shows push notifications for new messages; the web UI itself supports Web Push in the browser; and gotify/cli pushes messages from shell scripts with one command. A server-side plugin system adds custom behavior, and the whole thing runs as a single small binary with SQLite by default - near-zero resource footprint. Because dozens of tools (and Apprise) speak Gotify natively, it slots in as the notification hub for an entire homelab or ops stack.
Vaultwarden
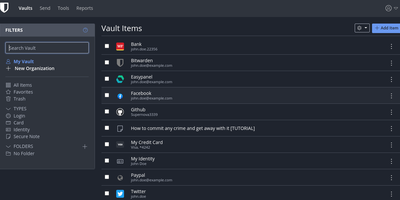
The Bitwarden server, reimplemented in Rust: Vaultwarden (formerly bitwarden_rs) is the unofficial lightweight edition. It speaks the same wire protocol as the official server, so every official Bitwarden client - browser extensions, iOS, Android, desktop, and the bw CLI - connects without modification, while the server itself runs as a single container against SQLite (or MySQL/MariaDB/PostgreSQL) instead of the official multi-container stack that wants gigabytes of RAM. Features Bitwarden gates behind paid tiers ship free: organizations with collections, groups, member roles, and policies; TOTP code storage; file attachments; Bitwarden Send; Emergency Access; event logs; and admin password reset. Two-factor options cover authenticator apps, email, FIDO2 WebAuthn, YubiKey, and Duo, and OIDC-based SSO landed natively in v1.35.0. Zero-knowledge encryption is unchanged - vault data is encrypted client-side and the master password never reaches the server. Attachments and Sends store on local disk or S3-compatible backends, an admin panel manages users and server settings, and backup is copying one data directory. Suited to individuals and teams up to roughly 50 users.
xyOps
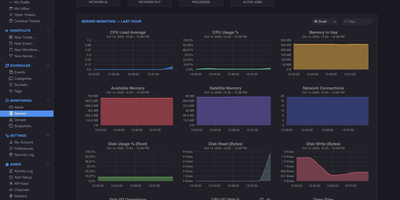
With 4,500+ GitHub stars and version 1.0.92 released August 2026, xyOps delivers a complete operations platform that unifies workflow automation, job scheduling, server monitoring, alerting, and incident response in one self-hosted system. The platform uses a distributed architecture where a central conductor coordinates lightweight xySat satellite agents running on Linux, macOS, or Windows worker nodes via persistent WebSocket connections. The visual workflow builder lets you chain events, triggers, actions, and monitors into multi-step pipelines with conditional logic, fan-out/fan-in parallelism, multiplex controllers for fleet-wide execution, and configurable resource limits. QuickMon provides per-second CPU, memory, disk, and network visibility streamed live to the web UI, while user-defined monitor plugins sample metrics every minute with time-series storage at hourly, daily, monthly, and yearly resolutions. Alert triggers evaluate expressions against live data and fire notifications via email, webhook, or custom actions, with full server snapshots attached showing every running process, network connection, and resource utilization at the moment of detection. Failed jobs and alerts automatically create tickets with linked logs, metrics history, and context for end-to-end incident tracking. The plugin marketplace supports extensions written in any language, and the Docker plugin enables container-based job execution. Deploy via Docker with persistent volumes on port 5522 for the web UI and 5523 for API access, running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD-3-Clause licensed.