WoodPecker CI
With 7,300+ GitHub stars and active releases through version 3.17, Woodpecker CI is the community-driven fork of Drone CI that kept the entire platform open source under Apache 2.0 — delivering a lightweight, container-native CI/CD engine that runs on minimal resources while providing enterprise-grade pipeline automation. Every pipeline step executes in an isolated Docker container, ensuring reproducible builds with zero host contamination and clean teardown after each run. Define workflows in simple YAML configuration files with step dependencies, conditional execution via when filters, service containers for databases and caches, and matrix builds that test across multiple language versions, platforms, or database engines simultaneously. Deep forge integration connects to GitHub, GitLab, Gitea, Forgejo, and Bitbucket via OAuth and webhooks, triggering pipelines on push, pull request, tag, deployment, and cron events. The plugin ecosystem inherits compatibility with the Drone plugin library — over 100 plugins for Docker builds, S3 uploads, SSH deployment, Slack and Telegram notifications, Helm deployments, and more. The server-agent architecture separates the web UI, API, and scheduler from pipeline execution, enabling horizontal scaling by adding agents across multiple machines or architectures including ARM. Secrets management supports global, organization, and repository-level scopes with approval workflows for forked repository pipelines. The admin web UI provides user management, agent monitoring, and queue control. Docker Compose deployment provisions the complete stack in under five minutes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Bitwarden
Backed by nearly 20,000 GitHub stars and ranked number one in G2's Enterprise User Satisfaction for eleven consecutive quarters, Bitwarden is the open-source password manager trusted by millions worldwide. The zero-knowledge encryption architecture ensures all vault data — passwords, passkeys, credit cards, identities, secure notes, and file attachments — is encrypted exclusively on client devices using AES-256 with PBKDF2-SHA256 or Argon2id key derivation and RSA-2048 for organization key exchange. Cross-platform clients span a web vault, browser extensions for Chrome, Firefox, Safari, Edge, Opera, Vivaldi, and Brave, native desktop apps for Windows, macOS, and Linux, mobile apps for iOS and Android, and a CLI for scripting. Bitwarden Send enables time-limited, password-protected sharing of text and files, while the built-in TOTP authenticator generates two-factor codes alongside stored credentials. Enterprise deployments integrate with identity providers through SAML 2.0 and OpenID Connect SSO, automate provisioning via SCIM or Directory Connector supporting LDAP, Active Directory, Azure AD, Okta, and OneLogin, and enforce security policies with custom roles and granular permissions. Emergency access allows designated contacts to request vault view or takeover through configurable waiting periods with cryptographic key exchange. The Secrets Manager stores API keys, tokens, and infrastructure credentials with native GitHub Actions, GitLab CI/CD, Ansible, and Terraform integrations. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Open Code Review
Originated as Alibaba Group's official internal AI code review assistant serving tens of thousands of developers and identifying millions of code defects over two years before open-sourcing in May 2026 — now at 21,000+ GitHub stars — Open Code Review is the production-hardened platform that proves enterprise-grade code review can be fully open-source under Apache 2.0. The hybrid architecture separates deterministic engineering pipelines (file selection, diff parsing, rule matching for NPE, thread-safety, XSS, and SQL injection across 10+ languages) from LLM-powered agent reasoning with tool-use capabilities including FileRead, CodeSearch, and cross-file context inspection, consuming approximately one-ninth the tokens of general-purpose coding agents while delivering line-level precise comments with severity and confidence scoring. The bundled web dashboard (port 4173) provides review management, findings triage, result browsing, and direct GitHub posting without external dependencies, while the session viewer (port 5483) renders full LLM request/response traces for debugging and auditing. Integration spans GitHub Actions, GitLab CI, GitFlic CI, and Gerrit with delegation mode enabling Claude Code, Cursor, and other AI agents to leverage OCR's engineering logic alongside their own LLM reasoning. Supports OpenAI, Anthropic, Google Gemini, DeepSeek via built-in providers plus Ollama and vLLM for air-gapped deployments. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
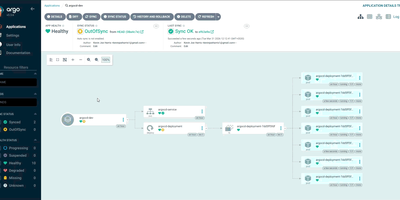
Argo CD
A CNCF Graduated project with over 23,700 GitHub stars and adoption by organizations including Intuit, Adobe, Capital One, and Red Hat, Argo CD has become the industry standard for GitOps-based Kubernetes deployments since its creation at Intuit in 2018, treating Git repositories as the single source of truth for application configurations and automatically reconciling live cluster state with declared desired state. The platform supports Helm charts including Helm 4, Kustomize overlays, Jsonnet, and plain Kubernetes YAML manifests, rendering templates and applying resources through configurable sync policies with automated or manual reconciliation, pruning of orphaned resources, and self-healing that reverts unauthorized cluster changes. ApplicationSets enable templated generation of applications across multiple clusters, environments, and Git repositories using generators for pull requests, Git directories, cluster lists, and merge strategies. The web UI provides a real-time application topology view with resource health status, sync state indicators, log streaming, and a network view supporting Gateway API and Ingress visualization. Version 3.5 introduced mTLS for internal component communication, graduated user impersonation and source hydrator to beta, added native ApplicationSet management with preview applications in the UI, and delivered source integrity validation. Multi-cluster management deploys applications across development, staging, and production environments from a single Argo CD instance with RBAC, SSO via OIDC and SAML, and audit logging. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Apache Airflow
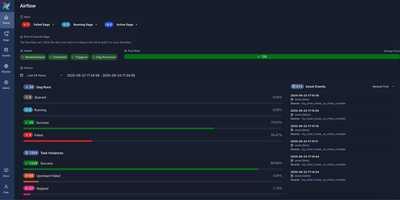
With over 46,000 GitHub stars and one of the largest communities in data engineering, Apache Airflow is the workflow orchestration platform that lets teams define, schedule, and monitor complex data pipelines as Python code through directed acyclic graphs. Airflow 3.x introduced a modernized architecture with a task execution API, the Language Task SDK for writing task implementations in Java and Go alongside Python, asset-based partitioning with FanOutMapper and FixedKeyMapper for data-driven scheduling, a first-class state store for tasks and assets, pluggable retry policies, and a redesigned React-based web UI built on FastAPI. The provider ecosystem ships 80+ packages covering AWS, Google Cloud, Azure, Snowflake, Databricks, Apache Spark, Apache Kafka, PostgreSQL, MySQL, MongoDB, Slack, HTTP, SSH, Docker, Kubernetes, and dozens more, enabling a single deployment to orchestrate jobs across multi-cloud and on-premises infrastructure. The scheduler supports cron expressions, timetable plugins, data-aware scheduling triggered by asset events, and dynamic task generation through Python loops and conditionals. Built-in operators include BashOperator, PythonOperator, DockerOperator, KubernetesPodOperator, and sensor operators that poll external systems. The web UI provides DAG visualization with Gantt charts, grid views, and graph views, task instance logs, SLA monitoring, connection and variable management, and role-based access control. Deployment options include standalone mode, Docker Compose with CeleryExecutor or KubernetesExecutor, Helm charts for Kubernetes, and managed cloud services. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache License 2.0 licensed.
Jaeger
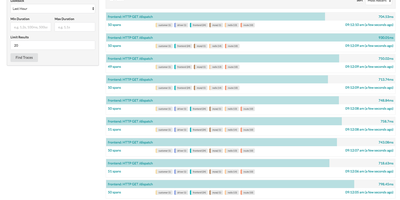
Created by Uber Technologies and graduated as the seventh CNCF top-level project in October 2019 with over 23,000 GitHub stars, Jaeger has become one of the most widely deployed open-source distributed tracing platforms, processing billions of spans per day in production environments at organizations including Uber, Red Hat, and Shopify. Version 2 rebuilt the platform on the OpenTelemetry Collector framework, inheriting its extensible pipeline architecture while implementing Jaeger-specific features as extensions and components, enabling seamless integration with the OpenTelemetry ecosystem through native OTLP protocol support. The platform stores traces in Cassandra 4.0+, Elasticsearch 7.x/8.x, OpenSearch 1.0+, ClickHouse, or the embedded Badger database for development setups. Three sampling strategies control trace volume: head-based sampling with constant, probabilistic, and rate-limiting modes, tail-based sampling using the OpenTelemetry Collector processor that evaluates complete traces before storage decisions, and adaptive sampling that dynamically adjusts probabilities based on observed traffic patterns. Service Performance Monitoring computes RED metrics directly from spans, displaying request rates, error rates, and latency percentiles in the Monitor tab with drill-down from aggregate service views to individual traces. The web UI provides trace search with multi-field filtering, trace detail views with span timeline visualization, trace comparison across services, and dependency graphs mapping service relationships from actual traffic. Deployment options range from a single all-in-one binary for development to distributed collector-ingester-query configurations with Kafka intermediate buffering for production scale. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Coroot
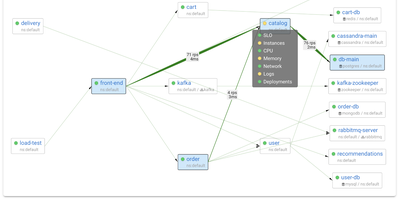
Coroot uses eBPF to capture metrics, distributed traces, logs, and continuous CPU profiles directly from the Linux kernel, delivering full observability without any application code changes, SDKs, or sidecars. From the first minute of deployment, an automatically generated service map covers every microservice, database, message queue, and external dependency with request rate, error rate, and latency measurements. When a service breaches its SLO, AI-powered inspections analyze telemetry across all dimensions to pinpoint the root cause and send a single consolidated alert with findings, replacing the flood of fragmented notifications typical of traditional monitoring. Deployment tracking automatically discovers Kubernetes rollouts and compares each release against the previous one to detect performance regressions, resource spikes, and cost impacts without CI/CD pipeline integration. Continuous profiling captures CPU flame graphs down to the line of code with negligible overhead. Integrated cost monitoring tracks cloud spending across AWS, GCP, and Azure, attributing expenses to individual services and deployments. Coroot supports Prometheus, OpenTelemetry, and ClickHouse as data sources and works identically on Kubernetes clusters, virtual machines, and bare-metal hosts. 7,700+ GitHub stars. Apache-2.0 licensed.
Checkmate
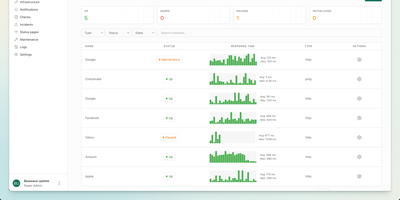
With 10,400 GitHub stars, 153 contributors, and no per-monitor pricing to worry about, Checkmate delivers comprehensive infrastructure monitoring from a single self-hosted dashboard — tracking uptime, page speed, server hardware, Docker containers, and even game servers without sending a byte of telemetry off your network. Ten monitor types cover HTTP, ping, TCP, gRPC, WebSocket, DNS, SSL certificate expiry, Docker container health, Lighthouse page speed with Core Web Vitals tracking, and game server status for over 100 server types including Minecraft and CS2. The Globalping integration enables geo-distributed monitoring from six continents, running ping and HTTP checks from Africa, Asia, Europe, North America, South America, and Oceania with results plotted on an interactive map. The optional Capture agent written in Go collects CPU, RAM, disk usage, temperature, and network metrics from any Linux, Windows, Mac, or Raspberry Pi host. Public status pages ship with four built-in themes and custom branding support, showing per-service uptime bars and incident history on a single shareable URL. Alert notifications reach teams through email, Discord, Slack, PagerDuty, Microsoft Teams, Telegram, Matrix, ntfy, Twilio SMS, and webhooks. Deploy via a single Docker Compose file requiring roughly 1 GB RAM — up and running in under five minutes on any Docker host. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPLv3 licensed.
Sencho
With over 430 GitHub stars and designed for DevOps engineers, platform teams, and homelab operators, Sencho is the self-hosted Docker Compose control plane that gives you a real operational cockpit without abandoning file-on-disk compose workflows. The web dashboard provides live CPU, memory, and disk sparklines per container, one-click start/stop/restart controls, and a Monaco-powered YAML editor with syntax highlighting, inline diff, and one-click rollback. Compose files remain the source of truth on the host filesystem. Multi-node management connects remote Sencho instances via authenticated HTTP and WebSocket proxy using long-lived API tokens, with no SSH access or exposed Docker sockets required. The Pilot Agent establishes an outbound-only WebSocket tunnel for nodes behind NAT, CGNAT, or strict firewalls. Blueprints define compose intent once and deploy it across label-targeted nodes, with drift detection keeping the fleet aligned. Fleet Federation provides cordon and pin controls for maintenance windows, while Fleet Actions execute bulk deploy, stop, and restart operations by stack label across the entire infrastructure. The security suite includes Trivy vulnerability scanning, deploy enforcement policies, SARIF and SBOM export, and Fleet Sync to replicate scan policies across replicas. Additional capabilities include 199+ one-click app templates, Git source integration, atomic deploys with auto-rollback, auto-heal, scheduled operations, webhooks, and custom S3 off-site backups to MinIO, R2, B2, or AWS. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
OliveTin
With over 3,600 GitHub stars and a philosophy of deliberate simplicity, OliveTin eliminates the need for SSH sessions, admin panels, and complex automation platforms by letting you define shell commands in a YAML config file and access them as clickable buttons through a clean browser interface. The Go binary consumes only a few megabytes of RAM, running on everything from tiny ARM and RISC-V devices through Linux VMs, containers, macOS, and Windows. Each button executes a predefined shell command with optional typed arguments that render as dropdowns, text fields, and validated inputs, preventing free-form command entry while giving users controlled access to server operations. Access control lists define exactly who can view or run each action — guests, family members, or junior administrators see only the buttons they are permitted to use. Entity templates generate actions dynamically from lists of hosts, containers, or other resources, creating one template that produces many buttons without manual duplication. Flexible triggers extend beyond browser clicks: cron schedules, webhooks, calendar file events, and filesystem watchers run actions automatically when conditions are met. Authentication supports OAuth2, JWT, and header-based methods for integration with reverse proxies and identity providers. Dashboards organize actions into folders and fieldsets for clear navigation across dozens of commands. No plugin system, no extension marketplace, no premium tiers — every feature ships in the single open-source release. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
SwarmClaw
Running a single AI agent is straightforward; running a team of specialized agents that delegate tasks, share memory, and coordinate through structured workflows requires an orchestration layer, and that is exactly what SwarmClaw provides. Define a hierarchy of agents in an org chart where a Coordinator (your CEO agent) delegates research tasks to a Researcher, coding tasks to a Developer, and design tasks to a Designer, each configured with its own LLM provider, tool permissions, and skill set. The Task Board presents a Kanban view of all work items across Backlog, Queued, Running, and Completed columns, with each task card showing its assigned agent, tags, due dates, and approval gates that pause execution until a human reviews and approves. Agents execute work using built-in tools for file operations, shell commands, browser automation, and persistent memory, plus any MCP server you connect via stdio, SSE, or streamable HTTP transport. Durable structured sessions support branching logic, repeat loops, parallel branches with explicit joins, and restart-safe run state that survives crashes without losing progress. Over 23 LLM providers ship built-in: Claude Code CLI, OpenAI, Anthropic, Google Gemini, DeepSeek, Groq, Mistral, xAI Grok, Fireworks, Ollama, and more. Connectors push messages to Discord, Slack, and Telegram, while cron schedules and webhooks trigger agent runs automatically. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Zabbix
Monitoring everything from network switches to Kubernetes clusters since 2001 with over 6,200 GitHub stars and deployments exceeding 100,000 devices per installation, Zabbix has established itself as one of the most mature and feature-rich open-source monitoring platforms available, trusted by organizations including Dell, Salesforce, ICANN, and T-Mobile. The platform collects metrics from virtually any source using Zabbix Agent written in C, Zabbix Agent 2 written in Go with native plugin support, SNMP v1/v2c/v3 polling and trapping, IPMI for hardware health, JMX for Java applications, SSH and Telnet checks, HTTP/HTTPS polling, and ODBC database queries. Version 7.0 LTS introduced synthetic browser monitoring that executes user-defined JavaScript via WebDriver to simulate multi-step user interactions on websites, proxy load balancing with automatic host redistribution across proxy groups for high availability, in-memory proxy data buffering delivering up to 100x performance improvement, native multi-factor authentication with TOTP and Duo support, and just-in-time user provisioning from SAML and LDAP. Low-level discovery automatically detects file systems, network interfaces, SNMP OIDs, VMware resources, and Kubernetes pods, creating monitoring items and triggers dynamically. The alerting engine correlates events with configurable escalation chains, sending notifications through Slack, Microsoft Teams, PagerDuty, Jira, email, and SMS with customizable message templates. Over 1,000 official templates provide instant monitoring for Linux, Windows, VMware, AWS, Azure, Docker, PostgreSQL, MySQL, Apache, Nginx, and hundreds more. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
UptimeKuma
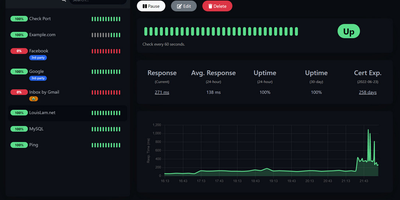
Sixty-thousand-plus GitHub stars make Uptime Kuma the most popular self-hosted monitoring tool - MIT-licensed, Node.js, and the standard replacement for UptimeRobot, Pingdom, and Freshping. It watches a dozen monitor types: HTTP(S) endpoints with keyword and JSON-query content validation, TCP ports, ICMP ping, DNS records, WebSockets, Docker containers via the socket, Steam game servers, MQTT brokers, gRPC services, and push-based heartbeats for cron jobs and internal workers. Checks run at intervals as tight as 20 seconds - versus UptimeRobot's 5-minute free tier - with unlimited monitors and unlimited data retention. When something fails, alerts fan out through 90+ notification channels: Slack, Discord, Telegram, email with LiquidJS templating, PagerDuty, OpsGenie, ntfy, Gotify, Matrix, and dozens more via native providers plus the Apprise library. Unlimited public or password-protected status pages - mappable to specific domains and organized into monitor groups - communicate health to customers, with maintenance windows that suppress alerts during planned work. The reactive dashboard graphs response times, tracks SSL certificate expiry with advance warnings, supports proxies and 2FA, and ships in dozens of languages. One Docker container with a SQLite volume covers an entire infrastructure.
ServerKit
ServerKit delivers a server control panel that fits on a small VPS while managing everything from Docker containers to mail servers. The Python/Flask backend exposes 1,519 REST endpoints across 107 blueprints with full OpenAPI documentation at /api/v1/docs, while the React frontend spans 65 screens in a 1.75MB gzipped bundle served entirely from your own infrastructure. Docker management includes full container lifecycle control, Docker Compose project orchestration, real-time log streaming, and terminal access. Database panels cover MySQL/MariaDB and PostgreSQL with user management, browser-based query consoles, and automated backups to S3, Backblaze B2, or local storage. Nginx virtual host management automates Let's Encrypt certificate provisioning with hardened TLS 1.2+ configurations and Cloudflare-aware setups. The Go-based cross-platform agent enables multi-server fleet management with HMAC-SHA256 authentication over a WebSocket gateway, supporting Linux, Windows, and macOS across amd64 and ARM64 architectures. Fleet monitoring provides cross-server heatmaps, metric comparison charts, alert thresholds, anomaly detection, and capacity forecasting. A built-in marketplace distributes 106 one-click application templates using a declarative YAML schema with Docker Compose stacks. The extension system allows community plugins for Kubernetes management, Redis browsers, and WordPress site orchestration. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
AWX
AWX transforms Ansible from a command-line tool into a centralized automation hub with a web UI, REST API, and distributed task engine for managing playbooks, inventories, and credentials at enterprise scale. The React-based dashboard provides real-time visibility into job status, inventory health, and execution history while Django REST Framework powers programmatic control over every automation resource. Job templates combine Ansible playbooks, inventories, and credentials into reusable units that chain together in workflow templates using directed acyclic graph orchestration with conditional branching on success, failure, or always-run logic and configurable convergence gates. The RBAC system built on django-ansible-base provides granular permission control over organizations, teams, projects, inventories, and credentials at object-level granularity. Dynamic inventory sources pull host data from AWS EC2, Google Cloud, Microsoft Azure, VMware vCenter, and Red Hat Satellite, while credential management securely stores SSH keys, cloud tokens, and vault passwords with HashiCorp Vault and CyberArk integration for external secret retrieval. Notifications deliver alerts via Slack, email, PagerDuty, Mattermost, IRC, and webhooks, while activity streams log every action for compliance auditing. The Receptor mesh network distributes job execution across isolated container-based execution environments with capacity-aware scheduling and hop-node routing for network-segmented infrastructures. Upstream of Red Hat Ansible Automation Platform. Deploys via Docker Compose with PostgreSQL and Redis or via the AWX Operator on Kubernetes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Checkcle
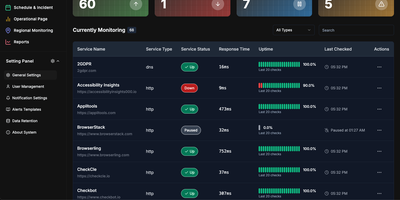
CheckCle provides a complete uptime monitoring and infrastructure observability platform that deploys with a single Docker container and stores all data in embedded SQLite via PocketBase. The Go backend runs three microservices — a service operation engine handling HTTP, HTTPS, DNS, Ping, and TCP checks at configurable intervals, a distributed regional check agent for multi-location network testing, and a server monitoring agent collecting CPU, RAM, disk usage, and network metrics via gRPC. The React frontend built with Vite, TypeScript, Tailwind CSS, and shadcn-ui subscribes to PocketBase WebSocket endpoints for real-time dashboard updates without polling. SSL and domain monitoring tracks certificate issuers, expiration dates, days remaining, and validation status. The incident management system records UP, DOWN, WARNING, and PAUSE states with full history, while scheduled maintenance windows prevent false alerts during planned downtime. Public status pages provide external stakeholders with live service health information. Health heatmaps visualize uptime performance and outage patterns over time. Notification channels include email, Telegram, Discord, and Slack, with multiple alert targets per monitored service. The one-click agent installation script supports Debian, Ubuntu, CentOS, Red Hat, Alpine, and Windows in beta. Docker deployment runs on port 8090 with a single persistent volume at /mnt/pb_data, requiring minimum 1 vCPU and 500MB RAM. On RepoCloud, deploy CheckCle on a dedicated VPS with root SSH access, persistent storage for your monitoring database, and complete control over agent endpoints and notification configurations, all under the MIT license.
LogTide
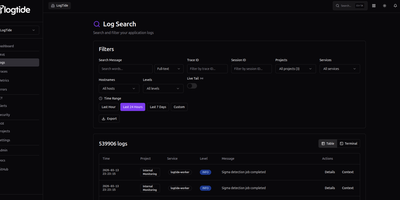
Every production incident starts the same way: someone asks "what do the logs say?" and the answer takes 45 minutes to find. LogTide collapses that search into seconds with a unified observability platform that indexes logs, traces, and metrics into a single queryable interface, backed by your choice of TimescaleDB, ClickHouse, or MongoDB. The log search interface supports full-text queries across millions of entries with filters for trace ID, session ID, project, service, hostname, and severity level, plus a live tail mode that streams new log lines as they arrive. Distributed traces render as waterfall timelines showing every span, its duration, and cross-service dependencies, while correlated logs for each trace are one click away. The metrics explorer visualizes OTLP gauge and counter data from your applications with system CPU, memory, disk, and network panels that update in near real-time. Where LogTide diverges from standard observability is its built-in SIEM engine: Sigma-compatible detection rules scan incoming logs for security threats like SQL injection, privilege escalation, lateral movement, and C2 communication, surfacing findings on a dedicated security dashboard with severity distribution, detection timelines, and affected service breakdowns. Alerting pushes notifications to Email, Slack, or Discord webhooks when thresholds trip or security rules fire. Native SDKs for Node.js, Python, Go, PHP, Kotlin, and Ruby ship logs with retry logic and circuit breakers, and the platform accepts OpenTelemetry data natively. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Infisical
API keys hardcoded in repos, database passwords pasted into CI variables, .env files emailed between developers - Infisical, the open-source platform for secrets, certificates, and privileged access management, is the answer to all three. Secrets live in versioned stores scoped by project, environment, and path, with fine-grained identity-aware access control and full audit logging on every read and change. Delivery covers every consumption pattern: CLI injection into local dev, SDKs for Go, Node.js, and Python, an HTTP API, agents, a Kubernetes Operator, and secret syncs that push to GitHub, GitLab, AWS Secrets Manager, and Vercel. Automatic rotation replaces credentials for PostgreSQL, MySQL, MSSQL, LDAP, AWS IAM, and Azure on a rolling schedule - new credentials issue while old ones stay temporarily valid, so nothing breaks mid-rotation. Dynamic secrets go further, generating ephemeral, time-bound database credentials on demand, and SSH access replaces static keys with short-lived CA-signed certificates that expire automatically. Secrets scanning catches hardcoded credentials in code and pipelines, certificate management automates X.509 issuance and renewal, and a built-in KMS handles encrypt/decrypt with central key control. Self-hosting keeps the keys to everything else on your own infrastructure.