Pulse
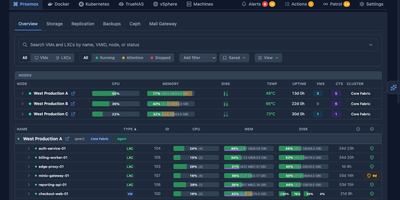
Pulse monitors your entire heterogeneous infrastructure from one screen: Proxmox VE, Proxmox Backup Server, Proxmox Mail Gateway, Docker, Podman, Docker Swarm, Kubernetes, TrueNAS SCALE/CORE, VMware vSphere, and standalone Linux/Windows/macOS machines. The Go binary embeds a SolidJS/TypeScript frontend, delivering WebSocket-driven dashboards with sub-second metric updates on port 7655. A unified agent auto-detects Docker, Podman, Kubernetes, and Proxmox on each host without manual configuration and self-updates silently, while Proxmox nodes need only API credentials with zero agent installation. Smart alerts use adaptive hysteresis-based thresholds to prevent notification floods, pushing to Discord, Slack, Telegram, Teams, email, ntfy.sh, Gotify, and generic webhooks with per-resource overrides. The standout feature is Pulse Patrol: scheduled AI health checks running every ten minutes to seven days using OpenAI, Anthropic, Gemini, or local Ollama models. Patrol catches silent backup failures, capacity creep, restart loops, unhealthy containers, and clock drift that dashboards miss when nobody is watching. Platform-specific views render Proxmox nodes, Ceph clusters, Docker Compose projects, Kubernetes workloads, TrueNAS pools, and vSphere VMs in familiar layouts. OIDC, SSO, and SAML authentication with credential encryption at rest secures access. 6,500+ stars and 441 releases since February 2025. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
VictoriaMetrics
Trusted by thousands of organizations processing billions of time series data points and backed by 17,000+ GitHub stars, VictoriaMetrics delivers a monitoring and time series database that outperforms Prometheus by 16x on query speed while consuming 2.5x less disk space through its optimized compression and storage engine. The architecture supports both single-node deployments handling 10M+ active time series and a horizontally scalable cluster version with vminsert, vmstorage, and vmselect components providing multi-tenancy, replication, and independent namespace isolation. Data ingestion accepts both push protocols including InfluxDB line protocol, Graphite plaintext, OpenTSDB HTTP, CSV, and OpenTelemetry OTLP alongside pull-based Prometheus scraping and remote write, enabling drop-in replacement of existing monitoring stacks without reconfiguring exporters. MetricsQL extends standard PromQL with additional functions, subqueries, and implicit time range alignment while maintaining full backward compatibility with existing Prometheus alerts and Grafana dashboards. The vmalert component processes recording and alerting rules with Alertmanager integration, while vmbackup and vmrestore enable point-in-time snapshots to S3, GCS, and Azure Blob Storage. Stream aggregation operates as a StatsD alternative for pre-aggregating high-cardinality metrics before storage. NFS-compatible storage backends including Amazon EFS and Google Filestore allow shared persistent volumes across cluster nodes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Agent Gateway
Backed by the Linux Foundation with contributions from AWS, Cisco, IBM, Microsoft, Red Hat, and Shell, Agentgateway is the first data plane built from the ground up for AI agent workloads — providing a unified Rust-based proxy that handles conventional HTTP and gRPC traffic alongside MCP tool servers, A2A agent communication, and LLM inference endpoints through a single deployment. The LLM gateway routes requests to OpenAI, Anthropic, Gemini, AWS Bedrock, and other providers through an OpenAI-compatible unified API with per-tenant budget controls, spend tracking, prompt enrichment, load balancing across multiple model endpoints, and automatic failover when providers experience outages. The MCP gateway federates multiple tool servers behind one endpoint, supporting stdio, HTTP/SSE, and Streamable HTTP transports with built-in OAuth authentication compliant with the MCP auth specification, integrating Auth0 and Keycloak out of the box. OpenAPI integration exposes existing REST APIs as MCP-native tools without code changes, enabling legacy services to participate in agent workflows. Policy-based RBAC controls which agents access which tools, while OpenTelemetry integration provides distributed tracing across agent communication chains. Deploy as a standalone binary with flat YAML configuration or on Kubernetes using the built-in controller with Gateway API support for declarative infrastructure-as-code management. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Dockge
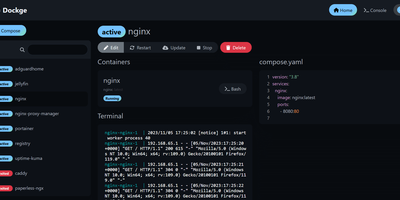
Created by the developer behind Uptime Kuma and carrying over 23,000 GitHub stars, Dockge brings the same clean, reactive design philosophy to Docker Compose stack management with a web interface that makes Portainer's compose handling feel like editing YAML in a terminal over SSH. The interactive editor provides syntax highlighting, inline validation, and a live preview of your compose.yaml files while keeping every stack stored as a standard file on disk in /opt/stacks by default, meaning you can seamlessly switch between the web UI and the docker compose CLI without lock-in or proprietary database formats. Real-time WebSocket updates stream pull progress, container start/stop transitions, and build output directly to the browser with no polling delays. The built-in web terminal opens a shell session inside any running container for quick debugging, while the docker-run-to-compose converter transforms single-container run commands into proper compose.yaml definitions with one click. Multi-agent support introduced in version 1.4.0 connects multiple Docker hosts to a single Dockge dashboard, enabling centralized management of stacks distributed across different servers. Image update detection shows which stacks have newer versions available, and one-click updates pull the latest images and recreate containers without manual intervention. The stack is a single Docker container running on Node.js with Socket.IO for reactivity and stores no external database. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
MongoDB
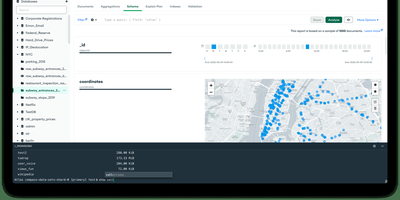
Used by over 46,800 companies including Forbes, Toyota, and Cisco, MongoDB stores data as flexible JSON-like BSON documents that eliminate rigid table schemas and support rapid application iteration. Its aggregation pipeline processes complex data transformations through composable stages including $match, $group, $lookup for joins, $unwind, and $project, operating directly within the database engine. Horizontal scaling is built in through automatic sharding, which distributes data across nodes using range-based, hashed, or zone-based shard keys, while replica sets provide automatic failover with configurable read preferences and write concerns. Multi-document ACID transactions span multiple collections and shards since version 4.0, enabling relational-style consistency guarantees within a document model. Starting with Community Edition 8.2, native full-text search and vector search are available directly in the database through $search and $vectorSearch aggregation stages, supporting RAG patterns, semantic retrieval, and hybrid search without external dependencies. Change streams provide real-time event-driven data access by tailing the oplog through the aggregation framework, enabling reactive architectures without polling. Time series collections offer optimized columnar storage for IoT sensor data and metrics with automatic bucketing and compression. Official drivers exist for Python, Node.js, Java, Go, C#, C++, Rust, Swift, and PHP, with MongoDB Compass providing a GUI for visual schema exploration and query building. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. SSPL v1 licensed.
MetaMCP
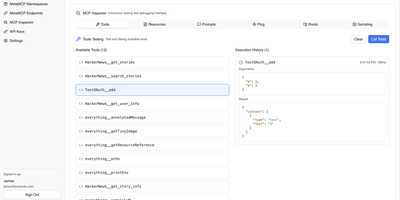
With 2,600+ GitHub stars, MetaMCP solves the MCP server sprawl problem by aggregating any number of upstream servers into a single authenticated endpoint that any MCP client connects to once. Group servers into namespaces — development tools in one, data sources in another — then publish each namespace as its own SSE, Streamable HTTP, or OpenAPI endpoint with API-key authentication in headers or query parameters, or full OAuth per the MCP Spec 2025-06-18 standard. The aggregation engine discovers tools, resources, and prompts from all active servers in parallel, prefixes tool names with server identifiers to prevent collisions, and applies configurable middleware including tool filtering to reduce context-window bloat and description overrides to improve LLM comprehension. The web management UI lets you configure MCP servers with stdio, SSE, or Streamable HTTP transports, toggle servers active or inactive per namespace, create and revoke API keys per endpoint, and inspect discovered tools with their schemas. Nested MetaMCP support enables hierarchical architectures where one MetaMCP instance consumes another, creating multi-level tool organization with automatic name resolution. Compatible with Claude Desktop, Claude Code, Cursor, Open WebUI, and any MCP-compatible client through a single connection URL. The Docker container packages the TypeScript backend with PostgreSQL for configuration persistence, exposing the management UI on port 12005 and MCP endpoints on configurable ports. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.

CubeSandbox
CubeSandbox gives every AI agent its own hardware-isolated MicroVM with a dedicated Linux kernel — not a shared-kernel container but a true KVM virtual machine — booting in under 60ms with less than 5MB of memory overhead per instance, enabling thousands of concurrent sandboxes on a single server via kernel sharing and Copy-on-Write memory. The Rust-built CubeProxy exposes an E2B SDK-compatible REST API on Axum, so existing E2B Cloud applications switch by changing one environment variable with zero client code changes. CubeMaster orchestrates cluster-level scheduling in Go while Cubelet manages node-local sandbox lifecycles including create, run, pause, resume, snapshot, and destroy operations. CubeVS, the eBPF-powered network layer, enforces per-sandbox isolation with LPM trie-based egress policies entirely in kernel space — no userspace context switches — while CubeEgress provides an L7 security proxy with per-domain, per-path, and per-method allowlists plus automatic credential injection that keeps secrets invisible to sandbox code. Hundred-millisecond-granularity snapshots enable checkpoint, rollback, and parallel fork from any saved state. The volume framework supports E2B-compatible pluggable storage with independent lifecycle and cross-sandbox sharing. Production deployment uses Terraform on Tencent Cloud or Helm charts on Kubernetes, K3s, or TKE, with full ARM64 support alongside x86_64 and AutoPause/AutoResume for cost optimization. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
MySQL
Powering Facebook, Uber, Twitter, and Booking.com, MySQL processes billions of queries daily as the world's most widely deployed open-source relational database. Its default InnoDB storage engine delivers full ACID compliance with row-level locking, crash recovery, and foreign key enforcement, making it the backbone of mission-critical e-commerce, SaaS, and financial applications. MySQL's Document Store bridges relational and NoSQL paradigms, allowing developers to work with schema-less JSON collections alongside traditional SQL tables through the X DevAPI protocol. For high availability, InnoDB Cluster combines Group Replication, MySQL Router, and MySQL Shell into an integrated solution with automatic failover, while InnoDB ClusterSet extends this across data centers for disaster recovery. The database supports multiple storage engines including MyISAM for read-heavy analytics, Memory for temporary high-speed caching, and Archive for compressed historical data. Native JSON functions like JSON_TABLE() transform document data into relational result sets, and spatial data types enable GIS applications. MySQL integrates with every major programming language through official connectors for Python, Java, Node.js, PHP, C++, and .NET, and works seamlessly with frameworks like Django, Laravel, Rails, and Spring. Replication topologies support read replicas for horizontal scaling, and the new Change Stream Applier in MySQL 26.7 enables configurable parallel transaction application with up to 1,024 workers per channel. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPLv2 licensed.
OpenLLM
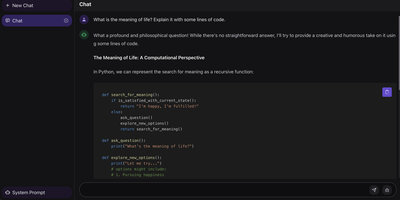
OpenLLM serves any large language model as an OpenAI-compatible API endpoint from a single CLI command, handling model download, backend selection, quantization, and port binding automatically. It supports the full spectrum of popular models including Llama 3.3, Qwen2.5, DeepSeek, Mistral, and Phi3, choosing between vLLM and PyTorch inference backends based on hardware capabilities. When vLLM is available, continuous batching with PagedAttention achieves up to 23x throughput improvement over naive serving, while GPTQ and bitsandbytes quantization reduces memory requirements for GPU-constrained deployments. The server exposes a RESTful API on port 3000 with full OpenAI client library compatibility, enabling drop-in replacement for commercial providers in any application using the standard chat completions format. A built-in web chat UI at the /chat endpoint provides immediate interactive testing without external clients. Custom model repositories allow teams to maintain private catalogs of fine-tuned models alongside the default repository that tracks the latest releases. Deployment workflows generate production-ready Docker images automatically, with Kubernetes manifest support for orchestrated scaling. Native integration with LangChain and LlamaIndex supports RAG pipelines, Transformers Agents enables tool-calling workflows, and HuggingFace Hub handles model discovery. Server-Sent Events enable real-time token streaming across all API endpoints. Backed by BentoML's production ML infrastructure. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Dockhand
Dockhand is a Docker management platforms, offering a modern alternative to Portainer with free OIDC SSO and vulnerability scanning that competitors gate behind paid tiers. Real-time container management provides start, stop, restart, and remove operations with live resource monitoring across CPU, memory, and network usage on a dashboard with real-time metrics. The visual Docker Compose editor enables stack creation and modification with syntax highlighting, while Git integration deploys stacks directly from repositories with webhooks and auto-sync for GitOps workflows. Vulnerability scanning powered by Grype and Trivy analyzes container images against CVE databases, with configurable auto-update scheduling that can trigger updates based on vulnerability severity criteria. The Hawser Go agent enables management of remote Docker hosts in Standard mode for LAN environments or Edge mode using outbound WebSocket connections for hosts behind NAT, firewalls, or dynamic IPs without exposing inbound ports. Interactive terminal sessions provide shell access into running containers, while the file browser enables uploading, downloading, and editing files directly within containers. Image management includes registry browsing, pull operations, and layer inspection alongside network and volume administration. The security-focused architecture builds its own OS layer from scratch using Wolfi packages via apko with every package explicitly declared. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSL 1.1 licensed, converting to Apache 2.0 in 2029.
Portabase
Portabase takes a zero-trust approach to database backups: lightweight Rust/Tokio agents deploy next to each database, encrypt dumps with AES-GCM before data ever leaves the host, and poll the Next.js control plane outbound every five seconds requiring zero inbound firewall rules. This architecture contains blast radius if the dashboard is compromised while supporting ten engines with stable backup and restore: PostgreSQL 12 through 18, MySQL 5.7 through 9, MariaDB 10 and 11, MongoDB 4 through 8, SQLite 3.x, Redis 2.8+, Valkey 7.2+, Firebird 3.0 through 5.0, Microsoft SQL Server 2017 through 2022 including Azure SQL, and Docker volumes on Engine 20.10+. Encrypted backups store on configurable backends including local filesystems, any S3-compatible provider (AWS, MinIO, RustFS), Google Cloud Storage, and Azure Blob Storage. Cron-based scheduling with Grandfather-Father-Son retention policies automates backup lifecycle management, while on-demand restore targets any compatible server for cross-environment recovery. The CLI installs agents with a single command and auto-updates when new versions ship. A RESTful API with MCP server integration enables automation from CI/CD pipelines and AI agent workflows. Developed by a non-profit under Apache-2.0. 1,270+ stars and 174 releases since October 2024. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console.
Semaphore
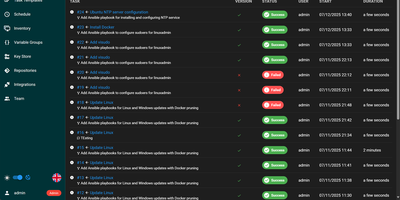
With nearly 14,000 GitHub stars and over 200 releases, Semaphore UI has established itself as the lightweight yet powerful alternative to enterprise automation platforms like Ansible AWX and Jenkins. Unlike AWX's heavyweight Kubernetes-dependent architecture, Semaphore ships as a single Go binary with zero external runtime dependencies — install it, run setup, and you have a production-ready automation server in minutes. The platform natively orchestrates Ansible playbooks, Terraform and OpenTofu infrastructure code, Terragrunt configurations, PowerShell scripts, Bash commands, and Python automation, all from a clean Vue.js web interface that displays task history, execution logs, and scheduling status at a glance. Semaphore supports concurrent task execution across multiple servers using distributed project runners, enabling horizontal scaling of automation workloads without complex clustering. The built-in inventory management system handles both static and dynamic inventory sources, while four-level RBAC (Owner, Manager, Task Runner, Guest) provides granular access control for team environments. Notifications flow to Slack, Microsoft Teams, Telegram, email, Rocket.Chat, and Gotify, keeping operators informed of failed tasks and deployment status. Integration with HashiCorp Vault secures sensitive credentials, and the comprehensive REST API with built-in Swagger documentation enables programmatic automation. Deploy via Docker Compose, Helm chart for Kubernetes, or native packages for Debian, Ubuntu, and RHEL-based distributions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
UptimeKuma
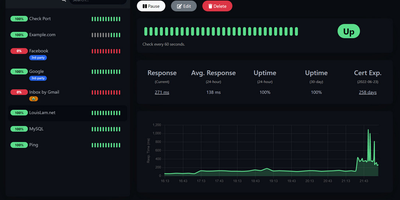
Sixty-thousand-plus GitHub stars make Uptime Kuma the most popular self-hosted monitoring tool - MIT-licensed, Node.js, and the standard replacement for UptimeRobot, Pingdom, and Freshping. It watches a dozen monitor types: HTTP(S) endpoints with keyword and JSON-query content validation, TCP ports, ICMP ping, DNS records, WebSockets, Docker containers via the socket, Steam game servers, MQTT brokers, gRPC services, and push-based heartbeats for cron jobs and internal workers. Checks run at intervals as tight as 20 seconds - versus UptimeRobot's 5-minute free tier - with unlimited monitors and unlimited data retention. When something fails, alerts fan out through 90+ notification channels: Slack, Discord, Telegram, email with LiquidJS templating, PagerDuty, OpsGenie, ntfy, Gotify, Matrix, and dozens more via native providers plus the Apprise library. Unlimited public or password-protected status pages - mappable to specific domains and organized into monitor groups - communicate health to customers, with maintenance windows that suppress alerts during planned work. The reactive dashboard graphs response times, tracks SSL certificate expiry with advance warnings, supports proxies and 2FA, and ships in dozens of languages. One Docker container with a SQLite volume covers an entire infrastructure.
Nango
The integrations your SaaS product offers its own users - that is what Nango, an open-source product-integrations platform, exists to build. It solves the repetitive infrastructure work behind every third-party API connection: OAuth flows, API key handling, token refresh, encrypted credential storage, rate-limit backoff, retries, and multi-tenant connection management. It ships pre-built auth configurations for 800+ APIs. Your users connect their accounts through an embeddable, white-label Connect UI, and your backend then reads or writes data through Nango's proxy, SDKs, or REST API without ever touching raw credentials. Integration logic is written as TypeScript functions covering actions, scheduled data syncs, and webhook processing - all running on one runtime with retries, checkpointing, and per-connection logs built in. Syncs pull records incrementally on a schedule, one-way or two-way, which suits RAG pipelines, search indexing, and keeping local copies of external data current. Selected actions can also be exposed as tool schemas or through a built-in MCP server, so AI agents operate on user-connected accounts without ever handling provider credentials. Auth support spans OAuth 2.0, OAuth 1.0a, API keys, basic auth, and JWT, and observability - logs, metrics, failure detection, and a reconnect flow for expired credentials - is scoped per customer connection for easier support debugging. Works with any backend language. Self-hosting on RepoCloud keeps all customer credentials and synced data on infrastructure you control, which matters for data residency and compliance requirements.
Ory Hydra
Ory Hydra is an OpenID Certified OAuth 2.0 and OpenID Connect provider that plugs into any existing user database or authentication system through a headless consent and login bridge, letting you own your authorization infrastructure without rebuilding identity management from scratch. The Go binary ships at under 15MB with zero system dependencies and exposes two distinct API surfaces: a public endpoint on port 4444 handling authorization code flows, token exchanges, PKCE challenges, device authorization grants per RFC 8628, and OpenID Connect discovery, plus an admin endpoint on port 4445 managing client registration, token introspection, consent session lifecycle, and JWKS rotation. Access tokens can be issued as opaque reference tokens or signed JWTs for stateless validation at resource servers, while refresh token rotation, token revocation per RFC 7009, and pairwise subject identifiers provide granular security controls. Persistent storage spans PostgreSQL, MySQL, and CockroachDB with automatic schema migrations, and the architecture supports horizontal scaling behind load balancers with shared database state. Dynamic client registration per RFC 7591 enables automated provisioning, and the OAuth 2.0 Threat Model security considerations are implemented as default behaviors rather than optional add-ons. Trusted by OpenAI and other internet-scale platforms. Helm charts and Docker Compose quickstarts provide production-ready deployment paths alongside the broader Ory ecosystem including Kratos for identity management, Oathkeeper for zero-trust API proxying, and Keto for fine-grained permissions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Treg
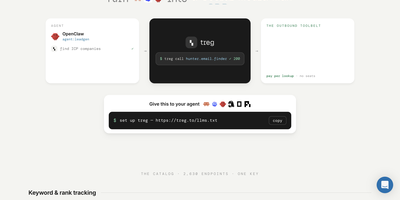
With over 330 GitHub stars and described as "OpenRouter, but for agent tools instead of models," Treg is the unified tool registry that gives your AI agent one base URL, one token, and instant access to approximately 2,800 cataloged endpoints across 56 providers — SEO and backlink analysis via Semrush and Moz, social media intelligence from TikTok and Instagram, people and company enrichment through Crunchbase and Hunter, media buying, scraping, and SERP data — all priced per call from fractions of a cent with no provider signup required. The FastAPI backend with PostgreSQL stores credential bindings and injects them server-side into every proxied request, ensuring API keys and OAuth tokens never touch the agent or local machine while every call is audit-logged. Teams register their own paid API accounts, OAuth connections, vendor CLIs like Stripe, GitHub CLI, Vercel, and gcloud, plus custom SKILL.md definitions — all callable by every teammate's agent through a single treg token with automatic credential injection. The evidence-based tool selector shows success rate, response speed, and last-seen timestamp for each provider, so agents pick tools on measured performance rather than guesswork. Bring-your-own-key routes bypass metering entirely, and the one-dollar free credit on every new team lets agents start calling immediately. The Vue.js web dashboard provides team management, audit logs, catalog browsing, and guided onboarding. Self-host with pip install tools-registry[server] on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Cognee
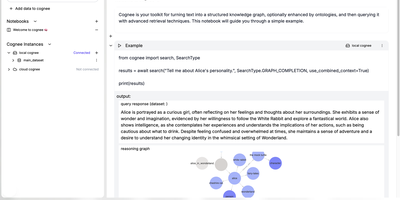
Cognee gives AI agents persistent long-term memory that survives across sessions, replacing the traditional stack of separate graph, vector, and session databases with a unified engine running on a single PostgreSQL instance. The memory-native API exposes four verbs (remember, recall, forget, and improve) enabling agents to persist context, retrieve cited answers, prune outdated knowledge, and self-improve from feedback. Under the hood, Cognee combines pgvector embeddings with a PostgreSQL-native graph store and cognitive-science-grounded ontology generation, delivering hybrid retrieval that fuses semantic similarity, structural graph traversal, and lexical search in a single query. Integrations span Claude Code, Cursor, LangGraph, OpenAI Agents, and any MCP-compatible client through a dedicated MCP server on port 8001, while the Python and TypeScript SDKs provide direct programmatic access. The platform supports swappable backends including Neo4j, FalkorDB, Qdrant, ChromaDB, Weaviate, Milvus, and LanceDB for teams with existing infrastructure. Built-in OpenTelemetry tracing, an experimental dashboard with knowledge graph visualization, multi-tenant user isolation, and audit trails ensure production readiness. Deploy via Docker Compose with optional profiles for PostgreSQL, Neo4j, Redis, and the web frontend. Reached v1.0 in April 2026 with 30,000+ stars. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Zitadel
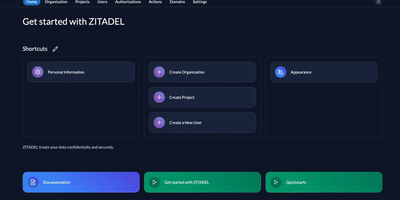
Securing a SaaS product, running B2B onboarding, or replacing Auth0 and Keycloak with a stack they own - teams needing more than basic auth reach for ZITADEL, an open-source identity and access management platform built in Go. Its multi-tenancy model is the differentiator: a strict Instance, Organization, Project hierarchy isolates data and scopes policy at each level, with identity brokering (pre-built templates for Google, GitHub, Microsoft, Apple, plus generic OIDC, OAuth, SAML, and LDAP), domain discovery that routes users to the right organization by email domain, and delegated management so customers administer their own users and roles. Authentication covers OpenID Connect (certified, including device authorization and token exchange), SAML 2.0 as both IdP and SP, SCIM, FIDO2 passkeys for phishing-resistant passwordless login, and MFA via OTP, email, SMS, and U2F; machine-to-machine flows support JWT profile, PATs, and client credentials. The architecture is event-sourced - every mutation is an immutable event, yielding a complete audit trail - with relational projections for queries and no external session store, so it scales horizontally. API-first with gRPC and REST, extensible via Actions webhooks, and the same codebase self-hosted (Docker Compose or Helm on PostgreSQL) as in the cloud.