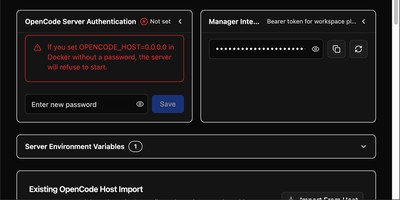
OpenCode Manager
OpenCode Manager is a mobile-first command center for AI coding agents. Install the PWA on your phone or tablet and you get real-time streaming chat, multi-repository Git operations, and scheduled automation right in your pocket. Git integration handles SSH-authenticated repo cloning, worktree management, unified diffs, and branch operations across all your projects in one dashboard. Chat with coding agents through Server-Sent Events streaming that supports slash commands, @-mentions for files, Plan and Build modes, and Mermaid diagram rendering for architecture discussions. Schedule reusable prompts to run against any repository on intervals or cron expressions, with each run tracking history and linking to sessions so you can pick up exactly where automation left off. MCP server configuration adds local and remote HTTP servers with OAuth support, plugging into the broader Model Context Protocol ecosystem. A dedicated assistant workspace provides an isolated AI environment with auto-provisioned skills for managing schedules, notifications, and settings. Multiple AI providers are supported including Anthropic, GitHub Copilot, and OpenAI-compatible services, each configurable with custom system prompts and granular tool permissions. Push notifications alert you to session events, agent questions, errors, and task completions across all managed repositories.
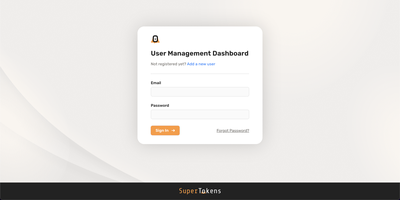
SuperTokens
Powering authentication for over 15,000 GitHub stargazers and production deployments across startups and enterprises alike, SuperTokens delivers the complete login infrastructure that Auth0, Firebase Auth, and AWS Cognito charge premium prices for — entirely open source under Apache 2.0 with no per-user limits. The Java-based core service runs as a lightweight HTTP microservice that connects to PostgreSQL or MySQL and handles email-password login, passwordless magic links and OTP via email or SMS, social OAuth with Google, GitHub, Facebook, Apple, and any custom OIDC provider, phone-password authentication, and time-based one-time password multi-factor authentication. Session management uses rotating refresh tokens with anti-CSRF and anti-session-fixation protections, verifying tokens locally in your backend SDK without network round-trips to the core. Frontend SDKs for React, React Native, Angular, Vue, and vanilla JavaScript provide pre-built UI components for login, signup, email verification, and password reset flows, all customizable through an override system that lets you add pre- and post-API logic, custom hooks, and user event handlers. The built-in user management dashboard enables administrators to view users, reset passwords, revoke sessions, modify roles, and manage email verification status. Multi-tenancy and organization support powers B2B SaaS applications with tenant-level authentication configuration and Enterprise SSO via SAML and OIDC. Migration tools support bulk importing millions of existing password hashes, TOTP secrets, and role mappings. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
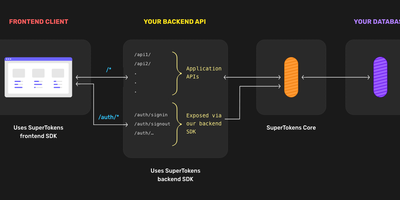
Supertokens Core
Authentication that lives inside your application rather than behind a redirect to an external identity provider - SuperTokens takes a fundamentally different architecture from Auth0 and AWS Cognito. Three tiers make that work - frontend SDKs (React, Angular, Vue, vanilla JS, React Native) render overridable login UI and manage tokens; backend SDKs (Node.js, Python, Go) expose auth endpoints on your own API domain; and SuperTokens Core, the piece you host here, is the stateless HTTP service handling core auth logic, password hashing, token signing, and database operations against PostgreSQL. The recipe system keeps features decoupled: use email/password, social login, passwordless (magic links, OTP), phone-password, multi-factor authentication (TOTP, WebAuthn), user roles, and microservice auth - individually or combined; you can even use SuperTokens purely for session management alongside another login provider. Sessions are where it shines: rotating refresh tokens with theft detection, automatic access-token refresh, CSRF protection, and secure cookie handling out of the box - the details that become vulnerabilities when hand-rolled. Verification happens locally in your backend via cached JWT signing keys, so the Core stays off the hot path. Self-hosted means no user limits, free forever, with all user data in your database. Apache-licensed.
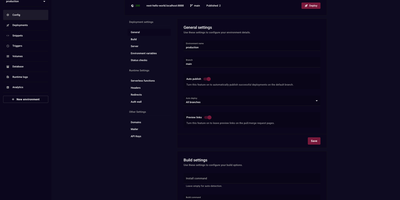
Stormkit
Stormkit delivers a self-hostable PaaS that eliminates vendor lock-in while providing Vercel-class deployment workflows. The Go backend handles build orchestration, hosting, and background job processing while the React frontend provides a complete management dashboard for applications, environments, and team collaboration. Git integration with GitHub, GitLab, and Bitbucket enables push-to-deploy workflows where every commit triggers automated builds with preview links posted directly to pull requests. Serverless functions use filesystem-based routing — each TypeScript or Node.js file in the API directory becomes an endpoint automatically, deploying to AWS Lambda with configurable timeouts. PostgreSQL database schemas ship with automatic migrations, isolated credentials per environment, and secure environment variable injection preventing credential leakage between staging and production. Custom domains provision TLS certificates automatically through Let's Encrypt with support for custom certificates and headers. The environment system creates isolated deployment contexts for production, staging, and development with independent variables, domain bindings, and auto-publish rules per branch. Privacy-respecting server-side analytics track visitors, referrers, and top paths without client cookies or third-party scripts. Role-based access control manages team permissions across applications. Docker Compose deployment provisions the full stack including the API server, hosting service, build runner, and worker server. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Activepieces
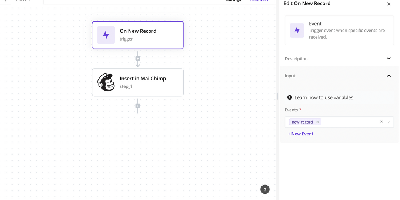
Zapier's job, on your own server: Activepieces is an open-source workflow automation platform built to be exactly that replacement. Flows are built in a visual no-code editor with triggers, actions, loops, conditional branches, auto-retries, raw HTTP steps, and code steps that run JavaScript or TypeScript with full npm package support. Integrations are "pieces" - type-safe TypeScript npm packages with hot reloading for local development - and the catalog spans 600+ services, with the large majority contributed by the community. The platform is AI-first in two directions: native AI pieces call OpenAI, Anthropic, Google, and Azure models inside flows, and every piece automatically doubles as an MCP server, so assistants like Claude Desktop and Cursor can invoke your integrations and workflows through natural language. A built-in MCP server also exposes 30 tools for building flows, managing tables, and running tests agentically. Flows are fully versioned with draft and locked states. The core is MIT-licensed and runs on TypeScript with PostgreSQL and Redis.
GrowChief
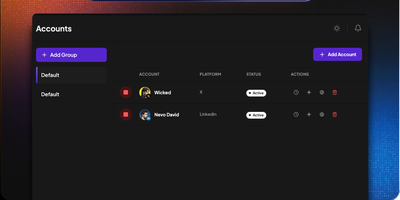
GrowChief delivers a self-hostable social media automation engine that replaces expensive SaaS tools like PhantomBuster, Expandi, and Zopto with a Docker-deployable alternative you fully control. The React and NestJS monorepo architecture runs headful Chrome via xvfb with Playwright and Patchright for maximum stealth — natural mouse movements and randomized interaction patterns make automation indistinguishable from manual browsing. Temporal orchestration manages workflow execution with built-in concurrency control that throttles actions to one every ten minutes per account even when ten workflows trigger simultaneously, preventing rate-limiting and account flags. The enrichment waterfall resolves profile URLs from partial data — provide an email address or organization name and GrowChief queries multiple providers to locate the correct social profile automatically. Working hours scheduling ensures outreach runs only during configurable business hours regardless of when leads enter the pipeline via the public REST API. Proxy support accepts custom SOCKS5 and HTTP proxies per account for geographic distribution and IP isolation. The public API enables full workflow management and lead injection from n8n, Make, Zapier, or any HTTP client, with a dedicated n8n custom node shipping ready to install. The multi-step workflow builder lets you chain connection requests, profile visits, message sends, and conditional delays into repeatable sequences. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
HolyClaude
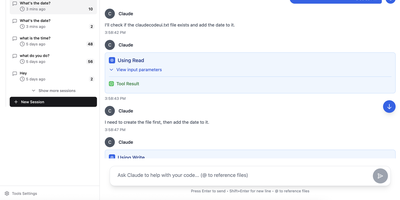
With 2,400+ GitHub stars, HolyClaude replaces a two-hour manual setup process with a single docker compose up command that launches a fully configured AI coding workstation. The container ships with Claude Code pre-installed alongside seven additional AI CLIs — Gemini CLI, OpenAI Codex, Cursor, TaskMaster AI, Junie, OpenCode with OpenRouter multi-provider support, and Pi Coding Agent — all accessible through the CloudCLI browser-based web interface on port 3001. A headless Chromium browser running on Xvfb display :99 comes pre-configured with Playwright 1.61 for automated screenshots, testing, and web scraping without additional setup. The development toolchain includes Node.js 26, Python 3, TypeScript, git, GitHub CLI, database clients for PostgreSQL, SQLite, and Redis, plus deployment CLIs for Vercel, Wrangler, Netlify, and Azure. Process management uses s6-overlay for automatic restarts and graceful shutdown, while bind mounts to ./data/claude and ./workspace ensure credentials, configuration, and project files persist across container rebuilds. The full image supports AMD64 and ARM64 architectures, running on Linux, macOS with Docker Desktop, Windows with WSL2, and Synology or QNAP NAS hardware. A slim tag at roughly 2GB omits the browser stack for environments that do not need it, while the full image at 4GB includes everything. Users authenticate with their existing Anthropic account directly through Claude Code with no credential relay or proxy involved. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Kutt
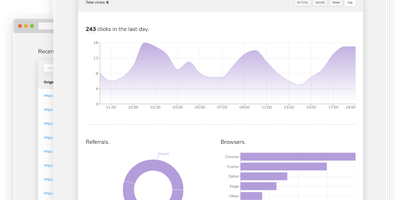
Built for self-hosting from the ground up, Kutt is a modern, MIT-licensed URL shortener: zero-configuration setup, no build step, and SQLite, PostgreSQL, or MySQL with optional Redis caching. Links carry real management features - custom slugs from a configurable alphabet (confusable characters like 0/O and l/1 omitted by default), password protection, descriptions, expiration times, and the ability to edit a destination URL without changing the short link already in circulation. Custom domains make branded short links first-class: add as many as you like and serve each under your own name instead of a third-party's. Private, per-link statistics track clicks, browsers, operating systems, and countries without logging visitor IPs or sensitive data. An admin page manages users and links instance-wide, and two environment flags (DISALLOW_REGISTRATION, DISALLOW_ANONYMOUS_LINKS) lock the instance down for private use; OpenID Connect login integrates with an existing identity provider. Automation runs through a documented REST API - create, list, delete, and pull stats - plus Chrome and Firefox extensions and ShareX compatibility for shortening from anywhere. Built with Node.js and React, deployed in one Docker container, it replaces Bitly with something you own: your domain, your analytics, and links that never die with a vendor.
Verdaccio
Private npm packages without shipping code to the public registry or paying for npm Enterprise: Verdaccio is the standard lightweight, zero-config private registry and caching proxy. It runs as a single Node.js process with its own tiny embedded database; no external database is required to start. Point npm, yarn, or pnpm at it and everything behaves as expected: install, publish, unpublish, dist-tags, and deprecation all work against the standard npm endpoints. The uplink system is where it earns its keep: packages not found locally are fetched from configured upstreams (npmjs.org, yarn, JFrog, Nexus, or another Verdaccio), cached as tarballs, and served locally thereafter - cutting CI latency and surviving registry outages. Multiple uplinks chain for failover, and per-package glob patterns in config.yaml route scopes to specific upstreams while controlling access, publish, and unpublish rights per group. You can even override a public package by publishing a patched version under the same name locally. A plugin architecture swaps in auth backends (htpasswd default, LDAP and others available), storage drivers (S3, Google Cloud Storage), middleware routes, and metadata filters. With official Docker images and a Kubernetes Helm chart, it slots into any pipeline in minutes.
NoteDiscovery
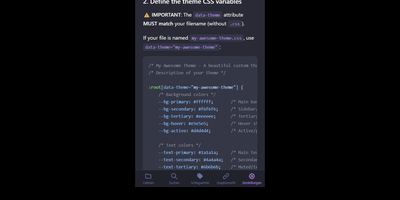
Transforming fragmented research notes, daily technical logs, and project documentation into an interconnected knowledge base is what NoteDiscovery delivers for privacy-conscious teams and researchers. Writers compose rich documents using a dual-pane editor that renders MathJax equations, interactive task lists, and dynamic Mermaid sequence diagrams side by side with raw text. The interactive knowledge graph maps semantic relationships across notebooks, allowing researchers to explore backlinks, uncover hidden topical connections, and navigate complex idea webs visually. Team members sketch architecture diagrams and wireframes directly inside note canvases using the integrated drawing tool, saving revisions as embedded image layers without external editors. The platform organizes thoughts through flexible tag hierarchies, nested folder trees, and reusable document templates equipped with automatic date and variable substitutions. Autonomous coding assistants and language models query documentation, create structured meeting summaries, and update project indexes directly through the native Model Context Protocol server. Built-in export tools convert notebook collections into standalone HTML packages, printable documents, or portable Markdown archives for offline archiving. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Kener
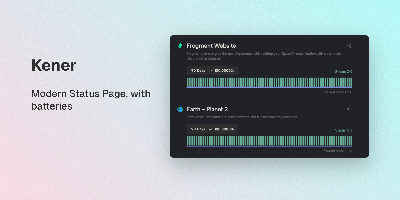
A polished public status page without Statuspage prices or a heavyweight observability suite: Kener is a status and uptime monitoring system built with SvelteKit and Node.js. It runs 11 monitor types - API, Ping, TCP, DNS, SSL certificate, SQL query, Heartbeat, gRPC, and GameDig game-server checks among them - each with configurable intervals and thresholds. Incident management covers the full lifecycle: structured timelines from investigation through resolution, acknowledgements, and subscriber-visible updates, plus maintenance windows with RRULE-based recurring schedules and automatic status transitions. Notifications reach email, Slack, Discord, and custom webhooks through trigger-based workflows with template-driven messaging. One instance can serve multiple branded status pages - per product, team, or region - with custom logos, colors, and CSS, localization into 21 languages, timezone-aware displays, and server-rendered pages that stay fast and SEO-friendly. Operations tooling includes role-based access for teams, API key management, a secrets vault, analytics integrations (Google Analytics, Plausible, Umami, and others), and a REST API with 17+ endpoints for automating incidents and monitors from CI/CD. MIT-licensed; Docker deployment with Redis, SQLite by default, PostgreSQL or MySQL for production.
Mage
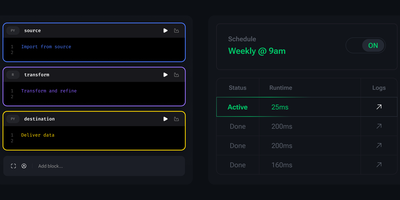
Backed by 8,700+ GitHub stars and designed as a modern alternative to Apache Airflow, Mage delivers the open-source data pipeline platform that combines the interactive flexibility of notebooks with production-grade orchestration in a single self-hosted environment accessible at port 6789. The modular block architecture lets data engineers compose pipelines from Python, SQL, and R code blocks with instant data previews, live execution logs, and visual debugging at each step. Over 100 prebuilt integrations connect sources and destinations including PostgreSQL, MySQL, Snowflake, BigQuery, Redshift, S3, Kafka, MongoDB, Amplitude, Salesforce, and Stripe with parallel stream synchronization for high-throughput data movement. Batch pipelines run on cron schedules or event triggers while streaming pipelines process real-time data from Kafka, Kinesis, and RabbitMQ with stream mode reducing memory usage by approximately 90 percent compared to batch processing. Native dbt integration builds, tests, and runs dbt models directly inside the pipeline editor alongside custom transformation blocks. Spark, Snowpark, and Databricks runtimes handle large-scale distributed processing. AI-assisted development generates code, fixes errors, and optimizes queries within the notebook interface. Monitoring dashboards track pipeline health with integrations to Datadog, Prometheus, New Relic, and OpenTelemetry. Terraform templates deploy production environments to AWS, GCP, or Azure with two commands, while Helm charts support Kubernetes clusters. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Tianji
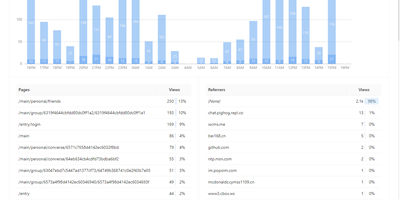
Website analytics, uptime monitoring, and server status - three tools most teams run separately - combined in Tianji, an open-source observability platform. The analytics layer tracks page views, unique visitors, referrers, and UTM parameters with a lightweight cookie-less script, which keeps collection GDPR and CCPA friendly. The uptime monitor checks availability and latency on configurable intervals, accepts passively reported results, and publishes public status pages for incident communication. Server status agents report CPU, memory, disk, and network metrics with threshold-based alerts, and notifications route through webhooks, Slack, Telegram, and other channels with noise control. It also includes anonymous telemetry for tracking deployments of your own open-source projects, surveys, waitlists, team collaboration, and an OpenAPI interface for integrations and exports. The consolidation is the point: traffic analytics, uptime checks, and server metrics share one interface and one alerting layer, so diagnosing an incident does not mean hopping between Google Analytics, Uptime Kuma, and Prometheus - and the built-in public status pages replace a separate paid Statuspage-style subscription. Because collection uses no cookies with IP truncation and aggregation by default, basic traffic measurement requires no consent banner. Built in TypeScript under the Apache 2.0 license and inspired by Umami and Uptime Kuma, it is deliberately right-sized for independent developers and small SaaS teams whose monitoring needs are real but lightweight.
Mission Control
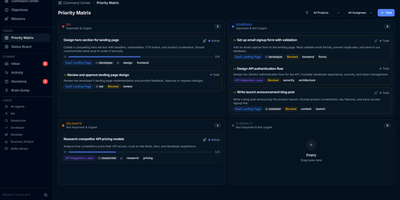
With over 600 GitHub stars and a featured Show HN launch, Mission Control is the agent-first command center that replaces the chaos of manually shepherding AI agents with structured delegation, approval workflows, and autonomous execution. The Next.js 15 web UI delivers an Eisenhower priority matrix with drag-and-drop quadrants, a Kanban board tracking tasks through Not Started, In Progress, and Done columns, and a goal hierarchy with milestone progress bars — powered by shadcn/ui, Radix UI, and @dnd-kit. Six built-in agent roles — Researcher, Developer, Marketer, Business Analyst, Tester, and You — receive tasks through a token-optimized API compressing context by 92 percent to approximately 50 tokens versus 5,400 unfiltered. The autonomous daemon polls task queues on cron schedules, spawns Claude Code sessions via the official CLI, enforces concurrency limits, and auto-retries with loop detection that escalates to human decisions after three failures. Field Ops extends execution to 64 external services across 16 categories with working X, Ethereum with MetaMask signing, and Reddit adapters, protected by AES-256-GCM encrypted vault with scrypt key derivation, per-service and global spend limits, a circuit breaker, and three autonomy levels. All data lives in local JSON files with Zod validation and async-mutex locking ensuring safe concurrent writes, backed by 193 automated Vitest tests. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Nexus Repository
Trusted by millions of developers and integrated into CI/CD pipelines at organizations worldwide, Sonatype Nexus Repository is the industry-standard binary artifact repository manager that stores, organizes, and distributes software components across every major package ecosystem. Community Edition supports over 20 formats including Maven for Java builds, npm for JavaScript packages, Docker for container images, PyPI for Python libraries, NuGet for .NET assemblies, Helm for Kubernetes charts, Go modules, RubyGems, Cargo for Rust crates, Conda for data science environments, APT for Debian packages, Yum for RPM distributions, and Hugging Face for AI/ML models. Three repository types serve different needs: hosted repositories store internally-produced artifacts, proxy repositories cache remote registries like Maven Central, npmjs.org, and Docker Hub reducing bandwidth and improving build reliability, and group repositories aggregate multiple hosted and proxy repositories behind a single URL endpoint. The web UI provides component browsing and search, repository configuration, blob store management with configurable cleanup policies, and direct artifact upload via drag-and-drop. Role-based access control enforces fine-grained permissions per repository with configurable security realms, while the comprehensive REST API enables automated repository provisioning, component management, and integration with Jenkins, GitHub Actions, GitLab CI, and Azure DevOps. External PostgreSQL database support enables Kubernetes deployments with improved backup, restore, and horizontal scaling capabilities. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Eclipse Public License 1.0 licensed.
Authorizer
Your users belong in your own database - Authorizer, an open-source authentication and authorization server shipping as a single Go binary, keeps them there. It connects to 13+ backends - PostgreSQL, MySQL, SQLite, SQL Server, MariaDB, MongoDB, Cassandra, ScyllaDB, ArangoDB, DynamoDB, Couchbase, YugabyteDB, PlanetScale, and CockroachDB - so identity data lives beside the application it protects instead of in an auth vendor's cloud. The server is fully OAuth 2.0 and OpenID Connect compliant, including authorization code flow with PKCE, a JWKS endpoint, token revocation, and nine JWT signing algorithms. Login options cover email/password, magic links, TOTP multi-factor, SMS OTP via Twilio, and social providers including Google, GitHub, Apple, Microsoft, and Discord. Authorization goes beyond roles: an embedded OpenFGA engine provides Zanzibar-style relationship-based permission checks in process. APIs are exposed over GraphQL, REST, and gRPC, with SDKs for JavaScript, React, Go, and Python, plus themeable built-in login pages and an admin dashboard. Apache 2.0 licensed.
Hasty Paste
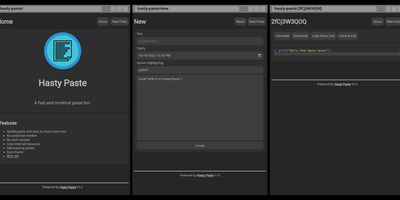
Paste some text, hit save, share the link - Hasty Paste is a fast, minimal pastebin written in Python on the async Quart framework, named, by its author's own admission, "because you use it so fast without a care in the world." No accounts, no authentication, no friction - built for the everyday case of handing a debug log, config snippet, or stack trace to someone in tech support or a chat channel. Pastes get randomly generated IDs, with an optional "long" ID mode that makes brute-force URL guessing impractical, and expiry times ensure throwaway content actually gets thrown away. Optional Pygments syntax highlighting makes code readable, a dark theme spares your eyes, and the whole interface works without JavaScript - it renders in terminal browsers and under the strictest script blockers. Storage is a custom flat-file system (no database), caching runs internally or through Redis for busier instances, and a REST API plus the companion "Hastily Paste It" CLI script enable piping command output straight into a paste from the terminal. The Alpine-based Docker image is tiny, resource usage is minimal, and the license is AGPL.
pgweb
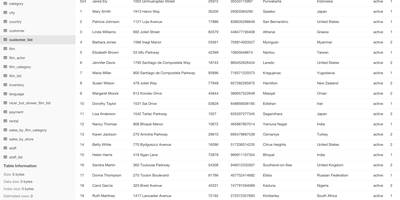
Inspect a PostgreSQL database right now, without installing pgAdmin or exposing Postgres to the internet - pgweb answers that recurring need. It's a Go application from Dan Sosedoff, a decade in development, shipped as a single statically-linked binary with zero dependencies - the Docker image is essentially just the executable - that puts a clean browser UI in front of any PostgreSQL 9.1+ server. Connect via URL string or host/port credentials, and browse tables, views, and sequences from the sidebar; selecting a table shows its rows immediately alongside tabs for structure, indexes, and constraints. The Query tab executes arbitrary SQL with query history, and the Explain Query button renders the query plan - estimated cost, row counts, execution strategy - which makes pgweb a quick performance-triage tool, not just a browser. Results and entire tables export to CSV, JSON, or XML in a click. Connectivity is more flexible than its size suggests: native SSH tunneling (password or key) reaches databases behind firewalls, server bookmarks make switching instances instant, and an optional multi-session mode handles several databases concurrently. For a RepoCloud stack full of Postgres-backed apps, one pgweb instance is the universal inspection hatch. MIT-licensed, actively maintained.