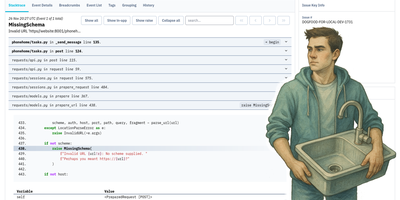
Bugsink
Bugsink has earned over 1,800 GitHub stars as the lightweight self-hosted error tracking platform that replaces Sentry without per-event billing by accepting error reports from any Sentry-compatible SDK across Python, JavaScript, Node.js, Ruby, Java, PHP, Go, and every other language Sentry supports. Simply update the DSN in your existing Sentry configuration and Bugsink captures the same stack traces, local variables, request context, and breadcrumbs that Sentry processes, displayed through a focused interface designed for debugging rather than dashboarding. Automatic issue grouping collapses duplicate error events into single actionable issues based on exception type, message, and stack frame context, turning thousands of raw events into a manageable list. Issue status tracking supports resolved, resolved-in-next-release, and muted states with automatic regression detection when resolved issues recur. Release tracking associates events with deploy versions to correlate error spikes with specific rollouts. Tag-based search filters issues by environment, release, user, browser, operating system, or any custom key-value pair sent by the SDK. Alerting notifies your team through Slack, Discord, Mattermost, and email when new issues appear or resolved issues regress, with per-project webhook configuration and user-level notification preferences. Per-project retention policies with automatic event eviction manage storage growth. A REST API with OpenAPI documentation enables custom integrations and dashboards. Source map support links minified JavaScript to original source. Deploy via Docker with the bugsink/bugsink image. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. PolyForm Shield licensed.
Dashy
Every service you run, behind one polished start page: Dashy is the most customizable homelab dashboard, built as a Vue.js homepage. Configuration lives in a single YAML file, but you never have to hand-edit it: an integrated UI editor with real-time validation writes changes back to disk, so both config-as-code and point-and-click camps are served. Status indicators put a live health dot next to every app - HTTP checks or pings on custom intervals, with response time and status details on hover - giving you an at-a-glance uptime overview before anything breaks. Over 50 built-in widgets pull dynamic content from the services you already run: Pi-hole and AdGuard block stats, Proxmox lists, Nextcloud status, Netdata CPU/memory history, Prometheus data, plus weather, RSS, crypto prices, and generic iframe/API-response widgets for anything with an endpoint. Instant fuzzy search launches any app as you type, with customizable hotkeys and web-search fallthrough. Theming is deep: dozens of built-in themes, a UI color palette editor, and custom CSS over CSS variables. Alternate views include a fast-loading minimal startpage and a workspace view that embeds apps side-by-side without leaving the dashboard. Icons resolve from Font Awesome, homelab icon packs, emojis, or auto-fetched favicons. Built-in authentication, multi-page support, cloud backup/sync, and multi-language round out an MIT project with a massive community.
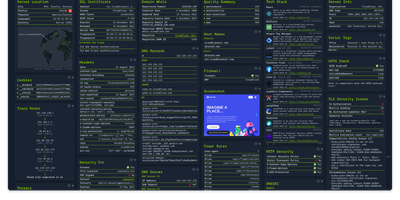
Web-Check
Enter a URL and get a dashboard of everything publicly discoverable about its security posture, server architecture, and technology stack: Web-Check is an all-in-one OSINT tool for analyzing any website. One scan surfaces IP info and server location, the full SSL certificate chain with issuing authority and validity, DNS records (A, MX, NS, CNAME, TXT) with DNSSEC status, HTTP response headers interpreted for security directives like HSTS, CSP, and X-Frame-Options, cookies and their flags, WHOIS domain info, robots.txt crawl rules, a sitemap-derived page map, the redirect ledger, open ports, traceroute, detected technologies, third-party trackers, associated hostnames, site performance, and even carbon footprint. Each card explains what the data means and why it matters, which makes the tool double as a security education resource - junior engineers learn headers and attack surfaces by scanning real sites. Practical uses span pre-deployment security audits (catch missing headers and misconfigurations before they ship), privacy compliance checks (identify trackers and cookie behavior for GDPR work), competitive tech-stack research, and network debugging via DNS and redirect inspection. Built by Lissy93 in TypeScript, it deploys as a single Docker container, and self-hosting keeps your reconnaissance targets and audit activity off third-party services.
OctoPrint
Over a million active instances make OctoPrint the standard web interface for consumer 3D printers - Gina Häußge's Python application, the center of the printing world since 2012. It talks to your printer over USB serial and turns every browser into a control panel: upload, organize, and start G-code prints; watch hotend and bed temperature graphs in real time; drive the print head manually; adjust feed rate, flow, and fan speed mid-print; and hit an emergency stop if things go wrong. The G-code visualizer renders the current layer in sync with the job, and a connected webcam adds a live feed plus automatic timelapse recording of every build. What keeps OctoPrint ahead is its plugin ecosystem - 300+ community plugins installable from the built-in manager. Highlights include Obico's AI spaghetti detection that pauses failed prints automatically, OctoEverywhere for tunnel-based remote access, Bed Level Visualizer's 3D mesh of your bed surface, PrintTimeGenius for accurate time estimates, Exclude Region to abandon one failed object mid-print while others continue, and Firmware Updater to flash Marlin or Klipper without SD-card shuffling. Event hooks fire notifications when prints finish or fail, and a full REST API supports slicer integration and custom automation. AGPL-licensed.
Keep
Keep is an open-source AIOps and alert management platform built with Python FastAPI and Next.js. It provides a single pane of glass for monitoring alerts from 110+ integrations, alert deduplication, correlation, enrichment, and filtering, YAML-based workflow automation similar to GitHub Actions, AI-powered correlation and summarization, and customizable dashboards for incident management. With 12,100+ GitHub stars, Y Combinator backing, and an Elastic partnership, Keep is the open-source AIOps platform that centralizes alert management across your entire monitoring stack into a single customizable dashboard. Alert deduplication identifies duplicate notifications across providers, correlation groups related alerts into incidents based on rules or AI-powered semantic analysis using pluggable LLM backends supporting OpenAI, Anthropic, and local models via Ollama, and enrichment adds context from external sources like CMDBs and databases. Workflow automation follows a GitHub Actions paradigm with declarative YAML files defining triggers, conditions, and actions that can query MySQL, update Jira tickets, send Slack messages, execute Python scripts, or call REST APIs. Authentication supports no-auth, database, Auth0, Keycloak, OAuth2 Proxy, Okta, and OneLogin. The Common Expression Language enables advanced alert querying, slicing, and rule-based grouping to reduce noise. On RepoCloud, deploy Keep on a dedicated VPS with Docker Compose, root SSH access, and complete control over your alert infrastructure, all under the MIT license.
OpenLIT
Your AI application is burning through API tokens faster than you can refresh the billing page, and you have no idea which prompt template is responsible. OpenLIT plugs that visibility gap with a self-hosted observability platform built specifically for LLM workloads. Add one line of code to instrument 90+ LLM providers, agent frameworks, and vector databases, then watch every request flow through a tracing dashboard that shows tokens consumed, latency measured, and dollars spent per call, per model, per environment. The requests view lists every LLM interaction with provider, model, cost, and token breakdown in a filterable table, while the trace detail panel lets you drill into individual spans to read the exact prompt sent and response received. Prompt Hub turns prompts into versioned artifacts you deploy, rollback, and A/B test without touching application code. OpenGround compares models side by side on the same input, so you can evaluate cost-versus-quality tradeoffs before committing to a provider. Automated evaluations run LLM-as-a-judge scoring on live production traces, flagging hallucinations, bias, and toxicity in real time. The Vault stores and rotates API keys centrally so secrets stay out of your codebase. Custom dashboards let you build drag-and-drop monitoring views with charts, stat cards, and tables backed by SQL queries against ClickHouse. GPU utilization, memory, temperature, and power metrics feed into the same platform for end-to-end infrastructure visibility. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
KubeSphere
Managing Kubernetes shouldn't require every developer to become a Kubernetes expert — KubeSphere wraps cluster operations, CI/CD, service mesh, and observability into guided web workflows that operations teams configure once and developers consume without kubectl. The LuBan extensible architecture treats each capability as an independently installable extension plugging into a lightweight microkernel: enable DevOps without service mesh, add monitoring without the app store, compose exactly what your organization needs. Multi-cluster management provides a centralized control plane for provisioning and operating clusters across cloud providers, data centers, and edge locations with unified identity and resource quotas. The DevOps extension integrates Jenkins for graphical pipeline creation with S2I and B2I workflows, while Argo CD powers GitOps continuous deployment with real-time sync status. Istio-based service mesh provides traffic management, canary deployments, circuit breaking, and distributed tracing through the console without CLI knowledge. Prometheus monitoring with custom dashboards, Fluentd log collection with multi-tenant search, and alerting via Slack and email complete the observability stack. Multi-tenant workspace hierarchy enforces resource quotas and fine-grained RBAC roles across teams. A built-in Helm-based app store handles lifecycle management across clusters. KubeKey deploys production-grade clusters on bare metal or VMs with air-gapped support. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Langfuse
Backed by Y Combinator and trusted by over 2,300 companies processing billions of observations monthly, Langfuse is the most widely adopted open-source platform for building, monitoring, evaluating, and debugging LLM applications. The hierarchical tracing engine captures every LLM call, tool invocation, retrieval step, and agent action as nested spans based on OpenTelemetry, with automatic cost calculation, latency tracking, and token usage attribution across sessions and users. Prompt Management separates prompts from code with versioned artifacts, label-based deployments, one-click rollbacks, and runtime SDK fetching with server-side caching, while linking every generation back to its exact prompt version for attribution analytics. The evaluation system supports LLM-as-a-judge scoring, heuristic code evaluators, user feedback collection, and manual annotation workflows that run automatically on production traces or against curated datasets. The Playground enables interactive prompt testing on real production inputs with side-by-side model comparison across providers. Datasets and Experiments define test cases for systematic benchmarking with comparative result visualization. Native SDKs for Python and TypeScript provide decorator-based instrumentation, while 100+ integrations cover LangChain, LlamaIndex, OpenAI SDK, LiteLLM, Vercel AI SDK, and any OpenTelemetry-instrumented framework. The analytics dashboard surfaces cost breakdowns, quality scores, latency percentiles, and usage trends across models and prompt versions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
QuestDB
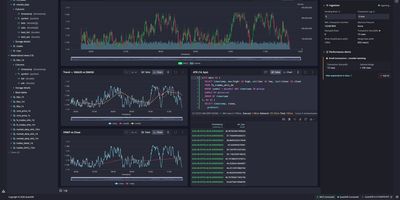
Powering trading floors at firms processing millions of market data events per second and trusted by organizations including Airbus, Yahoo, and Copenhagen Atomics, QuestDB has earned over 17,000 GitHub stars as the time-series database that refuses to make you choose between ingestion speed and query latency. The column-oriented, time-partitioned storage engine processes millions of rows per second on ingest through write-ahead logging with instant durability, while SIMD-accelerated parallel execution returns analytical queries over billions of rows in milliseconds. Time-series SQL extensions add ASOF JOIN for point-in-time lookups across tables with misaligned timestamps, SAMPLE BY for downsampling at arbitrary time intervals, LATEST ON for last-value queries, and WINDOW JOIN for sliding window aggregations — all through standard SQL syntax accessible via the PostgreSQL wire protocol, REST API, or the QuestDB Wire Protocol (QWP) that streams Apache Arrow at 220 million rows per second. Multi-tier storage automatically moves data from the WAL through native columnar format to Parquet files on S3-compatible object storage, keeping hot data fast and cold data portable without manual tiering. The built-in web console provides an interactive SQL editor with syntax highlighting, autocomplete, and charting for quick data exploration. Views, materialized views, and n-dimensional arrays support real-time analytics, while native Parquet export enables direct integration with Python, DuckDB, and AI/ML frameworks. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
CPA Manager Plus
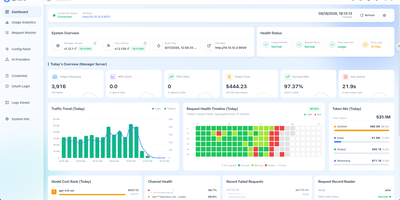
CPA Manager Plus is a self-hosted observability dashboard and management panel that tracks every AI request flowing through your CLI Proxy API gateway, breaking down failures, costs, and account health across providers like OpenAI, Anthropic, xAI, and Codex in one interface. When a request fails, drill into the persistent history to see status codes, affected models, latency, and redacted failure evidence without exposing raw response bodies. The cost analytics engine breaks down token consumption and estimated spend by model, provider, account, API key, project, channel, and time range while tracking input, output, reasoning, cache, and service-tier pricing semantics separately. Model prices sync automatically from models.dev with LiteLLM and OpenRouter fallbacks, and you can add local overrides for aliases or internal models. For teams running Codex or xAI accounts, the health inspector reads quota windows, reset evidence, credential state, and workspace status on a configurable schedule, routing credential failures into an action queue for review rather than letting them silently degrade throughput. Deploy the Lightweight Panel to replace your existing CPA management UI without adding another service, or run Full Mode as a single Docker container that adds the Manager Server with persistent SQLite storage for request history, historical analytics, and automated account inspections. Export or import request history as JSONL for external analysis, and back up the SQLite files alongside your encrypted management keys. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Grafana
The de facto dashboard of observability: Grafana is the open-source frontend that turns the data stores you already run into interactive graphs. It does not store metrics itself; it connects to the data stores you already run and turns their contents into interactive dashboards. Supported sources number over 150 via plugins: Prometheus, Loki, Tempo, InfluxDB, Elasticsearch, MySQL, PostgreSQL, Microsoft SQL Server, AWS CloudWatch, Azure Monitor, Google Cloud Monitoring, and many more. Dashboards are built from a large library of panel types (time series, heatmaps, tables, gauges, logs) with template variables for reusable, parameterized views. Unified alerting evaluates rules against any connected data source, not just Prometheus, and routes notifications to Slack, PagerDuty, email, and other channels with grouping and silencing - unlike Prometheus Alertmanager, a single rule can combine a Loki log pattern, a PostgreSQL query result, and a CloudWatch metric. Dashboards serialize to JSON and data sources configure via provisioning files, so the entire observability setup can live in Git and deploy repeatably across environments. Explore mode adds ad-hoc querying outside dashboards, with split view for correlating a metric spike against the matching log lines, and access control spans organizations, teams, folder permissions, and OAuth, LDAP, and SAML integration. Written in Go and TypeScript, AGPL-licensed. Self-hosting gives you unlimited users, dashboards, and queries at flat hosting cost, without Grafana Cloud's usage-based pricing.
Arcane
Arcane gives you a single polished dashboard to manage Docker containers, images, volumes, networks, and Compose projects across unlimited remote hosts. The SvelteKit frontend paired with a Go backend delivers real-time resource monitoring with historical graphs, container lifecycle controls including shell exec and live log streaming, and one-click Docker Compose deployment with Git repository synchronization for version-controlled stack definitions. The manager-agent architecture connects remote environments via Direct TCP on port 3553 or Edge mode where agents initiate outbound gRPC/WebSocket connections through NAT and firewalls without requiring inbound ports, all secured with mTLS certificates. Vulnerability scanning identifies security issues in running container images directly from the interface. The backup system enables scheduled container snapshots with configurable retention for disaster recovery. Network and volume administration includes visual relationship mapping between services, and the responsive interface supports dark/light themes with full mobile optimization and community-driven internationalization via Crowdin. 6,500+ stars and 89 releases since April 2025 reflect a rapid development cadence. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD-3-Clause licensed.
Beszel
Reaching 24,000 GitHub stars within two years of its first commit in July 2024, Beszel delivers Netdata-grade monitoring dashboards from a single Docker container with no Prometheus stack, no external database, and no complex configuration — just a one-binary hub on PocketBase (SQLite embedded) and a sub-15 MB agent per host that auto-discovers Docker and Podman containers on contact. The agent connects outbound via WebSocket or SSH tunnel, requiring zero open ports on monitored servers and zero manual network configuration. Per-host metrics cover CPU usage, memory with swap and ZFS ARC breakdown, disk I/O across multiple partitions, network throughput, load average, sensor temperatures, battery charge, and GPU utilization with power draw for Nvidia, AMD, and Intel cards — features that competitors lock behind paid tiers. S.M.A.R.T. disk health including eMMC wear indicators and Linux mdraid array status surface hardware degradation before failures occur. Container statistics track CPU, memory, and network history per container with automatic discovery as new containers start. Configurable threshold alerts notify via email, Discord, Telegram, ntfy, Pushover, Gotify, Matrix, Mattermost, Signal, Slack, Microsoft Teams, and Twilio when metrics exceed defined limits. Multi-user accounts with OAuth/OIDC authentication let teams share monitored systems with role-based access, while automatic backups persist data to disk or S3-compatible storage. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Wazuh
Protecting over 10,000 organizations worldwide with 16,000+ GitHub stars, Wazuh delivers enterprise-grade security operations through a fully open-source platform with zero feature gating. The unified XDR and SIEM solution deploys lightweight agents across Linux, Windows, macOS, Solaris, AIX, and HP-UX endpoints that stream security telemetry to a centralized cluster built on OpenSearch for indexing and the Wazuh Dashboard for visualization and management. Core capabilities include real-time file integrity monitoring with inotify-based detection and who-data attribution, automated vulnerability assessment that correlates software inventories against continuously updated CVE databases, Security Configuration Assessment against CIS benchmarks, rootkit detection, and log data analysis with a rules engine supporting over 3,000 built-in detection rules mapped to MITRE ATT&CK tactics and techniques. Wazuh monitors cloud infrastructure at the API level with native modules for AWS, Azure, and Google Cloud, detects container anomalies through Docker engine integration, and ingests third-party telemetry via syslog and REST APIs from sources like VirusTotal, TheHive, YARA, Suricata, and PagerDuty. Pre-built compliance dashboards and reports cover PCI DSS, HIPAA, NIST 800-53, GDPR, and TSC frameworks. Active response capabilities automatically trigger countermeasures including firewall rule updates, account lockouts, and endpoint isolation when threats are detected. The platform scales horizontally with multi-node clustering for high availability. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-2.0 licensed.
Headlamp
The Kubernetes project's own answer to cluster management UIs: maintained under SIG UI governance, Headlamp's roadmap tracks Kubernetes releases and its design philosophy reflects community needs rather than a vendor's product strategy. The React interface provides full read-write capabilities adapted to each user's RBAC permissions — delete, scale, edit, and restart buttons appear only when the authenticated user holds the corresponding cluster role, preventing accidental unauthorized actions. Multi-cluster support surfaces workloads across development, staging, and production from a single view without context switching. The plugin architecture drives extensibility through a curated catalog: an AI Assistant plugin answers natural-language cluster queries and performs operations via configurable LLM keys, Flux handles GitOps, Karpenter manages nodes. Integrated terminals provide browser-based exec access to running pods, live log streaming follows container output with filtering, and the YAML editor displays inline Kubernetes API documentation alongside resource definitions. Deployment creation forms let you configure containers, environment variables, volumes, and replicas without writing manifests. Side-by-side cluster comparison views surface differences in workload distribution. Works with any distribution: EKS, GKE, AKS, Minikube, Docker Desktop. Helm chart installation via the Headlamp repository with images on GitHub Container Registry. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
SigNoz
With over 31,000 GitHub stars and native OpenTelemetry support that eliminates vendor lock-in from day one, SigNoz delivers full-stack observability covering metrics, traces, and logs in a single pane of glass without the per-host pricing model of commercial APM platforms. The platform ingests telemetry data through the OpenTelemetry Collector, supporting auto-instrumentation for Java, Python, Node.js, Go, Ruby, PHP, and .NET applications with zero code changes required for basic tracing. ClickHouse serves as the columnar storage backend, providing fast aggregation queries over billions of spans and log lines with configurable retention policies and tiered storage. The distributed tracing view renders flame graphs and Gantt charts showing request flow across microservices with latency breakdowns, error rates, and p99 percentile calculations. Custom dashboards support PromQL and ClickHouse SQL queries with time-series charts, bar graphs, tables, and value widgets. The log management pipeline supports structured and unstructured logs with full-text search, log pipelines for parsing and enrichment, and correlation with traces via trace IDs. Alert rules can be configured on any metric or log query with notification channels including Slack, PagerDuty, OpsGenie, webhooks, and email. The exceptions monitoring module automatically groups and tracks application errors with stack traces, occurrence counts, and first-seen timestamps. Service maps visualize inter-service dependencies with real-time latency and error rate overlays. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed with an enterprise edition available.
Laminar
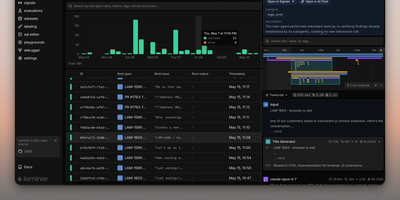
Backed by Y Combinator (S24) and processing traces from thousands of AI agents in production, Laminar is the open-source observability platform that treats agent debugging as a first-class engineering discipline rather than an afterthought. Its OpenTelemetry-native SDK auto-instruments Vercel AI SDK, LangChain, OpenAI, Anthropic, Gemini, Browser Use, Stagehand, Mastra, Pydantic AI, and the OpenAI Agents SDK with a single line of code, capturing every LLM turn, tool call, and sub-agent delegation as nested spans with full input/output data and token costs. The Signals engine lets you describe failures in plain language — "agent is stuck in a loop" or "tool returned empty results" — then reads every trace and alerts via Slack when it detects a match. A built-in debugger records runs and replays them from cache so each iteration takes seconds, designed for Claude Code, Cursor, or Codex to drive the repair loop via the MCP server or CLI. Run code-first evaluations in Python or TypeScript locally or in CI/CD pipelines, build datasets from production traces, and query everything with raw SQL through custom dashboards, the in-app editor, or your coding agent. The Rust backend delivers 20x trace compression, a custom real-time streaming engine, ultra-fast full-text search, and gRPC ingestion, while ClickHouse powers columnar analytics and PostgreSQL stores application state. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Homarr
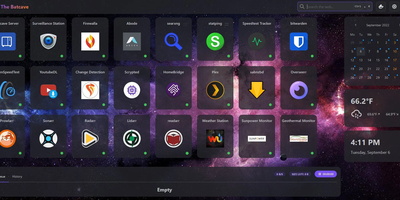
A single pane of glass for every service you run, arranged by drag-and-drop with no YAML or JSON files: Homarr is the modern dashboard for self-hosted infrastructure. Its grid system arranges apps, widgets, and bookmarks on desktop or touch, backed by an icon picker with over 11,000 icons. What separates Homarr from static launchers is 50+ live integrations: Plex, Jellyfin, and Emby media stats, the *arr suite (Sonarr, Radarr) with a unified release calendar, download clients, Pi-hole and AdGuard Home controls, Proxmox, Home Assistant, OPNsense, and Unifi monitoring. Widgets update in real time over WebSockets (tRPC and Redis under the hood), and a built-in search queries thousands of data points across connected services. Custom widgets extend the reach to any HTTP API without code: define endpoint, auth, and refresh interval in the management UI, then render responses as stat grids, tables, progress bars, status indicators, action buttons, or full custom JSX layouts - with an AI-prompt helper for generating templates. Multi-user support is first-class: credentials, OIDC, or LDAP sign-on, groups with granular permissions, and secrets encrypted with AES-256-CBC. A robust background-job system scales it from a Raspberry Pi homelab to deployments serving hundreds of users.