Dokploy VPS
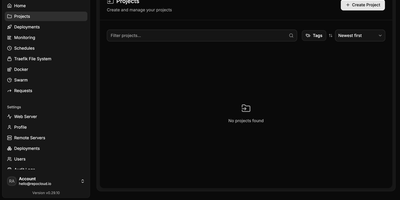
Your own Heroku or Vercel on a dedicated server — Dokploy is the open-source PaaS that replaces cloud platform subscriptions with a single dashboard you control. Point it at a Git repository or a Docker image, and it builds and deploys the application using Dockerfiles, Nixpacks, or Heroku/Paketo buildpacks. Traefik handles reverse proxying, routing, load balancing, automatic Let's Encrypt SSL, and HTTP/3. Databases — MySQL, PostgreSQL, MongoDB, MariaDB, libsql, and Redis — provision from the UI with automated backups to any S3-compatible destination. Complex multi-service applications deploy through native Docker Compose support, and multi-node scaling uses Docker Swarm. The web dashboard covers environment variables, volumes, resource limits, real-time CPU/memory/network monitoring, and deployment logs, with a CLI and REST API for automation. Deploy notifications go to Slack, Discord, Telegram, or email. One-click templates install common open-source tools, and a single control plane can manage deployments across multiple remote servers. Because everything is standard Docker, there is no lock-in: Dockerfiles, Compose files, and data volumes work anywhere else Docker runs. The push-to-deploy workflow of a $20/seat cloud PaaS, running on a dedicated VPS with guaranteed CPU, RAM, SSD, and full root access — no per-app, per-environment, or per-seat fees regardless of how many applications you deploy. 26,000+ GitHub stars.
Supabase
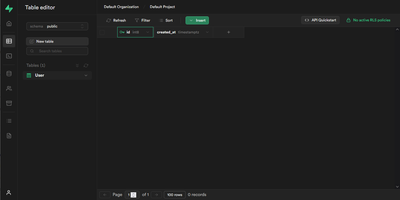
With over 107,000 GitHub stars and adoption by teams at Mozilla, 1Password, Peerlist, and thousands of startups, Supabase has become the most widely deployed open-source Firebase alternative — built entirely on PostgreSQL rather than a proprietary NoSQL store. Every project provisions a dedicated Postgres database with 40+ preinstalled extensions, auto-generating REST APIs via PostgREST, GraphQL via pg_graphql, and real-time change streams via an Elixir-based WebSocket engine that supports database change listeners, user presence tracking, and arbitrary broadcast messaging. Authentication covers email and password, phone OTP, magic links, and 20+ social providers including Google, GitHub, Apple, Azure, and SAML SSO, all enforced through Postgres Row Level Security policies that run inside the database itself. S3-compatible object storage delivers files through a CDN spanning 285+ cities with on-the-fly image transformations powered by imgproxy. Edge Functions run globally distributed TypeScript on the Deno runtime with Node.js compatibility and access to over two million NPM packages. The pgvector extension stores, indexes, and queries vector embeddings for AI-powered semantic search and retrieval-augmented generation workflows. Supabase Studio provides a browser-based dashboard with a table editor, SQL editor, schema visualizer, and log explorer. Official client SDKs ship for JavaScript, Python, Flutter, Swift, Kotlin, C#, Go, and Ruby. The self-hosted Docker Compose stack runs fourteen coordinated services including Kong API gateway, Supavisor connection pooler, and Logflare analytics. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Coolify VPS
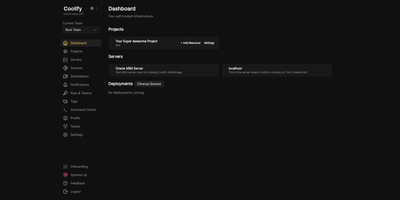
The open-source PaaS with 55,000+ GitHub stars and the largest one-click service catalog in its class — Coolify gives you the Vercel push-to-deploy workflow on a dedicated server you control. Connect a GitHub, GitLab, Bitbucket, or Gitea repository and every push builds and deploys automatically via Nixpacks, a Dockerfile, or Docker Compose, with Traefik or Caddy reverse proxying, automatic Let's Encrypt certificates, and per-branch preview deployments with their own URLs. Databases — PostgreSQL, MySQL, MariaDB, MongoDB, Redis — provision in a few clicks, and a catalog of 280+ one-click service templates covers WordPress, n8n, Grafana, MinIO, Plausible, Ollama, and more. One dashboard manages the entire server, with Docker Swarm available for clustering multiple nodes. Backups go to any S3-compatible storage with one-click restore, and a full API supports CI/CD integration. All configuration lives on your own server, so resources keep running even if you stop using Coolify — no vendor lock-in by design. Running on a dedicated VPS with guaranteed CPU, RAM, and SSD, full root access via SSH and browser console. Apache 2.0 licensed.

CubeSandbox
CubeSandbox gives every AI agent its own hardware-isolated MicroVM with a dedicated Linux kernel — not a shared-kernel container but a true KVM virtual machine — booting in under 60ms with less than 5MB of memory overhead per instance, enabling thousands of concurrent sandboxes on a single server via kernel sharing and Copy-on-Write memory. The Rust-built CubeProxy exposes an E2B SDK-compatible REST API on Axum, so existing E2B Cloud applications switch by changing one environment variable with zero client code changes. CubeMaster orchestrates cluster-level scheduling in Go while Cubelet manages node-local sandbox lifecycles including create, run, pause, resume, snapshot, and destroy operations. CubeVS, the eBPF-powered network layer, enforces per-sandbox isolation with LPM trie-based egress policies entirely in kernel space — no userspace context switches — while CubeEgress provides an L7 security proxy with per-domain, per-path, and per-method allowlists plus automatic credential injection that keeps secrets invisible to sandbox code. Hundred-millisecond-granularity snapshots enable checkpoint, rollback, and parallel fork from any saved state. The volume framework supports E2B-compatible pluggable storage with independent lifecycle and cross-sandbox sharing. Production deployment uses Terraform on Tencent Cloud or Helm charts on Kubernetes, K3s, or TKE, with full ARM64 support alongside x86_64 and AutoPause/AutoResume for cost optimization. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
UWAS
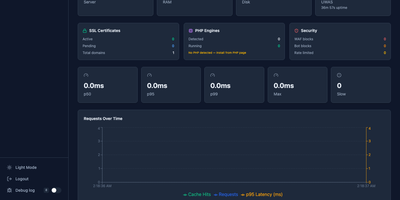
One 18 MB Go binary does the job of Apache, Nginx, Varnish, Caddy, and cPanel combined. Point UWAS at your /var/www directory and it auto-detects sites, provisions Let's Encrypt certificates, enables HTTP/3 via QUIC, and activates a two-tier caching engine with L1 memory shards and L2 disk storage, all before you write a single line of configuration. The React 19 admin dashboard provides 42 management pages for domains, PHP versions, databases, cron jobs, DNS records, file management, backup and restore, SFTP users, and uptime monitoring with real-time SSE updates. PHP sites run through FastCGI with connection pooling and full .htaccess compatibility, so WordPress, Laravel, and legacy applications work without migration effort. The built-in WAF catches SQL injection, XSS, path traversal, and shell exploits, while per-domain rate limiting and bandwidth caps protect against abuse. Reverse proxy mode supports five load balancing algorithms, circuit breakers, canary deployments, and mirroring for blue-green rollouts. Git deploy clones your repository, runs the build, checks health, and restarts the service with rollback on failure. An MCP server lets AI agents manage domains, cache, and deployments through natural language. The Nginx and Apache migration CLI converts existing configurations to UWAS format automatically. Deploy on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Ory Hydra
Ory Hydra is an OpenID Certified OAuth 2.0 and OpenID Connect provider that plugs into any existing user database or authentication system through a headless consent and login bridge, letting you own your authorization infrastructure without rebuilding identity management from scratch. The Go binary ships at under 15MB with zero system dependencies and exposes two distinct API surfaces: a public endpoint on port 4444 handling authorization code flows, token exchanges, PKCE challenges, device authorization grants per RFC 8628, and OpenID Connect discovery, plus an admin endpoint on port 4445 managing client registration, token introspection, consent session lifecycle, and JWKS rotation. Access tokens can be issued as opaque reference tokens or signed JWTs for stateless validation at resource servers, while refresh token rotation, token revocation per RFC 7009, and pairwise subject identifiers provide granular security controls. Persistent storage spans PostgreSQL, MySQL, and CockroachDB with automatic schema migrations, and the architecture supports horizontal scaling behind load balancers with shared database state. Dynamic client registration per RFC 7591 enables automated provisioning, and the OAuth 2.0 Threat Model security considerations are implemented as default behaviors rather than optional add-ons. Trusted by OpenAI and other internet-scale platforms. Helm charts and Docker Compose quickstarts provide production-ready deployment paths alongside the broader Ory ecosystem including Kratos for identity management, Oathkeeper for zero-trust API proxying, and Keto for fine-grained permissions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Dockhand
Dockhand is a Docker management platforms, offering a modern alternative to Portainer with free OIDC SSO and vulnerability scanning that competitors gate behind paid tiers. Real-time container management provides start, stop, restart, and remove operations with live resource monitoring across CPU, memory, and network usage on a dashboard with real-time metrics. The visual Docker Compose editor enables stack creation and modification with syntax highlighting, while Git integration deploys stacks directly from repositories with webhooks and auto-sync for GitOps workflows. Vulnerability scanning powered by Grype and Trivy analyzes container images against CVE databases, with configurable auto-update scheduling that can trigger updates based on vulnerability severity criteria. The Hawser Go agent enables management of remote Docker hosts in Standard mode for LAN environments or Edge mode using outbound WebSocket connections for hosts behind NAT, firewalls, or dynamic IPs without exposing inbound ports. Interactive terminal sessions provide shell access into running containers, while the file browser enables uploading, downloading, and editing files directly within containers. Image management includes registry browsing, pull operations, and layer inspection alongside network and volume administration. The security-focused architecture builds its own OS layer from scratch using Wolfi packages via apko with every package explicitly declared. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSL 1.1 licensed, converting to Apache 2.0 in 2029.
CubeJS
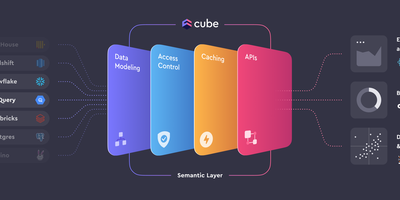
Between your databases and everything that consumes data - BI tools, embedded analytics, AI agents - sits Cube (formerly Cube.js), an open-source semantic layer. Metrics, dimensions, joins, and access rules are defined once as code in YAML, JavaScript, or Python, forming a governed data model that every downstream consumer shares, so "revenue" means the same thing in every dashboard. Caching is two-level: an in-memory cache absorbs bursts of identical queries, and declared pre-aggregations - rollup tables built in the warehouse or in Cube Store, Cube's distributed columnar engine, and refreshed in the background - deliver sub-second latency while cutting warehouse compute costs. The query planner routes each request to cache, rollup, or source automatically. Consumers connect through a Postgres-compatible SQL API (any tool that speaks Postgres works), plus REST, GraphQL, and a Meta API for model introspection. Row-level security and multi-tenancy are enforced in the layer itself, upstream of every client. Sources include Snowflake, BigQuery, Databricks, Postgres, MySQL, Presto, and Athena. Headless by design - bring your own UI.
ToolHive
ToolHive is an open-source MCP server management platform that lets you run, secure, and orchestrate Model Context Protocol servers in isolated containers, giving AI agents structured access to tools like GitHub, databases, and cloud services without exposing host credentials or network. Every server launches inside its own sandboxed container with a minimal permission file, network access filtering, and encrypted secrets management, preventing misbehaving connectors from reaching beyond their defined scope. The built-in registry provides a catalog of vetted servers you can install with one command, while custom images and package-manager references let you onboard proprietary connectors without writing Dockerfiles. Platform teams deploy the Kubernetes operator to declare MCP servers as cluster resources using Custom Resource Definitions, with automated lifecycle management and multi-namespace isolation. The Virtual MCP Server gateway aggregates multiple backends behind a single endpoint, centralizing OIDC authentication, tool filtering, and composite cross-server workflows so clients connect once instead of juggling separate URLs. An MCP Optimizer analyzes tool schemas via semantic search and surfaces only relevant tools per request, cutting token consumption by up to 85%. OpenTelemetry traces and Prometheus metrics deliver full visibility into tool execution, latency, and request audit trails across every managed server. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Arcane
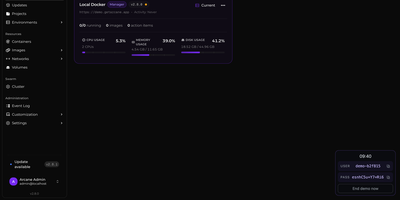
Arcane gives you a single polished dashboard to manage Docker containers, images, volumes, networks, and Compose projects across unlimited remote hosts. The SvelteKit frontend paired with a Go backend delivers real-time resource monitoring with historical graphs, container lifecycle controls including shell exec and live log streaming, and one-click Docker Compose deployment with Git repository synchronization for version-controlled stack definitions. The manager-agent architecture connects remote environments via Direct TCP on port 3553 or Edge mode where agents initiate outbound gRPC/WebSocket connections through NAT and firewalls without requiring inbound ports, all secured with mTLS certificates. Vulnerability scanning identifies security issues in running container images directly from the interface. The backup system enables scheduled container snapshots with configurable retention for disaster recovery. Network and volume administration includes visual relationship mapping between services, and the responsive interface supports dark/light themes with full mobile optimization and community-driven internationalization via Crowdin. 6,500+ stars and 89 releases since April 2025 reflect a rapid development cadence. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD-3-Clause licensed.
Beszel
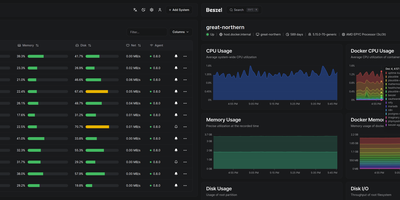
Reaching 24,000 GitHub stars within two years of its first commit in July 2024, Beszel delivers Netdata-grade monitoring dashboards from a single Docker container with no Prometheus stack, no external database, and no complex configuration — just a one-binary hub on PocketBase (SQLite embedded) and a sub-15 MB agent per host that auto-discovers Docker and Podman containers on contact. The agent connects outbound via WebSocket or SSH tunnel, requiring zero open ports on monitored servers and zero manual network configuration. Per-host metrics cover CPU usage, memory with swap and ZFS ARC breakdown, disk I/O across multiple partitions, network throughput, load average, sensor temperatures, battery charge, and GPU utilization with power draw for Nvidia, AMD, and Intel cards — features that competitors lock behind paid tiers. S.M.A.R.T. disk health including eMMC wear indicators and Linux mdraid array status surface hardware degradation before failures occur. Container statistics track CPU, memory, and network history per container with automatic discovery as new containers start. Configurable threshold alerts notify via email, Discord, Telegram, ntfy, Pushover, Gotify, Matrix, Mattermost, Signal, Slack, Microsoft Teams, and Twilio when metrics exceed defined limits. Multi-user accounts with OAuth/OIDC authentication let teams share monitored systems with role-based access, while automatic backups persist data to disk or S3-compatible storage. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Semaphore
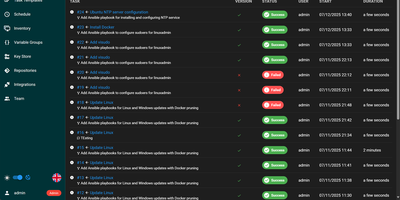
With nearly 14,000 GitHub stars and over 200 releases, Semaphore UI has established itself as the lightweight yet powerful alternative to enterprise automation platforms like Ansible AWX and Jenkins. Unlike AWX's heavyweight Kubernetes-dependent architecture, Semaphore ships as a single Go binary with zero external runtime dependencies — install it, run setup, and you have a production-ready automation server in minutes. The platform natively orchestrates Ansible playbooks, Terraform and OpenTofu infrastructure code, Terragrunt configurations, PowerShell scripts, Bash commands, and Python automation, all from a clean Vue.js web interface that displays task history, execution logs, and scheduling status at a glance. Semaphore supports concurrent task execution across multiple servers using distributed project runners, enabling horizontal scaling of automation workloads without complex clustering. The built-in inventory management system handles both static and dynamic inventory sources, while four-level RBAC (Owner, Manager, Task Runner, Guest) provides granular access control for team environments. Notifications flow to Slack, Microsoft Teams, Telegram, email, Rocket.Chat, and Gotify, keeping operators informed of failed tasks and deployment status. Integration with HashiCorp Vault secures sensitive credentials, and the comprehensive REST API with built-in Swagger documentation enables programmatic automation. Deploy via Docker Compose, Helm chart for Kubernetes, or native packages for Debian, Ubuntu, and RHEL-based distributions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Ralph
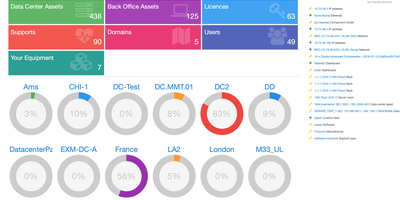
Ralph tracks thousands of assets across data centers and back offices through a unified CMDB, DCIM, and asset management platform, providing the same capabilities as ServiceNow, Device42, and Sunbird dcTrack without per-asset licensing fees. Used by Allegro in production and backed by over 2,500 GitHub stars, it is built on Python 3 with Django and Django REST Framework. Interactive data center floor plans support drag-and-drop rack placement, front and rear rack views showing U-level asset positioning, power consumption tracking per PDU, and ethernet and fiber connection mapping. The back office module manages laptops, desktops, printers, mobile phones, and accessories with user assignment tracking, warehouse inventory, stock-taking audits, and automated loan workflows. IP address management handles network environments with DHCP and DNS integration alongside network topology visualization. Software license tracking monitors per-user and per-core allocations with usage calculations, compliance reporting, and expiration alerts, while vendor support contracts track SLA agreements and warranty renewal dates. The transitions system automates asset lifecycle processes through configurable workflows that trigger HTTP webhooks, custom Python scripts, email notifications, and Puppet and Ansible configuration management integration. Custom fields extend the data model with text, numbers, dates, choices, and URLs per asset type, accessible via the REST API. Multi-tenant architecture organizes assets by regions, data centers, service environments, and business units. Deploy via Docker with the allegro/ralph image alongside MySQL and Redis. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
OpenLLM
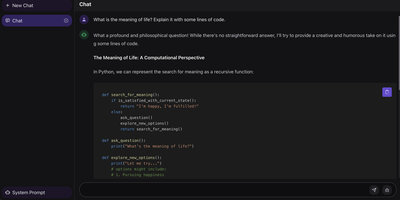
OpenLLM serves any large language model as an OpenAI-compatible API endpoint from a single CLI command, handling model download, backend selection, quantization, and port binding automatically. It supports the full spectrum of popular models including Llama 3.3, Qwen2.5, DeepSeek, Mistral, and Phi3, choosing between vLLM and PyTorch inference backends based on hardware capabilities. When vLLM is available, continuous batching with PagedAttention achieves up to 23x throughput improvement over naive serving, while GPTQ and bitsandbytes quantization reduces memory requirements for GPU-constrained deployments. The server exposes a RESTful API on port 3000 with full OpenAI client library compatibility, enabling drop-in replacement for commercial providers in any application using the standard chat completions format. A built-in web chat UI at the /chat endpoint provides immediate interactive testing without external clients. Custom model repositories allow teams to maintain private catalogs of fine-tuned models alongside the default repository that tracks the latest releases. Deployment workflows generate production-ready Docker images automatically, with Kubernetes manifest support for orchestrated scaling. Native integration with LangChain and LlamaIndex supports RAG pipelines, Transformers Agents enables tool-calling workflows, and HuggingFace Hub handles model discovery. Server-Sent Events enable real-time token streaming across all API endpoints. Backed by BentoML's production ML infrastructure. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Cognee
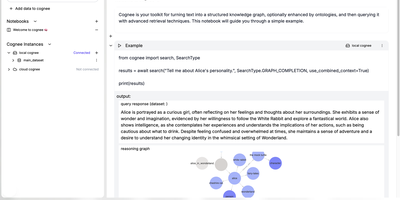
Cognee gives AI agents persistent long-term memory that survives across sessions, replacing the traditional stack of separate graph, vector, and session databases with a unified engine running on a single PostgreSQL instance. The memory-native API exposes four verbs (remember, recall, forget, and improve) enabling agents to persist context, retrieve cited answers, prune outdated knowledge, and self-improve from feedback. Under the hood, Cognee combines pgvector embeddings with a PostgreSQL-native graph store and cognitive-science-grounded ontology generation, delivering hybrid retrieval that fuses semantic similarity, structural graph traversal, and lexical search in a single query. Integrations span Claude Code, Cursor, LangGraph, OpenAI Agents, and any MCP-compatible client through a dedicated MCP server on port 8001, while the Python and TypeScript SDKs provide direct programmatic access. The platform supports swappable backends including Neo4j, FalkorDB, Qdrant, ChromaDB, Weaviate, Milvus, and LanceDB for teams with existing infrastructure. Built-in OpenTelemetry tracing, an experimental dashboard with knowledge graph visualization, multi-tenant user isolation, and audit trails ensure production readiness. Deploy via Docker Compose with optional profiles for PostgreSQL, Neo4j, Redis, and the web frontend. Reached v1.0 in April 2026 with 30,000+ stars. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Kong
With over 43,000 GitHub stars and adoption by companies including Nasdaq, Samsung, and Expedia, Kong Gateway is the world's most deployed open-source API gateway, processing billions of API requests daily across hybrid-cloud and multi-cloud architectures. Built on the battle-tested NGINX engine with OpenResty's LuaJIT runtime, Kong delivers sub-millisecond proxy latency while supporting REST, gRPC, GraphQL, WebSocket, SOAP, and Kafka protocols. The plugin architecture includes authentication via JWT, Basic Auth, HMAC, key authentication, OAuth 2.0, and LDAP, alongside rate limiting with configurable windows per consumer, IP address, or API key. The AI Proxy plugin provides a universal LLM API that routes across OpenAI, Anthropic, Google Gemini, AWS Bedrock, Azure AI, Databricks, Mistral, and Hugging Face through a single standardized interface, while MCP proxy capabilities convert REST APIs into MCP tools and provide traffic governance for AI agents. Kong supports declarative configuration via YAML for GitOps workflows, a RESTful Admin API for dynamic configuration, and decK CLI for version-controlled infrastructure-as-code management. Upstream health checking with active and passive probes enables automatic failover, and the ring balancer distributes traffic across upstream targets with consistent hashing, round-robin, or least-connections algorithms. The Kong Plugin Hub hosts over 100 community and official plugins covering logging, monitoring, transformation, security, and traffic control. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Treg
With over 330 GitHub stars and described as "OpenRouter, but for agent tools instead of models," Treg is the unified tool registry that gives your AI agent one base URL, one token, and instant access to approximately 2,800 cataloged endpoints across 56 providers — SEO and backlink analysis via Semrush and Moz, social media intelligence from TikTok and Instagram, people and company enrichment through Crunchbase and Hunter, media buying, scraping, and SERP data — all priced per call from fractions of a cent with no provider signup required. The FastAPI backend with PostgreSQL stores credential bindings and injects them server-side into every proxied request, ensuring API keys and OAuth tokens never touch the agent or local machine while every call is audit-logged. Teams register their own paid API accounts, OAuth connections, vendor CLIs like Stripe, GitHub CLI, Vercel, and gcloud, plus custom SKILL.md definitions — all callable by every teammate's agent through a single treg token with automatic credential injection. The evidence-based tool selector shows success rate, response speed, and last-seen timestamp for each provider, so agents pick tools on measured performance rather than guesswork. Bring-your-own-key routes bypass metering entirely, and the one-dollar free credit on every new team lets agents start calling immediately. The Vue.js web dashboard provides team management, audit logs, catalog browsing, and guided onboarding. Self-host with pip install tools-registry[server] on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
LiteLLM
Backed by 56,000+ GitHub stars and over 240 million Docker pulls, LiteLLM delivers the open-source AI gateway trusted by Netflix, Lemonade, Rocket Money, and thousands of engineering teams to route every LLM request through one unified API. The Rust-core gateway adds sub-millisecond overhead per request with 8ms P95 latency at 1,000 RPS, 15x throughput improvement and 11x lower memory footprint compared to Python-only proxies. A single OpenAI-compatible endpoint connects to 100+ providers and 1,800+ models spanning OpenAI, Anthropic, Google Gemini, AWS Bedrock, Azure OpenAI, Vertex AI, Hugging Face, vLLM, Nvidia NIM, Ollama, and Mistral with day-zero support for new model releases. The Auto Router V2 classifies request complexity across four tiers using rule-based scoring, semantic keyword matching, and adaptive Thompson sampling to route each request to the most cost-effective model without API calls or training data. Virtual API keys enable multi-tenant governance with per-team, per-user, and per-project cost tracking, budget caps with automatic fallback rerouting, and role-based access control. Built-in guardrails provide PII masking, prompt injection detection, and model-graded evaluation before requests reach providers. The Agent Gateway extends routing from model calls to agent workflows with MCP server integration. Observability integrates with Langfuse, Arize Phoenix, OpenTelemetry, and MLflow for complete request tracing. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.